AI agents: High effort, low return
AI has arrived in the business world — and the results are thus far underwhelming. According to McKinsey, 89% of companies now use AI regularly, and the majority are at least experimenting with AI agents. However, a significant gap remains between usage and economic success. “We find that only 37% of companies attribute any positive […]
Small businesses are having their AI moment — and it’s exposing a services gap
I have spent more than 30 years in enterprise IT and managed services. For most of that time, small businesses adopted new technology on a predictable lag. Large enterprises moved first because they had the budget, staff and risk tolerance to experiment. Everyone else waited for the tools to mature and prices to fall. That […]
In Other News: $15K iCloud Spoofing Bugs, AI Policy Experts Phished, Adblocker Spies on AI Chats
Noteworthy stories that might have slipped under the radar: Kiteworks patches over 100 vulnerabilities, Microsoft publishes 2026 Digital Defense Report, AI finds 24 Android app flaws. The post In Other News: $15K iCloud Spoofing Bugs, AI Policy Experts Phished, Adblocker Spies on AI Chats appeared first on SecurityWeek.
macOS Users Targeted by Fake Zoom Installer Carrying CloudSyncD Backdoor
The dropper “carries a complete universal Mach-O inside itself, roughly 756 KB in the development build, and extracts it at runtime. The post macOS Users Targeted by Fake Zoom Installer Carrying CloudSyncD Backdoor appeared first on SecurityWeek.
Crypto Scammers Hijack Microsoft’s Official X Account
Hackers used the account, which has 13 million followers, to amplify a Clippy-themed cryptocurrency account. The post Crypto Scammers Hijack Microsoft’s Official X Account appeared first on SecurityWeek.
In Rare Move, Alleged Iranian State Hacker Extradited to US
Amir Barati, an alleged member of the Mabna Institute, was indicted for targeting universities, private organizations, and government entities in the US and abroad. The post In Rare Move, Alleged Iranian State Hacker Extradited to US appeared first on SecurityWeek.
The State of Cybersecurity in 2026: Key Segments, Insights, and Innovations
Featuring: Cybersecurity is being reshaped by the expansion of cloud infrastructure, AI, distributed systems, and increasingly complex digital environments. As organizations manage more identities, devices, data, and internet-facing infrastructure, security is shifting toward continuous visibility, control, and the ability to respond to risk at scale. This report examines how core areas of
22-01970(4).pdf
22-01970(4).pdf Anonymous (not verified) Fri, 10/02/2026 – 17:30 Case ID 22-01970 Forum FINRA Document Type Award Claimants Merrill Lynch Pierce Fenner & Smith Inc. Respondents John Lahoud Neutrals Robert J. Kheel Sandra J. Mullings Arturo C. Porzecanski Hearing Site New York, NY Award Document 22-01970(4).pdf Documentum DocID 12637594 Award Date Official Fri, 04/11/2025 – 12:00 […]
26-01240.pdf
26-01240.pdf Anonymous (not verified) Fri, 10/02/2026 – 17:30 Case ID 26-01240 Forum FINRA Document Type Award Claimants Morgan Stanley Morgan Stanley Smith Barney Financing LLC Respondents Calvin Shiu Neutrals Arocles Aguilar Hearing Site San Francisco, CA Award Document 26-01240.pdf Documentum DocID 1efcfca6 Award Date Official Fri, 10/02/2026 – 12:00 Related Content Off Claimant Representatives Jennifer […]
24-00310.pdf
24-00310.pdf Anonymous (not verified) Fri, 10/02/2026 – 17:25 Case ID 24-00310 Forum FINRA Document Type Award Claimants Wells Fargo Clearing Services, LLC Respondents Chad Bushaw Neutrals Jill M. Zacha John Kenneth Popham Charles McGarry Hearing Site Dallas, TX Award Document 24-00310.pdf Documentum DocID 16df0aa4 Award Date Official Fri, 10/02/2026 – 12:00 Related Content Off Claimant […]
26-00385.pdf
26-00385.pdf Anonymous (not verified) Fri, 10/02/2026 – 16:25 Case ID 26-00385 Forum FINRA Document Type Award Claimants Wells Fargo Clearing Services, LLC Respondents Anne Satterfield Neutrals Langfred W. White Hearing Site Raleigh, NC Award Document 26-00385.pdf Documentum DocID ee2ec911 Award Date Official Fri, 10/02/2026 – 12:00 Related Content Off Claimant Representatives John Wesley Holston Respondent […]
25-02404.pdf
25-02404.pdf Anonymous (not verified) Fri, 10/02/2026 – 16:15 Case ID 25-02404 Forum FINRA Document Type Award Claimants Joel Angeles Respondents Fidelity Brokerage Services LLC Neutrals Mary Mackey Hearing Site San Francisco, CA Award Document 25-02404.pdf Documentum DocID 806cc3b7 Award Date Official Fri, 10/02/2026 – 12:00 Related Content Off Claimant Representatives Joel P. Angeles Respondent Representatives […]
Who should own analytics: IT, the business or both?
Clients ask me this question perhaps more than any other. They’ve usually just come off a bad experience, either analytics stuck in IT’s backlog for months or analytics scattered across the business without anyone accountable for what it all means. My answer is always the same. Split it. IT owns the data engineering. The business […]
Who should own AI? I started with an incomplete answer
Several months ago, I was invited to an event for CTOs. Just looking around the room, I could see someone had made an assumption about my title. I am a chief transformation officer, not a chief technology officer. I stayed anyway to see how the other type of CTO thinks about AI. When a CISO […]
$6T in annual AI revenue needed to pay off data center investments
Hyperscalers are rushing to build more data centers to run AI workloads — but will the AI industry ever generate enough revenue to pay for that infrastructure? Researchers at Bain and Company have looked into this and concluded that productivity gains from existing AI services are not enough to justify the money being pumped in: […]
AI could boost software engineer productivity by 32.6%
Tools such as Anthropic Claude Code or OpenAI Codex have changed the face of software development, and all the signs are that this investment is set to increase further. But is paying a monthly subscription (and perhaps additional usage fees) cost-effective? Will the increasing level of investment in AI-generated software prove to be worthwhile? That’s […]
Omnissa delivers a peek into the benefits of breaking through enterprise data silos
When Omnissa this week rolled out a new AI governance authority product, Elara, in beta, it delivered a glimpse into the potential of having visibility between the typical enterprise’s data silos, whether they’re in lines of business, disparate geographies, or corporate operational units. “By connecting signals across systems that often operate independently, Elara gives IT […]
A human rubber stamp on AI-based HR decisions won’t satisfy California’s No Robo Bosses law
California is setting a precedent for AI use in scenarios where workers’ jobs are at stake. Governor Gavin Newsom this week signed the No Robo Bosses Act (SB 947), which bans employers from relying solely on AI-powered automated decision-making systems (ADS), also known as “bossware,” to discipline or terminate workers. Introduced by Senator Jerry McNerney, […]
Microsoft, Google back Apache Ossie to make enterprise data and AI platforms more interoperable
Microsoft and Google are joining a project to create an open specification for exchanging semantic models across data, analytics, and AI platforms. The project already has the backing of over 60 companies including Databricks, Informatica, Mistral AI, Nvidia, Oracle, Salesforce, and Snowflake. Their support for Ossie makes it a little more likely that future analytics […]
GitLab Patches Critical 9.9 AI Gateway Flaw Allowing Command Execution on Self-Hosted Servers
A critical flaw in GitLab’s AI Gateway could let a logged-in user with Duo Agent Platform access run commands on the gateway under certain conditions, GitLab said in an advisory. The gateway is the service that connects a GitLab instance to AI models, and only organizations that host their own gateway need to act. The flaw […]
Antino Backdoor Uses Outlook and OneDrive for C2 in China-Nexus Espionage Campaign
Government and policy organizations across Asia have become the target of a new campaign orchestrated by a China-nexus threat actor. The activity, which has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamed Antino. Cisco Talos is tracking the cluster
Dell CSM Flaws Enable Unauthenticated Admin Access and Root on Kubernetes Nodes
Dell has released security updates to address multiple critical security flaws in Dell Container Storage Modules (CSM) that could be exploited by bad actors to take over susceptible systems. The vulnerabilities are listed below – CVE-2026-63688 (CVSS score: 10.0) – A missing authentication for critical function vulnerability in the csm-authorization-storage gRPC server that an
City of Vicksburg, Mississippi, shuts down computers after cyberattack
Joseph Topping reports: The City of Vicksburg, Mississippi, has shut down its computer systems after a ransomware attack, potentially delaying in-person utility payments while emergency response and utility service continue. Mayor Willis Thompson told The Vicksburg Post that the city had disconnected its internet operations. “We had to bring our internet operations down, just for… […]
OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling
OpenAI has parted ways with three members of its safety team after they leaked private information in violation of company policies, The Wall Street Journal reported. “We have parted ways with three individuals for violating our policies on accessing and handling sensitive company information,” a spokesperson for the company was quoted as saying. “Our investigation […]
CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-102489 Zammad GmbH Zammad Session Fixation Vulnerability CVE-2026-102490 Zammad GmbH Zammad Improper Privilege Management Vulnerability These types of vulnerabilities are frequent attack vectors for malicious cyber actors and pose significant risks to the federal enterprise. Binding […]
Why CISOs Struggle to Answer the Board's Three Hardest Questions, and How to Fix the Report
The quarterly board meeting is two weeks out. The security team is pulling exports from the identity provider, the cloud posture tool, the vulnerability scanner, the SIEM and the EDR console. Someone is building a spreadsheet to reconcile them. Someone else is turning that spreadsheet into slides. Then a board member asks three questions: How […]
Warlock Expands SharePoint Exploitation in Critical Infrastructure Attacks
The China-based hacking group has been exploiting SharePoint vulnerabilities since July 2025. The post Warlock Expands SharePoint Exploitation in Critical Infrastructure Attacks appeared first on SecurityWeek.
AI Agents Aimed SQL Injection at US and Canadian Government Sites
The attacks targeted the US Department of Education and Library and Archives Canada, and researchers linked some agents to OpenAI. The post AI Agents Aimed SQL Injection at US and Canadian Government Sites appeared first on SecurityWeek.
Exploited Fortinet FortiMail Zero-Day Calls for Urgent Action
CVE-2026-104286 is a critical-severity path traversal vulnerability that could allow attackers to write arbitrary files to the system. The post Exploited Fortinet FortiMail Zero-Day Calls for Urgent Action appeared first on SecurityWeek.
Zero Trust Creator Says Model Holds Firm Against AI-Assisted Attacks
Fifteen years after coining the framework, John Kindervag insists zero trust still works in the AI era—if you get the implementation right. The post Zero Trust Creator Says Model Holds Firm Against AI-Assisted Attacks appeared first on SecurityWeek.
Osavul Lands $10 Million to Spot Hostile Intent Across Cyber, Physical Domains
Hybrid risk intelligence company Osavul has raised $10 million in a Series A funding round led by 33N Ventures. The post Osavul Lands $10 Million to Spot Hostile Intent Across Cyber, Physical Domains appeared first on SecurityWeek.
Hacker Conversations: Rob Juncker, a Knock at the Door and a Moral Compass
Rob Juncker is chief product and technology officer at Mimecast. Is he a hacker? “Unequivocally yes,” he says. The post Hacker Conversations: Rob Juncker, a Knock at the Door and a Moral Compass appeared first on SecurityWeek.
Enterprises Struggle to Prepare for AI and Quantum Threats, PwC Says
PwC’s survey found that only 22% of leaders would use fully autonomous AI for cyber defense, while just 21% are implementing quantum-resistant security measures. The post Enterprises Struggle to Prepare for AI and Quantum Threats, PwC Says appeared first on SecurityWeek.
Police Shut Down KillSec Ransomware, Identify Alleged Teen Leader
Police took control of KillSec’s leak site and secured at least 110 terabytes of data stolen from victims. The post Police Shut Down KillSec Ransomware, Identify Alleged Teen Leader appeared first on SecurityWeek.
AI Has Changed Attack Speed, Not Security Fundamentals
As AI accelerates vulnerability discovery and exploitation, so-called virtual patching still comes down to defense-in-depth and strong application security fundamentals. The post AI Has Changed Attack Speed, Not Security Fundamentals appeared first on SecurityWeek.
Zimbra Vulnerability Exploited in the Wild Prior to Public Disclosure
Under certain conditions, CVE-2026-73570 can be exploited via specially crafted emails without user interaction. The post Zimbra Vulnerability Exploited in the Wild Prior to Public Disclosure appeared first on SecurityWeek.
Rolling the cyber dice with open-source and open-weight AI models
With typical cybersecurity exposure, I can conduct pen testing with deterministic tools. I am able to predict how a piece of software is going to respond. I even stand a decent chance of finding vulnerabilities before they can be exploited against me. What we are dealing with now is a new kind of exposure. For […]
EU Cyber Resilience Act ‘completely kills’ manual vulnerability triage
Independent security experts see the EU Cyber Resilience Act (CRA) reshaping international technology markets to emphasize cyber resilience from the ground up, thereby testing the operational capacities of technology vendors whose wares compete in those markets. The EU CRA introduces mandatory reporting within 24 hours for any actively exploited vulnerabilities or severe incidents affecting products […]
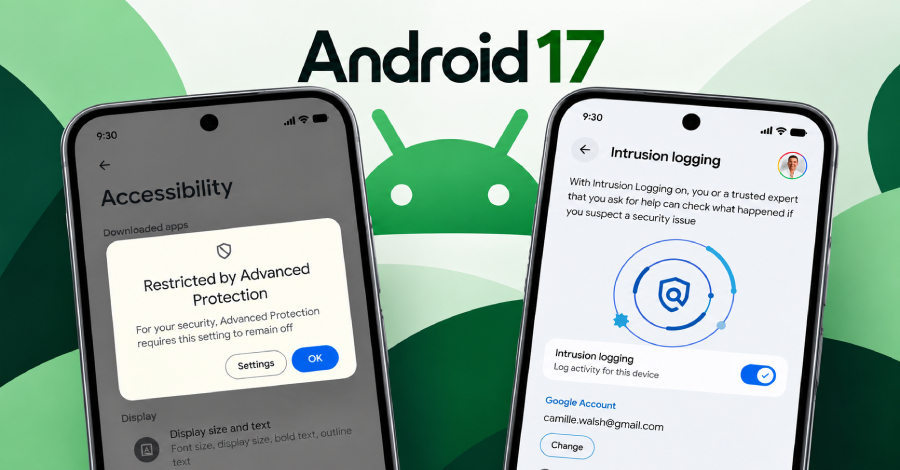
Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools
Google has announced a new security measure that limits access to Android’s accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android applications abusing the API serving as the main conduit for malware and financial fraud, the tech giant said the move would block a major attack pathway. […]
Critical FortiMail Zero-Day Flaw Exploited in Attacks Allows Unauthenticated Arbitrary File Writes
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added a critical security flaw impacting Fortinet FortiMail to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability, tracked as CVE-2026-104286 (CVSS score: 9.8), allows unauthenticated attackers to write arbitrary files on the underlying system. “An improper
ISC Stormcast For Friday, October 2nd, 2026 https://isc.sans.edu/podcastdetail/10120, (Fri, Oct 2nd)
Post Content
2025087193401 Joel A Benanti CRD 4210681 OHO Decision df.pdf
2025087193401 Joel A Benanti CRD 4210681 OHO Decision df.pdf Anonymous (not verified) Thu, 10/01/2026 – 18:35 Case ID 2025087193401 Document Number f4735b07 Document Type OHO Decisions Individuals Joel A Benanti Action Date Wed, 09/23/2026 – 12:00 Related Content On Attachment 2025087193401 Joel A Benanti CRD 4210681 OHO Decision df.pdf Individual CRD 4210681
25-01613.pdf
25-01613.pdf Anonymous (not verified) Thu, 10/01/2026 – 16:35 Case ID 25-01613 Forum FINRA Document Type Award Claimants Frank Mastropaolo Respondents Fidelity Brokerage Services LLC Neutrals Sandra J. Mullings Ann Judith Gellis Edmund Timothy Donovan Hearing Site New York, NY Award Document 25-01613.pdf Documentum DocID 15b1b3da Award Date Official Thu, 10/01/2026 – 12:00 Related Content Off […]
Alexander Cohen Comment On Regulatory Notice 26-15
Alexander Cohen Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 16:15 Alexander Cohen Alex Cohen <alexander.ross.cohen@gmail.com> Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File Alexander Cohen_26-15_10.1.2026.pdf
Anonymous Comment On Regulatory Notice 26-15
Anonymous Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 16:11 Anonymous Counter Culture <bryanmosley1@gmail.com> Regulatory Notice 26-15 Core Official Date Tue, 09/29/2026 – 12:00 Comment File Anonymous_cc_26-15_9.29.2026.pdf
Bloomberg Comment On Regulatory Notice 26-15
Bloomberg Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 16:06 Gregory Babyak Gary Stone (BLOOMBERG/ 731 LEX) <gstone2@bloomberg.net> Bloomberg Regulatory Notice 26-15 Core Official Date Tue, 09/29/2026 – 12:00 Comment File Bloomberg_Gregory Babyak_26-15_9.29.2026.pdf
Teenagers suspected of leading KillSec ransom group arrested during international operation
DataBreaches has reported on a group known as KillSec for almost two years. This time, we get to report on their arrest. The European Union Agency for Criminal Justice Cooperation issued this press release today: An international group of authorities from nine countries, coordinated by Eurojust and Europol, has successfully shut down a ransomware group… […]
Memory squeeze set to tighten through 2028, Micron says
The global memory shortage that has driven up the cost of servers, storage and PCs through 2026 will get worse in 2027 and 2028, according to memory maker Micron Technology. “We expect memory and storage supply-demand conditions to be much tighter in calendar 2027 and 2028 than they were in 2026,” CEO Sanjay Mehrotra said […]
ServiceNow launches standalone AI service desk to provide support in Teams, Slack, and email
ServiceNow has a new take on the service desk: Flow by ServiceNow, a standalone AI product that allows users to get help via chats in Microsoft Teams, Slack, or a Flow web app, or by email, rather than having to leave what they’re doing to open a helpdesk ticket. Flow can be up and running […]
AI and the impending third technology talent drought
Every technology professional working today owes their career, in part, to someone who took a chance on them. The software engineers, cybersecurity analysts and infrastructure specialists on our teams didn’t arrive fully formed and ready to perform. Someone hired them, trained them and gave them room to grow. That’s worth remembering now, because the tech […]
Modernization without disruption: Rethinking the rip-and-replace mindset
I’ve seen organizations reach a point in a modernization program where the technology itself is no longer the biggest risk. A decision was made for a full rip-and-replace. The new environment is ready. The migration plan has been tested. The business case has been approved. But the team responsible for delivering it is also responsible […]
Where AI agents are showing real IT savings
Many IT leaders still struggle to find ROI when deploying AI agents at scale, but a few IT sweet spots are emerging as use cases that can provide CIOs tangible cost relief. Rhonda Baldwin, CIO at LaunchDarkly, says coding agents and service desk agents are helping the SaaS provider cut IT costs. “Coding agents increase […]
AI won’t replace CIOs. It will expose the ones who can’t lead people
In one stretch last year, several executives at the same level in one organization each told me, separately, that the hardest part of their job was talking candidly to each other. Each had spent 15 to 25 years in technology, and none of them was struggling with the technology. I’ve coached more than 1,000 technology […]
What separates true enterprise leaders from strong tech execs
New technology executives often discover the skills that made them successful early in their careers can be the very things that limit their success as a CIO, particularly as the scope, complexity, and expectations of the role expand. Few leaders understand that evolution better than AlTi Global CTO Phil Dundas, my recent guest on the […]
Building an enterprise AI benchmark changed how I evaluate AI
I spent the early part of my career building database systems, managing Oracle’s storage engine group and later helping build Aster Data. That work taught me to watch the gap between benchmark results and production behavior. When the Transaction Processing Performance Council (TPC) was formed in 1988, it was because vendors, customers and researchers lacked […]
OpenAI bets enterprises are ready to delegate real work to autonomous agents
OpenAI says true agentic AI has finally arrived, pushing beyond the trivial capabilities of early-stage virtual assistants. This week at OpenAI Dev Day, the company introduced Dots, which CEO Sam Altman described as “remarkably capable, always-on” agents powered by GPT‑6 Astra. Dots have their own cloud computer, can be accessed in ChatGPT, Slack, or Teams, […]
CIO 100 Leadership Live Boston: Agentic AI pushes CIOs toward continuous enterprise reinvention
BOSTON — Business leaders are looking beyond a single-minded focus on artificial intelligence and the returns generated by individual agents as they confront the broader challenge of continuously reinventing their organizations around what emerging technologies make possible. This shifting mindset emerged during CIO 100 Leadership Live Boston, where discussions began with the human dimensions of […]
Police Arrest 16-Year-Old Suspected of Running KillSec, Seize Ransomware Leak Site and Servers
Police in Spain have arrested a 16-year-old whom investigators suspect of running the KillSec ransomware group. KillSec is accused of stealing data from organizations and threatening to publish it on its leak site unless they paid. The 16-year-old was one of 3 people arrested on September 30, when police also took control of that site. […]
ThreatsDay: AI-Powered Zero-Day Chain, 543K Live Secrets, Model Inspection RCE and 13 More Stories
This week, the useful words are boring ones: inspect, cache, compile, store, trust. Each sounds harmless. Each can become an attack path when a system does a little more than people expect. A model check can run code. A cache can mix up requests. A public secret can stay useful for years. That is the […]
‘A treasure trove of information:’ Cybersecurity specialist says sensitive McMinnville records exposed online
KOIN in Oregon reports: Three clicks. That’s all Chuck Dornon said it took to reach private McMinnville records that should never have been public on the dark web. “Anything and everything that the city’s done is out there,” Dornon said. “This is probably the easiest form of information I’ve come across in a breach.” The… […]
WordPress Backdoor Rebuilds Itself After Cleanup Using Files, Database, and Shared Memory
Cybersecurity researchers have shed light on a WordPress compromise in which threat actors deployed multiple persistence mechanisms to ensure that the final payload kept returning without having to infect the site again. The backdoor has been codenamed SC after the “SC_” markers present in the injected content. Sucuri has described the malware as a “self-healing […]
Google makes Gemini 4 AI model available to a trusted few
Google has unveiled a new frontier AI model after months of delay. Gemini 4 Argon is designed to handle complex, long-horizon workloads spanning software engineering, enterprise knowledge work such as legal and financial analysis, and cybersecurity. But only a few organizations can get their hands on it for now. Argon is “rolling out to a […]
Cisco SD-WAN Manager hit by zero-day admin access attack
Cisco’s SD-WAN management software has been letting some attackers walk through an authentication check without having to prove who they are. The company says it has now fixed the flaw that was allowing it. The affected platform, Cisco Catalyst SD-WAN Manager, is used to configure and operate software-defined network deployments. Cisco said in an advisory […]
Armatura LLC Armatura One
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to gain unauthorized access to the database, execute arbitrary code on the host with the highest level of privilege, or gain control of the physical access-control system. The following versions of Armatura LLC Armatura One are affected: Armatura One <4.7.2 (CVE-2023-46604, CVE-2026-94591, CVE-2026-94592, […]
Meari IoT Cloud Platform OpenAPI Service
View CSAF Summary Successful exploitation of these vulnerabilities could allow attackers to manipulate device configurations, trigger unauthorized behaviors, and access sensitive information such as device credentials, owner details, and network data without proper authorization. The following versions of Meari IoT Cloud Platform OpenAPI Service are affected: IoT Cloud Platform OpenAPI Service vers:all/* (CVE-2026-101104, CVE-2026-96613) CVSS […]
Monta monta.app
View CSAF Summary Successful exploitation of these vulnerabilities could enable attackers to gain unauthorized administrative control over vulnerable charging stations or disrupt charging services through denial-of-service attacks. The following versions of Monta monta.app are affected: monta.app vers:all/* (CVE-2026-95102, CVE-2026-97363, CVE-2026-97212, CVE-2026-93474) CVSS Vendor Equipment Vulnerabilities v3 9.4 Monta Monta monta.app Missing Authentication for Critical Function, […]
Johnson Controls EasyIO Neo Series EC and CW Controllers
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to gain access to sensitive information that could be used to conduct further attacks against the system. The following versions of Johnson Controls EasyIO Neo Series EC and CW Controllers are affected: EasyIO Neo Series EC Controllers V3.3b63 (CVE-2026-64892) EasyIO Neo Series EC […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-104286 Fortinet FortiMail Path Traversal Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based […]
ABB Protection and Control IED Manager PCM600
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to escalate privileges or overwrite files. The following versions of ABB Protection and Control IED Manager PCM600 are affected: Protection and Control IED Manager PCM600 <=2.14 (CVE-2026-15952, CVE-2026-15953) CVSS Vendor Equipment Vulnerabilities v3 6.4 ABB ABB Protection and Control IED Manager PCM600 Incorrect […]
Johnson Controls EasyIO Neo Series EC and CW Controllers
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker tointercept and read sensitive information, including credentials andsession data. The following versions of Johnson Controls EasyIO Neo Series EC and CW Controllers are affected: EasyIO Neo Series EC Controllers V3.3b62 (CVE-2026-64893) EasyIO Neo Series EC Controllers V3.3b63 (CVE-2026-64893) EasyIO Neo Series CW Controllers […]
CISA Malcolm
View CSAF Summary The following versions of CISA Malcolm are affected: Malcolm CVSS Vendor Equipment Vulnerabilities v3 8.8 CISA CISA Malcolm Improper Neutralization of Input During Web Page Generation (‘Cross-site Scripting’), Improper Neutralization of Special Elements used in an OS Command (‘OS Command Injection’), Improper Limitation of a Pathname to a Restricted Directory (‘Path Traversal’), […]
Suspected State Hackers Exploited Citrix NetScaler for Weeks. 50,000 Devices May Still Be Exposed.
Datawater reports: Two critical NetScaler zero-days, CVE-2026-88771 and CVE-2026-88772, were used against organizations worldwide before a patch existed. CISA’s deadline is today. Patching alone will not tell you whether you were already breached. Threat level: Critical What: Two unauthenticated remote-code-execution flaws in Citrix NetScaler ADC and NetScaler Gateway, both CVSS 9.5. Status: Exploited as zero-days…. […]
How Financial Services Companies Can Modernize Their Software Supply Chain
Every security leader at a bank, insurer, or asset manager has had a version of this conversation: Security wants to eliminate a class of vulnerabilities. Engineering explains what it would take to upgrade the platform where they live. Somebody prices out the regression testing. Somebody else raises the change-freeze calendar. The finding gets an exception, […]
Zammad Zero-Days Exploited in AI-Powered DIVD Hack
The flaws were chained to hijack sessions, achieve remote code execution, and elevate privileges to root. The post Zammad Zero-Days Exploited in AI-Powered DIVD Hack appeared first on SecurityWeek.
500,000 Active Credentials Left Exposed on GitHub
Roughly 200,000 of the credentials were exposed after GitHub enabled push protections by default. The post 500,000 Active Credentials Left Exposed on GitHub appeared first on SecurityWeek.
Cisco Patches Exploited Catalyst SD-WAN Zero-Day Vulnerability
The flaw could allow remote, unauthenticated attackers to access vulnerable appliances with administrative privileges. The post Cisco Patches Exploited Catalyst SD-WAN Zero-Day Vulnerability appeared first on SecurityWeek.
Google Launches Gemini 4 Argon With Guardrail-Free Access for Vetted Defenders
The company says its new frontier AI model found a critical vulnerability in software used by hospitals worldwide. The post Google Launches Gemini 4 Argon With Guardrail-Free Access for Vetted Defenders appeared first on SecurityWeek.
FTC is Investigating OpenAI and Anthropic Over Possible Risks to Consumers
An FTC spokesperson confirmed the investigation but declined further comment. The post FTC is Investigating OpenAI and Anthropic Over Possible Risks to Consumers appeared first on SecurityWeek.
Google: AI Is Changing the Pace and Profile of Vulnerability Discovery
Google’s analysis found that AI-discovered vulnerabilities are more likely to enable remote code execution. The post Google: AI Is Changing the Pace and Profile of Vulnerability Discovery appeared first on SecurityWeek.
WatchGuard Patches Critical Fireware OS Code Injection Vulnerability
WatchGuard has rolled out patches for 15 code execution, DoS, authorization, and path traversal bugs in Fireware OS. The post WatchGuard Patches Critical Fireware OS Code Injection Vulnerability appeared first on SecurityWeek.
Government, Finance Orgs Targeted in Weeks-Long NetScaler Zero-Day Attacks
Several security firms have confirmed seeing exploitation of the NetScaler vulnerabilities CVE-2026-88771 and CVE-2026-88772. The post Government, Finance Orgs Targeted in Weeks-Long NetScaler Zero-Day Attacks appeared first on SecurityWeek.
Chrome, Firefox Updates Patch Over 100 Vulnerabilities
Some of the flaws could allow remote attackers to execute arbitrary code or escape the browser sandbox. The post Chrome, Firefox Updates Patch Over 100 Vulnerabilities appeared first on SecurityWeek.
Treasury Blacklists Most-Wanted ATM Malware Developer and His Network
The US government continues its crackdown on Tren de Aragua over its ATM jackpotting scheme. The post Treasury Blacklists Most-Wanted ATM Malware Developer and His Network appeared first on SecurityWeek.
Philip Gommers Comment On Regulatory Notice 26-15
Philip Gommers Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 06:45 Philip Gommers Philip Gommers <philipgommers@gmail.com> Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File Philip Gommers_26-15_9.24.2026.pdf
OpenAI Disrupts Reasoning Extraction Campaign Linked to Moonshot AI Associates
OpenAI on Wednesday said it identified and disrupted a coordinated distillation campaign that was designed to illicitly extract protected reasoning from its artificial intelligence (AI) models. A “core cluster of the activity,” going back to the first week of July, has been attributed to individuals associated with Moonshot AI, a Chinese AI company based in […]
E. Lukas Comment On Regulatory Notice 26-15
E. Lukas Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 06:40 E. Lukas Erich Lukas <erich.lukas@hotmail.com> Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File E. Lukas_26-15_9.24.2026_Redacted.pdf
Anonymous Comment On Regulatory Notice 26-15
Anonymous Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 06:37 Anonymous quan19@yahoo.com Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File Anonymous_qn_26-15_9.24.2026_Redacted.pdf
Rick Comment On Regulatory Notice 26-15
Rick Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 06:33 Rick Richard Desjardins <rickdesjardins@me.com> Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File Rick_26-15_9.24.2026_Redacted.pdf
Mike Henslin Comment On Regulatory Notice 26-15
Mike Henslin Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 06:33 Mike Henslin Mike Henslin <mike@groundtechmn.com> Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File Mike Henslin_26-15_9.24.2026.pdf
CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a critical authentication bypass flaw impacting Cisco Catalyst SD-WAN Manager to its Known Exploited Vulnerabilities (KEV), following reports of active exploitation. The vulnerability, tracked as CVE-2026-76504 (CVSS score: 9.8), could allow an unauthenticated, remote attacker to access an affected system with
Why AI agents are like the dog that pushed kids into the Seine
There is an interesting story about a French dog on the banks of the Seine river that helps us understand misbehaving AI agents. The dog is trained to save children from drowning. He succeeds and is rewarded, becoming an overnight sensation. He saves another child a week later. Not long after, someone witnesses the dog […]
Google Rolls Out Gemini 4 Argon to Trusted Cyber Defenders, Plans Guardrail-Free Version
Google on Wednesday announced its latest frontier artificial intelligence (AI) model, Gemini 4 Argon, that it said is being rolled out to a set of trusted cyber defenders through its Fairwind Program. “It delivers frontier performance in complex workflows across real-world software engineering, enterprise knowledge work like legal and finance, and cybersecurity defense,” Koray Kavukcuoglu,
Apple CoreGraphics PoC Emerges as WhatsApp PDF Checks Hint at Possible Delivery Path
Security researchers have published the first public proof-of-concept for CVE-2026-86950, an Apple CoreGraphics flaw Apple says may have been used in attacks against specific targeted individuals. The trigger is a malicious PDF with a crafted embedded font that crashes unpatched iPhones and Macs. The code causes a crash, not an execution error. Turning the memory […]
ScreenConnect Client (Ab)used by Attackers, (Thu, Oct 1st)
Threat Actors do not always use top-notch techniques or very complex malware to perform their attacks. Sometimes, they just abuse of existing applications…
Bitget Confirms Third-Party Zero-Day Behind $387.5 Million Cryptocurrency Theft
Cryptocurrency exchange Bitget on Wednesday confirmed that attackers who stole $387.5 million last week exploited a zero-day flaw in third-party security products, citing ongoing investigation findings from SlowMist. “Their investigation identified malicious activity involving third-party security products, including a zero-day vulnerability, and recovered a customized tool used by the attacker
MetaMask Security Incident Prompts Exit of Affected Ethereum Validators
MetaMask on Thursday said it’s responding to what it described as an “ongoing security incident” impacting part of its infrastructure. “We are actively addressing and remediating the issue internally, in coordination with external partners and security advisors,” the software cryptocurrency wallet maker said. “At this time, we have identified no immediate threat to MetaMask wallets.” […]
Citrix NetScaler Post-Exploitation Payload Creates Superuser, Maps Web Shell to CSS-Like URLs
Threat actors have been observed exploiting a critical pre-authentication command injection vulnerability in Citrix NetScaler ADC and NetScaler Gateway to drop web shells and attempt theft of configuration data. LevelBlue’s Threat Hunt Operations & Research (THOR) team, which analyzed the exploitation activity across multiple customer environments, said it identified malicious NetScaler
ISC Stormcast For Thursday, October 1st, 2026 https://isc.sans.edu/podcastdetail/10118, (Thu, Oct 1st)
Post Content