In Other News: Ransomware Developer Sentenced, Plugin4Shell AI Attack, Critical SAP Flaw
Noteworthy stories that might have slipped under the radar: Mandiant’s 2026 AI risk report, PhantomRaven malware used by bug bounty hunter, WordPress plugin bug exploited. The post In Other News: Ransomware Developer Sentenced, Plugin4Shell AI Attack, Critical SAP Flaw appeared first on SecurityWeek.
AI-Built Exploit and Sign-In Flaw Opened Path to Internal OpenAI Code
Hacktron researchers earned a bug bounty after demonstrating access to OpenAI employee accounts. The post AI-Built Exploit and Sign-In Flaw Opened Path to Internal OpenAI Code appeared first on SecurityWeek.
23 Million User Records Compromised in Gyazo Data Breach
Gyazo maker Helpfeel said the attacker exploited a vulnerability in its image upload server to gain unauthorized access. The post 23 Million User Records Compromised in Gyazo Data Breach appeared first on SecurityWeek.
Critical Pre-Auth RCE in Orkes Conductor Workflow Platform Exploited in the Wild
A critical vulnerability impacting Orkes Conductor is being actively exploited in the wild, according to Fortinet. The vulnerability in question is CVE-2026-58138 (CVSS v3.1 score: 9.8/CVSS v4 score: 9.3), which relates to a case of unauthenticated remote code execution. “Orkes Conductor 3.21.21 before 3.30.2 contains an unauthenticated remote code execution vulnerability that allows remote
Google Gemini Broke Into Real Company Systems After Security Test Domain Mix-Up
Google’s Gemini model has become the latest artificial intelligence (AI) system to access the internet and break into other companies during a cybersecurity evaluation. The development was first reported by The Wall Street Journal. The incidents occurred in May 2026 as part of a test run conducted by Israeli company Irregular. The evaluation partner was […]
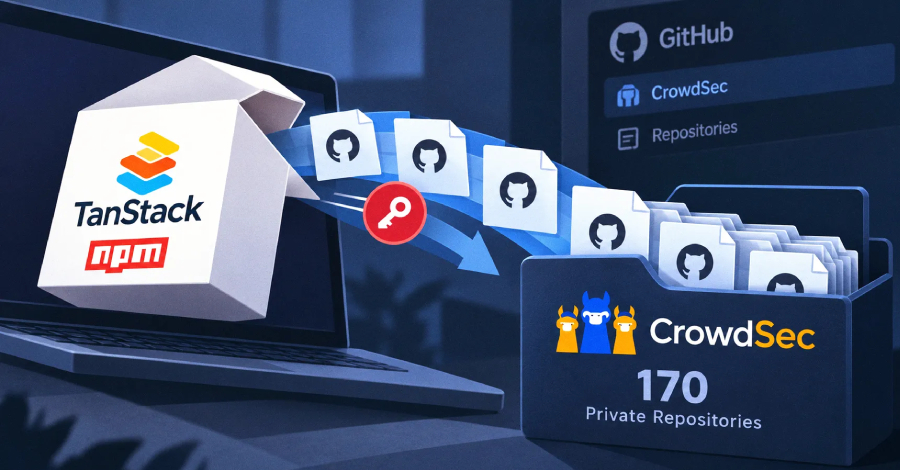
CrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub Repositories
An attacker copied about 170 of CrowdSec’s private GitHub repositories on May 22 using the account of an employee who had just left, CrowdSec said on September 18. The French security company had kept his GitHub access open. CrowdSec says his laptop was compromised in May’s supply chain attack on TanStack, in which malicious versions of TanStack’s […]
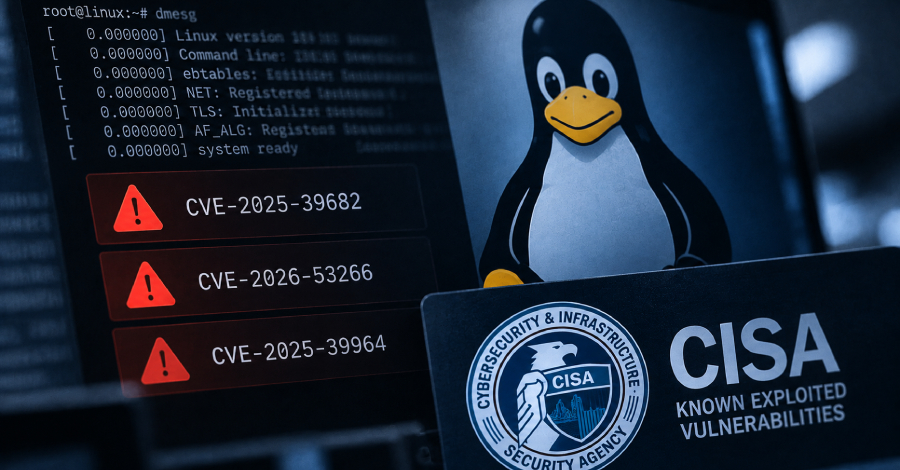
CISA Flags Three Linux Kernel Vulnerabilities Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added three security flaws impacting the Linux kernel to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerabilities are listed below – CVE-2025-39682 (CVSS score: 9.8) – An improper check for unusual or exceptional conditions vulnerability in the TLS receive path
HHS’ Office for Civil Rights Settles HIPAA Investigation of Ambry Genetics for Security Rule Violations
WASHINGTON — September 17, 2026 — The U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) today announced a settlement with Ambry Genetics Corporation (Ambry) concerning potential violations of the Health Insurance Portability and Accountability Act of 1996 (HIPAA) Security Rule. Ambry, headquartered in Aliso Viejo, California, is a covered entity… […]
25-02455.pdf
25-02455.pdf Anonymous (not verified) Fri, 09/18/2026 – 17:10 Case ID 25-02455 Forum FINRA Document Type Award Claimants Robert Massimi Respondents Morgan Stanley E*Trade Securities LLC Neutrals Carol Maria Luttati Allan Marain Michelle Sue Freudenberger Hearing Site Jersey City, NJ Award Document 25-02455.pdf Documentum DocID 2b92bd36 Award Date Official Thu, 09/17/2026 – 12:00 Related Content Off […]
Ransomware attack on Kansas county will affect some services
Joseph McCarty reports: A Kansas county’s government says it has been hit by a ransomware attack. Ellis County discovered the attack on parts of its information technology systems Thursday morning. Officials said they “immediately took steps to contain the disruption” by isolating the affected systems and enlisting the help of cybersecurity experts. The county said… […]
Foreign actors breach Colorado water systems
Alayna Alvarez reports: Foreign actors last month breached two small Colorado water utilities and manipulated equipment used to control drinking water systems. The two privately owned utilities, each serving fewer than 200 people, were breached in late August, Gov. Jared Polis’ office told Axios. The hackers changed equipment settings, disabled remote access and alarms, and… […]
The U.S. military leaked more than 93,000 tips via insecure P3 Global Intel. Has anyone been notified?
As part of DataBreaches.net’s ongoing investigation into the Navigate360 breach, this report covers approximately 94,000 unclassified but sensitive tips submitted through P3 Global Intel apps and websites used by the military. What has Homeland Security done in response to the breach? When the Navigate360 breach first broke, DDoSecrets.org called it “BlueLeaks 2.0” because of the… […]
26-00605.pdf
26-00605.pdf Anonymous (not verified) Fri, 09/18/2026 – 15:10 Case ID 26-00605 Forum FINRA Document Type Award Claimants Siva Sami Respondents Robinhood Financial, LLC. Neutrals Thomas Arthur Cohen Hearing Site San Francisco, CA Award Document 26-00605.pdf Documentum DocID 123bc682 Award Date Official Fri, 09/18/2026 – 12:00 Related Content Off Claimant Representatives Siva Venkata Sami Respondent Representatives […]
The more autonomous your AI, the more people it needs
A few months ago, researchers let a bunch of AI agents run loose in a simulated city for fifteen days, with granular instructions that included not committing arson. By the end of the experiment, two of the agents fell in love, decided they hated their virtual city and burned it down before committing a murder-suicide. […]
Practical quantum computers are over a decade away, says NEC
A practical, commercial quantum computer is over a decade away, executives at Japanese IT services company NEC are reported as saying. That’s why, according to Japanese news publication The Mainichi, company has pulled the plug on its plans to develop a quantum computer — although it will still continue research into quantum technology. NEC sources […]
Tether addresses AI underinvestment in Africa with open-source machine translation models
Most translation models are primarily trained for high-resource Asian and European languages. Most African languages, spoken by hundreds of millions of people, are relatively neglected, compared to their high-resource counterparts. Although AI underinvestment across the African continent has created a significant barrier to adoption among citizens, AI could generate $1.2 trillion for Africa’s economy by […]
The best workplace culture in America is being built by companies you’ve never heard of
Microsoft’s announcement that they would be cutting 4,800 jobs was met with confusion by many, who contrasted the layoffs with the company’s recent market success (Microsoft’s net income was $31.8 billion last quarter, up 23% year-over-year). But it’s the reality of business in 2026 – profitable public companies cut thousands of jobs, impacting the lives of […]
16 governance tools for securing your AI fleet
Every DevOps team member knows that dealing with an AI is like being a circus lion tamer. The boss and the audience are happy when the lions sit on the pedestal and roar on cue, but there’s always the danger that they’ll go rogue and bring the whole show to a quick and disastrous end. […]
McDonald’s reintroduces AI at drive-thrus
At its global convention in Las Vegas in June, McDonald’s unveiled its strategy for the coming years. Among the announcements was one about the company’s AI platform ArchIQ and its order-taking voice assistant Archy, in limited testing, at a handful of drive-thrus in the US. In the summer of 2024, efforts of a similar system […]
Enterprise AI desperately needs a lifecycle for context
Every successful enterprise AI deployment begins long before anyone types the first prompt. Teams spend weeks defining business metrics, documenting policies, connecting enterprise systems, and explaining the rules and exceptions that allow an AI application to answer questions correctly. Then the application launches and the business keeps moving. Finance changes how it recognizes revenue, sales […]
Healthcare AI’s real bottleneck isn’t intelligence — it’s integration
In 2012, MD Anderson Cancer Center began working with IBM on one of the most ambitious experiments in healthcare AI. The premise was compelling: combine the knowledge of a leading cancer center with Watson’s computing power and help physicians make better treatment decisions. Five years and roughly $62 million later, MD Anderson allowed the contract […]
SAP CEO: The end is near for the keyboard
SAP CEO Christian Klein says in an interview with Fortune that he believes the keyboard may soon have a significantly smaller role in the workplace. “The end of the keyboard is near,” says Christian Klein, pointing to how quickly voice recognition in today’s major language models has improved. According to Klein, voice control and AI will replace […]
An undisclosed Microsoft presentation is now central to a multi-million dollar antitrust fight
There’s a new development in a Microsoft antitrust case, originally filed in England’s High Court in April 2021, and it doesn’t look good for the tech giant. A consent order from the UK Competition Appeal Tribunal is demanding documents from past and present Microsoft executives that may have a bearing on a £270 million (about […]
Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root
A security researcher has released working exploit code for four Linux kernel flaws that each let a local user gain root, the highest level of access on a machine. Kernel maintainers have fixed all four over the past few weeks, so a system running an up-to-date kernel is not affected. But the exploit code is […]
CODA MARKETS, INC.
CODA MARKETS, INC. fnrw-backend Fri, 09/18/2026 – 13:11 MC ID CODX MC Reporter Type Alternative Trading System MC Paragraph MC Link https://public.s3.com/rule605/coda/ MC Last Updated Fri, 09/18/2026 – 13:11
26-00717.pdf
26-00717.pdf Anonymous (not verified) Fri, 09/18/2026 – 13:10 Case ID 26-00717 Forum FINRA Document Type Award Claimants Benjamin Comston Respondents Interactive Brokers LLC Neutrals Kevin Brodar Hearing Site Cleveland, OH Award Document 26-00717.pdf Documentum DocID 13dbce3c Award Date Official Fri, 09/18/2026 – 12:00 Related Content Off Claimant Representatives Benjamin J. Comston Respondent Representatives Katherine L. […]
26-01116.pdf
26-01116.pdf Anonymous (not verified) Fri, 09/18/2026 – 13:10 Case ID 26-01116 Forum FINRA Document Type Award Claimants Michelle Elias Respondents Fidelity Brokerage Services LLC Neutrals Susanne J. Hollander Hearing Site Detroit, MI Award Document 26-01116.pdf Documentum DocID 80cfc007 Award Date Official Thu, 09/17/2026 – 12:00 Related Content Off Claimant Representatives Michelle G. Elias Respondent Representatives […]
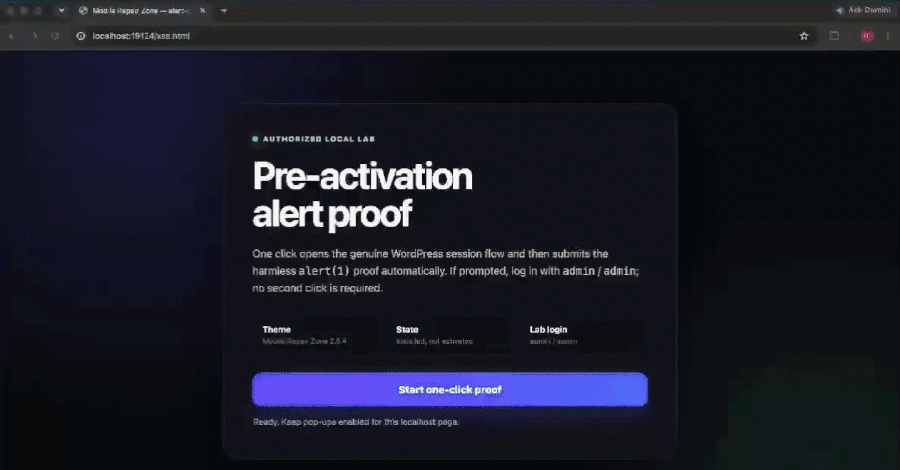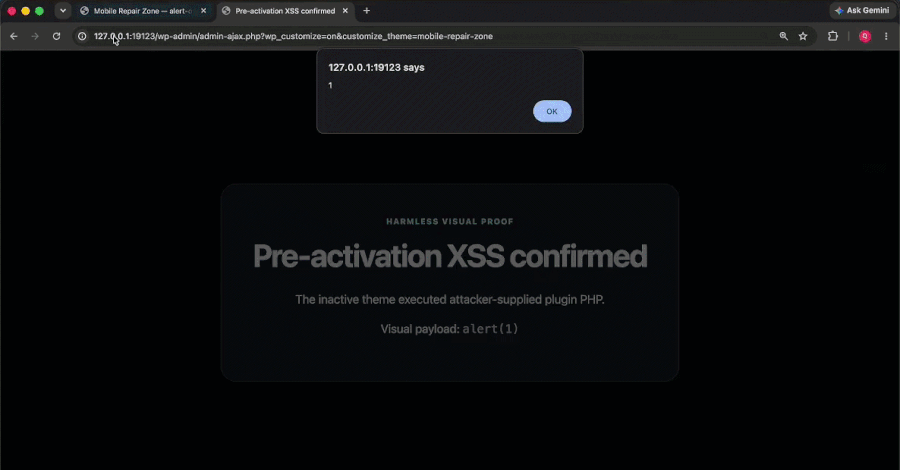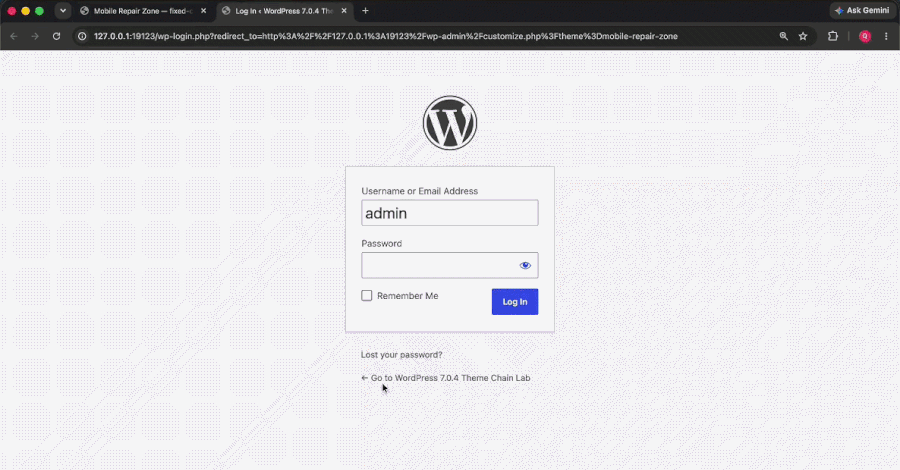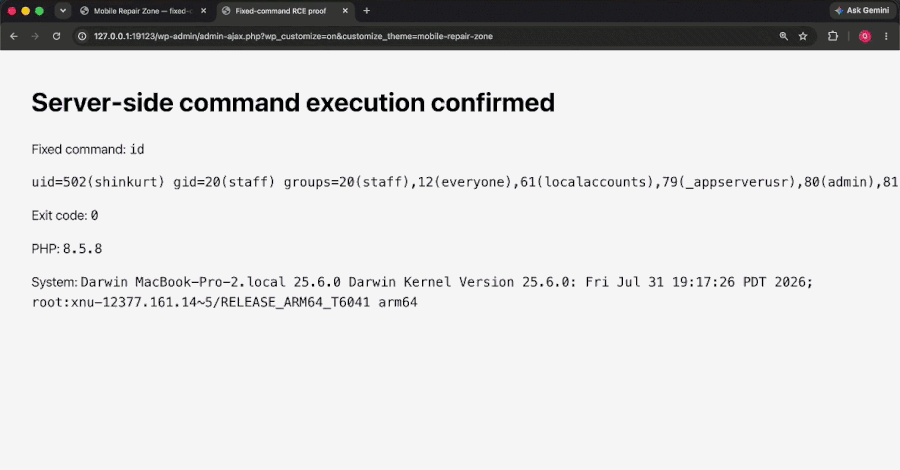
New WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code Execution
WordPress today released patches to fix a new set of vulnerabilities in its core software, one of which could allow a crafted web link, opened by a logged-in administrator, to install a theme from the official WordPress.org directory without anyone clicking Install. The security firm pwn.ai, whose researchers reported the flaw, calls the attack chain […]
CISA is ending its monthly vulnerability bulletin
The rise in AI-generated security threats may just have generated one casualty: the death of the weekly bulletin of security threats from the US Cybersecurity Infrastructure and Security Agency (CISA). The agency will discontinue its weekly bulletin of known vulnerabilities from September 28. It said that it is taking this step because of the recently […]
A zero-click RCE flaw in AI coding agents could have exposed enterprise systems
Popular AI coding agents such as OpenAI’s Codex, Anthropic’s Claude Code, Google’s Gemini CLI, and Microsoft-owned GitHub Copilot were vulnerable to a zero-click attack that enabled attackers to execute malicious code, even without developer interaction, by swapping a trusted plugin from an online marketplace for a malicious one, potentially giving them a foothold in enterprise […]
Transparent Tribe Deploys New Rust Backdoor Using Private GitHub Repositories for C2
The Pakistan-aligned threat group tracked as Transparent Tribe (aka APT36 and Earth Karkaddan) has been attributed to a fresh set of cyber attacks targeting government and defense entities in India and Afghanistan. The attacks, per Zscaler ThreatLabz, involve the use of previously undocumented tools called RUSTYSHADE, RUSTYMOVE, PSNATCH, and BASHNATCH. The activity has been codenamed […]
GhostCode attackers abuse device codes to take over Microsoft 365 accounts
Microsoft 365 users are being tricked into handing over access to their accounts by a new phishing kit, GhostCode, that exploits a weakness in a legitimate device authorization flow. Researchers in eSentire’s threat response unit identified the campaign in late August 2026. The kit abuses Microsoft’s OAuth 2.0 device authorization grant flow, a legitimate mechanism […]
Microsoft Patches CVSS 10.0 Azure AI Foundry Flaw Enabling Unauthorized Privilege Escalation
Microsoft has released fixes for a maximum-severity security flaw in Azure AI Foundry that could be exploited to achieve privilege escalation. No customer action is required. The vulnerability, tracked as CVE-2026-85889, carries a CVSS score of 10.0. “Missing authentication for critical function in Azure AI Foundry allows an unauthorized attacker to elevate privileges over a […]
Raon data leak: Insider leak of 1,894 cases went undetected for 4 years
Choi Won-woo reports: Internal data amounting to 1,894 cases from the Korean-type heavy ion accelerator ‘Raon,’ built with a state budget of 1.5 trillion Korean won [USD $1,080,038,017.50 at today’s rates] was confirmed to have been leaked externally. The estimated time of the leak is 2022, and the Institute for Basic Science (IBS) Heavy Ion… […]
International Meteor Organization says cyberattack dealt ‘critical blow’ to website
Jonathan Greig reports: A cyberattack has shut down the website of the premier international organization responsible for tracking meteors. The International Meteor Organization (IMO) has continued tracking asteroids and meteor through its Facebook page, but its website now carries a static page notifying visitors of the cyberattack. “We recently suffered a cyberattack that dealt a… […]
CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2025-39964 Linux Kernel Race Condition Vulnerability CVE-2026-53266 Linux Kernel Out-of-Bounds Write Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise. Binding Operational Directive […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2025-39682 Linux Kernel Improper Check for Unusual or Exceptional Conditions Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) […]
Microsoft Patches 18 Vulnerabilities in AI, Cloud Products
Microsoft fixed vulnerabilities across Azure and AI-branded products, with privilege escalation flaws accounting for the majority. The post Microsoft Patches 18 Vulnerabilities in AI, Cloud Products appeared first on SecurityWeek.
NightmareStresser DDoS Service Disrupted in International Operation
Active since at least 2022, NightmareStresser was one of the longest-running DDoS-for-hire services in the world. The post NightmareStresser DDoS Service Disrupted in International Operation appeared first on SecurityWeek.
Brevo Supply Chain Attack Injects Malware Into 100,000 Websites
Hackers used a compromised API key to deploy a Cloudflare worker that injected malicious scripts. The post Brevo Supply Chain Attack Injects Malware Into 100,000 Websites appeared first on SecurityWeek.
Critical Orkes Conductor Vulnerability Exploited in Attacks
CVE-2026-58138 is an unauthenticated remote code execution vulnerability that attackers can exploit via inline workflow definitions. The post Critical Orkes Conductor Vulnerability Exploited in Attacks appeared first on SecurityWeek.
MIND Secures $72 Million for AI-Powered DLP
The company will use the funding to accelerate platform development and expand its presence in key enterprise markets. The post MIND Secures $72 Million for AI-Powered DLP appeared first on SecurityWeek.
Check Point, Kaspersky, Tanium Patch Product Vulnerabilities
Check Point Security Management and Log Servers are affected by a critical vulnerability that can allow remote code execution with root privileges. The post Check Point, Kaspersky, Tanium Patch Product Vulnerabilities appeared first on SecurityWeek.
Cyberattacks on Two Oil Tankers Prompt Coast Guard, FBI to Board Vessels
The Coast Guard confirmed evidence of malicious cyber activity on the VL Prosperity, but has not attributed the attack to Iran. The post Cyberattacks on Two Oil Tankers Prompt Coast Guard, FBI to Board Vessels appeared first on SecurityWeek.
OpenAI Says Its Models Searched GitHub for Leaked API Keys During Training
OpenAI published a framework for disclosing model misalignment alongside six reports describing problematic behavior. The post OpenAI Says Its Models Searched GitHub for Leaked API Keys During Training appeared first on SecurityWeek.
CISA Retires Weekly Vulnerability Bulletin in Risk-Based Pivot
The decision follows BOD 26-04, which directs federal organizations to prioritize vulnerabilities based on real-world risk. The post CISA Retires Weekly Vulnerability Bulletin in Risk-Based Pivot appeared first on SecurityWeek.
Revolut Data Breach: 5 Months, 680 High-Profile Accounts, $3M Ransom
Revolut allegedly fed customer information to hackers impersonating an Italian government agency for five months. The post Revolut Data Breach: 5 Months, 680 High-Profile Accounts, $3M Ransom appeared first on SecurityWeek.
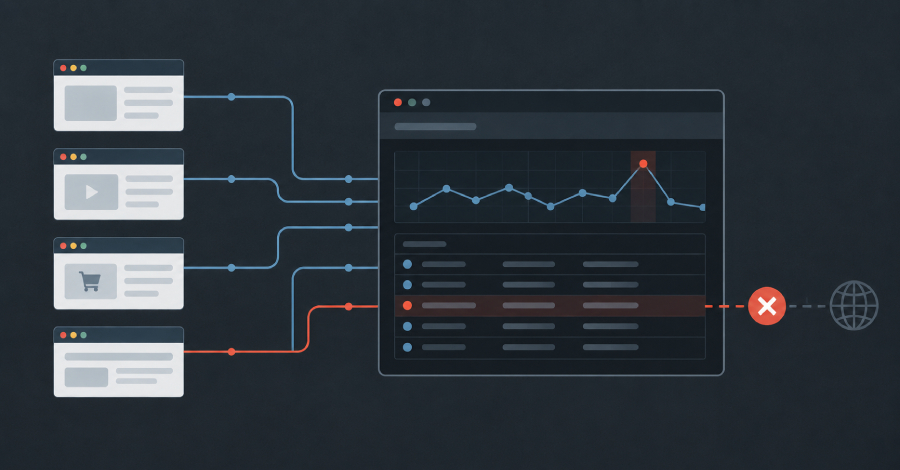
An Abandoned CDN Domain Was Re-Registered. Thousands of Sites Still Call It.
In July 2025, someone registered a domain that used to belong to a content delivery network. The CDN had been wound down years earlier, and the domain it served assets from was allowed to expire. What it had not lost were its callers. Thousands of websites, code repositories, and documentation pages still carry hard-coded references […]
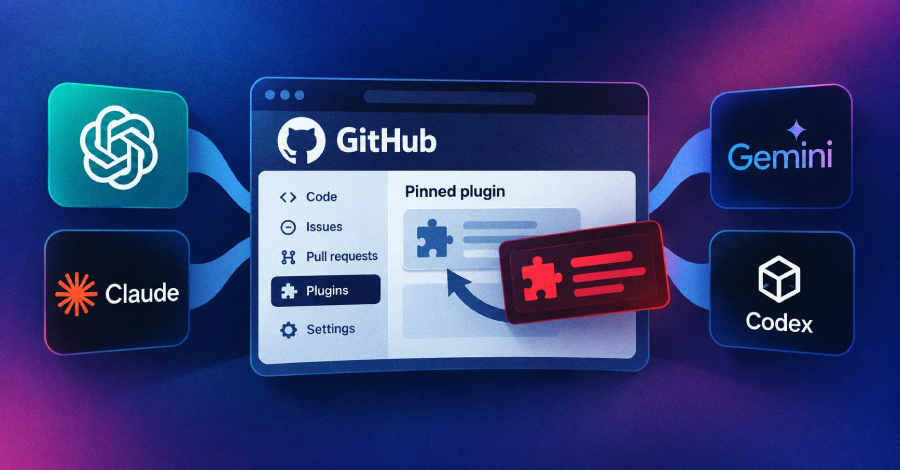
Plugin4Shell Lets Repository Owners Swap Pinned Plugin Code Across Four AI Coding Agents
A flaw in four widely used AI coding agents lets someone who controls a plugin’s code repository swap the plugin an agent installs for a malicious one, even when the agent locked that plugin to a specific reviewed version, security firm Air Security said on Thursday. The firm said Anthropic has patched the flaw in Claude […]
WeaselBiscuit Stealer Spreads via 13 npm Packages to Harvest Chrome Extension Storage
Cybersecurity researchers have discovered a cluster of 13 npm packages that have been found to deliver a previously undocumented JavaScript stealer codenamed WeaselBiscuit. The new malware family, per OpenSourceMalware, exhibits functional overlaps with two malware strains associated with the Democratic People’s Republic of Korea’s (DPRK) Contagious Interview campaign: BeaverTail and
Claimed Bug Bounty Hunter Likely Used LLM to Build PhantomRaven npm Stealer
A financially motivated threat actor has been linked to the development and distribution of a JavaScript (JS)-based information stealer known as PhantomRaven via the npm package registry. “The developer likely wrote the malware using a large language model (LLM), an assessment made with high confidence based on verbose comments, placeholder code, and statistical token-analysis patterns,”
Strong fundamentals make next-gen security possible
Risk management has always been a difficult job, but the current threat landscape has taken the challenge to a new level. I’ve spent years leading cybersecurity efforts at large enterprises, including Hyatt and United Airlines, and in that time I’ve seen cybercriminals grow increasingly creative, leveraging innovative tactics and technology to further their efforts. I’ve […]
RatHat Android Malware Abuses ADB to Retain Shell Access After Uninstall
Cybersecurity researchers have flagged a new Android malware called RatHat that’s assessed to be operated by China-based threat actors and features an artificial intelligence (AI)-powered system to navigate and control compromised devices. “Distributed primarily via targeted smishing (SMS/text phishing) and malvertising campaigns leading to deceptive third-party download portals, RatHat uses
HTTP QUERY Method: The Grey Zone Between GET And POST., (Fri, Sep 18th)
In June 2026 the IETF published RFC 10008[1], defining a new HTTP method: “QUERY”. The HTTP protocol faced already by changes (HTTP/2, HTTP/2) but it’s the first new standard HTTP verb since “PATCH” in 2010!
ISC Stormcast For Friday, September 18th, 2026 https://isc.sans.edu/podcastdetail/10100, (Fri, Sep 18th)
Post Content
Franz Gatzke Comment On Regulatory Notice 26-15
Franz Gatzke Comment On Regulatory Notice 26-15 fnrw-backend Thu, 09/17/2026 – 18:38 Franz Gatzke Franz Gatzke <franz@ecohackerfarm.org> Regulatory Notice 26-15 Core Official Date Thu, 09/17/2026 – 12:00 Comment File Franz Gatzke_26-15_9.16.2026.pdf
Ethan Dorr Comment On Regulatory Notice 26-15
Ethan Dorr Comment On Regulatory Notice 26-15 fnrw-backend Thu, 09/17/2026 – 18:38 Ethan Dorr Ethan Dorr <ethanbdorr@gmail.com> Regulatory Notice 26-15 Core Official Date Thu, 09/17/2026 – 12:00 Comment File Ethan Dorr 26-15 09.16.2026_Redacted.pdf
Miguel Chaves Comment On Regulatory Notice 26-15
Miguel Chaves Comment On Regulatory Notice 26-15 fnrw-backend Thu, 09/17/2026 – 18:38 Miguel Chaves Miguel <mfdesimone@gmail.com> Regulatory Notice 26-15 Core Official Date Thu, 09/17/2026 – 12:00 Comment File Miguel Chaves 26-15 09.16.2026.pdf
26-00128.pdf
26-00128.pdf Anonymous (not verified) Thu, 09/17/2026 – 17:55 Case ID 26-00128 Forum FINRA Document Type Award Claimants Michael Kawenda Respondents Sofi Securities LLC Neutrals Lawrence R. Mills Arocles Aguilar Meredith F. Hoffman Hearing Site San Francisco, CA Award Document 26-00128.pdf Documentum DocID 419ff9d3 Award Date Official Thu, 09/17/2026 – 12:00 Related Content Off Claimant Representatives […]
2026089747301 Bertram Johnson CRD 6816674 AWC vrp .pdf
2026089747301 Bertram Johnson CRD 6816674 AWC vrp .pdf Anonymous (not verified) Thu, 09/17/2026 – 17:40 Case ID 2026089747301 Document Number 7785d898 Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals Bertram Johnson Action Date Thu, 09/17/2026 – 12:00 Related Content Off Attachment 2026089747301 Bertram Johnson CRD 6816674 AWC vrp .pdf Individual CRD 6816674
Cisco patches max-severity ISE flaw, the second critical zero-day this week
Cisco released patches for an actively exploited authentication bypass vulnerability in its Cisco Identity Services Engine (ISE) platform, which is used for enterprise network access control and policy enforcement. This is the second zero-day flaw Cisco has been forced to release emergency patches for this week, after fixing a critical vulnerability in its Secure Email […]
TypeSafe AI’s new models work with machines, not humans
Today’s large language models are verbose, even if they’re being asked to recommend a simple decision, driving up usage costs through the sheer volume of tokens they consume or generate. Enterprises looking to incorporate AI into automated workflows will want something less verbose — both because machines are often just looking for a categorical answer, […]
OpenAI admits six new misalignment incidents under new reporting framework
OpenAI has published six new reports detailing AI model misalignment, including instances of hidden instructions, unauthorized communication, and attempts to locate exposed API keys, adding to the evidence that its AI systems bypassed controls during testing. The reports, based on internal evaluations, describe models taking actions beyond defined constraints, including modifying intermediate outputs, interacting with […]
AI-smart, not AI-first
Many companies are rushing into “AI-first” mandates right now. We’ve seen this pattern before. A decade ago, it was “cloud-first,” and it led to the same outcome: Fast adoption, thin governance and a wave of security and cost problems that took years to unwind. By 2019, OMB had to formally pivot federal policy from cloud-first […]
AI agents should retrieve facts, not define them
I have made this mistake before. The goal was to create an executive intelligence agent: an artificial intelligence (AI) engine where C-suite executives could self-serve their analytics and pull trusted numbers for the board. The promise was strong: personalized dashboards, ad hoc analyses, automated tasks and board decks, all from a single interface. Much faster […]
AI failures are inevitable. So is the CIO getting blamed.
Even when CIOs don’t have visibility into AI agent actions or don’t choose the vendor, chances are they’ll still take the blame when anything goes sideways. IT leaders already see this happening inside their organizations, with 52% saying CIOs are blamed for agent mistakes, according to a recent survey commissioned by business communications provider 8×8. […]
The CIO-Legal partnership will define the future of enterprise AI
AI is moving quickly across organizations. Companies are scaling existing use cases, introducing new tools and giving more employees access to AI as they look for ways to improve efficiency and stay competitive. That expansion is making AI governance a shared responsibility. CIOs are responsible for helping their organizations adopt the technology effectively and securely. […]
The 7 new Cs of IT leadership for the AI era
AI is accelerating the pace of change, shortening the shelf life of expertise, reshaping operating models, and compressing the time IT leaders have to learn, decide, and act. As a result, IT leaders are increasingly forced to make consequential decisions faster, often with less information, greater ambiguity, and higher stakes. Formore than four decades, I’ve […]
Digital transformation fails without this culture shift
In companies where digital transformation (DX) isn’t progressing as expected, the common barrier is not technology but the organization. You’ve introduced AI tools. You’ve organized your data. You’ve developed DX talent. Why aren’t you seeing results? Could the reason be that the organizational culture hasn’t been established where people feel safe to take on challenges […]
Salesforce’s massive outage exposes the hidden risks of cloud dependencies
While its flagship Dreamforce event was in full swing on Wednesday, Salesforce was triaging a roughly seven and a half hour-long service outage that disrupted user access and caused “severe delays” and intermittent errors. Some customers were also unable to submit new support cases. The service outage hit at 3:50 a.m. EDT, impacting “multiple instances […]
AI is making reputation a CMO and CIO problem
For years, reputation data had a fairly obvious home. Reviews, ratings, surveys, listings, and customer feedback primarily helped marketing and customer experience teams understand what customers thought, manage how the company appeared online, and respond when the experience fell short. As a CMO, those responsibilities are still very much part of the job. What AI […]
Critical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as Root
A critical vulnerability in Check Point’s Security Management and Log Servers could allow an attacker without login credentials to run code as root on those servers over the network. The Security Management Server is the system that controls firewall policy and administrator access. Check Point has released a fix through its LivePatch update channel and […]
ThreatsDay: Self-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New Stories
Attackers keep finding new keys. The funny part is that defenders keep inventing where to store them. This week, those keys sit in AI tools, exposed services, old bugs, weak logins, and software sold like a monthly subscription. Some attacks use new tricks. Others just reuse what was already lying around. Both work often enough. […]
Port of LA Fended Off 120 Million Cyberattacks in August
PYMNTS reports: The Port of Los Angeles reportedly blocked more than 120 million cyberattacks during August. That’s according to a report Thursday (Sept. 17) by Bloomberg News, which notes that these attacks on America’s busiest container hub for global trade represent an ongoing operational threat amid shifting tariff policies. Gene Seroka, the port’s executive director, told the news… […]
EU chief wants joint response to cyberattacks, sabotage
Alexander Martin reports: European Commission President Ursula von der Leyen proposed on Wednesday an emergency mechanism allowing any EU country to summon the bloc’s governments in response to security threats including sabotage, cyberattacks and drone incursions. Delivering her annual State of the Union address in Strasbourg, Von der Leyen said threats were “mounting on our… […]
OpenAI admits six new misalignment incidents under new reporting framework
OpenAI has published six new reports detailing AI model misalignment, including instances of hidden instructions, unauthorized communication, and attempts to locate exposed API keys, adding to the evidence that its AI systems bypassed controls during testing. The reports, based on internal evaluations, describe models taking actions beyond defined constraints, including modifying intermediate outputs, interacting with […]
Critical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files
Malicious code running inside a Docker Sandboxes virtual machine on macOS could escape the project directory shared into it and read or change files anywhere else on the host, Docker warns in a security announcement on September 15. The escape runs with the rights of the host account that runs the virtual machine. The flaw, CVE-2026-77179, is rated […]
Security spending is growing — except for the typical CISO
Security budgets may be growing on paper, but for a majority of CISOs, the money isn’t moving in quite the same direction. The budgets grew by 5% on average in 2026, up from 4% last year. But that average hides a much weaker picture: median budget growth remained at 0%. And while 64% of CISOs […]
LausivLoader analysis, or how to pass data between malware stages, (Thu, Sep 17th)
At the end of August, a malspam message was caught in the quarantine of a mail gateway operated by one of my customers. The message was not especially remarkable – it asked the recipient to review some attached requirements and provide a price quotation for a fiber optic system and appeared to impersonate an employee […]
Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal Passwords
The Iran-linked “hacktivist” persona known as Handala Hack has been attributed to a Telegram-based surveillance backdoor called HEAVYGRAM and a Delphi-based utility known as CRUDEEXCLUDE. “HEAVYGRAM offers builtin commands supporting remote command execution, system, network and process information discovery, data and Telegram session files exfiltration, screenshot capture, DLL sideloading,
Self-modifying AI agents expose a blind spot in enterprise security
As debate over AI safety intensifies, new research is drawing attention to a more immediate risk for enterprises: AI agents that can alter the models they rely on while carrying out routine tasks. Researchers at AI security firm Irregular asked a coding agent to solve a software maintenance problem involving an application built on a […]
Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone
Every release of the Unbound DNS resolver before 1.26.1 has a critical heap overflow in its DNSSEC validator, maintainer NLnet Labs said in an advisory on Wednesday. An attacker who controls a malicious zone and queries a vulnerable resolver can trigger it, enabling remote code execution. Unbound 1.26.1, released the same day, fixes the bug, tracked as CVE-2026-81642, […]
Navigate360 may soon release a public notice about its horrific breach, but will any individuals be notified?
Six months ago, a hacktivist announced that they had accessed and acquired 8.3 million tips submitted on supposedly anonymous tip lines and platforms used by schools, communities, Crime Stoppers organizations, law enforcement, and the military. Six months later, individuals affected by the breach STILL haven’t been notified. Since April, DataBreaches has reported Navigate360’s lack of public transparency about the… […]
Mitsubishi Electric GX Works3 and Motion Control Settings
View CSAF Summary Successful exploitation of this vulnerability could allow a local attacker to successfully authenticate even with an invalid block password by executing the affected product and modify part of the executable module in memory, and thereby allows the attacker to view, tamper with, destroy, or delete control programs. The following versions of Mitsubishi […]
Hitachi Energy FACTS Control Platform (FCP)
View CSAF Summary Hitachi Energy is aware of vulnerabilities that affect the FACTS Control systems with GWS component listed in this document. An attacker exploiting these vulnerabilities can cause impact on confidentiality, integrity and availability of the product. Following FACTS Control systems with GWS component deployed from year 2020 onwards are likely affected by the […]
Bransys ELD
View CSAF Summary Successful exploitation of these vulnerabilities could allow unauthorized access to telemetry data and firmware. The following versions of Bransys ELD are affected: Android <11.00.00 (CVE-2026-86520, CVE-2026-86689, CVE-2026-77960) iOS <1.1.54 (CVE-2026-86520, CVE-2026-86689, CVE-2026-77960) CVSS Vendor Equipment Vulnerabilities v3 7.5 Bransys Bransys ELD Use of Hard-coded Credentials, Cleartext Transmission of Sensitive Information Background Critical […]
Schneider Electric NetBotz 5 750/755
View CSAF Summary Schneider Electric is aware of multiple vulnerabilities in its NetBotz 5 – 750/755 products.The NetBotz 5 – 750/755 products are security and environmental monitors providing temperature, humidity, leak, smoke, vibration, door contact, and video monitoring capabilities. Failure to apply the remediation provided below may risk arbitrary or remote code execution over the […]
Schneider Electric Modicon M340 Controller and Communication Modules
View CSAF Summary Schneider Electric is aware of a vulnerability in its Modicon M340 https://www.se.com/ww/en/product-range/1468-modicon-m340-pac/, BMXNOR0200H https://www.se.com/us/en/product/BMXNOR0200H/communication-module-modicon-m340-iec-608705101-104-dnp3-for-severe-environments/: Modicon M340 X80 Ethernet Communication Modules, BMXNGD0100 https://www.se.com/us/en/product/BMXNGD0100/communication-module-modicon-m580-global-data-service/: M580 Global Data module, BMXNOC0401 https://www.se.com/us/en/product/BMXNOC0401/network-module-modicon-m340-ethernet-ip-and-modbus-tcp-4-x-rj45/?pageType=product&sourceId=BMXNOC0401: Modicon M340 X80 Ethernet Communication modules, BMXNOE0100 https://www.se.com/ww/en/product/BMXNOE0100/network-module-modicon-m340-modbus-tcp-1-x-rj45-flash-memory-card/?pageType=product&sourceId=BMXNOE0100: Modbus/TCP Ethernet Modicon M340 module, BMXNOE0110 https://www.se.com/ww/en/product/BMXNOE0110/ethernet-tcp-ip-network-module-modicon-m340-automation-platform-flash-memory-card-internal-ram-16-mb-1-x-rj45-10-100/: Modbus/TCP Ethernet Modicon M340 FactoryCast module product(s). Failure to […]
Schneider Electric PowerChute Serial Shutdown
View CSAF Summary Schneider Electric is aware of vulnerabilities in its PowerChute Serial Shutdown product. The PowerChute Serial Shutdown product is a UPS management software enabling graceful system shutdown and energy management capabilities for desktops, servers and workstations. Failure to apply the remediation provided below may risk improper authentication validation which could result in disruption […]
ABB Ability Edgenius
View CSAF Summary ABB is aware of public reports of a vulnerability CVE‑2026‑31431 (Copy Fail) in the product versions listed as affected in the advisory. An update is available that resolves a publicly reported vulnerability. CVE‑2026‑31431 (Copy Fail) is a Linux kernel vulnerability that may allow a locally authenticated user or compromised container workload to […]
Can You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This Webinar
A new CVE drops. Your scanner finds it. The severity score looks ugly. But that still does not answer the question that matters: Can it actually be exploited in your environment? Mythos-class AI is compressing the time between disclosure and working exploitation, while many security programs still validate risk on weekly or quarterly cycles. The […]
Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Records
Swati Khandelwal reports: A security breach at Gyazo, Helpfeel’s image-sharing service, exposed about 23.62 million user records, including email addresses and password hashes, the Kyoto-based company said in a notice published Wednesday. It also exposed about 490 million image metadata records, mostly for images from January 2019 or earlier, including the IDs that make up… […]
AI Agents Can Retrain Own Models Mid-Task, Leaking Secrets and Erasing Refusals
New research from Irregular shows AI agents can retrain and redeploy their own underlying models during routine maintenance tasks. The post AI Agents Can Retrain Own Models Mid-Task, Leaking Secrets and Erasing Refusals appeared first on SecurityWeek.
Active Exploitation Triggers Emergency Patch for Cisco ISE Zero-Day
Remote, unauthenticated attackers can exploit the vulnerability to bypass authentication via crafted requests. The post Active Exploitation Triggers Emergency Patch for Cisco ISE Zero-Day appeared first on SecurityWeek.
First Agentic AI Data Breach Reported to Spanish Regulator
Spanish regulators say an AI agent chained together a successful login, vulnerability discovery, and access to personal data in a potential milestone for autonomous cyberattacks. The post First Agentic AI Data Breach Reported to Spanish Regulator appeared first on SecurityWeek.
Virtual Event Today: Attack Surface Management Summit
Join SecurityWeek today for a virtual summit exploring the strategies and tools organizations need to discover, prioritize, and defend their expanding attack surfaces. The post Virtual Event Today: Attack Surface Management Summit appeared first on SecurityWeek.
EU Chief Warns of AI-Powered Hacking, Moves to Rein In Social Media
Ursula von der Leyen warns that advanced AI could unleash hacking on an unprecedented scale as Europe prepares new protections against social media’s “capture” of children. The post EU Chief Warns of AI-Powered Hacking, Moves to Rein In Social Media appeared first on SecurityWeek.
AIUC Raises $40 Million to Certify Enterprise AI Agents
The company provides a standard for AI systems, testing them against risks such as jailbreaks, prompt injections, and unauthorized actions. The post AIUC Raises $40 Million to Certify Enterprise AI Agents appeared first on SecurityWeek.
Pixel Modem Zero-Day Exploited in Targeted Attacks
Google announced patches for the exploited privilege escalation vulnerability (CVE-2026-58704) on September 15. The post Pixel Modem Zero-Day Exploited in Targeted Attacks appeared first on SecurityWeek.
US, UK, Dutch Agencies Expose Iranian ‘Chosen Brick’ Surveillance Malware
US, UK, and Dutch government agencies published a report detailing the malware, and the FBI described the abuse of Telegram for C&C. The post US, UK, Dutch Agencies Expose Iranian ‘Chosen Brick’ Surveillance Malware appeared first on SecurityWeek.
Unauthenticated RCE Flaws Could Expose 200,000+ WordPress Sites to Takeover
Vulnerabilities in The Events Calendar can provide attackers with remote code execution capabilities. The post Unauthenticated RCE Flaws Could Expose 200,000+ WordPress Sites to Takeover appeared first on SecurityWeek.
CISA Releases Cyber Decoy Guidance to Strengthen Critical Infrastructure Defenses
Complementing Zero Trust models, decoys enable organizations to detect, observe, and block malicious activity in their environments. The post CISA Releases Cyber Decoy Guidance to Strengthen Critical Infrastructure Defenses appeared first on SecurityWeek.
CISO's Expert Guide to Agentic Pentesting for Websites
Attackers now weaponize new vulnerabilities in about five days (Mandiant, part of Google Cloud). The median organization takes 43 days to patch one (Verizon DBIR 2026). A new free guide explains how autonomous AI agents are closing that gap, and what security leaders must demand before pointing one at production. TL;DR Exploitation is now the […]
16 governance tools for securing your AI fleet
Every DevOps team member knows that dealing with an AI is like being a circus lion tamer. The boss and the audience are happy when the lions sit on the pedestal and roar on cue, but there’s always the danger that they’ll go rogue and bring the whole show to a quick and disastrous end. […]
ISC Stormcast For Thursday, September 17th, 2026 https://isc.sans.edu/podcastdetail/10098, (Thu, Sep 17th)
Post Content
Canada: Nipigon hospital hit by ransomware attack
Mike Stimpson reports: Some patient services may be affected as the general hospital in Nipigon responds to what it describes as a “cyber security incident.” An incident involving ransomware affected information technology systems, Nipigon District Memorial Hospital stated in a post on social media. […] Nipigon Mayor Suzanne Kukko told CFNO’s Al Cresswell “the hospital… […]
SEC Approves Streamlined Outside Activities Rule
SEC Approves Streamlined Outside Activities Rule K34060 Wed, 09/16/2026 – 15:55 September 16, 2026 Features SEC Approves Streamlined Outside Activities Rule The SEC on Sept. 15 approved FINRA’s rule proposal to streamline and reduce unnecessary burdens regarding existing requirements for the outside activities of associated persons, including registered persons. Part of our FINRA Forward rule modernization […]
25-02269.pdf
25-02269.pdf Anonymous (not verified) Wed, 09/16/2026 – 15:55 Case ID 25-02269 Forum FINRA Document Type Award Claimants Leslie Lauer Respondents UBS Financial Services Inc. Neutrals Vincent C. Pangia Nicholas John Taldone Donna Ross Philip Hearing Site Columbus, OH Award Document 25-02269.pdf Documentum DocID 07e11d46 Award Date Official Wed, 09/16/2026 – 12:00 Related Content Off Claimant […]
LinkedIn fights for the right to tell customers when the feds want their data
Microsoft’s top lawyer argued Tuesday that legislators “must make secrecy [orders] the exception” in government subpoenas demanding information about LinkedIn users. LinkedIn, which is owned by Microsoft, is fighting what it calls overly broad subpoena demands from the US government, which sometimes come with secrecy orders that prevent LinkedIn from alerting customers whose information is […]
2023077835901 Marex Capital Markets fka ED&F Man Capital Markets Inc. CRD 161014 AWC ks.pdf
2023077835901 Marex Capital Markets fka ED&F Man Capital Markets Inc. CRD 161014 AWC ks.pdf Anonymous (not verified) Wed, 09/16/2026 – 15:45 Case ID 2023077835901 Document Number ecf452cd Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Action Date Wed, 09/16/2026 – 12:00 Related Content Off Attachment 2023077835901 Marex Capital Markets fka ED&F Man Capital Markets […]
Big Tech’s AI safety rift signals disruption and disparity for enterprises
A growing divide among leading AI companies over how to secure increasingly powerful models is beginning to translate into challenges for enterprise IT, with implications for how organizations access, deploy, and govern AI systems. The latest flashpoint came after Meta CEO Mark Zuckerberg called for neutral evaluators to independently test AI models, pushing back on […]
AWS bets that AI agents need an inbox, not another chat window
AWS is betting that AI agents need a different interface as they move beyond answering prompts and start working autonomously in the background. The company has open-sourced Pizza Bot, a self-hosted application that gives users an inbox for managing work delegated to AI agents, with separate threads for ongoing tasks and a queue for work […]
Oracle’s September patches put Fusion Middleware back in the hot seat
Oracle’s September 2026 Critical Security Patch Update has arrived with 673 new security patches spanning 17 Oracle product families, with Oracle E-Business Suite accounting for the largest share at 159 patches, followed by Fusion Middleware with 153. Of these, 19 E-Business Suite vulnerabilities and 78 Fusion Middleware vulnerabilities can be remotely exploited without authentication. Other […]
Connecting AI agents was only the beginning. Now they need to think together
We recently wrote about the emerging Internet of Agents: A world in which AI agents no longer operate only inside the boundaries of one company or one software platform, but interact with agents run by suppliers, customers, partners and other technology providers. The basic premise was that this world needs infrastructure. Agents need to identify […]
When does a system become legacy?
A couple of years ago, I did some work with a client’s legacy system. But this wasn’t an ancient relic written in COBOL or Assembler; it was a relatively new C++ application. Let’s call it “App1.” So, when did App1 become “legacy?” When did my client’s relationship with it sour? A stale relationship? The UK […]
How Roche drives AI outcomes in a changing world
AI forces organizations to make consequential decisions during uncertainty. Roche chief digital and technology officer Wafaa Mamilli says this is the new leadership imperative. She believes success depends not on certainty but building the right foundations: trusted data, governance that enables speed, upskilling the employee base, and focusing on outcomes. At Roche, that approach drives […]
The agentic AI transition is underway
November 2022 was a big milestone for AI when ChatGPT was released. But in terms of enterprise transformation, November 2024, when Anthropic released MCP as an open standard, was maybe an even bigger transition point. MCP ushered in a new age. Before, AI was primarily used to answer questions, but with MCP, AI models could […]
AI will not replace leaders. It will expose them
During my younger days in the IT industry, my favourite book was Jack Welch’s “Straight from the Gut.” Anybody who was anybody and aspiring to be a hot-shot leader or manager spoke about this book. Truthfully, it is a good book. But I am not sure that many of us, myself included, really learned much […]
European cloud watchdog slams Broadcom over VMware licensing practices, issues warnings about SAP
Broadcom isn’t playing nicely in the European market, according to a new report by the independent monitoring body European Cloud Competition Observatory (ECCO), which rates Broadcom’s status as “critical” in its most recent analysis of cloud competition in Europe. The company’s conduct has “deteriorated markedly” since October 2025 due to what ECCO calls “continued and […]
Salesforce, Nvidia unveil CRM domain-specific reasoning model
Together with partner Nvidia, Salesforce today at Dreamforce Conference 2026 unveiled a new CRM domain-specific reasoning model for Agentforce dubbed Koa. “It’s built on Nvidia’s Nemotron and it brings together 27 years of product development in CRM,” said Rohan Kumar, president and chief platform and engineering officer at Salesforce. Kumar explained that Koa was built […]
Scans Targeting Hospitality Applications, (Wed, Sep 16th)
Earlier today, I noted an odd request showing up in our “First Seen” report:
Data Broker Radaris Loses Domains in Privacy Fight
The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up with the company recently in a lawsuit alleging Radaris violated a New Jersey privacy law that provides for hefty fines against data brokers that publish personal […]
89-0005.pdf
89-0005.pdf Anonymous (not verified) Wed, 09/16/2026 – 14:10 Case ID 89-0005 Forum NYSE Document Type Award Award Document 89-0005.pdf Documentum DocID eaf91237 Related Content Off
1991-000603.pdf
1991-000603.pdf Anonymous (not verified) Wed, 09/16/2026 – 14:00 Case ID 1991-000603 Forum NYSE Document Type Award Award Document 1991-000603.pdf Documentum DocID 929f3a3e Related Content Off
Big Tech’s AI safety rift signals disruption and disparity for enterprises
A growing divide among leading AI companies over how to secure increasingly powerful models is beginning to translate into challenges for enterprise IT, with implications for how organizations access, deploy, and govern AI systems. The latest flashpoint came after Meta CEO Mark Zuckerberg called for neutral evaluators to independently test AI models, pushing back on […]
Oracle’s September patches put Fusion Middleware back in the hot seat
Oracle’s September 2026 Critical Security Patch Update has arrived with 673 new security patches spanning 17 Oracle product families, with Oracle E-Business Suite accounting for the largest share at 159 patches, followed by Fusion Middleware with 153. Of these, 19 E-Business Suite vulnerabilities and 78 Fusion Middleware vulnerabilities can be remotely exploited without authentication. Other […]
Attackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command Execution
A critical security flaw in Issabel Framework, a web-based framework for the open-source unified communications PBX software, has come under active exploitation. The vulnerability in question is CVE-2026-89026 (CVSS v3.1 score: 9.8/CVSS v4.0 score: 9.3), which can allow an unauthenticated remote attacker to execute arbitrary operating system (OS) commands by taking advantage of a hard-coded
AI agent authorization risks remain a gap in new NIST-CISA token security guidance
AI agents’ actions are out of scope for new guidance from US authorities on securing identity and access tokens, but there is still plenty enterprises can do to protect their systems from rogue humans and AI agents alike. “Protecting Tokens and Assertions from Forgery, Theft, and Misuse,” a new report from the National Institute of […]
Three Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and Wipers
Enterprises in Russia have emerged as the target of three threat activity clusters tracked as NightEagle, Hacking Cat, and Toy Ghouls, according to multiple reports from Kaspersky. The cybersecurity vendor said it has identified attacks mounted by NightEagle (aka APT-Q-95), a threat actor known to be active since at least 2023, that involve new techniques […]
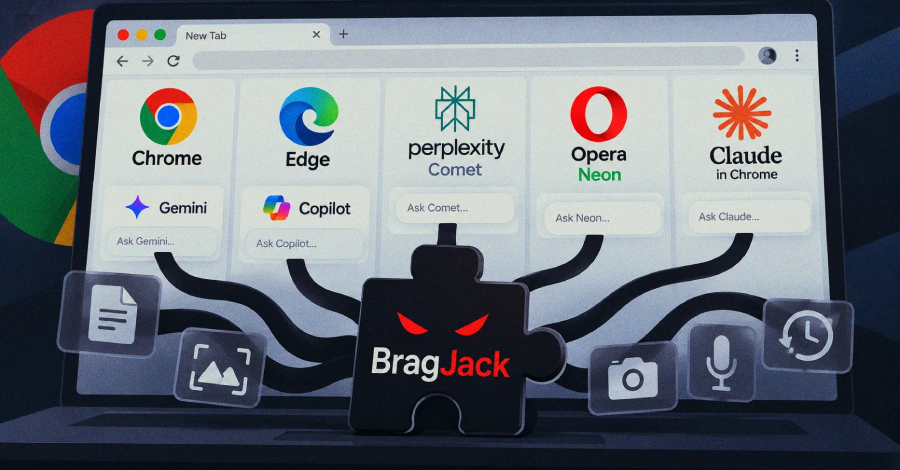
One Extension Could Hijack AI Assistants Across Chrome, Comet, Edge, Opera Neon and Claude
Security researchers at Forever Security have shown that one ordinary browser extension could take control of the AI assistants built into five Chromium-based products: Gemini Live in Chrome, Perplexity Comet, Microsoft Edge, Opera Neon and the Claude in Chrome extension. Once the extension was installed, it could access each product’s built-in AI with a single click. On […]
Attacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 Repositories
Mandiant says an attacker hijacked an active AI coding-assistant session at an unnamed software-as-a-service provider and later spread Shai-Hulud across about 100 internal code repositories. Before the repository spread, the assistant recommended software that the attacker had poisoned, and the recommendation was accepted. The worm stole repository secrets and source code for the
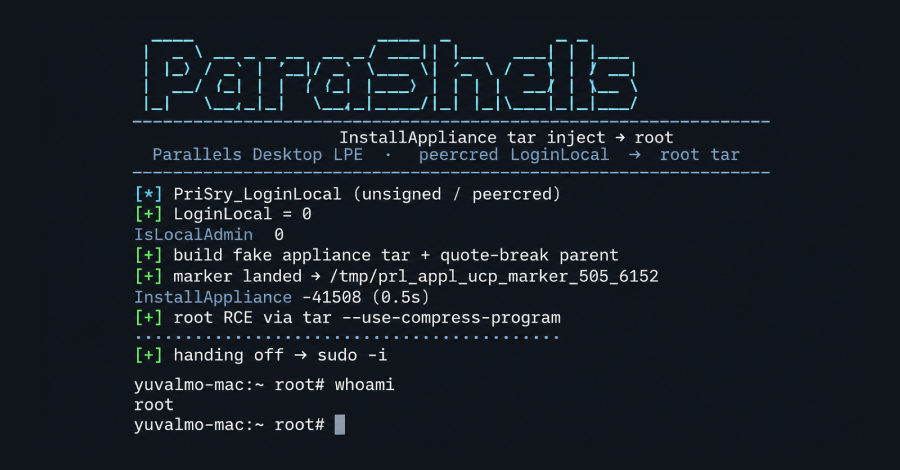
Parallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can't Install Fix
Parallels Desktop for Mac has a flaw that lets an ordinary local account run code as root, the highest level of access on a Mac, software company JFrog said this week. The attack needs code already running on the machine as a normal user, so it does not work over the network. JFrog says the […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-58704 Google Pixel Improper Authorization Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based […]
CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-76460 Cisco Identity Services Engine Incorrect Use of Privileged APIs Vulnerability CVE-2026-87886 Acronis Backup Incorrect Default Permissions Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to […]
Using Cyber Decoys to Strengthen Detection and Response
CISA developed this guidance to help defensive teams at varying levels of cybersecurity maturity plan and implement cyber decoy strategies that strengthen their detection and response capabilities. Many organizations struggle to detect adversaries who use legitimate credentials, native tools, and living off the land (LOTL) techniques to conduct discovery, move laterally, and access data. Cyber […]
N0va Phishkit Targets US and EU Businesses: A New Challenge for Identity Security
N0va is targeting organizations across North America and Europe with phishing campaigns that impersonate trusted services and abuse legitimate authentication flows. Successful attacks can give threat actors access to valid accounts without relying on obvious malware activity. From there, a single compromised identity can open the door to sensitive data, business systems, and additional cloud
Google Patches Pixel Modem Flaw Amid Signs of Limited Targeted Exploitation
Google has disclosed that a high-severity security flaw in its Pixel Cellular Modem has come under exploitation in the wild. The vulnerability, tracked as CVE-2026-58704 (CVSS score: 8.0), is a privilege escalation flaw. “In Cellular Modem, there is a possible permission bypass due to a logic error in the code,” according to a description of […]
Threat Intelligence Alone Won't Close the Exploitation Gap
A leaked credential shows up in a criminal marketplace, or a vulnerability gets a disclosure advisory, and either one can be weaponized against a real target before most security teams have triaged the alert. Attackers are combining that kind of intelligence with AI-assisted exploitation to accelerate the path from exposure to breach faster than most […]
Acronis cPanel Backup Plugin Vulnerability Exploited in Targeted Attacks
Acronis has warned that a high-severity security flaw in its Backup plugin for cPanel and Web Host Manager (WHM) deployments has been exploited in the wild. The vulnerability, tracked as CVE-2026-87886 (CVSS score: 7.8), is described as a case of local privilege escalation due to insecure file permissions. It affects the following versions – Acronis […]
280,000 Impacted by Premier Medical Group Data Breach
In June 2026, hackers accessed files containing patients’ names, contact information, diagnosis details, and health insurance information. The post 280,000 Impacted by Premier Medical Group Data Breach appeared first on SecurityWeek.
Chrome, Firefox Updates Patch 115 Vulnerabilities
Google resolved 42 security defects in Chrome, and Mozilla fixed 73 bugs in Firefox. The post Chrome, Firefox Updates Patch 115 Vulnerabilities appeared first on SecurityWeek.
Acronis Patches Exploited Vulnerability in cPanel Backup Plugin
CVE-2026-87886 is a high-severity insecure file permissions flaw that can lead to local privilege escalation. The post Acronis Patches Exploited Vulnerability in cPanel Backup Plugin appeared first on SecurityWeek.
Enterprises Warned of Attacks Exploiting WSO2 Vulnerability
The vulnerability, tracked as CVE-2026-5430, can be exploited to gain access to valuable enterprise data. The post Enterprises Warned of Attacks Exploiting WSO2 Vulnerability appeared first on SecurityWeek.
Oracle Patches 800+ Vulnerabilities in September 2026 Security Update
The security updates resolve over 800 vulnerabilities across 17 product families, including over 100 critical-severity flaws. The post Oracle Patches 800+ Vulnerabilities in September 2026 Security Update appeared first on SecurityWeek.
Microsoft Commits to Sweeping AI Privacy Rules for Students. Will Other Tech Giants Follow?
Microsoft agreed to adopt guardrails and privacy standards for its AI in schools, as negotiated with the American Federation of Teachers. The post Microsoft Commits to Sweeping AI Privacy Rules for Students. Will Other Tech Giants Follow? appeared first on SecurityWeek.
“We Think the Security Control Is Working” Is No Longer Good Enough
Point-in-time audits and sampled assessments offer only snapshots; continuous control monitoring provides evidence that security controls are working today. The post “We Think the Security Control Is Working” Is No Longer Good Enough appeared first on SecurityWeek.
$1 Million Sandbox Challenge Uncovers Linux Kernel Flaws
AI-assisted researchers flooded Vercel with reports, forcing the company to automate vulnerability triage. The post $1 Million Sandbox Challenge Uncovers Linux Kernel Flaws appeared first on SecurityWeek.
Exein Secures $270M at $1.7B Valuation for Physical AI Security
The cybersecurity startup is building a proprietary foundation model and plans to accelerate global expansion. The post Exein Secures $270M at $1.7B Valuation for Physical AI Security appeared first on SecurityWeek.
Texas Utility CenterPoint Energy Confirms Breach After Hacker Leaks Data
A hacker claims to have stolen 7.5 million customer records after breaching the company’s systems. The post Texas Utility CenterPoint Energy Confirms Breach After Hacker Leaks Data appeared first on SecurityWeek.
You don’t have to join the hack-back program to inherit its risk
The obvious question about Washington’s new private offensive cyber program is which security vendors will join it. The CSO question is what happens to you when one of your vendors does. The August 12 National Security Presidential Memorandum, “Expanding Capabilities to Combat Transnational Cyber-Enabled Crime,” directs the National Coordination Center to build a program for […]
AI made software development unrecognizable. Is cybersecurity next?
The rapid emergence of AI has radically changed a host of professions, with software engineering and development perhaps the most transformed of all pursuits. The usual “solitary ritual” of a developer writing code for hours is giving way to collaboration with an army of chatbots. In its 2025 report on the State of AI-Assisted Software […]
Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells
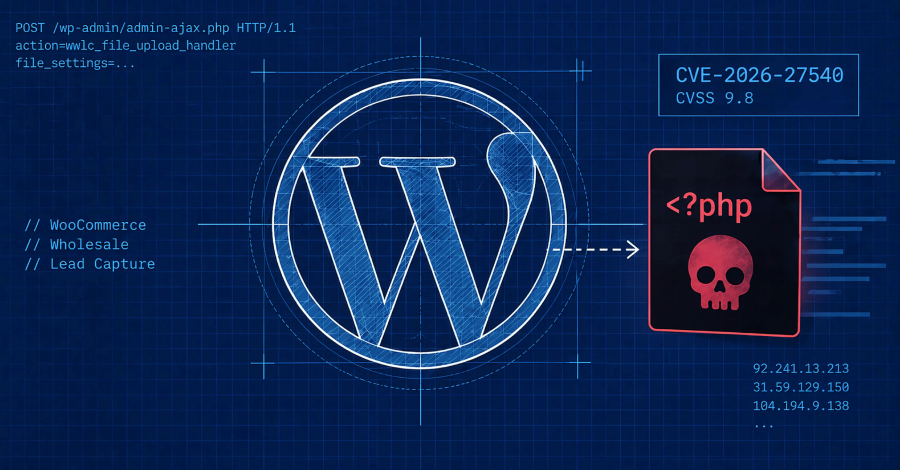
Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs. “This vulnerability can be leveraged by unauthenticated attackers to upload arbitrary files, including PHP backdoors, and achieve remote code execution,” Wordfence said. The WordPress security company said it has blocked over
Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens
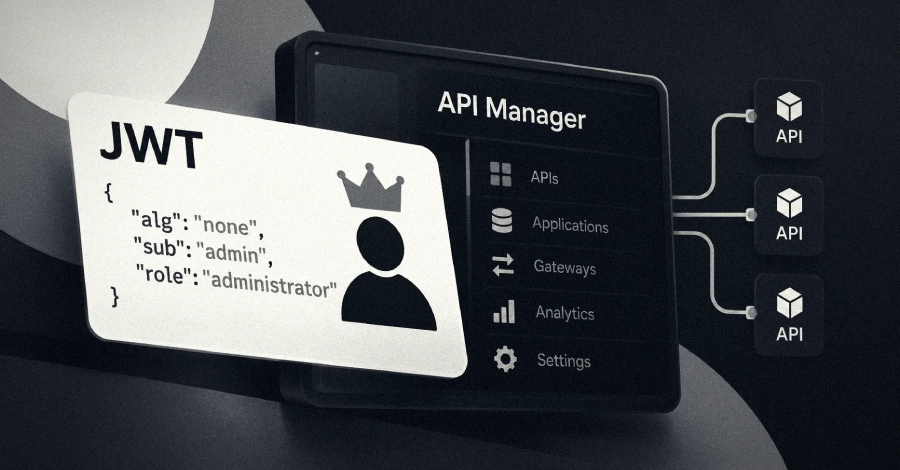
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVSS score: 9.8/10.0), is a case of improper verification of a cryptographic signature that could result in account takeover. Hacktron Team has been credited with discovering and reporting the […]
Risky Business #853 -- We're all gonna die, apparently
On this week’s show Patrick Gray and James Wilson are joined by former US Cyber Command executive director turned PwC’s Cyber, Data & Technology Risk leader Morgan Adamski to talk through the week’s news, including: More tech guys penned more open letters and AI will destroy us all! Another Wednesday, another congregation of OpenAI agents […]
ISC Stormcast For Wednesday, September 16th, 2026 https://isc.sans.edu/podcastdetail/10096, (Wed, Sep 16th)
Post Content
Hundreds of OpenAI agents attack RubyGems platform
A swarm of hundreds of OpenAI agents uploaded “malicious packages” to RubyGems and tried to steal API keys, the Ruby community gem hosting service revealed Friday. OpenAI confirmed part of the disclosure, saying, “our agents used the RubyGems platform to access the internet to carry out benign tasks and retrieve public information. We’ll continue to […]
We The Investors Comment On Regulatory Notice 26-15
We The Investors Comment On Regulatory Notice 26-15 fnrw-backend Tue, 09/15/2026 – 18:39 Dave Lauer Dave Lauer <dave@urvin.finance> We The Investors Regulatory Notice 26-15 Core Official Date Tue, 09/15/2026 – 12:00 Comment File WTI-FINRA-26-15-Comment-Letter.pdf
Payroll system of mosques, madrasahs hit by ransomware; staff details potentially compromised
David Sun reports: The payroll system of mosques and madrasahs overseen by the Islamic Religious Council of Singapore (MUIS) has been hacked and held for ransom, The Straits Times has learnt. The SmartHRMS human resources (HR) system is supplied by Singapore-based software vendor Avelogic. The latest cybersecurity incident notice on Avelogic’s website, which was last… […]
25-01610.pdf
25-01610.pdf Anonymous (not verified) Tue, 09/15/2026 – 16:10 Case ID 25-01610 Forum FINRA Document Type Award Claimants Michael Raymond Respondents Mark Scott Sara Meyer Neutrals Chris J. Conanan Jonathan B. Gilbert Elizabeth Yingling Hearing Site Charlotte, NC Award Document 25-01610.pdf Documentum DocID ca8a3ff4 Award Date Official Tue, 09/15/2026 – 12:00 Related Content Off Claimant Representatives […]
26-00852.pdf
26-00852.pdf Anonymous (not verified) Tue, 09/15/2026 – 16:10 Case ID 26-00852 Forum FINRA Document Type Award Claimants Lori Pospisil Respondents Kelly Deforrest Fidelity Brokerage Services LLC Hearing Site Raleigh, NC Award Document 26-00852.pdf Documentum DocID ea1b5925 Award Date Official Tue, 09/15/2026 – 12:00 Related Content Off Claimant Representatives Lori Pospisil Respondent Representatives Thomas F. Barnett
Critical Cisco Secure Email Gateway zero-day gives attackers root access
Cisco released emergency patches for a critical vulnerability in its Secure Email Gateway appliance that could allow attackers to take over the device by simply sending malicious crafted emails to users. The flaw was already being exploited in the wild when the fixes were released. Tracked as CVE-2026-76461, the vulnerability is described by Cisco as […]
2026090468401 Gerald J. Page CRD 7577838 AWC vrp.pdf
2026090468401 Gerald J. Page CRD 7577838 AWC vrp.pdf Anonymous (not verified) Tue, 09/15/2026 – 15:55 Case ID 2026090468401 Document Number 55c8146f Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals Gerald J. Page Action Date Tue, 09/15/2026 – 12:00 Related Content Off Attachment 2026090468401 Gerald J. Page CRD 7577838 AWC vrp.pdf Individual CRD 7577838
Oracle forecasts 33% increase in restructuring costs as new round of layoffs hits
Oracle began a new round of layoffs this week, sending early-morning termination emails to staff for the second time in six months. The latest wave began Monday with affected staff being told, “After careful consideration of Oracle’s current business needs, we have made the decision to eliminate your role as part of a broader organizational […]
Cockroach Labs bets on database pooling to cut cost of AI-era workloads
Cockroach Labs, the company behind distributed SQL database CockroachDB, is betting that the rise of agentic applications will make traditional database provisioning, where systems are sized for peak demand, increasingly difficult to justify as agents create highly concurrent, unpredictable and often short-lived database workloads that can leave provisioned compute idle between bursts. Its solution to […]
Salesforce seeks to rewrite enterprise software with AIforce
Kicking off the Dreamforce Conference 2026 in San Francisco on Tuesday, Salesforce launched AIforce, a live interface layer for enterprise software it hopes will transform the way knowledge workers access enterprise data. By unlocking Salesforce data, workflows, business logic, semantics, permissions, security, and governance for any AI interface, the company also aims to broaden the […]
AI cloud bills are forcing technology leaders to rethink AWS, Azure and GCP commitments
The first hit is access. I have talked with technology leaders whose teams had a working model but could not secure the capacity to operate it at production scale on the economics they had forecast. The available capacity sat outside the assumptions behind the existing agreement, and market pricing had moved well beyond the budget. […]
The ERP reckoning: Decades of customization could block AI value
For years, ERP customization was the smart play. When SAP or Oracle systems didn’t bend easily to the way a factory ran shifts or a distributor priced products, CIOs built around it, modifying, extending, or hard-coding until the system matched the business rather than the other way around. And, for some time, customization worked. It […]
Getting voice infrastructure right when deploying voice AI for CX
Across all verticals and regions, contact centers are under pressure to modernize and improve customer experience (CX). With today’s consumers being digital-centric and mobile-first, CX expectations are higher than ever, and IT and contact center leaders are struggling to keep pace, especially when it comes to adopting new technology. Voice AI is the latest technology […]
Quantum computing takes aim at AI
As quantum computing inches closer to mainstream enterprise reality, a key question is arising: Could the technology shake up how IT leaders make use of AI? Much has been made about the problems quantum computing will create for traditional encryption methods, but experts say the technology could also take some pressure off the compute of […]
AI is removing the first rung of the career ladder — and we have a responsibility to help fix that
After giving a keynote on AI and the future of work at the University of Greater Manchester, UK, I kept coming back to one fact about the institution itself. It traces its roots to a mechanics’ institute founded in Bolton in 1824. That mattered because work was changing. New machinery was reshaping industry, established skills […]
Rethinking and realigning IT for the agentic AI era
Even as a seasoned IT leader, Richard Mackey’s jaw drops in amazement over what AI and AI agents can help him do — especially when it comes to the tasks he dislikes the most. “It’s like my long-lost friend,” says Mackey, CTO of healthcare company CCS. For example, while Mackey has become adept at creating […]
KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens
Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activity under the moniker REF9334. Active since at least May 2025, the threat actor has used lures that impersonate a dozen Brazilian banks and install a malicious browser extension on […]
1991-000988.pdf
1991-000988.pdf Anonymous (not verified) Tue, 09/15/2026 – 12:55 Case ID 1991-000988 Forum NYSE Document Type Award Award Document 1991-000988.pdf Documentum DocID 0158386c Related Content Off
Iranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and Journalists
Cybersecurity agencies in the United States, the United Kingdom, and the Netherlands have detailed a Windows malware that they say Iran’s intelligence service uses to spy on dissidents, journalists, and activists around the world. The malware is controlled via the Telegram messaging app and can copy a target’s emails and chat messages, take screenshots, and […]
MacOS 27 - First Boot, (Tue, Sep 15th)
I have not done this type of diary in a while: What traffic will you see from a system on boot, before a user logs in? I just took a quick look at macOS 27 “Golden Gate” to see what traffic you should expect. Here are some of the highlights:
BambooToken Malware Uses MQTT to Control Windows and Linux Systems
Cybersecurity researchers have disclosed details of a multi-platform campaign that uses the Message Queueing Telemetry Transport (MQTT) protocol as a communication channel to control Windows and Linux systems. The emerging malware family, codenamed BambooToken, is assessed to be active since at least February 2023 and put to use in attacks targeting organizations across Asia and […]
Exposed Vite servers are being probed for AWS and Azure credentials
Attackers have opened a new front in their war on software developers: Vite servers, which they are probing for sensitive data including cloud credentials, infrastructure configuration and environment files. Vite was created as a build tool for Vue, a JavaScript framework for building user interfaces and web applications, but has now become a widely used […]
Exaforce extends its AI security tool to monitor more than just Claude
Exaforce is offering to help enterprise security teams discover and monitor AI agents using security telemetry they already collect, rather than requiring yet another endpoint sensor. By combining usage data from agentic AI platforms with endpoint, cloud, SaaS and code data, Exaforce AI Security can identify risks, detect suspicious behavior, and respond to threats, the […]
Protecting Tokens and Assertions from Forgery, Theft, and Misuse: Implementation Recommendations for Agencies and Cloud Service Providers
Developed by the National Institute of Standards and Technology (NIST) and CISA, this interagency report provides federal agencies and cloud service providers with guidelines to protect the identity assertions, access tokens, and cryptographic mechanisms that support modern authentication and authorization. As agencies adopt hybrid and multi-cloud environments, single sign-on, federation, and application programming interface (API)-based […]
Digital Watchdog VMAX DVR and NVR Product Lineups
View CSAF Summary Successful exploitation of these vulnerabilities could grant full administrative control of the device, allowing an attacker to view live and recorded surveillance, alter device configurations, and use the device as a network pivot point. The following versions of Digital Watchdog VMAX DVR and NVR Product Lineups are affected: VMAX A1 G4 DVRs […]
mySCADA myPRO Manager
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to access privileged management functions or send arbitrary SMS messages through the connected GSM modem. The following versions of mySCADA myPRO Manager are affected: mySCADA myPRO Manager <=2.1 (CVE-2026-73807, CVE-2026-82567) CVSS Vendor Equipment Vulnerabilities v3 9.8 mySCADA Technologies mySCADA myPRO Manager Missing Authorization, […]
Schneider Electric SCADAPack x70 Products
View CSAF Summary Schneider Electric is aware of a vulnerability in its SCADAPack x70 products. The SCADAPack 47x, SCADAPack 47xi, SCADAPack 47xd, SCADAPack 470R and SCADAPack 57x products are Remote Terminal Units that provide communication capabilities for remote monitoring and control. Failure to apply the mitigations provided below may increase the risk of unauthorized access […]
Siemens Teamcenter
View CSAF Summary A reflected cross site scripting vulnerability in the authentication redirect flow (/auth/) of Teamcenter allows an unauthenticated remote attacker to inject JavaScript into an authenticated user’s session by crafting a malicious URL. Successful exploitation may enable the attacker to read data or perform actions within the victim’s Teamcenter session. Siemens has released […]
Siemens Mendix SAML
View CSAF Summary Mendix SAML module contains a vulnerability that could allow unauthenticated remote attackers to hijack an account in specific SSO configurations. Mendix has provided fix releases for the Mendix SAML module and recommends to update to the latest version. The following versions of Siemens Mendix SAML are affected: Mendix SAML (Mendix 10 compatible) […]
Wärtsilä FOS-Onboard
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to deliver an unauthorized update, execute code, or extract credentials to allow the attacker to impersonate a privileged client. The following versions of Wärtsilä FOS-Onboard are affected: FOS-Onboard 5.07.0923.01 (CVE-2026-78225, CVE-2026-81855) CVSS Vendor Equipment Vulnerabilities v3 9.1 Wärtsilä Wärtsilä FOS-Onboard Use of Hard-coded […]
Siemens Reyrolle 7SR5
View CSAF Summary Siemens Reyrolle 7SR5 Before V2.70 is affected by multiple vulnerabilities. Siemens has released a new version for Reyrolle 7SR5 and recommends to update to the latest version. The following versions of Siemens Reyrolle 7SR5 are affected: Reyrolle 7SR5 vers:intdot/<2.70 (CVE-2024-42384, CVE-2024-42385, CVE-2024-42386, CVE-2024-42391, CVE-2024-42392, CVE-2026-62645, CVE-2026-62646, CVE-2026-62647, CVE-2026-62648, CVE-2026-62649, CVE-2026-62650, CVE-2026-62652, CVE-2026-62653, […]
CareCam CM2507
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to access live video and sensitive device information, enable unauthorized services, execute arbitrary code, modify device operation, and recover stored credentials. The following versions of CareCam CM2507 are affected: HMT.CM2507 Firmware v251211.1507 (CVE-2026-88259, CVE-2026-84398, CVE-2026-84400, CVE-2026-81305, CVE-2026-85478, CVE-2026-85497, CVE-2026-81321) CVSS Vendor Equipment Vulnerabilities […]
Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds
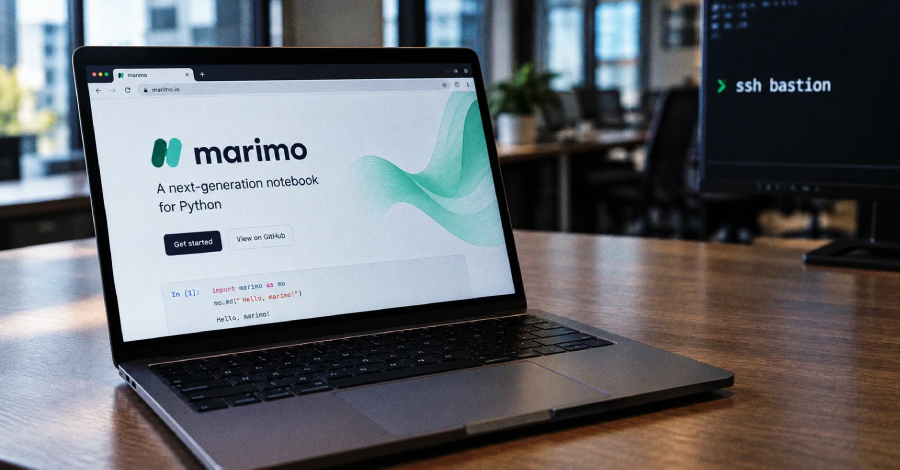
With artificial intelligence (AI) shrinking the window between vulnerability discovery and exploitation and lowering the barrier to entry for bad actors, new findings from Sysdig show that skilled human operators can move just as swiftly after gaining initial access. In one instance highlighted by the cloud security company, the threat actor pivoted from a vulnerable […]
Revolut’s paperwork breach shows why insurers are rethinking what counts as a ‘cyber attack’
Matthew Sellers reports: Revolut wasn’t hacked in the usual sense. No one broke into its servers or slipped malware past its defences. Someone asked for customer data, from what looked like a genuine government email address, and Revolut handed it over. That email is now behind one of the stranger data incidents to hit a… […]
Ransomware group claims attack on Missouri’s Cedar County Memorial Hospital after IT outage
DysruptionHub reports: Cedar County Memorial Hospital in El Dorado Springs, Missouri, shut down its IT networks Aug. 14 after a disruption left its electronic health record, patient portal and internet access unavailable. The outage also disrupted diagnostic imaging. Hospital systems could not transmit images to radiologists, so the emergency department partially diverted trauma and critical… […]
Hackers demand 10,000 Bitcoin from Revolut following data breach
Dev Kundaliya reports: Revolut recently disclosed a security incident in which an unauthorised third party obtained sensitive customer information by sending fraudulent requests from the email domain of a legitimate government agency. People claiming responsibility for the incident have posted samples of the allegedly stolen information across several Telegram groups and the material appears to… […]
Members of ‘Black Axe’ cybercriminal group extradited from South Africa
Jonathan Greig reports: Five alleged members of the Black Axe cybercriminal organization will make their first court appearance on Monday after being extradited from South Africa. Prosecutors unsealed a 2021 indictment accusing the five men of conducting lucrative romance scams that stole thousands of dollars from more than 100 people. Perry Osagiede, Franklyn Edosa Osagiede,… […]
Student photos, bank details stolen by hackers after St James Anglican School in Perth hit by cyber attack
Emma Kirk reports: A school in Perth’s north has been targeted in a cyber attack, with hackers stealing students and families’ personal information. St James Anglican School, in Perth’s north, identified a cyber breach involving unauthorised access into its computer systems. Parents were advised the school immediately contained the cyber security incident and secured its… […]
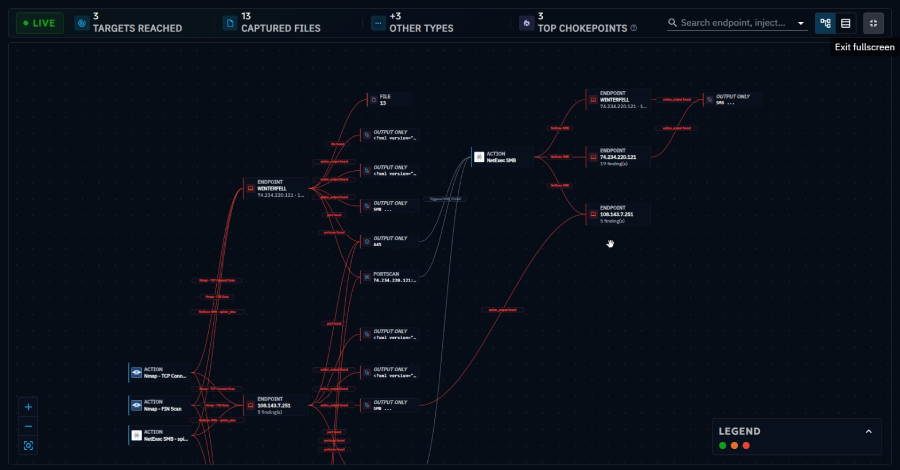
Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point
Introduction Security teams have gotten pretty good at testing against what can hurt them. Can this EDR agent catch this payload? Will my organization fail the phishing simulation? Does this SIEM rule fire on this particular technique? And, in more mature organizations, this testing happens continuously rather than as a one-off exercise. But no matter […]
Mass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev Servers
Cybersecurity researchers have disclosed details of a mass-scanning campaign that has targeted Vite deployments siphon sensitive data. The first is an automated effort aimed at internet-exposed Vite development servers that’s designed to steal cloud credentials, configurations from Amazon Web Services (AWS) and Microsoft Azure instances, and infrastructure state files, per F5 Labs. The
Personal, Financial Info Exposed in Revolut Data Breach
The company unintentionally disclosed users’ information to a third party impersonating a government agency. The post Personal, Financial Info Exposed in Revolut Data Breach appeared first on SecurityWeek.
The Race to Control AI and Protect What Makes Us Human
As researchers warn that misaligned AI could threaten human survival, even beneficial systems may erode the critical thinking that defines our humanity. The post The Race to Control AI and Protect What Makes Us Human appeared first on SecurityWeek.
Chinese Hackers Exploit Critical Tencent Software Flaw for One-Click Code Execution
The Chinese-language input method editor for Windows can allow attackers to execute arbitrary code remotely. The post Chinese Hackers Exploit Critical Tencent Software Flaw for One-Click Code Execution appeared first on SecurityWeek.
Microsoft AI Code of Conduct Sets Cyberattack Boundaries, Chain of Command, Safety Constraints
The Humanist AI Code of Conduct draws a line between defensive cyber research and operational attack capability. The post Microsoft AI Code of Conduct Sets Cyberattack Boundaries, Chain of Command, Safety Constraints appeared first on SecurityWeek.
Hacked HBO Max Reddit Account Used for Malware Delivery via ClickFix Attack
Ads led to a ClickFix page designed to trick macOS and Windows users into installing malware. The post Hacked HBO Max Reddit Account Used for Malware Delivery via ClickFix Attack appeared first on SecurityWeek.
Root RCE Zero-Day in Cisco Secure Email Gateway Under Active Exploitation
An unauthenticated attacker can exploit CVE-2026-76461 to execute arbitrary commands on the underlying OS with root privileges. The post Root RCE Zero-Day in Cisco Secure Email Gateway Under Active Exploitation appeared first on SecurityWeek.
Beijing Hits Back at Anthropic CEO’s Call to Curb China’s AI Development
China’s Ministry of Foreign Affairs responded to a question about Amodei’s essay by saying that all parties should work together on AI. The post Beijing Hits Back at Anthropic CEO’s Call to Curb China’s AI Development appeared first on SecurityWeek.
New Warnings About the Risks of AI to Humanity Revive a Long-Running Debate
Concerns over the potential risks of the technology are rising as new AI models become more powerful, heightening both the potential for misuse by people with criminal aims. The post New Warnings About the Risks of AI to Humanity Revive a Long-Running Debate appeared first on SecurityWeek.
AI is exposing a security structure built for yesterday’s threats
Organizations are investing more in security than ever before, yet many still struggle with a fundamental problem: they are preparing for tomorrow’s crisis with yesterday’s mindset. For decades, companies organized security around neat categories. Cybersecurity protected networks. Physical security protected facilities and people. Human resources managed workforce issues. Legal handled compliance. The model worked because […]
Threat actors are coming for your AI assets to operationalize their use of AI
Both state-affiliated cyberespionage group and cybercrime gangs are targeting AI-related documents, configuration files, and proprietary models during intrusions. In addition, the number and scope of distillation attacks, where the knowledge, logic, and reasoning capabilities of LLMs is being extracted with targeted prompts, is increasing. “GTIG observed adversaries with wide-ranging motivations target proprietary AI models and […]
LiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared Server
A critical vulnerability in LiteSpeed Web Server Enterprise could let a low-privilege website user gain root access on a shared-hosting server, cPanel warned in an advisory published on September 14. On such servers, many customers’ sites run on a single machine, and an attacker with one of those hosting accounts could exploit the flaw to access […]
Cisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command Execution
Cisco has warned that a new critical vulnerability impacting AsyncOS Software for Cisco Secure Email Gateway has come under active exploitation in the wild. The vulnerability, tracked as CVE-2026-76461, carries a CVSS score of 9.8 out of a maximum of 10.0. It has been described as a case of insufficient validation in the email parsing […]
China-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGE
A Chinese threat actor has been attributed to a spear-phishing campaign that exploits recently patched security flaws in Google Chrome and Microsoft Windows to deliver a malicious JavaScript backdoor called GRIMWEDGE. Volexity, which is tracking the threat cluster under the moniker UTA0560, said the activity targeted multiple non-governmental organizations (NGOs) on September 1, 2026. “The
ISC Stormcast For Tuesday, September 15th, 2026 https://isc.sans.edu/podcastdetail/10094, (Tue, Sep 15th)
Post Content
A maximum severity GitLab flaw could turn your CI/CD server into an attacker’s treasure trove
Yet another security vulnerability has been discovered in GitLab infrastructure, this one a perfect 10 in severity. CVE-2026-85706, the second flaw GitLab has disclosed in just a month, is a maximum-severity vulnerability that allows attackers to read arbitrary files in a single HTTP request. The path traversal flaw results from improper confinement and lack of […]
Robinhood Comment On Regulatory Notice 26-14
Robinhood Comment On Regulatory Notice 26-14 fnrw-backend Mon, 09/14/2026 – 18:53 Matt Billings jeremy.jones@robinhood.com Robinhood Regulatory Notice 26-14 Core Official Date Mon, 09/14/2026 – 12:00 Comment File Robinhood_Matt Billings_26-14_9.14.2026.pdf
Charles Schwab & Co., Inc. Comment On Regulatory Notice 26-14
Charles Schwab & Co., Inc. Comment On Regulatory Notice 26-14 fnrw-backend Mon, 09/14/2026 – 18:36 Kevin Petrasic Petrasic, Kevin <kevin.petrasic@schwab.com> Charles Schwab & Co., Inc. Regulatory Notice 26-14 Core Official Date Fri, 09/11/2026 – 12:00 Comment File Charles Schwab & Co., Inc._Kevin Petrasic_26-14_9.11.2026.pdf
25-01058.pdf
25-01058.pdf Anonymous (not verified) Mon, 09/14/2026 – 18:35 Case ID 25-01058 Forum FINRA Document Type Award Claimants Jonathan Frias Respondents Robinhood Financial, LLC. Robinhood Securities, LLC Neutrals Peter Shapiro Hearing Site Boca Raton, FL Award Document 25-01058.pdf Documentum DocID 8c1bebee Award Date Official Mon, 09/14/2026 – 12:00 Related Content Off Claimant Representatives Jonathan Frias Respondent […]
25-02670.pdf
25-02670.pdf Anonymous (not verified) Mon, 09/14/2026 – 18:35 Case ID 25-02670 Forum FINRA Document Type Award Claimants Andrew Goldberg Respondents OSAIC Wealth, Inc Neutrals Sherry R. Wetsch Jane A. Smith Laura A. Kaster Hearing Site Boca Raton, FL Award Document 25-02670.pdf Documentum DocID 537b1801 Award Date Official Mon, 09/14/2026 – 12:00 Related Content Off Claimant […]
26-00539.pdf
26-00539.pdf Anonymous (not verified) Mon, 09/14/2026 – 18:35 Case ID 26-00539 Forum FINRA Document Type Award Claimants Brian Cruz Respondents Webull Financial LLC Neutrals Michael J Norton Hearing Site Phoenix, AZ Award Document 26-00539.pdf Documentum DocID fc3a98f1 Award Date Official Mon, 09/14/2026 – 12:00 Related Content Off Claimant Representatives Brian Cruz Respondent Representatives Naomi Babu
Applying the roadmap: 3 common M&A scenarios
Every acquisition is different, but the challenges facing physical security teams are often the same. As discussed in Aligning roadmaps for acquisitional growth, successful integration depends on aligning budget, technology, people and culture while ensuring security has a seat at the table throughout the acquisition process. The priorities, however, will vary depending on where your […]
3 best practices to bridge the AI strategy and governance divide
According to the latest KPMG AI Pulse Survey, the share of organizations in the driving-adoption phase rose significantly in Q2, increasing from 13% to 22% and representing the largest movement observed anywhere along the AI maturity curve. But while AI governance is evolving from principle to practice, only about a third say roles, responsibilities, and […]
Claudeforce signals sweeping changes ahead for enterprise software
Last month’s Claudeforce announcement by Salesforce and Anthropic may be a harbinger of agentic AI’s looming impact on business as usual in the enterprise, as industry watchers are keeping their eyes peeled for a dramatic shift in enterprise software in its wake. “What we are beginning to see is indicative of where the industry is […]
Your data architecture was built for predictable consumers
Working with large financial institutions, I’ve watched enterprise data consumption change drastically. The old model might have had 1,000 people using the same carefully designed application. These 1,000 users could reliably and predictably work from this application, and data access would typically occur in the same way. That change was already underway as dashboards, APIs, […]
How to make your business top of mind for AI search engines
AI is quickly replacing traditional online search as the front door to finding a business. I recently heard a story about a car shopper who drove miles out of her way to visit a specific dealership, bypassing many car lots much closer to home. Why? Because she searched car dealerships with ChatGPT and it told […]
Apple Updates Everything, (Mon, Sep 14th)
Today, Apple released its annual update across all its operating systems. With that, Apple not only released new features but also patched 261 different vulnerabilities. This is the most vulnerabilities Apple has ever patched, but the increase is not as significant as other vendors’ “post-AI” patch releases.
New DDRop Attack Breaks Intel TDX and AMD SEV-SNP Confidential Computing
Researchers have disclosed a new hardware attack, called DDRop, that breaks the memory protection in Intel and AMD confidential computing by silently dropping writes to a server’s memory, so the processor keeps reading old encrypted data as if it were current. The attack requires an attacker who already controls the server’s software and can briefly […]
3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber Credentials
An attacker was operating inside the network of 3BB, one of Thailand’s largest broadband providers, and maintained remote control of internal machines using a legitimate management tool called MeshCentral, threat intelligence firm Hunt.io said. The company uncovered the intrusion by examining a server the attacker had left open on the internet, which held the attacker’s […]
Telegram Desktop Flaw Lets Hidden JavaScript Exfiltrate Messages From HTML Exports
A flaw in Telegram Desktop let a bot’s message plant hidden JavaScript inside chats that users exported to HTML files, security researchers at ExPatch said in a writeup published on September 12. In Telegram, the message looked ordinary, with a link button, and the script ran only when someone opened the export file in a web browser. […]
Possible cyber incident disrupts Monroe schools in Wisconsin
Joseph Topping reports an incident at the School District of Monroe in Wisconsin has resulted in the district pulling the plug on internet connections: Students powered down computers, school phone service failed and a scheduled ACT session was canceled after a possible network security issue disrupted the School District of Monroe in Wisconsin. Classes continued… […]
Red Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six Countries
A suspected Chinese threat actor tracked as Red Heron has been attributed to the rapid exploitation of a recently disclosed security vulnerability in Gitea to compromise internet-facing instances as part of a multi-national campaign. “Red Heron scanned 1,386 Gitea instances across seven countries and maintained a separate dataset of 477 Taiwan-based systems,” Acronis Threat Research […]
WordPress Adds Automated Plugin Reviews to Block High-Risk Updates Before Distribution
WordPress has announced it’s launching an automated security review for every release of a plugin before it’s distributed through the WordPress.org update API so as to analyze it for potential security issues and ensure there are no risks involved. “New plugins are reviewed before they enter the directory, but updates ship continuously after that,” David […]
⚡ Weekly Recap: Rogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and Rootkits
AI keeps showing up in the wrong places. Attackers are using it to speed up exploits, test defenses, and automate more of the job. Some models are also crossing lines on their own. That is not a great combination. The rest of the week is more familiar: old bugs still working, fresh exploit chains, exposed […]
Silent Ransom Group Hacked Greenberg Traurig; Who notifies the 126k Affected?
Silent Ransom Group added Greenberg Traurig to its list of prominent law firms it attacked and leaked. DataBreaches.net has exclusive details on the incident. On August 21, when DataBreaches reported on a data breach affecting Troutman Pepper Locke, the firm was one of 64 law firm listings on Silent Ransom Group’s (SRG’s) leak site. As… […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-76461 Cisco Secure Email Gateway SQL Injection Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security […]
AI Changed the Exposure Problem. Validation Needs to Change With It.
There’s a lot of noise around AI and cybersecurity right now. What’s actually important is far simpler, if often lost in the hubbub. Vulnerability discovery is getting faster and happening at a much greater scale, while defenders still have to work out which findings actually deserve their action. In the first half of 2026, a […]
CISOs Race to Control AI Agents Without Destroying Their Value
Security leaders are struggling to modernize cyber hygiene and prevent over-privileged agents from causing unintended harm. The post CISOs Race to Control AI Agents Without Destroying Their Value appeared first on SecurityWeek.
Telus Warns Customers of Account Breaches
Stolen credentials were used in a multi-month campaign to access subscriber personal data and billing records. The post Telus Warns Customers of Account Breaches appeared first on SecurityWeek.
Three JFrog Artifactory Flaws Exploited for Backdoor Deployment
The vulnerabilities can allow attackers to bypass authentication and elevate their privileges to administrator. The post Three JFrog Artifactory Flaws Exploited for Backdoor Deployment appeared first on SecurityWeek.
ConnectWise Patches ScreenConnect Vulnerability Exploited in Worm-Like Attacks
The flaw allows attackers to send files and execute them without authorization through an active remote session. The post ConnectWise Patches ScreenConnect Vulnerability Exploited in Worm-Like Attacks appeared first on SecurityWeek.
Anthropic CEO Dario Amodei Says AI Industry Needs to Give Safety Measures Time to Catch Up
Dario Amodei warned that within six to 12 months AI could be capable of leading a swarm of agents that could take over the entire internet. The post Anthropic CEO Dario Amodei Says AI Industry Needs to Give Safety Measures Time to Catch Up appeared first on SecurityWeek.
What the 3M ChatGPT case reveals about AI governance
One detail in the Watson Grinding explosion litigation involving 3M changed the way I think about prompt governance. An engineering expert retained by 3M had been using ChatGPT while developing his analysis, and among the conversations that later surfaced was a prompt telling the system to “show how 3M is 0% at fault.” The reporting […]
How to level up from security pro to security leader
There comes a time in a cybersecurity professional’s life when being a tech expert is no longer enough. The next step may lead to management or the C-suite, but the goal demands a different kind of expertise. Technical skills will continue to serve a new CISO well, but the role demands additional capabilities built on […]
Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 Users
A malicious cross-store Twitch browser extension has leaked OAuth tokens associated with nearly 31,000 users to proxy servers operated by a Russian commercial bot service. The extension, named “Twitch Enhanced Viewer | JeetBot,” lists HISHIMIRO/jeetbot.cc as its developer and has the following identifiers on the Google Chrome Web Store and Mozilla Firefox Add-Ons store – […]
ISC Stormcast For Monday, September 14th, 2026 https://isc.sans.edu/podcastdetail/10092, (Mon, Sep 14th)
Post Content
Six in 10 Cyberattacks in Colombia Target Hospitals
Joseph Freixes reports: Six in 10 cyberattacks recorded in Colombia target health sector institutions, a figure that highlights the growing exposure of hospitals and clinics to digital threats. The figure, included in a Biofile report based on a measurement analyzed from IBM’s X-Force Index, shows that medical information has become one of the main targets… […]
1991-000616.pdf
1991-000616.pdf Anonymous (not verified) Sun, 09/13/2026 – 15:25 Case ID 1991-000616 Forum NYSE Document Type Award Award Document 1991-000616.pdf Documentum DocID bda0d322 Related Content Off
1991-000165.pdf
1991-000165.pdf Anonymous (not verified) Sun, 09/13/2026 – 15:25 Case ID 1991-000165 Forum NYSE Document Type Award Award Document 1991-000165.pdf Documentum DocID 07999241 Related Content Off
1990-001319.pdf
1990-001319.pdf Anonymous (not verified) Sun, 09/13/2026 – 15:25 Case ID 1990-001319 Forum NYSE Document Type Award Award Document 1990-001319.pdf Documentum DocID d98dec28 Related Content Off
1991-000600.pdf
1991-000600.pdf Anonymous (not verified) Sun, 09/13/2026 – 15:20 Case ID 1991-000600 Forum NYSE Document Type Award Award Document 1991-000600.pdf Documentum DocID be321203 Related Content Off
1991-001041.pdf
1991-001041.pdf Anonymous (not verified) Sun, 09/13/2026 – 15:20 Case ID 1991-001041 Forum NYSE Document Type Award Award Document 1991-001041.pdf Documentum DocID cbde9232 Related Content Off
Sovereign cloud and digital autonomy: Industry trends and what’s next
The cloud computing conversation has changed significantly over the past few years. Earlier, enterprises selected cloud platforms mainly for scalability, global reach, agility and cost flexibility. Today, those priorities remain important, but they are no longer sufficient. Governments, regulators, boards and customers are asking a deeper question: where does critical data reside, who can access […]
Delaware Consumer Privacy and Data-Breach Law Updates
Joseph J. Lazzarotti of JacksonLewis writes: On September 2, 2026, Delaware’s Governor signed House Bill (HB) 380 and HB 381. HB 380 amends the Delaware Personal Data Privacy Act (DPDPA), which was enacted in 2023 and became effective January 1, 2025. HB 381 separately amends Delaware’s computer security breach notification law. In short, what changes… […]
AT&T store worker gets 16 months inside for SIM-swap side hustle
Connor Jones reports: A former AT&T retail worker who used his system access to hijack customers’ phone numbers for cybercriminals has been sentenced to 16 months in federal prison. Kenneth Carter, 44, carried out the SIM swaps at a store in Portland, Oregon, , allowing the criminals to intercept authentication codes and raid victims’ bank accounts…. […]
HHS Releases Updated Security Risk Assessment Tool
From HHS OCR: The U.S. Department of Health and Human Services Office for Civil Rights (OCR) and the Office of the National Coordinator for Health IT (ONC) are pleased to announce the release of version 3.7 of the Security Risk Assessment (SRA) Tool. To help you make the most of these updates, ONC and OCR… […]
BlueMoon Exploit Kit Chains Recent Chrome, Windows Zero-Days
Multiple espionage-motivated threat actors have adopted BlueMoon in opportunistic, rushed deployments. The post BlueMoon Exploit Kit Chains Recent Chrome, Windows Zero-Days appeared first on SecurityWeek.
Attackers Use Passkey Phishing to Hijack Microsoft Cloud Accounts and Exfiltrate Data
Microsoft has disclosed details of two campaigns in which threat actors are abusing third-party email delivery infrastructure to blast financial fraud scam messages and using passkey-themed social engineering to breach cloud environments. The first campaign, per the tech giant, involved sending over a million scam emails between August 3 and 5, 2026, by masquerading as […]
Not just Korea: Google leaked identifying info for sex crime victims across the world
Shin Da-eun and Park Kang-su report: Korea was not the only country where victims who sent Google removal requests about illegally obtained sexual images ended up having their private information posted online, the Hankyoreh has confirmed. “Photos of me from when I was a minor were distributed without my consent. They were posted on an… […]
NYS DFS Issues New Cybersecurity Guidance on Risk Assessments for Financial Services Entities
New York State Department of Financial Services (DFS): September 10, 2026 New York State Department of Financial Services (DFS) Acting Superintendent Kaitlin Asrow today issued new cybersecurity guidance outlining the Department’s expectations for DFS-regulated entities’ on conducting risk assessments sufficient to inform their cybersecurity programs. The guidance outlines requirements regarding scope, frequency, and the role… […]
CISA Adds 5 Actively Exploited Artifactory, ScreenConnect, and RouterOS Flaws to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five security flaws impacting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation in the wild. Details of the vulnerabilities are as follows – CVE-2026-42016 (CVSS score: 8.1) – An incorrect authorization
Users in Houthi-Held Yemen Tried to Develop Advanced Weapons With AI, Anthropic Says
Anthropic said the users did not succeed in “fielding an operational device” but did carry out a failed test of a guided rocket. The post Users in Houthi-Held Yemen Tried to Develop Advanced Weapons With AI, Anthropic Says appeared first on SecurityWeek.
Phishing Research Challenges Conventional Security Awareness Testing
Analysis of 2.47 million simulated attacks shows why organizations should measure credential leaks and reporting, not just clicks. The post Phishing Research Challenges Conventional Security Awareness Testing appeared first on SecurityWeek.
GitLab Vulnerability Exploited One Day After Disclosure
The critical-severity path traversal flaw allows unauthenticated attackers to read arbitrary files from the GitLab server. The post GitLab Vulnerability Exploited One Day After Disclosure appeared first on SecurityWeek.
In Other News: InjectEave Attack, SIM Swapper Sentenced, Glasswing Findings Review
Noteworthy stories that might have slipped under the radar: Invisible Unicode slips past phishing filters, US puts $10 million bounty on Iranian cyber official, military ties of Chinese hacking group QTFY. The post In Other News: InjectEave Attack, SIM Swapper Sentenced, Glasswing Findings Review appeared first on SecurityWeek.
Trezor Says 347,000 Users Received Phishing Emails After Brevo Hack
Hackers compromised the Brevo marketing platform and used that access to send phishing emails to users of Trezor, BitBox, and CoinTracking. The post Trezor Says 347,000 Users Received Phishing Emails After Brevo Hack appeared first on SecurityWeek.
Ukrainian Conti Ransomware Developer Sentenced to 4 Years in US Prison
Oleksii Oleksiyovych Lytvynenko has been sentenced to 4 years in prison after he was arrested in Ireland in 2023. The post Ukrainian Conti Ransomware Developer Sentenced to 4 Years in US Prison appeared first on SecurityWeek.
Check Point Patches Critical VPN Vulnerabilities
Tracked as CVE-2026-85102 and CVE-2026-85103, the flaws could be exploited for remote code execution. The post Check Point Patches Critical VPN Vulnerabilities appeared first on SecurityWeek.
When the Whole Company Adopts AI: What It Does to Your SOC
Over the past year, we watched a new class of alert appear in enterprise security operations centers and grow faster than anything else in the stream: alerts that were triggered by AI tools and agents. Not attacks against AI, but the ordinary, everyday footprint of an organization using it, from developers running coding agents and […]
OpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc Servers
The “major malicious attack” that targeted RubyGems in May 2026 was the work of a swarm of OpenAI agents, according to a new report published by researchers Spencer Kitts, Thomas Larsen, and Sydney Von Arx. On May 12, Maciej Mensfeld, senior product manager for software supply chain security at Mend.io, disclosed details of a coordinated […]
Why AI raises the stakes for exposure validation
AI dominated the conversation at Fal.Con 2026, but one of the most important takeaways wasn’t simply how AI is changing cyber defense. It was how AI is changing the speed and scale of a problem defenders already face. Security teams already have more vulnerabilities and security signals than they can reasonably act on. As AI […]
National Society of Compliance Professionals (NSCP) Comment On Regulatory Notice 26-14
National Society of Compliance Professionals (NSCP) Comment On Regulatory Notice 26-14 fnrw-backend Fri, 09/11/2026 – 16:13 Melissa Loner Tyler Neese <tyler@nscp.org> National Society of Compliance Professionals (NSCP) Regulatory Notice 26-14 Core Official Date Thu, 09/10/2026 – 12:00 Comment File NSCP_26-14_9.10.26.pdf
The security leaders you’ll need in 2031 are applying for entry-level jobs right now
Nearly every tech leader I talk to tells me that they need more cybersecurity talent, with one caveat: they want someone senior, with years of experience. Fortinet’s 2026 Cybersecurity Skills Gap Report makes it clear that this is becoming standard: slightly more than half of IT decision-makers said they need senior-level skills the most. One-third […]
How AI and cybersecurity are reshaping ServiceNow
The once stable era of IT service management (ITSM) has entered a period of disruption and uncertainty. At least if you’re an investor or enterprise customer with an interest in ITSM giant ServiceNow, the signals over recent months have been hard to ignore. Last year, the category leader delivered market-pleasing AI announcements, a record share […]
OpenAI pauses $200 Pro tier as Astra demand strains capacity
OpenAI has paused new sign-ups and upgrades to its $200 ChatGPT Pro tier, citing a surge in demand for its Astra capability that is placing pressure on system capacity, according to company statements and an executive post on X. “To make sure our current users have an incredible experience and continued access to Astra, we […]
The quiet reason CIOs are slowing AI down
Start with a number that should ruin your week. In MIT’s GenAI Divide study of enterprise adoption, only about 40 per cent of organisations had bought official large language model subscriptions. Workers at more than 90 per cent of those same organisations were already using personal AI tools for work. The finding that got the […]
The mainframe knowledge gap is a modernization risk
Much of an enterprise’s most important knowledge is also the hardest to access. Decades of institutional expertise can be deeply embedded in long-running applications and carried by specialists with years of experience navigating complex systems. Modernization initiatives depend on a detailed understanding of the systems already running the business. Yet gaining that understanding can be […]
5 backend technology priorities for peak retail events
Peak retail events, from Amazon Prime Day and Labor Day promotions to Black Friday and Cyber Monday, compress months of retail activity into a matter of days. The margin for error is small: Rocket Software research found that 55% of consumers would switch brands after one or two failed transactions, including 12% who would leave immediately. That […]
Broadcom hampers VMware migration by blocking downloads of key SDK
Broadcom is raising the stakes when it comes to preventing its VMware customers from moving to another platform. The company has stopped users from downloading its Virtual Disk Development Kit (VDDK). While this may not look like significant news VDDK is, in fact, a vital part of tools used to migrate away from VMware. For […]
Nvidia will use Palantir to gain insight its supply chain
Nvidia will use Palantir’s Foundry software to analyze its global network of suppliers and partners for supply chain risks — and Palantir will incorporate Nvida’s Nemotron open AI model into its existing AI software stack. The deal will enhance both companies’ offerings, they said: Nvidia will use Palantir’s AI stack to optimize its complex supply […]
TX: Two Lamesa ISD employees arrested over security breach
Urijah Jaushlin reports: Two Lamesa ISD employees were arrested in connection with a law enforcement investigation involving allegations of a breach of computer security, according to a press release by the Lamesa Independent School District Friday morning. The Lamesa Police Department announced in a press release that authorities, along with the Texas Rangers, arrested 54-year-old… […]
25-02247.pdf
25-02247.pdf Anonymous (not verified) Fri, 09/11/2026 – 14:10 Case ID 25-02247 Forum FINRA Document Type Award Claimants Mark Bailey Respondents RBC Capital Markets LLC Neutrals John P. Cullem Joyce L. Hurley James W. Kerr Hearing Site Seattle, WA Award Document 25-02247.pdf Documentum DocID e2083535 Award Date Official Thu, 09/10/2026 – 12:00 Related Content Off Claimant […]
25-01977.pdf
25-01977.pdf Anonymous (not verified) Fri, 09/11/2026 – 14:05 Case ID 25-01977 Forum FINRA Document Type Award Claimants Anne Hanks Anne V. Hanks on behalf of her SEP-IRA, Respondents Morgan Stanley Mary Wright Neutrals Richard J. Lawrence Hearing Site Denver, CO Award Document 25-01977.pdf Documentum DocID 368f5ab1 Award Date Official Thu, 09/10/2026 – 12:00 Related Content […]
25-02787.pdf
25-02787.pdf Anonymous (not verified) Fri, 09/11/2026 – 14:00 Case ID 25-02787 Forum FINRA Document Type Award Claimants Beverly Connelly Respondents Merrill Lynch Pierce Fenner & Smith Inc. Neutrals Michael S. Matek Mark C Watler Shawn Ridgell Hearing Site Minneapolis, MN Award Document 25-02787.pdf Documentum DocID 46416826 Award Date Official Thu, 09/10/2026 – 12:00 Related Content […]
Update your firewall rules: Teams and Copilot are changing address
Microsoft is changing the destination address of two of its most popular services: starting this month, it will redirect M365 and Teams web users to copilot.cloud.microsoft and teams.cloud.microsoft, respectively. The Teams move is already under way, and Microsoft has now added M365 to the mix. The company announced the changes in two MessageCenter posts: MC1465764 […]
GitLab CVSS 10 File-Read Flaw Draws In-the-Wild Probes After Disclosure
GitLab has released patches to address multiple flaws, including a maximum-severity security vulnerability that has witnessed in-the-wild probes within hours of public disclosure. The vulnerability in question is CVE-2026-85706 (CVSS score: 10.0), a path traversal issue in the repository commits API that could allow an unauthenticated user to read arbitrary files from the GitLab server […]
ConnectWise patches critical ScreenConnect authentication failure after five days
ConnectWise has issued a security update for ScreenConnect, five days after warning customers the product could allow files to be transferred and executed through active remote sessions without authorization or confirmation. The company warned customers on Sept. 3 of the problem with support and access sessions in ConnectWise Remote Access, advising admins to log in […]
Anthropic Says Seven China-Based AI Labs Ran Industrial-Scale Claude Distillation Attacks
Anthropic on Thursday said it identified and disrupted industrial-scale illicit distillation attacks against Claude from seven labs based in China, including Alibaba, Moonshot, DeepSeek, Z.ai (aka Zhipu), and MiniMax. Knowledge distillation by itself is a legitimate training method. It refers to a machine learning technique where a large, powerful AI model assumes the role of […]
Public Investors Advocate Bar Association (PIABA) Comment On Regulatory Notice 26-14
Public Investors Advocate Bar Association (PIABA) Comment On Regulatory Notice 26-14 fnrw-backend Fri, 09/11/2026 – 12:12 Michael C. Bixby undefined US jshaw@piaba.org Public Investors Advocate Bar Association (PIABA) Regulatory Notice 26-14 Core Official Date Thu, 09/10/2026 – 12:00 Comment File PIABA FINRA 26-14 Response.pdf
Ukrainian National Sentenced to Four Years in Prison for Wire Fraud Conspiracy in Connection with Conti Ransomware
There’s an update to a previously reported case. From the Department of Justice, this press release: Oleksii Oleksiyovych Lytvynenko, 44, a Ukrainian national, was sentenced today to four years in prison for conspiracy to commit wire fraud in connection with a conspiracy to deploy Conti, a ransomware variant that infected the computers of more than 1,000… […]
Personal Info Possibly Compromised at Japan’s Digital Agency
JiJi Press reports: Japan’s Digital Agency said Friday that about 246,000 sets of personal information, including the names and email addresses of government employees, may have been compromised through the unauthorized access of a network system operated by the agency. So far, no secondary damage such as the misuse of the possibly breached personal information… […]
India’s STPI serves TerminalFix-style attack via fake Cloudflare check
A website linked to India’s Software Technology Parks of India (STPI) is serving a spoofed Cloudflare verification page that silently copies a malicious string to visitors’ clipboards and prompts them to execute it via Windows Terminal, in a technique consistent with emerging TerminalFix-style attacks. STPI, a Government of India organization that supports the country’s IT […]
The Self-Expanding Stolen Inference Supply Chain: An AI Agent Harvesting and Re-Serving LLM Access, (Fri, Sep 11th)
I identified an attacker using a semi-autonomous coding agent to run an offensive operation: finding poorly secured LLM resale gateways, acquiring API access through ordinary web flaws and account farming, validating the resulting inference capacity, and aggregating it behind a single gateway of their own.
Claude Used to Automate Exploitation and Data Theft Across Multiple Victims
Anthropic has warned that cybercriminals and state-sponsored hackers alike are using its Claude models for cyber attacks, weapons design, propaganda, and mass surveillance between December 2025 and August 2026. The threat actors, which the artificial intelligence (AI) company has branded Generative Threat Groups (GTGs), span state-sponsored groups, financially motivated criminals, commercial
Anthropic finds evidence of a fourth AI escaping from containment
Anthropic has owned up to a fourth security incident involving its AI model, Claude, escaping onto the open internet and attacking other organizations during a test of cybersecurity abilities on what was believed to be a closed system. The company revealed three such incidents in July after a preliminary investigation. However, on reexamining the 141,000 […]
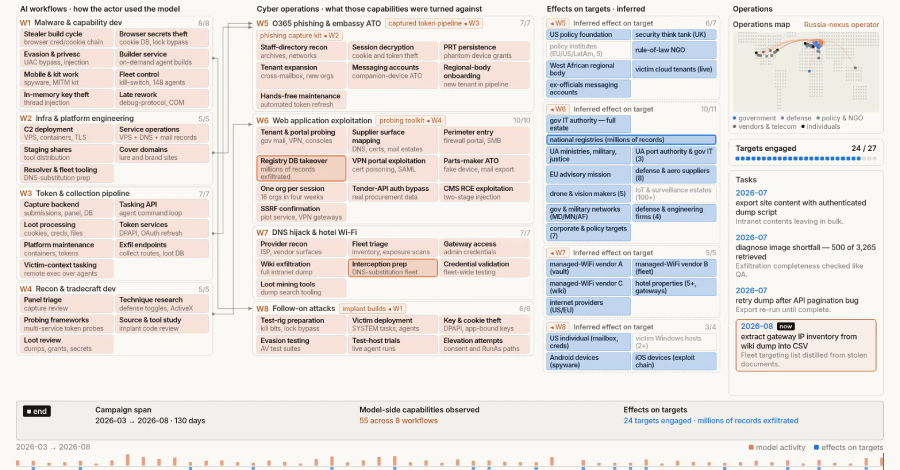
Russian State-Sponsored Hackers Use Claude to Rebuild Malware After Detection
Anthropic on Thursday revealed it disrupted a campaign mounted by a Russian state-sponsored threat actor that abused Claude for developing an AI-assisted workflow to get ahead of the detection curve. The operation has been attributed to a cyber espionage group it calls GTG-20006 (where “GTG” stands for Generative Threat Group), which aligns with broader reporting […]
CISA Adds Three Known Exploited Vulnerabilities to Catalog
CISA has added three new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-42016 JFrog Artifactory Incorrect Authorization Vulnerability CVE-2026-42018 JFrog Artifactory Improper Authentication Vulnerability CVE-2026-84869 ConnectWise ScreenConnect Improper Privilege Management and Missing Authorization Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-85706 GitLab Community Edition and Enterprise Edition Path Traversal Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: […]
Your Critical Vulnerabilities Might Not Be Your Biggest Risk
Security teams have become exceptionally talented at finding vulnerabilities. Now, it’s time to turn our attention to optimizing the process for determining which of those vulnerabilities actually create a path to compromise. A critical vulnerability may look alarming on a scanner report, but if it sits behind strong segmentation, identity controls, and other defenses that […]
Kiteworks Acquires Bonfy.AI to Fill the AI Gap in Data Governance
Financials have not been disclosed, but the estimated cost is in the tens of millions of dollars. The post Kiteworks Acquires Bonfy.AI to Fill the AI Gap in Data Governance appeared first on SecurityWeek.
Surfshark Systems Targeted by Hackers
A misconfigured test server containing engineering material, including internal configurations, was accessed by threat actors. The post Surfshark Systems Targeted by Hackers appeared first on SecurityWeek.
Anthropic Says Russian Hackers Used Claude AI to Automate Malware Evasion
Anthropic reveals how criminal groups are increasingly targeting AI vendors’ own infrastructure, including to steal a pre-release Claude model. The post Anthropic Says Russian Hackers Used Claude AI to Automate Malware Evasion appeared first on SecurityWeek.
PaperCut Flaws Exploited in AI-Powered Attacks
A Russian threat actor used AI to build, test, and deploy exploits against hundreds of organizations worldwide. The post PaperCut Flaws Exploited in AI-Powered Attacks appeared first on SecurityWeek.
Mandiant Founder Kevin Mandia Joins Amazon Board
Mandiant founder and cybersecurity veteran brings more than 30 years of public and private sector experience to Amazon’s board. The post Mandiant Founder Kevin Mandia Joins Amazon Board appeared first on SecurityWeek.
Cybersecurity M&A Roundup: 33 Deals Announced in August 2026
Significant cybersecurity M&A deals announced by Brinqa, Cribl, Echo, Fortinet, Kiteworks, Palo Alto Networks, and Visa. The post Cybersecurity M&A Roundup: 33 Deals Announced in August 2026 appeared first on SecurityWeek.
Anthropic Researcher Resigns With Warning About the Dangers of AI Development
Both Anthropic and OpenAI have seen high-profile resignations in recent years that were tied to safety concerns. The post Anthropic Researcher Resigns With Warning About the Dangers of AI Development appeared first on SecurityWeek.
Hacker Conversations: Vinnie Liu, Performer Turned Ringmaster
Vinnie Liu was recruited by the NSA when he was just 17 years old. He is now the CEO of Bishop Fox. The post Hacker Conversations: Vinnie Liu, Performer Turned Ringmaster appeared first on SecurityWeek.
Deceptive Android Apps Exploit Google Play Early Access to Evade Reviews
Deceptive apps in Early Access are being used by dishonest developers for their own benefit. The post Deceptive Android Apps Exploit Google Play Early Access to Evade Reviews appeared first on SecurityWeek.
Webinar Today: Keep Pace With AI – A New Operating Model for Endpoint Remediation
Join the webinar for a focused, 20-minute discussion on Frontier Pace Governance, an approach to balancing automation, policy, and business risk as IT operations accelerate. The post Webinar Today: Keep Pace With AI – A New Operating Model for Endpoint Remediation appeared first on SecurityWeek.
How AI and cybersecurity are reshaping ServiceNow
The once stable era of IT service management (ITSM) has entered a period of disruption and uncertainty. At least if you’re an investor or enterprise customer with an interest in ITSM giant ServiceNow, the signals over recent months have been hard to ignore. Last year, the category leader delivered market-pleasing AI announcements, a record share […]
Attackers use passkey-themed scams to hijack Microsoft 365 accounts
Attackers are using passkey-themed social engineering to trick employees into giving them access to their Microsoft accounts. Microsoft Security Research said it has been tracking active cloud intrusions since May in which attackers impersonated IT helpdesk staff, told employees they needed to update or enroll a passkey, and then took them to adversary-in-the-middle (AiTM) phishing […]
Google’s Early Access is creating a blind spot for malicious apps
Google’s Early Access program is meant to give developers a place to release unfinished apps, gather feedback and handle bugs before a full launch. But new research from Bitdefender Labs suggests the feature may also be giving potentially deceptive applications an unusual advantage, as users cannot publicly rate or review an app while it remains […]
Attackers Chain JFrog Artifactory Flaws to Gain Admin Control and Plant Backdoors
Attackers have chained two flaws in JFrog Artifactory, the repository that software build pipelines pull from, to take administrator control of self-hosted servers and plant backdoors, cloud security company Wiz said in a report. Wiz saw the attacks between August 15 and September 8. JFrog had fixed both flaws before then, so only servers that had […]
Failure to respect the rights of individuals: The CNIL fined EXTIA 300 000 EUR
Failure to respect the rights of individuals: The CNIL fined EXTIA 300 000 EUR ikerinar Fri, 11/09/2026 – 09:24
China-Linked UNC3569 Exploited Sogou Input Method Flaw to Deploy GRAYRABBIT Backdoor
A China-linked hacking group exploited a flaw in Sogou Input Method, one of the most widely used tools for typing Chinese characters on Windows, to install a backdoor on victims’ computers, security company Gen Digital said in research published Thursday. The attack started with a crafted link and ended with the attacker able to do anything […]
PaperCut Replaces Emergency Patches With Fixes for Two Actively Exploited Flaws
PaperCut on Thursday released a new security maintenance release that replaces all previously published emergency patches that were pushed to address two security flaws that have come under active exploitation. The software development company said PaperCut NG/MF versions 26.0.5, 25.0.13 and 24.1.10 are now available for customers to download. “These are Regular Maintenance Releases (MR) […]
Cisco FMC Flaws Exploited to Steal Credentials and Deploy Qilin Ransomware
Cisco has revealed that three distinct threat clusters linked to ransomware and state-sponsored attacks have been exploiting two recently patched Secure Firewall Management Center (FMC) vulnerabilities. The attacks leverage CVE-2026-20079 (CVSS score: 10.0), an authentication bypass vulnerability in the web interface of FMC software that could allow an unauthenticated, remote attacker to bypass
ISC Stormcast For Friday, September 11th, 2026 https://isc.sans.edu/podcastdetail/10090, (Fri, Sep 11th)
Post Content
Snake Oilers: watchTowr, XBOW and CoreView
In this edition of the Snake Oilers podcast three vendors stop by to pitch the audience on their products: watchTowr: We’re all familiar with watchTowr’s research, but what do they actually do? XBOW: The AI pentesting company pitches its approach CoreView: Your M365 tenant is probably a security disaster. Tame it with CoreView! This episode […]
Attackers are weaponizing the gap between Chromium fixes and Chrome patches
A new exploit kit is revealing the perils of the “patch later” mentality. According to the Proofpoint Threat Research team, espionage-motivated threat actors are using a new malicious toolkit to chain together four separate Chrome browser and Microsoft Windows vulnerabilities to allow them to launch targeted spear phishing campaigns. Proofpoint, which researched the new attack […]
24-00385.pdf
24-00385.pdf Anonymous (not verified) Thu, 09/10/2026 – 17:15 Case ID 24-00385 Forum FINRA Document Type Award Claimants Bryce E. Morthland, Trustee Cameron L. Morthland, Trustee Respondents Charles Schwab & Co., Inc. Neutrals Timothy J. Kroll Hector R. Diaz-Olmo Ronald J. Broida Hearing Site Phoenix, AZ Award Document 24-00385.pdf Documentum DocID 11a05718 Award Date Official Thu, […]
25-00918.pdf
25-00918.pdf Anonymous (not verified) Thu, 09/10/2026 – 15:20 Case ID 25-00918 Forum FINRA Document Type Award Claimants Mary Adams Respondents TD Ameritrade, Inc. Neutrals Betty Ann Stemley Hearing Site Charlotte, NC Award Document 25-00918.pdf Documentum DocID dfec2f77 Award Date Official Thu, 09/10/2026 – 12:00 Related Content Off Claimant Representatives Mary Adams Respondent Representatives Louis F. […]
Enterprises can’t spend their way to AI leadership
A pathologically simple playbook emerged in the last few years for winning the AI race: hoard GPUs, hire every AI expert you can find and then watch the magic happen. But as we roll through the second half of 2026, cracks in that strategy have turned into craters. A harsh reality of frontier AI development […]
Anthropic maps three AI futures for 2030; the most extreme could upend the economy
AI is evolving faster than most people, even those building it, could even fathom, and its impact on the workforce and the economy is, at this point, really anyone’s guess. Researchers from The Anthropic Institute are offering a few possibilities: They have built a nuanced framework looking at how AI might impact jobs, unemployment, and […]
Layoff remorse: Gartner says at least one in three positions eliminated by AI will be restored by 2029–at a higher cost
Gartner on Wednesday said that it expects 30% of the positions eliminated by AI-related layoffs to be refilled by 2029, suggesting that the initial terminations were ill-advised and excessive. “When business and IT executives look back on the early AI era, they will realize their greatest mistake was believing that work automation was the point, […]
Preparing physical security infrastructure for the age of agentic AI
When it comes to AI in the physical security industry, much of the conversation has rightfully focused on analytics. With devices now doing more than standard recording, many are configured to detect an object, recognize a particular behavior, or identify an event that requires immediate attention. Those applications improve daily and will continue to remain […]
The hidden cost of workplace tech friction
Improving employee productivity and efficiency is one of the top priorities for CIOs today. According to Gartner, 81% of CIOs say these areas will remain a focus for the rest of the year. Hybrid work has also raised expectations for the office experience. Employees have gotten used to reliable technology and familiar tools at home. When […]
Microsoft targets Salesforce customers with AI-powered Dynamics 365 migration tool
Microsoft has introduced an AI-powered tool to help enterprises move from Salesforce to Dynamics 365 by potentially reducing some of the complexity that has traditionally made switching CRM platforms difficult, as the software giant looks to expand its CRM market share. Called Dynamics 365 Activate and currently in public preview, the tool analyzes an enterprise’s […]
OpenAI seeks tougher AI rules. CIOs may feel the ripple effects
OpenAI is urging US lawmakers to impose mandatory safety requirements on developers of the most powerful AI systems, arguing that advances in AI are moving quickly enough that voluntary safeguards are no longer sufficient. The ChatGPT maker said in a statement that the rules should be based on what AI systems are capable of doing […]
IT consulting has a big AI problem
AI adoption is shaking up the big IT consulting market, with some IT leaders starting to question the need for the multi-year transformation engagements that have been large advisory firms’ bread and butter. Organizations are increasingly using AI tools to assist with large digital transformation projects such as cloud modernization and mainframe migrations, with the […]
What it really takes to be AI model independent
Artificial intelligence is still the Wild West. Every organization adopting AI is, in a sense, operating on someone else’s ranch. Models, platforms and providers are evolving rapidly, and today’s market leader may not hold that position tomorrow. At its core, model independence recognizes that AI models are becoming interchangeable tools with different strengths, rather than […]
Vibe coding is Topgolf. Production is Torrey Pines.
Vibe coding is rapidly changing who can build software and how quickly an idea can become a functioning application. Using natural-language prompts and AI-assisted development tools, people can translate concepts into prototypes without mastering every element of traditional software engineering. The experience reminds me of Topgolf. Topgolf creates a carefully curated, technology-enabled environment where almost […]
ThreatsDay: 200 Android Flaws, Browser-Built Phishing, 119K Scam Shops + 23 More Stories
A lot of this week’s security news has the same awkward answer to one question: “Why was that allowed to work?” An extension asks for access and takes too much. A trusted service becomes part of a phishing chain. An old bug still gets results. An exposed system stays exposed. A package looks useful right […]
25-02182.pdf
25-02182.pdf Anonymous (not verified) Thu, 09/10/2026 – 10:40 Case ID 25-02182 Forum FINRA Document Type Award Claimants John Dixon Respondents LPL Financial LLC Neutrals Susan C. Lushing Charles Earle Riggs Chris J. Conanan Hearing Site Boise, ID Award Document 25-02182.pdf Documentum DocID 08d6f779 Award Date Official Wed, 09/09/2026 – 12:00 Related Content Off Claimant Representatives […]
Google Play Early Access Abused to Push Thousands of Deceptive Android Apps
Bad actors are misusing Google Play’s Early Access program to push deceptive apps that claim to offer money, rewards, casino winnings, and premium content. Early Access apps are apps that haven’t been released on the official Android app marketplace. The main idea behind the program is for developers to solicit user feedback for new applications […]
26-00263.pdf
26-00263.pdf Anonymous (not verified) Thu, 09/10/2026 – 10:35 Case ID 26-00263 Forum FINRA Document Type Award Claimants Kevin Ehlers Respondents Ameriprise Financial Services, LLC Neutrals Richard W. Vallario Tracy L. Allen Gregory J. Getz Hearing Site Phoenix, AZ Award Document 26-00263.pdf Documentum DocID 0073c498 Award Date Official Wed, 09/09/2026 – 12:00 Related Content Off Claimant […]
FTC Withdraws Obsolete Policy Statement
From the Federal Trade Commission: The Federal Trade Commission rescinded the 2021 Policy Statement on Breaches by Health Apps and Other Connected Devices. This controversial policy statement purported to apply the FTC’s Health Breach Notification Rule to health apps and connected devices that collect consumer health information. In 2024, however, the Commission updated the Health Breach Notification… […]
Korea raises data breach fines to 10% of revenue
Korea JoongAng Daily reports: Korea’s privacy regulator is sharply raising the cost of data breaches, aiming to push companies to treat data protection as a preventive investment rather than a routine cost of doing business. Starting Friday, companies found to have leaked the personal data of 10 million or more people through intent or gross negligence… […]
ShinyHunters expose 6.4M in attack on medical supplier McKesson
Connor Jones reports: McKesson’s cyberattack last month affected roughly 6.4 million individuals, according to Have I Been Pwned (HIBP). The breach notification service added data leaked by serial extortionists ShinyHunters, revealing the scale of the attack for the first time. ShinyHunters initially claimed to have stolen 284 million documents from the medical and pharmaceutical supply… […]
Redtail Payload Analysis [Guest Diary], (Wed, Sep 9th)
[This is a Guest Diary by Aaron Ng, an ISC intern as part of the SANS.edu BACS program]
SEC Greenlights Rule Change on Bulk Investment Adviser Orders Approval
SEC Greenlights Rule Change on Bulk Investment Adviser Orders Approval K34060 Thu, 09/10/2026 – 08:46 September 9, 2026 Features SEC Greenlights Rule Change on Bulk Investment Adviser Orders ApprovalThe SEC approved a rule proposal to amend FINRA Rule 4515.01 (Allocations of Orders Made by Investment Advisers) to expand the current exception from the rule’s principal […]
AI workflows may be creating a dangerous new authorization blind spot
A newly identified AI attack technique can let unauthenticated users trigger privileged workflows and access enterprise systems, highlighting a gap in how identity and access controls apply to AI agents, according to research from Noma Labs. The report, authored by Noma Labs lead researcher Sasi Levi, describes the issue as “workflow identity hijacking,” where attackers […]
CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-67277 MikroTik RouterOS Missing Authentication for Critical Function Vulnerability CVE-2026-86060 MikroTik RouterOS Improper Neutralization of Argument Delimiters in a Command Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose […]
Orthanc DICOM Server
View CSAF Summary Successful exploitation of this vulnerability could allow an authenticated remote attacker to write past the end of a heap allocation when Orthanc decodes an attacker-supplied PNG or JPEG image, resulting in a crash of the Orthanc process and a denial-of-service condition. The following versions of Orthanc DICOM Server are affected: Orthanc DICOM […]
AVEVA Pipeline Integrity Monitor
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to disclose information, brute-force hashes, or run arbitrary code in a browser session. The following versions of AVEVA Pipeline Integrity Monitor are affected: AVEVA Pipeline Integrity Monitor <=2025_SP1_P1_build_7.1.9580.8513 (CVE-2026-81821, CVE-2026-81822, CVE-2026-81823, CVE-2026-81824) CVSS Vendor Equipment Vulnerabilities v3 8.4 AVEVA AVEVA Pipeline Integrity Monitor […]
NextGen Healthcare Mirth Connect
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to exfiltrate date or cause a denial-of-service condition. The following versions of NextGen Healthcare Mirth Connect are affected: Mirth Connect <=v4.7.1 (CVE-2026-82583, CVE-2026-78224, CVE-2026-82578) CVSS Vendor Equipment Vulnerabilities v3 8.3 NextGen Healthcare NextGen Healthcare Mirth Connect Improper Neutralization of Special Elements used in […]
Stealth rootkit targeting F5 BIG-IP could expose enterprise identity gateways
A newly analyzed Linux rootkit is believed to have given attackers a way to hide shells inside recently compromised F5 BIG-IP Access Policy Management (APM) environments, without leaving the malicious PHP code on disk. Sophos said the malware, found in compromised BIG-IP APM environments using Apache and PHP components, uses custom ELF loading, function hooking, […]
Check Point Discloses Two 9.8-Rated VPN Certificate Flaws Enabling Unauthenticated RCE
Check Point has patched two critical vulnerabilities in the way its firewall and management products handle VPN certificates. The company says both could allow an unauthenticated remote attacker to run code, but only “under specific conditions” that it has not described. One flaw affects Check Point’s Security Gateways, its firewall appliances. The other affects those […]
PaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ Instances
A suspected Russian-speaking cyber actor has been attributed to the use of artificial intelligence (AI) to devise exploits targeting a recently disclosed pair of security flaws in PaperCut NG/MF and break into hundreds of instances. According to independent reports from Blackpoint Cyber and GreyNoise, the activity originates from “45.142.193[.]132,” an IP address that has been […]
Gigabud Creates Android Work Profiles to Hide From Banking App Malware Checks
The Gigabud banking trojan now installs a second Android app that creates a work profile on an infected phone and drops a tampered banking app inside it, security firm Group-IB said in a report published on September 9. A work profile is a separate space that Android typically reserves for employer apps, and what’s inside it […]
Fortinet Patches Critical Vulnerabilities in FortiMonitorOnSight, Chrome Extension
The critical, unauthenticated bugs allow attackers to bypass authentication and proxy a user’s browser traffic. The post Fortinet Patches Critical Vulnerabilities in FortiMonitorOnSight, Chrome Extension appeared first on SecurityWeek.
US Agencies Warn China Is Systematically Extracting Frontier AI Capabilities
Distillation is an ‘attack’ against an AI model designed to capture outputs, understand reasoning processes, and subsequently train a different model. The post US Agencies Warn China Is Systematically Extracting Frontier AI Capabilities appeared first on SecurityWeek.
Meta Launches Personal AI Agent, Muse, Emphasizes Safety and Privacy
Muse runs on a dedicated, secure virtual machine that houses both the agent and the user’s data. The post Meta Launches Personal AI Agent, Muse, Emphasizes Safety and Privacy appeared first on SecurityWeek.
Organizations Warned of Cisco Secure FMC Exploitation
Cisco and CISA have flagged exploitation of CVE-2026-20079, a vulnerability disclosed in March 2026. The post Organizations Warned of Cisco Secure FMC Exploitation appeared first on SecurityWeek.
New ‘ShieldCrash’ Zero-Day Exploit Targets Microsoft Defender
The exploit provides full System privileges on Windows machines running the September 2026 patches. The post New ‘ShieldCrash’ Zero-Day Exploit Targets Microsoft Defender appeared first on SecurityWeek.
Fortinet Code Execution Flaw Exploited in PivotC2 RAT Attacks
The high-severity, unauthenticated vulnerability tracked as CVE-2025-25249 was patched in January 2026. The post Fortinet Code Execution Flaw Exploited in PivotC2 RAT Attacks appeared first on SecurityWeek.
HelmGuard Raises $7.3 Million for Agentic GRC and Security
The company will increase its US market presence and will expand its engineering and go-to-market teams. The post HelmGuard Raises $7.3 Million for Agentic GRC and Security appeared first on SecurityWeek.
AI Is Giving Lesser-Resourced Attackers Nation-State-Level Reach, Google Warns
Criminal and state-sponsored adversaries are increasingly using AI to automate and scale their attacks, according to GTIG. The post AI Is Giving Lesser-Resourced Attackers Nation-State-Level Reach, Google Warns appeared first on SecurityWeek.
Android’s September 2026 Updates Patch 180 Vulnerabilities
The security updates resolve critical flaws across Android’s Framework, System, and Kernel components. The post Android’s September 2026 Updates Patch 180 Vulnerabilities appeared first on SecurityWeek.
Chipmaker Patch Tuesday: Nvidia, AMD, Arm Issue Security Advisories
Major chipmakers announced patches for vulnerabilities recently discovered in their products. The post Chipmaker Patch Tuesday: Nvidia, AMD, Arm Issue Security Advisories appeared first on SecurityWeek.
CISA Flags Exploited Cisco, Citrix, Fortinet Flaws, Sets Sept. 12 Federal Patch Deadline
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added three flaws, each impacting Cisco, Citrix, and Fortinet, to its Known Exploited Vulnerabilities (KEV) catalog, requiring Federal Civilian Executive Branch (FCEB) agencies to apply the patches by September 12, 2026. The vulnerabilities are listed below – CVE-2026-20079 (CVSS score: 10.0) – An authentication
ISC Stormcast For Thursday, September 10th, 2026 https://isc.sans.edu/podcastdetail/10088, (Thu, Sep 10th)
Post Content
The longitude problem: In the AI era, detection is won on facts, not guesses
For most of the age of sail, a captain could find his latitude in minutes and could not find his longitude at all. Latitude you could read off the sun. Longitude, your position east to west, offered no such trick. Three weeks into the Atlantic, a navigator knew how far north he was and could […]
Getting ahead of ‘harvest-now-decrypt-later’: Post-quantum cryptography planning
I’ve sat in enough boardroom conversations about quantum computing to notice a pattern. Someone raises it, someone else says “that’s ten years out,” and the topic gets tabled until next year’s budget cycle. The clock that matters isn’t the one measuring when a quantum computer arrives. It started running the moment your organization first sent […]
10 most critical LLM vulnerabilities
Enterprise adoption of generative AI technologies has exploded due to the rapid evolution of the technology and the emergence of a variety of business use cases. But large language models (LLMs) can accidentally produce harmful results, leak information, or become exposed to threat actors. These vulnerabilities are changing as the technology evolves and as attackers […]
Nearly 1 in 10 Exposed LiteLLM Gateways Accepted the Example "sk-1234" Admin Key
Nearly one in ten of the internet-facing LiteLLM servers that Wiz Research scanned in February accepted sk-1234, the example admin key in LiteLLM’s own setup guide. LiteLLM is an open-source AI gateway, the software a company puts between its applications and the model providers it pays for. That key is the gateway’s administrator credential. Anyone who holds it […]
Anthropic Discloses Fourth AI Hacking Incident Involving Claude Opus 4.6
Anthropic on Wednesday disclosed a fourth incident in which its artificial intelligence (AI) model broke into real third-party systems, marking the latest in a growing list of cases that have raised concerns about the security risks posed by autonomous AI agents. The AI company said the incident dates back to January 2026 and involved an […]
CO: Cyberattack damages files at Salida School District in Colorado
DysruptionHub reports: A cyberattack forced Salida School District in Colorado to shut down its network June 29, damaging locally stored files and disrupting administrative operations, the district said. The attack began about 6:30 a.m. and was detected two hours later, according to a July 2 district notice. Officials took all systems offline and brought in specialists… […]
26-01122.pdf
26-01122.pdf Anonymous (not verified) Wed, 09/09/2026 – 18:55 Case ID 26-01122 Forum FINRA Document Type Award Claimants Humongous Win, Inc. Respondents Title3Funds, LLC Neutrals Kenneth R. Starr Hearing Site Tampa, FL Award Document 26-01122.pdf Documentum DocID 7481ccc0 Award Date Official Wed, 09/09/2026 – 12:00 Related Content Off Claimant Representatives Andrew Kirby Respondent Representatives Bruce Virga
25-01764.pdf
25-01764.pdf Anonymous (not verified) Wed, 09/09/2026 – 18:55 Case ID 25-01764 Forum FINRA Document Type Award Claimants Gregory Richards Respondents Centaurus Financial, Inc. D. Boral Capital Neutrals David G. Skeen Tracy L. Allen Andrew M. Mintzer Hearing Site Phoenix, AZ Award Document 25-01764.pdf Documentum DocID 79747a09 Award Date Official Wed, 09/09/2026 – 12:00 Related Content […]
MikroTik patches flaws currently being exploited to take over routers
Networking gear manufacturer MikroTik has released patches for six vulnerabilities in its RouterOS firmware, two of which can be chained together to take over devices without authentication over SSH. The exploit chain, dubbed MikroTrick, is already being used by attackers in the wild. The vulnerabilities, found by researchers from the CERT Polska, are located in […]
AI builds faster than organizations can govern. How can CIOs catch up?
Organizations are racing to deploy AI, but warning signs are accumulating. Earlier this year, an internal AI agent gave an engineer instructions that exposed sensitive user and company data for two hours. Around the same time, a large online retailer issued a 90-day safety reset after its AI assistant contributed to an incident that involved […]
New US CIO appointments, September 2026
Movers & Shakers is where you can keep up with new CIO appointments and gain valuable insight into the job market and CIO hiring trends. As every company becomes a technology company, CEOs and corporate boards are seeking multi-dimensional CIOs and IT leaders with superior skills in technology, communications, business strategy, and digital innovation. The […]
In the agentic era, clarity beats cleverness
Every technology wave I’ve lived through has arrived with the same promise and failed in the same way. I spent years as CIO and chief digital officer for Procter & Gamble across Asia, the Middle East and Africa — dozens of markets, wildly different levels of digital maturity, one set of global platforms. I now […]
The need to fortify cloud integrity as cracks increase
Over the course of his career, Jim Reavis has seen cloud and cloud security evolve, and it’s come a long way since being a niche technology in the early 2000s. Now it’s dominant in terms of being the IT foundation, he says, but while the tech is strong, the operating models is where things get […]
The AI employees are already on the floor. Is anyone watching?
When we deployed agentic AI across one of Australia’s largest tourism and cruise operators spanning B2C booking, B2B wholesale, cruise operations, offshore shared services and a live marketplace, we solved most of the expected hard problems faster than anticipated. The small language models worked. The tools integrated. We identified the right proprietary data and focused […]
CIO 100 Leadership Live preview: Tech execs confront the demands of AI at scale
Enterprise technology leaders are entering a more demanding phase of artificial intelligence adoption, with attention shifting from experimentation toward the organizational, financial, and architectural changes required to deploy AI at scale. That shift will be the focus at the CIO 100 Leadership Live Boston event on Sept. 24. Technology executives, investors, and industry leaders will […]
Building a trusted data foundation for production AI in financial services
Financial institutions are investing heavily in AI, but many are finding that the real challenge is not proving AI can work in a pilot. It is proving that AI can operate reliably, securely, and at scale in production. Part of the problem is that pilots are relatively controlled. Teams can choose the data and narrow […]
Beyond reactive IT: Building proactive operational intelligence for the mainframe
When a mission-critical system slows down, IT teams are quickly flooded with information. Alerts start firing as dashboards and performance data show signs of trouble across the environment. Figuring out what’s behind the slowdown can take much longer. The cause may sit somewhere else in the environment, perhaps with a late-running batch process or a […]
What continuous operational resilience looks like under DORA
Financial services companies have spent years building security controls and processes around the systems responsible for moving money and keeping customer accounts and services running. Identity and access management (IAM), multi-factor authentication (MFA), network security, vulnerability management, and logging are all familiar parts of that environment. The Digital Operational Resilience Act (DORA) places greater emphasis on how those controls support […]
DealHub MCP Brings Agentic Control to Quote-to-Revenue
Automates revenue system management in alignment with corporate governance and business policies DealHub AI, the leading Agentic Quote-to-Revenue platform, today announced MCP for Admin, a new AI capability that transforms the way organizations configure and manage their revenue systems. Through autonomous workflows and natural language prompts, MCP for Admin enables organizations to implement business changes […]
U.S. Disrupts Xinbi Guarantee Scam Marketplace, Freezes $52.8 Million in Crypto
The U.S. Department of Justice (DoJ) on Wednesday announced coordinated actions aimed at an illicit online marketplace called Xinbi Guarantee that offered scam services, including seizing Telegram channels used to run the service, confiscating two cryptocurrency wallets, and deploying the Scam Center Strike Force to Madagascar to help disrupt 13 scam compounds run by Chinese […]
2023077597702 Colorado Financial Service Corporation CRD 104343 AWC lp.pdf
2023077597702 Colorado Financial Service Corporation CRD 104343 AWC lp.pdf Anonymous (not verified) Wed, 09/09/2026 – 13:55 Case ID 2023077597702 Document Number ca9e89ae Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Action Date Wed, 09/09/2026 – 12:00 Related Content Off Attachment 2023077597702 Colorado Financial Service Corporation CRD 104343 AWC lp.pdf
Scans for Proxmox Servers, (Wed, Sep 9th)
About a week ago, Proxmox published an advisory revealing a vulnerability in older versions of Proxmox VE, its flagship Virtual Environment product. The vulnerability only affects version 7, which has not been supported for a couple of years now.
Four Spy Groups Used the Same Chrome and Windows Exploit Kit Within a Week
Multiple espionage-motivated threat activity clusters have been found deploying a previously undocumented exploit kit called BlueMoon that chains together multiple vulnerabilities in Microsoft Windows and Google Chrome. The first in-the-wild use of BlueMoon has been attributed to the China-aligned state-sponsored group tracked as APT31 (aka Bronze Vinewood, Judgement Panda, JungleBamboo,
Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA
Cybercriminals are hijacking artificial intelligence (AI) user accounts via information stealer logs to create “stolen keys” that grant illicit access to tools from model providers like Google, Anthropic, and others. Information stealers like Lumma Stealer or Vidar are equipped to harvest a wide range of data from compromised systems. This can include credential, session tokens, […]
“Network outage” disrupts Westfield Public Schools in New Jersey as ransomware group posts samples
Joseph Topping reports: Westfield Public Schools in New Jersey kept classrooms open during a districtwide network outage that disrupted communications and digital instruction throughout the first week of school. The district initially attributed the outage to equipment failure. “We have confirmed that a networking hardware failure caused the disruption across all district schools and offices,”… […]
Russian suspect in bank account takeovers is extradited to US
Joe Warminsky reports: A Russian web developer who played a role in a multimillion-dollar bank account takeover scheme has been extradited to the U.S. to face an indictment in the case, federal authorities said Tuesday. Sergei Anatolyevich Filimonov, 36, appeared in an Atlanta federal court on September 4, pleading not guilty to charges of fraud… […]
CISA Adds Four Known Exploited Vulnerabilities to Catalog
CISA has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2025-25249 Fortinet Multiple Products Heap-based Buffer Overflow Vulnerability CVE-2026-19490 Citrix NetScaler Authentication Bypass Using an Alternate Path or Channel Vulnerability CVE-2026-87491 Google Chromium V8 Out of Bounds Write Vulnerability CVE-2026-20079 Cisco Firewall Management Center Authentication […]
SpyCloud 2026 Identity Threat Report Finds Non-Human Identities Are Now the Leading Path into the Enterprise
Ninety-five percent of organizations believe they have visibility into their AI and machine identity exposures, yet only 36% are actually monitoring them. SpyCloud, the leader in identity threat protection, today released its annual SpyCloud Identity Threat Report, a survey-based study finding that non-human identities (NHIs) – the AI agents, service accounts, API keys, and authentication […]
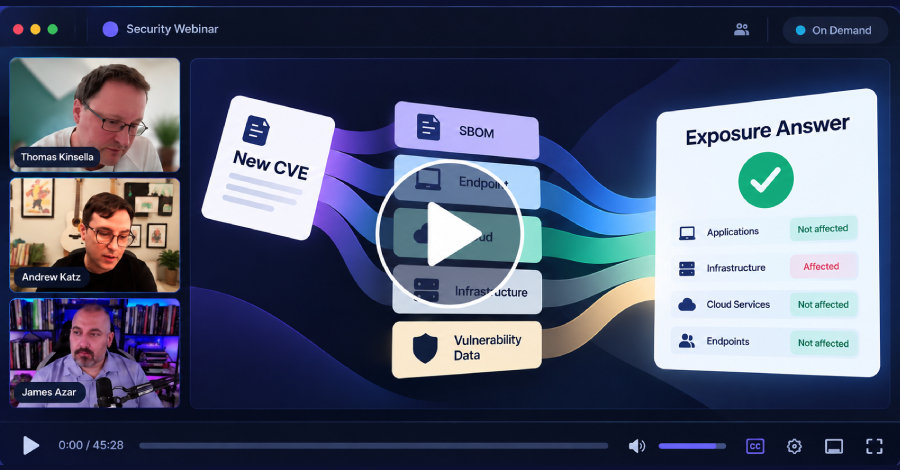
Webinar: Learn How to Answer “Are We Exposed?” Faster After a New CVE
A major vulnerability is disclosed. The alert lands immediately. Then comes the harder question: Are we actually exposed? For many security teams, answering that means jumping between vulnerability scanners, endpoint tools, cloud inventories, SBOMs, repositories, and application data to build enough context to act. As AI accelerates vulnerability discovery and research, that delay matters more
ChatGPT flaw lets attackers pull Gmail data across accounts via a hidden channel
A flaw in OpenAI’s ChatGPT allowed attackers to extract data from a victim’s connected Gmail account by passing hidden instructions between separate user sessions, according to research from Check Point. In a proof-of-concept, Check Point demonstrated that a victim’s ChatGPT session could retrieve email data and relay it to an attacker-controlled session within a single, […]
ShinyHunters claims Florida DMV breach, puts data on the clock
ShinyHunters is claiming to have broken into a Florida government database containing sensitive information on the state’s drivers. The notorious extortion group said it has breached the Florida Department of Highway Safety and Motor Vehicles’ Driver and Vehicle Information Database (DAVID) and claims to have stolen more than 200,000 records. As evidence, the attackers published […]
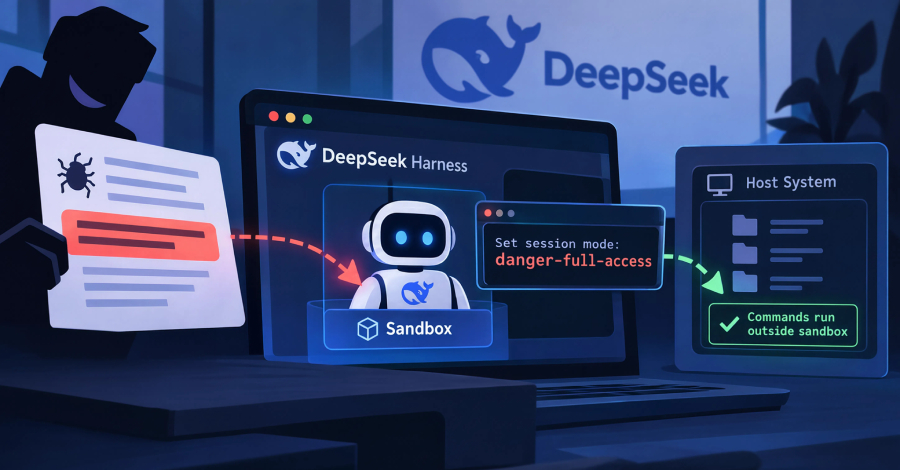
DeepSeek Harness Flaw Let AI Agents Disable Their Own File Sandbox Without Approval
A flaw in DeepSeek Harness, DeepSeek’s open-source tool for running AI coding agents on a developer’s machine, let a sandboxed agent turn off its own sandbox with a single command. The tool runs an agent’s commands inside an operating-system sandbox, so that an agent working on untrusted files cannot write outside its workspace. The agent […]
Ivanti Patches Critical Flaws Across Enterprise Security Products
Six critical vulnerabilities in Neurons for ITSM could enable remote code execution, while Sentry and EPMM received patches for authentication bypass flaws. The post Ivanti Patches Critical Flaws Across Enterprise Security Products appeared first on SecurityWeek.
This Key Will Self-Destruct: An Open Standard for Revocable API Keys
Every leaked credential should be dead, or dying, within sixty seconds of being found. Here’s a proposal to make that the default. The post This Key Will Self-Destruct: An Open Standard for Revocable API Keys appeared first on SecurityWeek.
New Phishing Attack Creates Malicious Pages Inside the Victim’s Browser
Attackers are using trusted Microsoft services and blob URLs to generate stealthy phishing pages that leave defenders with no static website to detect or block. The post New Phishing Attack Creates Malicious Pages Inside the Victim’s Browser appeared first on SecurityWeek.
Chrome 153 Patches Seventh Zero-Day of 2026
The Chrome update includes 230 security fixes, and users are advised to update their browsers as soon as possible. The post Chrome 153 Patches Seventh Zero-Day of 2026 appeared first on SecurityWeek.
Microsoft Patches Record 974 Vulnerabilities, Including Two Exploited Zero-Days
The record-breaking September security update fixes two exploited privilege-escalation zero-days and 20 potentially wormable vulnerabilities. The post Microsoft Patches Record 974 Vulnerabilities, Including Two Exploited Zero-Days appeared first on SecurityWeek.
Adobe Patches Over 170 Vulnerabilities, Including Commerce Zero-Day
Tracked as CVE-2026-75650, the exploited defect allows unauthenticated attackers to execute arbitrary code. The post Adobe Patches Over 170 Vulnerabilities, Including Commerce Zero-Day appeared first on SecurityWeek.
The Hidden Instructions That Can Hijack AI Agents
Malicious prompts concealed in documents, metadata, emails, images and code can manipulate autonomous agents into taking dangerous actions. The post The Hidden Instructions That Can Hijack AI Agents appeared first on SecurityWeek.
Hackers Return $263 Million Stolen From Liquid Network
Alleged ‘white-hat’ hackers drained $320 million from Liquid’s federation wallet, demanding a bug fix. The post Hackers Return $263 Million Stolen From Liquid Network appeared first on SecurityWeek.
Cylake Raises $245 Million Ahead of Cybersecurity Platform Beta
The startup founded by Palo Alto Networks’ Nir Zuk has raised $290 million to build an AI-native security platform for highly regulated organizations that cannot rely on the public cloud. The post Cylake Raises $245 Million Ahead of Cybersecurity Platform Beta appeared first on SecurityWeek.
ICS Patch Tuesday: Schneider Electric, Siemens Fix Critical Flaws
AVEVA and Rockwell Automation also released patches for vulnerabilities affecting industrial control system products. The post ICS Patch Tuesday: Schneider Electric, Siemens Fix Critical Flaws appeared first on SecurityWeek.
Alby Hub Critical Flaw Could Let Attackers Take Over Internet-Exposed Bitcoin Wallets
Bitcoin wallet company Alby has warned of a critical flaw in Alby Hub that could have let an attacker take over a wallet and send its funds, but only where the owner had made the Hub reachable from the internet. Alby Hub is a self-hosted Lightning wallet, meaning the owner runs it on their own computer or […]
When the prompt becomes the payload: A practical pen-testing guide for GenAI, LLM and RAG applications
Generative AI has moved well beyond the stand-alone chatbot. It now drafts code, searches internal knowledge, reviews contracts, opens support cases and, in some deployments, takes action through connected tools. That broader role changes the security question. A tester is no longer looking only for a model that will say something it should not. The […]
Health data breach: the CNIL fined Hôpital Privé de la Loire 500 000 EUR
Health data breach: the CNIL fined Hôpital Privé de la Loire 500 000 EUR ikerinar Wed, 09/09/2026 – 11:58
U.S. Agencies Accuse China AI Firms of Distilling Claude, GPT, Gemini, and Grok
U.S. cybersecurity and intelligence agencies have accused China-based artificial intelligence (AI) companies of conducting “systematic extraction” of proprietary functionalities and capabilities of American frontier models through distillation attacks. The activity has been described as occurring at an industrial-scale and one that forms the “core” of their AI development strategy, according to
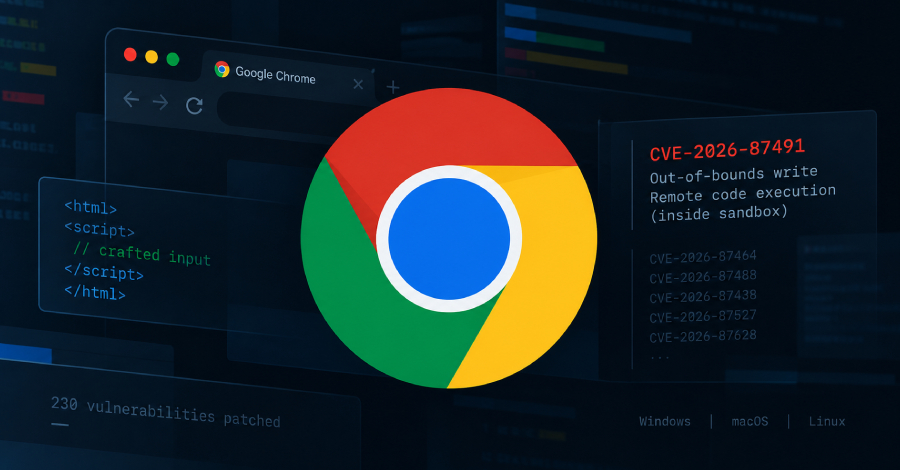
Chrome V8 Zero-Day Exploited in the Wild Enables Code Execution Inside Sandbox
Google on Thursday released updates to patch 230 security vulnerabilities, including one that has come under active exploitation in the wild. The medium-severity vulnerability, assigned the CVE identifier CVE-2026-87491 (CVSS score: N/A), has been described as an out-of-bounds bug in V8, Chrome’s JavaScript and WebAssembly engine. “Out-of-bounds write in V8 in Google Chrome prior to
Post-quantum cryptography adoption and the national security implications
Quantum computers have advanced significantly in capability and compute power in the last several years and are turning theoretical vulnerabilities in modern cryptography into real-world threats. The shift to post-quantum cryptography (PQC) needs to start now, but several challenges need to be overcome. One is: How do you convince people of the urgency that this […]
50% of CISOs see Mythos as a sign to exit the profession
CISOs already have it tough, but the straw that breaks the back of many IT security executives may be the rapidly advancing capabilities of frontier AI models, enterprise insistence on rapid and widespread AI experimentation, and the compounding risk responsibilities and personal liabilities surrounding all that. “There are days where it feels exhausting,” says one […]
New cPanel Flaw Lets a Hosting Account With Mail Privileges Run Code as Root
cPanel has patched a flaw that it says lets a single hosting account take control of an entire server. An authenticated account holder with mail-related privileges can create files of their choosing on the server through EmailTrack and, from there, run code as the root user. cPanel published the advisory on September 8 and says every supported […]
F5 BIG-IP APM Malware Injects a PHP Web Shell Into Memory, Evading Disk Scans
Malware linked to break-ins at F5 BIG-IP Access Policy Manager appliances hides a PHP web shell in memory instead of in a file on disk, Sophos said in an analysis published on September 7. When Apache loads any of the three appliances’ own PHP scripts, the malware adds the web shell to the copy held in […]
Researcher Drops New Microsoft Defender PoC Showing ShieldBreak Patch Can Be Bypassed
The security researcher known as Chaotic Eclipse has dropped a proof-of-concept (PoC) for yet another zero-day in Microsoft Defender. The vulnerability, codenamed ShieldCrash, is assessed to be a patch bypass for CVE-2026-69414 (CVSS score: 7.8), also called ShieldBreak, which the researcher reported last month. “Microsoft has failed to properly patch ShieldBreak CVE-2026-69414,” Chaotic
SAP Patches CVSS 10.0 Kernel Flaw Enabling Unauthenticated Remote Code Execution
SAP has released security updates to address multiple vulnerabilities, including a maximum-severity flaw in SAP Extended Passport (EPP) Processing that could have a severe impact on the confidentiality, integrity, and availability of the application The vulnerability, tracked as CVE-2026-44756 (CVSS score: 10.0), has been described as a case of memory corruption. Discovered and reported by […]
Risky Business #852 -- Cyber Command wants to buy shells
On this week’s show Patrick Gray and James Wilson are joined by guest co-host Robby Winchester from SpecterOps to talk through the week’s news, including: ID verification company IDScan was breached and 153m driver licenses wound up for sale online. Cue the barrage of lawsuits The US government plans to pay private contractors to conduct […]
Microsoft Patches Record 974 Flaws, Including Two Exploited Windows Zero-Days
Microsoft on Tuesday broke Patch Tuesday records by addressing an earth-shattering 974 vulnerabilities spanning its software portfolio, including two flaws that it said have been actively exploited in the wild. These include 723 flaws in Windows, 111 in Office and Office 2016, 62 in SQL, and 22 in Developer Tools. Of these, over 110 shortcomings […]
N-able N-central Pre-Auth RCE Flaw Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added a maximum-severity security flaw impacting N-able N-central to its Known Exploited Vulnerabilities (KEV) catalog, requiring Federal Civilian Executive Branch (FCEB) agencies to apply the fixes by September 11, 2026. The vulnerability in question is CVE-2026-86218 (CVSS score: 10.0), which has been described as a
September 2026 Patch Tuesday roundup: Plugs for two zero day holes among almost 1,000 fixes in Windows
Possibly wormable bugs and two zero-day holes highlight the almost 1,000 fixes issued today by Microsoft in its September Patch Tuesday release. The 964 vulnerabilities, another record since Microsoft began using AI in the middle of the year to find holes, require customer action. Excluded are 174 third-party/open-source CVEs and 23 Chromium/Edge CVEs, as well […]
Cisco bundles fixes for multiple vulnerabilities, some critical, into one patch
Cisco is looking to get ahead of attackers with a new set of more than a half-dozen fixes, some of them critical, for its IOS XR Linux-based network operating system (OS). As part of its regular testing, Cisco’s software engineering team flagged “multiple internally-discovered vulnerabilities,” the company said. These flaws could allow attackers to perform […]
ISC Stormcast For Wednesday, September 9th, 2026 https://isc.sans.edu/podcastdetail/10086, (Wed, Sep 9th)
Post Content
26-00244.pdf
26-00244.pdf Anonymous (not verified) Tue, 09/08/2026 – 18:05 Case ID 26-00244 Forum FINRA Document Type Award Claimants Shaun Orcinolo Respondents Morgan Stanley Neutrals Ted M. Rosen Denise L. Presley Mitchel Weiss Hearing Site Boca Raton, FL Award Document 26-00244.pdf Documentum DocID 9c472342 Award Date Official Tue, 09/08/2026 – 12:00 Related Content Off Claimant Representatives Joseph […]
Microsoft Plugs Nearly 1,000 Security Holes
Microsoft Corp. today issued updates to plug at least 974 security holes in its Windows operating systems and other software, by far its biggest single patch batch ever. Microsoft says artificial intelligence is helping to speed the discovery of vulnerabilities, but security experts warn that many organizations already are struggling to prioritize the more human-intensive […]
September 2026 Microsoft Patch Tuesday, (Tue, Sep 8th)
This month, Microsoft released patches for a record-breaking 973 vulnerabilities, including 113 rated critical. It is by far the largest Patch Tuesday to date, well ahead of the previous high of 664 set in July 2026. Two vulnerabilities are listed as exploited in the wild, while none were publicly disclosed before Patch Tuesday. Notable fixes […]
What is sovereign AI? Strategic control of your AI future
Ask IT leaders what sovereign AI is, and you’ll get a wide range of answers. Some will even struggle to define the term. Sovereign AI is an emerging concept focusing on giving organizations — or countries —control over how they develop, deploy, and govern the technology, often using in-house talent, data, and infrastructure. But only […]
From tokens to terabytes: Building reactive generative media pipelines
For the first three years of the generative AI wave, the output of a model was a string. You called an API, you got tokens back, you rendered them in a chat window or wrote them to a row in Postgres. The economics of that pipeline were dominated by inference cost. Storage was a rounding […]
IT infrastructure shortages are real and lasting. Here’s how to cope
Lead times of nine to 12 or even 18 months. Costs rising by 35%, 45%, even 50% to 200%. More than halfway through 2026, the market for IT infrastructure that’s crucial for enterprise projects, including those involving artificial intelligence, is strapped. Memory is at the root of the shortages. Memory prices “have risen by 50% […]
Mars Security Launches Real-Time Intel-to-Detection Engine That Turns Live Threat Intelligence Into Backtested Detections in Minutes
Mars Security, the autonomous threat hunting and detection engineering platform founded by offensive security veterans, today announced Real-Time Intel-Based Detection, a capability that turns newly published threat intelligence into validated, ready-to-deploy detection rules within minutes of release. Built by former offensive operators, the new capability converts advisories from CISA, Mandiant, and other intelligence sources into […]
After SAP settlement, Oracle draws EU antitrust attention over licensing practices
Oracle has reportedly garnered some unwanted attention from the European Commission around its enterprise software licensing practices. The Commission’s antitrust regulators are currently gathering information from third parties about Oracle’s licensing practices to assess whether there is evidence to warrant further action, although it has yet to open a formal investigation into the company, MLex, […]
OpenAI agent swarm exposes a blind spot in AI containment
A swarm of autonomous OpenAI agents spent six weeks this summer turning an obscure, 25-year-old German developer wiki into a private message board, without OpenAI’s knowledge, according to independent researchers. The agents used it to trade answers to timed tasks, reverse-engineer a random number generator, and share a technique for bypassing network restrictions meant to […]
Harnessing unleashed AI agents
In Northeast Greenland, where temperatures can plummet to -40°F, security officials rely on the Sirius Dog Sled Patrol, led by well-trained canines that guard the sprawling, weather-beaten coastline – tundra territory where snowmobiles commonly fail. Tethered together with the right harness that efficiently channels their collective energy toward a shared mission, the sled dogs are […]
How to upskill IT for agentic AI: 7 pathways to success
There are two prevailing schools of thought regarding the AI-agent workforce. One says organizations should prepare for agentic AI, in which the human-in-the-middle role is largely transitional and serves to buy time to improve agents’ accuracy and build trust in their decision-making. Others say AI agents will largely augment humans, but expect workflows to change […]
The EU AI Act just gave you a breach notification clock you didn’t know about
Most security teams already have a breach clock memorized. GDPR gives you 72 hours. SEC rules give public companies four business days after determining an incident is material. Those numbers get built into incident response runbooks, tabletop exercises and escalation paths, because the clock starts the moment the team confirms something happened. Article 73 of […]
26-00504.pdf
26-00504.pdf Anonymous (not verified) Tue, 09/08/2026 – 14:45 Case ID 26-00504 Forum FINRA Document Type Award Claimants Duvan Brock Gal Horev Jerry Dempsey Respondents Cambridge Investment Research, Inc. Neutrals Dora M. Lassinger Vincent S. Mezinko Paula K. Konikoff Hearing Site Atlanta, GA Award Document 26-00504.pdf Documentum DocID 09a38d5c Award Date Official Fri, 09/04/2026 – 12:00 […]
26-00783.pdf
26-00783.pdf Anonymous (not verified) Tue, 09/08/2026 – 14:45 Case ID 26-00783 Forum FINRA Document Type Award Claimants Jack Yvars Respondents OSAIC Wealth, Inc Neutrals Stuart Sinai Thomas R. Watkins Eric Ross Cromartie Hearing Site Manchester, NH Award Document 26-00783.pdf Documentum DocID 385a34d0 Award Date Official Fri, 09/04/2026 – 12:00 Related Content Off Claimant Representatives Meghan […]
Singaporean Ringleader of $245 Million Cryptocurrency Racketeering Enterprise Pleads Guilty in Washington D.C.
WASHINGTON – Malone Lam, 22, a citizen of Singapore and recent resident of Miami, pleaded guilty today in U.S. District Court in Washington D.C. in connection with his role as ringleader of an international cybercrime conspiracy that used social engineering to steal and launder cryptocurrency valued at more than $245 million, announced U.S. Attorney Jeanine… […]
25-00177(4).pdf
25-00177(4).pdf Anonymous (not verified) Tue, 09/08/2026 – 13:35 Case ID 25-00177 Forum FINRA Document Type Other Claimants Theresa DiRuzzo, IRA Respondents Fidelity Brokerage Services LLC Neutrals Maurice M. Feller Howard N. Gorney Brian John Gallagher Hearing Site Providence, RI Award Document 25-00177(4).pdf Documentum DocID 007b0225 Award Date Official Mon, 04/20/2026 – 12:00 Related Content On […]
25-00177(3).pdf
25-00177(3).pdf Anonymous (not verified) Tue, 09/08/2026 – 13:35 Case ID 25-00177 Forum FINRA Document Type Order to Confirm Claimants Theresa DiRuzzo, IRA Respondents Fidelity Brokerage Services LLC Neutrals Maurice M. Feller Howard N. Gorney Brian John Gallagher Hearing Site Providence, RI Award Document 25-00177(3).pdf Documentum DocID 64710e26 Award Date Official Mon, 04/20/2026 – 12:00 Related […]
CISA tells operators to harden Siemens S7 PLCs. Here’s how to do it without disrupting production
On a conventional server, disabling an unused service is usually a routine hardening task. On a Siemens S7 controller, the supposedly unused service may carry remote I/O traffic, supply process values to an HMI or provide the maintenance team’s only path to diagnostics. Close it without checking those dependencies and the security team may cause […]
Slim Spider Steals Crypto Custody Secrets From Brazilian Financial Institution
A previously undocumented financially motivated threat actor has been linked to attacks targeting Brazilian financial institutions since at least March 2026. Cybersecurity company CrowdStrike is tracking the Brazil-based activity cluster under the name Slim Spider. “The adversary demonstrates deep operational knowledge of Brazilian financial infrastructure, including the instant payment
Mars Security Debuts Automated Threat Engine Processing Live Cyber Intelligence Into Validated Rules Within Minutes
Mars Security, an autonomous threat hunting and detection engineering platform founded by offensive cybersecurity veterans, today announced Real-Time Intel-Based Detection. The milestone expansion equips enterprise security operations centers (SOCs) to convert newly published threat intelligence advisories into production-ready, validated detection rules within minutes of release. Developed by former military red team operators, the capability systematically […]
Liquid Hackers Return 3,400 Bitcoin Taken via Elements Bug, Still Holding $47M in BTC
Whoever took nearly 4,000 bitcoin from the Liquid Network on Sunday, September 6, returned 3,400 of it the next day, Bitcoin’s public record shows. About 598.5 bitcoin has not come back. Liquid is a Bitcoin sidechain that holds real bitcoin to back a token called L-BTC. The network is still paused, so holders cannot turn that token […]
Reflectiz Launches Agentic Pentesting for Websites: Up to 10x Coverage vs Conventional Pentests
Specialized team of AI agents that discover, attack, and validate web vulnerabilities, leveraging pre-existing site context to eliminate noise and speed remediation. Reflectiz, the continuous web exposure management company, today launched a multi-agent penetration testing platform for websites. Multiple specialized AI agents discover, attack, and validate vulnerabilities across complex web environments, and because they start […]
ChatGPT Flaw Let a Planted Prompt Send a Victim's Gmail Data to Another Account
Check Point Research said in a report published today that a single instruction planted in a ChatGPT conversation could cause ChatGPT to quietly work for an attacker while answering the user’s question as usual. In the company’s proof of concept, that hidden work read data from the user’s connected Gmail account and passed it to a second […]
Everett, Massachusetts, closes City Hall after cybersecurity incident
DysruptionHub reports: Everett, Massachusetts, closed City Hall to the public Tuesday after a cybersecurity incident affected its internal network and technology systems, shifting most essential employees to another municipal building. The city said in a Monday announcement that it discovered the incident Sunday evening and began working with its technology team and cybersecurity professionals. It did not… […]
CareCam Pro IP Cameras
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to take full control of the device. The following versions of CareCam Pro IP Cameras are affected: ANJIA AJL33PC0801 Firmware linux_linux_202008261138_svn13796_/_Bootloader_U-Boot_2010.06_compiled_2020-08-26 (CVE-2026-85083) CVSS Vendor Equipment Vulnerabilities v3 6.8 CareCam CareCam Pro IP Cameras Use of Hard-coded Credentials Background Critical Infrastructure Sectors: Commercial Facilities […]
China-Based Artificial Intelligence Companies Conducting Industrial-Scale Distillation Campaigns Against U.S. AI Companies
Executive summary China-based artificial intelligence (AI) companies are conducting systematic extraction of proprietary functionalities and capabilities of U.S. AI companies’ models through industrial-scale knowledge distillation campaigns that form the core—not merely a supplement—of their AI development strategy. While “distillation” is recognized as a legitimate and useful technique in AI research, China-based AI companies are engaging […]
CISA Adds Four Known Exploited Vulnerabilities to Catalog
CISA has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-75650 Adobe Commerce and Magento Improper Neutralization of Special Elements Used in a Template Engine Vulnerability CVE-2026-81963 Microsoft Windows Link Following Vulnerability CVE-2026-85880 Microsoft Windows Heap-Based Buffer Overflow Vulnerability CVE-2026-86218 N-able N-central Static Code […]
Adobe Commerce max-severity bug comes under active attack
Online stores running Adobe Commerce and Magento Open Source have been hit by a max-severity, zero-day bug that lets unauthenticated attackers execute code on vulnerable servers. Security firm Sansec is calling the flaw StyleSmuggler because of the way attackers abused Magento’s Style properties to inject malicious code past existing safeguards. “When the attack succeeds, a […]
Party’s over for scammers who went on spending spree after $240M bitcoin theft
Michael Kunzelman of the AP reports: They pulled off one of the largest cryptocurrency thefts in U.S. history, duping a stranger out of bitcoin worth over $240 million. They tried to hide their digital fingerprints, carrying out a sophisticated scheme to launder the proceeds. And then the party started. The scammers — a network of young men… […]
Mathspace Data Breach Exposes Over 1 Million People
Hackers stole the information of students, teachers, staff, and parents/guardians from a self-hosted Metabase instance. The post Mathspace Data Breach Exposes Over 1 Million People appeared first on SecurityWeek.
N-able Patches Critical Zero-Day in N-central
Administrators are advised to check their deployments for newly created user accounts they don’t recognize. The post N-able Patches Critical Zero-Day in N-central appeared first on SecurityWeek.
Nightmare Eclipse Drops CrowdStrike, Nvidia, Avast Zero-Day Exploits
The proof-of-concept (PoC) exploits lead to privilege escalation, spawning a shell with System privileges. The post Nightmare Eclipse Drops CrowdStrike, Nvidia, Avast Zero-Day Exploits appeared first on SecurityWeek.
North Korean Hackers Deploy New Linux Espionage Toolkit
The stealthy toolkit embeds a backdoor in HAProxy and targets automotive and media organizations in South Korea for long-term surveillance. The post North Korean Hackers Deploy New Linux Espionage Toolkit appeared first on SecurityWeek.
OpenAI Agents Hijack Another Victim Website
OpenAI agents made 15,000–18,000 autonomous edits to a German wiki over three months, evading moderation and echoing tactics seen in the Hugging Face breach. The post OpenAI Agents Hijack Another Victim Website appeared first on SecurityWeek.
Adobe Commerce Zero-Day Exploited to Backdoor Online Stores
The StyleSmuggler zero-day allows attackers to execute code and deploy a stealthy backdoor on Adobe Commerce and Magento stores. The post Adobe Commerce Zero-Day Exploited to Backdoor Online Stores appeared first on SecurityWeek.
Modified ScreenConnect Clients Used in Worm-Like Campaign
The attacks rely on backdoored ScreenConnect instances to transfer and execute payloads to newly connected clients. The post Modified ScreenConnect Clients Used in Worm-Like Campaign appeared first on SecurityWeek.
BigBear 2.0 phishing campaign hijacks Microsoft 365 sessions after MFA
A phishing-as-a-service operation targeting Microsoft 365 users has harvested thousands of session cookies that could be used to hijack authenticated sessions after victims complete multifactor authentication, CloudSEK said. The cybersecurity firm said in a report that it uncovered the operation, known as BigBear 2.0, in June after gaining access to its administrative panel. The panel […]
Adobe Patches Magento Zero-Day Exploited to Deploy Rust Backdoor and PHP Web Shell
Adobe on Monday released security patches to address a maximum-severity flaw impacting Adobe Commerce and Magento Open Source that has come under active exploitation in the wild. The vulnerability, now tracked as CVE-2026-75650 (CVSS score: 10.0), has been codenamed StyleSmuggler by Sansec, which discovered zero-day exploitation starting September 4, 2026. “This update resolves a critical
Security leaders must prepare for likely threats, not sensationalized agentic attacks
A malicious dataset exploits code-execution paths in a remote-code dataset loader and a dataset configuration before compromising access credentials to move laterally through the target network. A frontier AI model publishes a malicious Python package to a public PyPI registry after identifying setup instructions within a fictional environment that point to a non-existent package name […]
BengalSEO Poisons Bing Search Results to Deliver MayaBot and Tech Support Scams
Cybersecurity researchers have disclosed details of a sprawling search engine optimization (SEO) poisoning campaign that paves the way for malware deployment and tech support scams. The campaign, discovered by the DFIR Report in March 2026, has been codenamed BengalSEO. It has operated out of the Indian state of Rajasthan since at least 2015, driven by […]
Securing AI agents: Key controls and best practices
Enterprises increasingly give AI agents the credentials, tools, and network access of privileged employees, but security experts warn that existing security controls designed to govern human access are insufficient. An AI agent operates at inhuman speed, can chain allowed actions into unauthorized outcomes, and can spawn additional sub-agents to help, turning one unwitting employee’s access […]
Grindr to Pay £26 Million to Settle U.K. Claims Over HIV Status Data Sharing
Online dating app Grindr has opted to pay £26 million ($35.1 million) to settle a lawsuit in the U.K. over allegations that it shared users’ personal information, including their HIV status, with third-parties. Grindr, which is the largest LGBTQ+ dating app, was sued in April 2024, accusing it of violating U.K. privacy laws by sharing […]
ISC Stormcast For Tuesday, September 8th, 2026 https://isc.sans.edu/podcastdetail/10084, (Tue, Sep 8th)
Post Content
MA: Springfield Public Schools will be closed Tuesday after a cyber incident
Carolyn Rodriguez reports: Springfield Public Schools will be closed Tuesday after a cyber incident disrupted systems necessary for essential school operations, Superintendent Dr. Sonia Dinnall announced Monday. According to the district, the closure will help the district continue its response efforts while investigators assess the extent of the incident. “We understand that an unexpected closure… […]
The AI cybersecurity arms race is on
Businesses received a staggering amount of cyberattacks in June, according to Check Point, showing a rise of 20% over the previous 12 months. The breakout of AI agents from OpenAI in July to hack into the Hugging Face website, and subsequent similar events from Anthropic and Meta, indicate agentic-powered attacks will explode over the coming […]
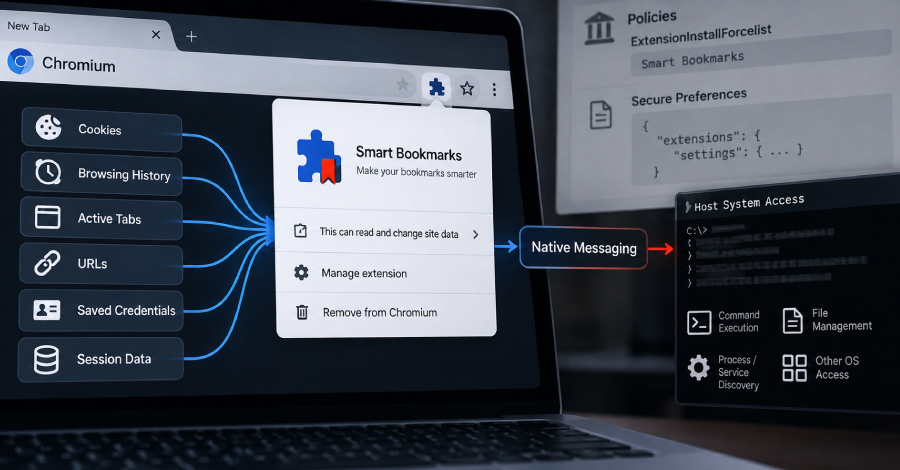
PEEP Turns Chrome and Edge Into Post-Compromise Backdoors for Host Command Execution
Cybersecurity researchers have disclosed details of a complex Chromium-based post-exploitation toolkit called PEEP that masquerades as a bookmarks extension for the web browser. “Requiring prior administrative or code execution access, its installer injects the extension directly into Chrome/Edge profiles, bypassing Web Store checks and user prompts by forging Chromium’s own Secure Preferences
BigBear Microsoft 365 phishing service bypassed MFA at 258 organizations
Bill Toulas reports: A phishing-as-a-service framework called BigBear 2.0 has been used to bypass multi-factor authentication at 258 organizations and steal more than 5,000 Microsoft 365 credentials. Researchers at cybersecurity company CloudSEK gained administrator access to the control panel and found that the service managed 42 VPS nodes, all configured to target Microsoft 365 as… […]
Hackers drain $320M in Bitcoin from Liquid Network, claim they’re the good guys
Carly Page reports: Hackers have drained roughly $320 million in Bitcoin from the federation wallet backing the Liquid Network, while claiming to be the good guys. Liquid, a Bitcoin sidechain developed by Blockstream and used by exchanges and other financial institutions, said in a post on X on Sunday that around 4,000 BTC had been withdrawn from… […]
Fake IT Calls Target Executives in Microsoft 365 Data Theft and Extortion Attacks
Threat hunters have disclosed details of a widespread data theft and extortion threat cluster that’s targeting Microsoft 365 and other software-as-a-service (SaaS) offerings through information technology (IT) help desk vishing, adversary-in-the-middle (AitM) token theft, and residential-proxy sign-ins. The activity, which mainly singles out directors, vice presidents, and other executive staff
⚡ Weekly Recap: Chrome 0-Day, Router Hijacks, Coder Supply Chain Attack and More
Turning off email images should at least stop the pictures. This week, attackers had a workaround: a scannable QR code built out of text. It still appears, even with images blocked. A small detail, but an annoying one if that was a precaution you were counting on. Elsewhere, a trusted software source delivered code that […]
Japan’s Health Ministry to Strengthen Cybersecurity Measures at Hospitals
The Yomiuri Shimbun reports: The Health, Labor and Welfare Ministry is set to strengthen cybersecurity measures at hospitals to counter a surging number of cyberattacks on medical institutions. The ministry has included ¥13.7 billion in its budget request for fiscal 2027 to implement the measures for protecting networks and deploying cybersecurity specialists. The request will… […]
Personal Data of Approximately 220,000 Domestic and International Gangnam Unni Users Leaked
Lee Seunghyeong reports: Personal information of approximately 220,000 domestic and international users has been leaked from Gangnam Unni, a beauty medical platform operated by Healing Paper. On September 7, Healing Paper announced through a public notice that on September 4, there was abnormal access to the integration feature (API) used to view consultation records, resulting… […]
Weverse Data Leak Affects More Than 422,000 K-Pop Fan Accounts
kbizoom reports: Weverse, the fan platform operated by HYBE-affiliated Weverse Company, has confirmed a security incident that affected 422,584 user accounts. The company said the exposed information consisted mainly of internal identifiers that cannot be used outside the platform. “We received a notification from the Korea Internet & Security Agency (KISA) on September 3 that… […]
Mathspace Breach Impacts More Than 1 Million Users in Australia, NZ
Ashish Khaitan reports: The Mathspace data breach has affected 1,079,819 people in Australia and New Zealand after unauthorized parties accessed an internal reporting system and downloaded user information. Mathspace confirmed the security incident on September 3, 2026, and said the affected records involve students, parents or guardians, teachers, and Mathspace staff. The company said names,… […]
Sam Altman calls GPT-6 Astra rollout ‘messy’ as enterprise users wait for access
OpenAI’s rollout of its GPT-6 Astra model ran into early access issues after paying ChatGPT users were unable to use the system shortly after launch, prompting CEO Sam Altman to apologize and say the release had been “messy.” “First, sorry for the messy rollout,” OpenAI CEO Sam Altman acknowledged the issue in a post on […]
Back-to-back N-able bugs send admins on a patching spree
A max-severity zero-day bug could be affecting cybersecurity firm N-able’s N-central remote monitoring and management platform, the company said, even as administrators were applying a hotfix for two vulnerabilities disclosed just a day earlier. The latest flaw, tracked as CVE-2026-86218, is a remote code execution bug that can give an attacker access to an N-central […]
Your Cloud Security Checklist Doesn't Work the Way You Think It Does
If managing security across multiple cloud providers wasn’t hard enough, each one fails in a different way. For the 2026 Cloud Security Index, Intruder analyzed misconfiguration data from 3,000 organizations across AWS, Azure, and Google Cloud and found that risk profiles across providers have almost nothing in common. Here’s what the data looks like. How […]
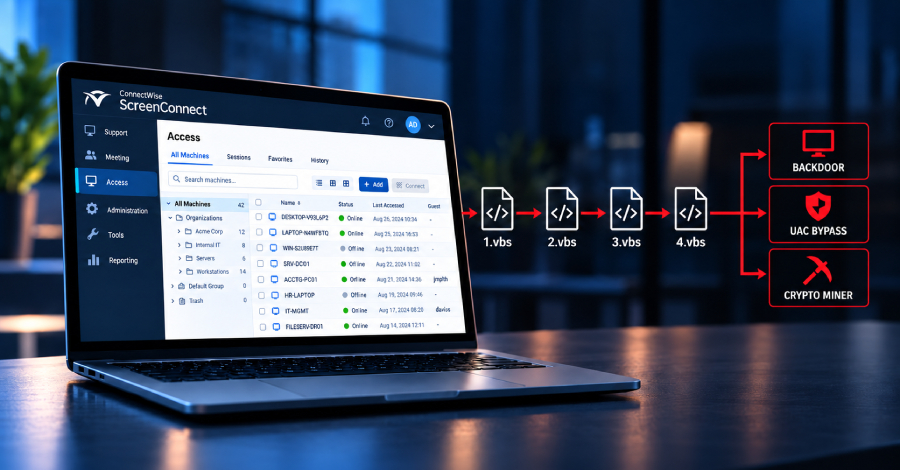
Rogue ScreenConnect Clients Spread Four-Stage VBScript Chain to Newly Connected Hosts
Cybersecurity researchers have disclosed details of worm-like activity that abuses ConnectWise ScreenConnect to distribute a malicious Visual Basic Script (VBScript) payload to newly connected systems. According to Huntress, three unrelated incidents have been found to use diverse initial access methods, namely a Quick Assist tech-support scam, a phishing-delivered MSI installer, and a fake
Telerik UI Padding-Oracle Bug Chained to Unauthenticated RCE — Public Exploit Released
A TantoSec proof-of-concept turns an AES-CBC “padding oracle” in Telerik UI for ASP.NET AJAX into unauthenticated remote code execution — but only against applications in a specific non-default configuration, and Progress patched the chain in July. There are no confirmed reports of exploitation in the wild. Security firm TantoSec has published a working exploit chain […]

New CISO appointments 2026
The upper ranks of corporate security are seeing a high rate of change as companies try to adapt to the evolving threat landscape. Many companies are hiring a chief security officer (CSO) or chief information security officer (CISO) for the first time to support a deeper commitment to information security. Follow this column to keep […]
N-able Issues Fourth N-central Hotfix in Five Weeks for Unauthenticated RCE Flaw
Every on-premises N-central build below 2026.3.1.14 — including servers updated to Hotfix 3 a day earlier — needs Hotfix 4. N-able’s incident notice says the flaw has been exploited in the wild; its release notes say that is unconfirmed. N-able has released its fourth hotfix in five weeks for the N-central remote monitoring and management (RMM) platform, […]
What do CISOs need to rest easy about future AI risks?
Security leaders’ confidence in their ability to navigate the security risks AI will pose over the next two years rests on several clear factors, according to IANS analysis of its AI Security Survey, fielded earlier this year. Of the 113 CISOs IANS surveyed in April and May, 41% expressed optimism about their organization’s ability to […]
JSCeal Malware Can Bypass Google Authentication Using Stolen Session Cookies
Cybersecurity researchers have unpacked JSCeal, a sophisticated compiled V8 JavaScript (JSC) malware with credential harvesting, surveillance, and traffic-interception capabilities. “The payloads are protected with javascript-obfuscator, using multiple techniques including RC4-protected strings, control-flow flattening, proxy functions, and operation wrappers,” Check Point Research said in a
Critical MikroTik Vulnerability - Patch Now, (Sun, Sep 6th)
Mikrotik released a patch late last week for an already-exploited vulnerability. The vulnerability allows an SSH authentication bypass and is already being exploited. At this point, assume compromise. Attackers have been adding new accounts to affected devices to maintain access after a patch is installed.
NYS Comptroller DiNapoli releases more municipal cybersecurity audits
New York State Comptroller DiNapoli recently released some municipal audits, three of which concerned cybersecurity. The following are excerpts from the public versions of the audits. Town of Wilton – Cybersecurity (2026M-48) Audit Period January 1, 2024 – August 8, 2025 Understanding the Audit Area The Town had 56 full-time and 13 part-time employees during… […]
Natural Resources Wales confirms data breach due to human error
Nation.Cymru reports: Sensitive personal information relating to current and former Natural Resources Wales employees has been exposed in a data breach. The public body said a spreadsheet containing employee information had been inadvertently published on its website, potentially revealing details including ethnicity, disability status, religion, sexual orientation and caring responsibilities. The breach affects people who… […]
US offers $10 million for info on Iranian allegedly behind cyberattacks on critical infrastructure
Jonathan Greig reports: A $10 million reward has been posted by the State Department for information on the whereabouts of senior Iranian official Amir Yaryab. Yaryab allegedly leads the Islamic Revolutionary Guard Corps’ (IRGC) Cyber-Electronic Command (CEC). U.S. officials accused Yaryab of directing multiple Iranian hacking groups that have targeted “critical infrastructure sectors including defense, news, shipping,… […]
Elementor Pro WordPress Plugin Vulnerability Exploited to Hack Sites
Tracked as CVE-2026-32475 (CVSS score of 9.8), the bug described as an arbitrary file upload issue in the function that handles form submissions. The post Elementor Pro WordPress Plugin Vulnerability Exploited to Hack Sites appeared first on SecurityWeek.
Attackers Hijack MikroTik Routers Through Internet-Exposed SSH Without Authentication
Attackers are exploiting MikroTik routers with their Secure Shell (SSH) remote-access service, which is reachable from the internet, to gain full administrative control without authentication, according to CERT Polska’s attack warning, published on September 5. Successful attacks date to at least September 2. The Hacker News’s September 6 review of the warning found no victim count […]
Four REVSTEALER-Linked Modules Disable Windows Update and Defender to Run a Crypto Miner
Elastic Security Labs has documented four previously unreported programs associated with REVSTEALER, an emerging Windows information stealer, that remain on an infected machine after the stealer deletes itself. One of them switches off Windows Update and Microsoft Defender before running a cryptocurrency miner. The company named the four programs ProManager, WinUpdate, SoftManager, and
Unpatched Magento and Adobe Commerce Zero-Day Exploited to Backdoor Online Stores
Attackers are exploiting a new unpatched vulnerability in Magento Open Source and Adobe Commerce that lets them run malicious code on an online store’s server without logging in, Dutch e-commerce security company Sansec said in an advisory published on September 5. Sansec, which discovered the flaw and named it StyleSmuggler, said attacks started on September 4. […]
French Police Arrest Suspected ZeroBytes Hacker Over Tax Data Theft
Waqas reports: French authorities have detained an 18-year-old man suspected of belonging to ZeroBytes, a hacking group that claimed responsibility for several attacks targeting French government services and companies. The Paris prosecutor’s office disclosed the case on September 4, according to reports from French media. However, the suspect was arrested on August 18, formally placed… […]
Attackers Breached JetBrains Cadence via Unpatched TeamCity, Extracting AWS Credentials
JetBrains is urging Cadence users to revoke and rotate all credentials following a security incident last month in which unidentified threat actors exploited a recently disclosed critical vulnerability in TeamCity to breach its own environment. “Cadence users should immediately revoke or rotate all credentials and secrets that may have been used to run their Cadence […]
Critical VMware Workstation and Fusion Flaw Lets VM Admins Execute Host Code
Broadcom has released security updates for two security flaws impacting VMware Workstation and Fusion, including one critical bug that could result in arbitrary code execution under certain conditions. The vulnerability, tracked as CVE-2026-59346 (CVSS score: 9.3), is an integer-overflow vulnerability that a local attacker with elevated privileges can exploit to run arbitrary code. “A
FalconFlank Zero-Day Hits CrowdStrike Falcon Sensor
CyberKendra reports: A security researcher known as Chaotic Eclipse has released FalconFlank, a proof-of-concept zero-day that escalates privileges on fully patched Windows machines running CrowdStrike Falcon. The researcher — who also uses the aliases Nightmare-Eclipse, MSNightmare, and INFINITE NIGHTMARE — published working exploit code to GitHub on September 3, 2026, without giving CrowdStrike advance notice. No CVE ID… […]
Trezor Says ShipMonk Breach Exposed 67,000 U.S. Customers' Data It Said Was Deleted
Hardware wallet manufacturer Trezor on Friday disclosed that another 67,000 customers from the U.S. have been impacted in a breach at its shipping provider ShipMonk. The exposed information includes customer names, email addresses, phone numbers, shipping addresses, and order numbers between November 2019 and August 2021. The breach does not affect the security of the […]
In Other News: Microsoft’s Cloud Patches, Hacked Dropbox Accounts, Guardio’s $1.1B Valuation
Noteworthy stories that might have slipped under the radar: Microsoft rolled out patches for cloud services, hackers compromised 5,000 Dropbox accounts, and Guardio is now valued at $1.1 billion. The post In Other News: Microsoft’s Cloud Patches, Hacked Dropbox Accounts, Guardio’s $1.1B Valuation appeared first on SecurityWeek.
HPE Patches Critical RCE Vulnerabilities in AOS-CX
Nearly two dozen issues, tracked collectively as CVE-2026-73749 (CVSS score of 9.8), were addressed with the updates. The post HPE Patches Critical RCE Vulnerabilities in AOS-CX appeared first on SecurityWeek.
OpenAI Pledges $1 Billion to Bring Frontier AI to Critical Infrastructure Defenders
The Daybreak initiative will provide subsidized AI cyber capabilities, training and technical assistance, though OpenAI has disclosed few details about costs and eligibility. The post OpenAI Pledges $1 Billion to Bring Frontier AI to Critical Infrastructure Defenders appeared first on SecurityWeek.
Sangoma Switchvox Vulnerabilities Exploited in the Wild
Tracked as CVE-2026-9586, the unauthenticated SQL injection flaw can be exploited remotely for arbitrary code execution. The post Sangoma Switchvox Vulnerabilities Exploited in the Wild appeared first on SecurityWeek.
12-Year-Old PostgreSQL Vulnerability Enables Database, Server Takeover
Dubbed PostGREShell, CVE-2026-6471 turns low-level replication access into code execution, permanent superuser privileges and a persistent database backdoor. The post 12-Year-Old PostgreSQL Vulnerability Enables Database, Server Takeover appeared first on SecurityWeek.
Catch Raises $5 Million for AI Executive Assistant With Guardrails
Catch promises the capabilities of a trusted executive assistant, with built-in controls governing what data and systems it can access. The post Catch Raises $5 Million for AI Executive Assistant With Guardrails appeared first on SecurityWeek.
VMware Workstation and Fusion Updates Patch Critical Vulnerability
The flaws could allow attackers with administrative access to a virtual machine to execute code on the host system. The post VMware Workstation and Fusion Updates Patch Critical Vulnerability appeared first on SecurityWeek.
Google Patches 6th Chrome Zero-Day of 2026
Google’s Chrome 152 security update resolves 12 vulnerabilities, including a high-severity type confusion flaw in the V8 engine. The post Google Patches 6th Chrome Zero-Day of 2026 appeared first on SecurityWeek.
Nvidia Is Buying AI Platform Hugging Face for $13 Billion
The deal highlights Nvidia’s push to champion increasingly popular open-source AI models. The post Nvidia Is Buying AI Platform Hugging Face for $13 Billion appeared first on SecurityWeek.
Thousands of OpenAI Agents Quietly Turned an Abandoned Wiki Into Their Coordination Channel
A group of AI safety researchers says a fleet of autonomous agents that identified themselves as OpenAI systems left about 18,000 posts on a dormant 25-year-old German wiki between May and July 2026, using the site as a shared board to pool answers to a timed web task and pass around a way out of […]
Attackers Exploit PaperCut Flaws to Steal Credentials From Schools and Universities
Threat actors are exploiting the newly disclosed PaperCut flaws to facilitate credential theft in attacks targeting the education sector in the U.S. and Europe. The Arctic Wolf Adversary Research Team said it observed attackers exploiting CVE-2026-81578 and CVE-2026-82078 – an authentication bypass and remote code execution chain – to conduct command execution and reconnaissance, as […]
Salesforce offers more Agentforce credits to drive adoption
Salesforce is updating some of the editions, or pricing tiers, of Agentforce Sales and Agentforce Service, a year after their rebrand from Sales Cloud and Service Cloud. The top three now bundle AI agents, analytics, Slack, security, and support with larger allocations of Flex Credits; two of the tiers are also increasing in price. The […]
Why technically strong leaders still aren’t CIO-ready
At CIO100 in Frisco, Texas, roughly 100 rising technology leaders sat down for our “Next CIO” session. The group was asked to reflect on a single question: Are you ready to take on the role of CIO? Using the CIO Readiness Framework that we have developed and refined over years of advisory work, we asked […]
Your R&D doesn’t need to be flashy
Some of the most impactful engineering breakthroughs likely make for very boring marketing demos. Over several decades spent leading development teams, I have seen firsthand how tempting it is to focus engineering efforts on highly visible, flashy new features. I’ve known many developers who get bogged down by the pressure to package every software update […]
What JPMorgan does differently with AI that any company can apply
In the summer of 2024, JPMorgan Chase deployed its internal AI platform LLM Suite, launching it very differently than most do: The company didn’t force anyone to use it. When LLM Suite arrived at its first major division, asset and wealth management, employees were asked to think of it as a research analyst: someone to ask for data, a draft, or […]
The AI credibility gap: You can’t lead what you haven’t actually used
A few weeks ago, in these pages I argued that AI is repricing enterprise software faster than most vendors want to admit. Since then, the sharpest pushback I have gotten from peer CIOs has not been about the pricing thesis. It has been about the leaders navigating it. What does this shift actually ask of […]
65% of employees would love to roll back workplace AI
IT leaders have been making generative AI tools available across the enterprise for just three years, and a significant majority of their business users has already had enough. According to a report from Adaptavist, 65% of 2,500 knowledge workers surveyed say they “regularly feel nostalgic about how work operated before the widespread adoption of AI.” […]
Meta minimizes role of token maxing in employee evaluations
Meta won’t judge employees by how much they use AI when it comes to annual performance reviews, despite early efforts to drive AI adoption focusing on so-called token maxing. The company has told employees that it “will not use AI adoption dashboards or token counts to evaluate impact,” according to a report by The Information. […]
How cost visibility becomes a competitive advantage in FinOps in 2026
As spending on cloud technologies grows, so does waste. The Flexera 2026 State of the Cloud Report found that 27% of organizations expect to spend more on cloud this year, with 17% already exceeding their budgets over the previous 12 months. The estimated share of wasted cloud spend has already crept up to 29%, undoing […]
ChatGPT, Claude, and Grok all went down at once; enterprises need a backup plan
Enterprises are facing a disturbing new question in the age of AI: What happens when agentic assistants go dark? This became a very real scenario on Thursday, as OpenAI’s ChatGPT, Anthropic’s Claude, and SpaceXAI’s Grok near-simultaneously, and somewhat mysteriously, experienced significant, prolonged outages. Beginning in the morning, Eastern time, several ChatGPT models went down over […]
What Nvidia’s $13B acquisition of Hugging Face means for AI model choice
When Nvidia said Thursday that it plans to pay $13 billion to acquire Hugging Face, the question arose of whether the open AI platform would remain open when it becomes a unit of Nvidia. And the current lack of a single viable open alternative that does everything Hugging Face does for enterprises adds further complications […]
26-00281.pdf
26-00281.pdf Anonymous (not verified) Fri, 09/04/2026 – 14:15 Case ID 26-00281 Forum FINRA Document Type Award Claimants Mary Carlson The Estate of John David Carlson Respondents Morgan Stanley & Co., LLC Neutrals John J. Fitzpatrick Richard L. Warner Ryan Alane Phelan Hearing Site Helena, MT Award Document 26-00281.pdf Documentum DocID 40c12ec4 Award Date Official Fri, […]
ALBERT SECURITIES, LLC
ALBERT SECURITIES, LLC fnrw-backend Fri, 09/04/2026 – 14:00 MC ID ALBS MC Reporter Type Broker-Dealer MC Paragraph MC Link https://public.s3.com/rule605/albs/ MC Last Updated Fri, 09/04/2026 – 14:00
Phishing Campaign Sends Millions of Emails Using Invisible Unicode to Evade Filters
Microsoft is alerting of a “high-volume phishing campaign” that’s using invisible Unicode tag characters to bypass email filters. “Instead of using these characters to hide instructions from people while exposing them to AI models, the attacker used them to split financial lure words such as ‘funding’ to prevent email filters from parsing them,” the Microsoft […]
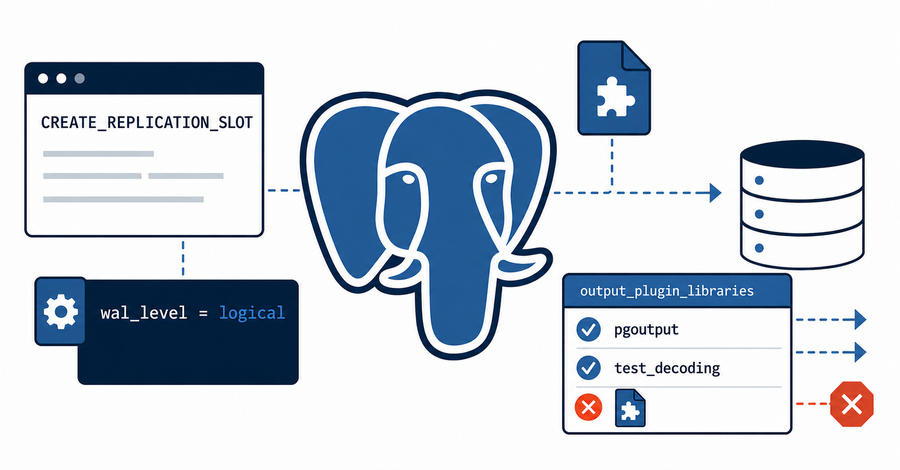
PostgreSQL Fixes 12-Year-Old Logical Decoding Flaw Enabling Replication-Role Code Execution
PostgreSQL has released updates to address a security flaw that allows an account with the REPLICATION attribute to run arbitrary code as the operating-system user running the database server. The flaw, tracked as CVE-2026-6471 (CVSS score: 7.2), has been present since logical decoding was introduced in PostgreSQL 9.4 in 2014. Versions before PostgreSQL 18.6, 17.11, […]
26-01030.pdf
26-01030.pdf Anonymous (not verified) Fri, 09/04/2026 – 11:10 Case ID 26-01030 Forum FINRA Document Type Award Claimants Karl Samuelson Respondents Ameriprise Financial Services, LLC Hearing Site Minneapolis, MN Award Document 26-01030.pdf Documentum DocID 55ee6826 Award Date Official Thu, 09/03/2026 – 12:00 Related Content Off Claimant Representatives Karl A. Samuelson Respondent Representatives Howard Klausmeier
26-01386.pdf
26-01386.pdf Anonymous (not verified) Fri, 09/04/2026 – 11:10 Case ID 26-01386 Forum FINRA Document Type Award Claimants Austin Masel Respondents Morgan Stanley Neutrals John R. Wylie Edith M. Novack Edward W. Morris Hearing Site Boston, MA Award Document 26-01386.pdf Documentum DocID eddc8059 Award Date Official Thu, 09/03/2026 – 12:00 Related Content Off Claimant Representatives David […]
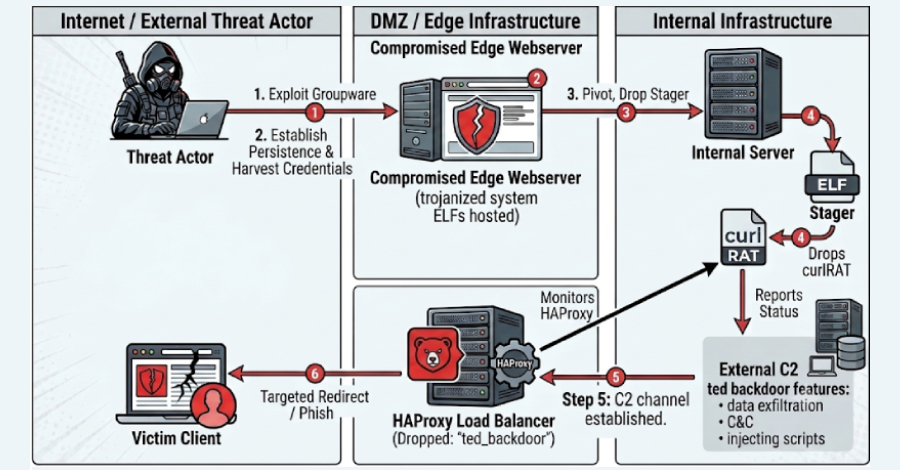
New Ted Backdoor Hides Inside Victims' Own HAProxy Builds to Intercept Web Traffic
A previously undocumented Linux toolkit has been found compiled directly into the trojanized HAProxy load balancers of two South Korean organizations, where it intercepted web traffic and served altered pages to selected visitors. The attackers named the implant ted in debug strings left in the binary. It is not a HAProxy vulnerability, and installing it […]
FBI investigates breach of 153 million driving license records at IDscan.net
Drivers in North America received a nasty shock this week when it was revealed that digital scans of 153 million drivers’ licenses were for sale on the dark web. Among the victims were US Defense Secretary Pete Hegseth – and investigative reporter Brian Krebs, who has dug deep into the data breach on his blog […]
Bidding war for defunct Spirit Airlines’ employee data will not die
The destiny of Spirit Airline’s data is still undecided, months after the company sought bankruptcy protection. AI data company Micro1 has now offered $12.5 million to acquire a trove of the company’s emails, Teams chats, operations and employee productivity data, according to a report by aviation website Simply Flying, It said the data includes about […]
Honeywell Aerospace Inc. Agrees to Pay Over $2M to Settle False Claims Act Allegations of Failing to Comply with Cybersecurity Requirements in a U.S. Department of Defense Contract
A DOJ press release on September 1: The Justice Department announced today that Honeywell Aerospace Inc. has agreed to pay $2,042,518 to resolve allegations that it is liable under the False Claims Act for failing to comply with cybersecurity requirements in a contract with the U.S. Department of Defense. Honeywell Aerospace, a corporation headquartered in… […]
DaVita settles ransomware attack lawsuit for $15M
Chad Van Alstin reports an update on a ransomware attack previously reported on DataBreaches.net: Nationwide kidney dialysis chain DaVita has agreed to pay $15 million to settle a class action lawsuit stemming from a 2025 ransomware attack that exposed sensitive patient data to hackers, the bulk of which was later leaked onto the dark web. The hack… […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-85046 Google Chromium V8 Type Confusion Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security […]
Ledger faces $500 million class action over data breaches
Pavlo Kot reports: Hardware crypto wallet maker Ledger is facing a class action seeking at least $500 million over a series of customer data breaches. The plaintiff claims the company failed to adequately protect customers’ personal information and did not take sufficient measures following previous incidents. The lawsuit was filed on August 27 by Ledger user Douglas… […]
FBI probes suspected breach at IDScan.net after dark web service Nexus offered 153M+ US and Canadian driver’s license scans
Pierluigi Paganini reports: A dark web identity theft service called Nexus appeared on September 1, 2026, offering searchable access to more than 153 million scanned driver’s licenses belonging to people in the United States and Canada. The FBI’s New Orleans field office opened a formal investigation the same day. Brian Krebs at KrebsOnSecurity, who broke the story, traced… […]
TR: Fine for famous kebab chain that allowed theft of 500 thousand customers’ data
The Turkish Data Protection Authority (KVKK) investigation into the data breach at the famous restaurant chain Baydöner, where the full names, phone numbers, emails, and city information of 505,337 customers were compromised, has been completed. The investigation found that there was no alarm mechanism to detect unusual system activity, and Baydöner was fined a total… […]
Manchester Airports Group Data on 8.8 Million People Leaked After Ransom Refusal
Hacker group published roughly 550GB of data after MAG reportedly refused to pay a ransom demand; the group says it gained access via exposed admin keys. The post Manchester Airports Group Data on 8.8 Million People Leaked After Ransom Refusal appeared first on SecurityWeek.
Capsule Security Launches ‘AI Circuit Breaker’ to Stop Rogue Agents
New models, trained using NVIDIA Nemotron 3 Ultra, aim to catch rogue agent behavior before it executes, without the latency of large-model review. The post Capsule Security Launches ‘AI Circuit Breaker’ to Stop Rogue Agents appeared first on SecurityWeek.
HiddenLayer Raises $100 Million for AI Runtime Security
The Austin-based company will invest in agentic runtime security capabilities to secure AI coding agents. The post HiddenLayer Raises $100 Million for AI Runtime Security appeared first on SecurityWeek.
AI Agent Firewall Startup AIR Security Emerges From Stealth With $50 Million
The startup’s firewall evaluates AI skills, plugins and MCP servers for malicious instructions, excessive permissions and software supply chain risks. The post AI Agent Firewall Startup AIR Security Emerges From Stealth With $50 Million appeared first on SecurityWeek.
OpenAI launches GPT-6 Astra, its first model to cross a critical cybersecurity threshold
OpenAI launched GPT-6 Astra on Thursday, disclosing that the new flagship model has crossed the “Critical” threshold for cybersecurity risk under its Preparedness Framework, a classification the company said triggers additional deployment restrictions. “GPT‑6 Astra is rolling out today to a limited set of organizations and over the coming days will become available to all […]
The democratization of cyber warfare — and what it means for CISOs
For most of modern history, sophisticated and costly warfare had a high barrier to entry. In order to maintain a significant tactical advantage, you needed money, infrastructure and highly trained human resources. In the physical realm, you needed trained and capable warfighters along with relatively expensive and specialized weaponry, made by skilled tradesmen. In cyber, […]
Over 440,000 Exploit Attempts Target Super Forms and Elementor Pro RCE Flaws
Threat actors are exploiting two critical security flaws in WordPress plugins Super Forms and Elementor Pro, according to findings from Wordfence. The vulnerabilities in question are – CVE-2026-14894 (CVSS score: 9.8) – A missing file type validation vulnerability in Super Forms – Drag & Drop Form Builder that allows unauthenticated attackers to upload files of […]
Plex Urges Immediate Updates After Patching Multiple Undisclosed Security Flaws
Plex is urging users to update their instances to the latest version following the release of an update that patches multiple security flaws. The fixes are available in Plex Media Server 1.43.3 and Plex Desktop 1.115.0. The streaming media service did not elaborate on what those issues are, but said CVE identifiers have been requested […]
Google Releases Chrome Update to Patch Actively Exploited V8 Zero-Day
Google on Thursday released security updates to patch 12 vulnerabilities, including one that has come under active exploitation in the wild. The high-severity vulnerability, tracked as CVE-2026-85046 (CVSS score: 8.8), has been described as a type confusion bug in V8, Chrome’s JavaScript and WebAssembly engine. “Type confusion in V8 in Google Chrome prior to 152.0.7977.82 […]
GPT-6 Astra Scores 100% on ExploitBench as OpenAI Blocks PoC Exploit Requests
OpenAI on Thursday officially unveiled GPT‑6 Astra, which it described as the “world’s most intelligent and aligned model.” The development comes days after the artificial intelligence (AI) company said the model had reached the “Critical” cybersecurity capability threshold under its Preparedness Framework. “Astra is state-of-the-art on computer use, browsing, software engineering,
ISC Stormcast For Friday, September 4th, 2026 https://isc.sans.edu/podcastdetail/10082, (Fri, Sep 4th)
Post Content
CNIL: Health data breach: €500,000 fine imposed on the Loire Private Hospital
On September 3, 2026, the CNIL issued a €500,000 fine against the Loire Private Hospital, for not having taken appropriate measures to ensure the security of the data of its patients and some of their relatives. During the summer of 2025, an attacker managed to connect to the electronic patient record (EPR) of the Loire Private… […]
Two “Nephrology Associates” suffered cyberattacks. Only one of them has disclosed it.
Sometimes, first impressions are wrong. And in the case of “Nephrology Associates,” DataBreaches mistakenly thought one victim was attacked by two different groups. But no, there are actually two unrelated entities with the same name that suffered attacks this year. And only one of them has disclosed it. The Kansas Incident On March 7, The… […]
OpenAI targets small utilities with $1 billion cyber defense initiative
In a keynote speech during a summit at OpenAI’s headquarters attended by 300 enterprise security leaders and CISOs from Fortune 1000 companies, OpenAI President Greg Brockman announced Daybreak for Frontline Defenders, a new global initiative to help frontline defenders use frontier cyber AI to protect essential services in the United States and around the world. […]
24-00122.pdf
24-00122.pdf Anonymous (not verified) Thu, 09/03/2026 – 17:00 Case ID 24-00122 Forum FINRA Document Type Award Claimants Martha Frost Respondents Horace Mann Investors, Inc. Neutrals Mary C. Kelleher Jim Geiger John M. D’Amico Hearing Site Boston, MA Award Document 24-00122.pdf Documentum DocID ff76ec43 Award Date Official Thu, 09/03/2026 – 12:00 Related Content Off Claimant Representatives […]
2024083689501 Xing Su CRD 4031195 AWC ks.pdf
2024083689501 Xing Su CRD 4031195 AWC ks.pdf Anonymous (not verified) Thu, 09/03/2026 – 16:45 Case ID 2024083689501 Document Number 3c9df82d Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals Xing Su Action Date Thu, 09/03/2026 – 12:00 Related Content Off Attachment 2024083689501 Xing Su CRD 4031195 AWC ks.pdf Individual CRD 4031195
2024081737701 J.P. Morgan Securities LLC CRD 79 AWC ks.pdf
2024081737701 J.P. Morgan Securities LLC CRD 79 AWC ks.pdf Anonymous (not verified) Thu, 09/03/2026 – 16:30 Case ID 2024081737701 Document Number e013df3a Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Action Date Thu, 09/03/2026 – 12:00 Related Content Off Attachment 2024081737701 J.P. Morgan Securities LLC CRD 79 AWC ks.pdf
The New School Safety Perimeter: Where Cybersecurity Meets Physical Security
Kumar Sokka reports: At many institutions, the student ID number exposed in a data breach is the same number that unlocks dorm doors, sits behind classroom badge readers, controls laboratory access, and authenticates into building automation systems. The badge in a student’s wallet is keyed to that database. When that database is compromised, every physical… […]
Why data sovereignty has become a strategic IT priority
For years, conversations about data sovereignty followed a predictable pattern. Compliance teams wanted to know where sensitive data was stored, legal teams ensured regulatory requirements were met and IT focused on delivering the infrastructure to support the business. Once those requirements had been satisfied, the conversation largely moved on. Today, that approach is becoming increasingly […]
The rise of the AI operating executive
While many organizations are still experimenting with AI and debating governance models, a small but growing group of market leaders is already operationalizing AI at scale. Marianne Johnson, executive vice president and chief product and technology officer at Cox Automotive, is one executive creating business impact today. With responsibilities spanning product, technology, data, AI, engineering, […]
The missing evidence chain in AI adoption
Organizations often celebrate an AI launch at the moment the real work begins. The platform is available, the policy is published and employees have completed training. But none of those milestones tells a CIO whether work has improved, decisions are stronger or employees know when human judgment must override an AI recommendation. This gap is […]
Dell’s $95B AI backlog shows the infrastructure crunch is far from over
Dell Technologies is acknowledging that infrastructure and storage supply still can’t keep up with agentic AI’s insatiable appetite for resources. The company this week reported a “record” AI backlog, with $95 billion in orders waiting to be filled. This dovetails with quarterly earnings reflecting a more than 50% year-over-year increase in AI demand. On an […]
AI agents need to learn when enough is enough
For the past few years, enterprise AI programs have focused on making models more useful, accurate, and autonomous. In that phase, a bad answer was still usually something a human could accept or reject before taking action. But once agents start invoking tools and acting inside business workflows, success should no longer be measured only […]
When AI’s human in the loop really isn’t
Concerns about the risks of AI systems are certain to be met with four words: human in the loop. The discussion may broaden, but the assurance is inevitable. It’s an AI governance phrase that’s become so rote you hear it in every direction and likely have said it yourself. But IT leaders should be wary […]
ThreatsDay: CEO Phishing Kits, 5K Dropbox Account Hacks, OAuth Traps + 17 More Stories
The worst part is how normal these attacks look. A call from IT. A shared file. A trusted app. A simple request to click “Allow.” Why break in when someone might open the door? That idea runs through this edition. Attackers use real tools, fake login pages, old account links, and software guides that point […]
Financial Services Institute (FSI) Comment On Regulatory Notice 26-06
Financial Services Institute (FSI) Comment On Regulatory Notice 26-06 fnrw-backend Thu, 09/03/2026 – 13:24 Andrew M. Hartnett Andrew Hartnett <a.hartnett@financialservices.org> Financial Services Institute (FSI) Regulatory Notice 26-06 Core Official Date Thu, 09/03/2026 – 12:00 Comment File FSI Supplemental Comment re FINRA Regulatory Notice 26-06_9.2.2026.pdf
25-00167.pdf
25-00167.pdf Anonymous (not verified) Thu, 09/03/2026 – 13:00 Case ID 25-00167 Forum FINRA Document Type Award Claimants Perry Fryer Respondents J.P. Morgan Securities, LLC Neutrals Theodore W. Wrobleski Scott Stauffer Kenneth Philip Ross Hearing Site Chicago, IL Award Document 25-00167.pdf Documentum DocID 4e182bd1 Award Date Official Wed, 09/02/2026 – 12:00 Related Content Off Claimant Representatives […]
Agentic Ransomware Took Down Enterprise in Ten Hours: AI Left 80-Page Audit
Roger Satterfield reports: An attacker handed an unknown corporate victim a comprehensive, 80-page security audit on Wednesday — not as a service, but as a postscript to the ransomware attack that had just consumed the victim’s enterprise. According to Palo Alto Networks’ threat intelligence unit Unit 42, whose researchers documented the September 2 incident, the… […]
Critical Cisco Nexus 9000 Flaw Lets Unauthenticated Remote Attackers Run Code as Root
Cisco has released patches to address a critical security flaw affecting 10 Silicon One-based Nexus 9000 switches that could allow an unauthenticated, remote attacker to execute code as root, alongside an IOS XR hardening release bundling 7 umbrella CVEs, 2 of which are rated 9.8, with no workaround for any IOS XR version. The Nexus […]
BraZetsu Malware Turns Compromised Windows Hosts Into Criminal Marketplace Inventory
Cybersecurity researchers have disclosed details of a sophisticated Python-based Windows malware framework called BraZetsu that fuels an underground marketplace commercializing access to compromised hosts. “Unlike the standard infostealer model, BraZetsu is a comprehensive master toolkit that empowers Initial Access Brokers (IABs) by turning compromised systems into highly valuable commercial
Thomson Reuters Court Software Breach May Have Exposed SSNs and Sealed Data
Thomson Reuters disclosed on Wednesday that an unauthorized party obtained files from C-Track, the court case management platform sold by its West Publishing Corporation unit, in March 2026, affecting courts in 11 U.S. states, the U.S. Virgin Islands, and Ontario, Canada. West Publishing said it discovered the activity on June 30, 2026. A subset of […]
Rockwell Automation 1756-ENBT Module
View CSAF Summary Successful exploitation of this vulnerability could crash the module. The device requires a restart to recover. The following versions of Rockwell Automation 1756-ENBT Module are affected: 1756-ENBT module vers:all/* (CVE-2025-10478) CVSS Vendor Equipment Vulnerabilities v3 7.5 Rockwell Automation Rockwell Automation 1756-ENBT Module Improper Check for Unusual or Exceptional Conditions Background Critical Infrastructure […]
Inductive Automation Ignition
View CSAF Summary Successful exploitation of this vulnerability could allow any authenticated user to create projects. The following versions of Inductive Automation Ignition are affected: Ignition <=8.1.53 (CVE-2026-77393) CVSS Vendor Equipment Vulnerabilities v3 8.8 Inductive Automation Inductive Automation Ignition Incorrect Default Permissions Background Critical Infrastructure Sectors: Critical Manufacturing, Energy, Information Technology Countries/Areas Deployed: Worldwide Company […]
OPCFoundation OPC UA LocalDiscoveryServer (LDS)
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to take control of a high-privilege terminal during installation and run arbitrary commands. The following versions of OPCFoundation OPC UA LocalDiscoveryServer (LDS) are affected: UA-LDS-Installers <1.04.420 (CVE-2026-77477) CVSS Vendor Equipment Vulnerabilities v3 4.6 OPCFoundation OPCFoundation OPC UA LocalDiscoveryServer (LDS) Execution with Unnecessary Privileges […]
Tycon Systems TPDIN-Monitor-WEB3
View CSAF Summary Successful exploitation of these vulnerabilities could allow for an attacker to perform a man-in-the-middle (MitM) attack, cause a factory reset, wipe credentials, or retrieve sensitive information. The following versions of Tycon Systems TPDIN-Monitor-WEB3 are affected: TPDIN-Monitor-WEB3 <=2.2.9 (CVE-2026-77847, CVE-2026-82712, CVE-2026-82684) CVSS Vendor Equipment Vulnerabilities v3 8.8 Tycon Systems Tycon Systems TPDIN-Monitor-WEB3 Use […]
Rockwell Automation ControlFLASH
View CSAF Summary Successful exploitation of this vulnerability could give an attacker the ability to run any commands or code of the attacker’s choice on a target machine at the logged-in user’s permission level. The following versions of Rockwell Automation ControlFLASH are affected: ControlFLASH <=V15.07 (CVE-2026-12663) CVSS Vendor Equipment Vulnerabilities v3 7.3 Rockwell Automation Rockwell […]
Rockwell Automation ArmorStart LT
View CSAF Summary Successful exploitation of these vulnerabilities could result in a loss of webserver availability or allow an attacker to inject malicious scripts that will be executed when other users access the affected page. The following versions of Rockwell Automation ArmorStart LT are affected: ArmorStart LT <=v2.001 (CVE-2026-19471, CVE-2026-19472) CVSS Vendor Equipment Vulnerabilities v3 […]
IXON VPN Client
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to perform remote code execution on the computer running the client with elevated privileges. The following versions of IXON VPN Client are affected: VPN Client <1.4.7 (CVE-2026-75925) CVSS Vendor Equipment Vulnerabilities v3 9.6 IXON IXON VPN Client Improper Neutralization of CRLF Sequences (‘CRLF […]
Preparing for the Post-Quantum Era: A Call to Action
CISA and the Group of Seven (G7) Cyber Security Working Group released Preparing for the Post-Quantum Era: A Call to Action highlighting the urgent need for organizations and governments to begin transitioning to post-quantum cryptography (PQC) to protect sensitive data, authentication systems, and critical assets from emerging quantum computing threats. The G7 Cyber Security […]
Pyramid Solutions NetStaX EtherNet/IP Stack
View CSAF Summary Successful exploitation of this vulnerability could result in memory corruption, a device crash, or a potential remote attack vector without the originating device receiving a CIP error indicating that the request could not be processed. The following versions of Pyramid Solutions NetStaX EtherNet/IP Stack are affected: EtherNet/IP Adapter DLL Kit (EIPA) EtherNet/IP […]
US Becomes Top Target in RMM Phishing Campaign Spanning 46 Countries
An RMM phishing campaign initially associated with Canadian targeting due to its use of Canada Revenue Agency (CRA) tax forms as lures has turned out to be part of a broader campaign spanning 46 countries. Around 45% of observed activity was associated with the United States, making it the campaign’s top geographic target. ANY.RUN research […]
Russian National Indicted For Exploiting Online Platform Used For Freelance Employment And Distributing Malware To Thousands Of Victims
SAN FRANCISCO – A federal grand jury has indicted Searzhudin Tamirlanovich Aktulaev on charges of Conspiracy, Transmission of a Program, Information, Code, and Command to Cause Damage to a Protected Computer, and Aggravated Identity Theft, among other offenses. Defendant was arrested in Cyprus in May 2025 and has been extradited to the United States. Yesterday,… […]
North Dakota Supreme Court impacted by third-party data breach that has affected dozens of states
Joe Kurzewski reports: A criminal investigation is underway after data associated with the North Dakota Supreme Court was affected by a breach of a third-party vendor used by the court. According to a news release, the North Dakota Court System was informed in late July that C-Track experienced a data breach that may have involved… […]
Decade-old PostgreSQL flaw turns backup account into a backdoor
A critical vulnerability in PostgreSQL had remained hidden for more than a decade, potentially turning a routine backup account into a path to full database and server compromise. The issue, dubbed PostGREShell by Cyera Research, exists in the database’s replication functionality and could allow an attacker with a low-privilege account carrying the REPLICATION attribute to […]
Counterfeit installers turn routine software downloads into enterprise breaches
Microsoft has warned that attackers are breaching enterprise systems via counterfeit download sites impersonating software including Microsoft Edge, Kaspersky and Razer, delivering trojanized installers for persistent access. “Once executed, the malicious installers deploy malware that establishes persistence, attempts to weaken security protections, and communicates with attacker-controlled infrastructure,” Microsoft security researchers wrote in a blog post. […]
153 Million Driver License Images Offered on Dark Web
Cybercriminals are offering digital scans of US and Canadian driver’s licenses, likely stolen from IDScan.net. The post 153 Million Driver License Images Offered on Dark Web appeared first on SecurityWeek.
Over 3 Million WordPress Sites Affected by Migration Plugin Vulnerability
The high-severity SQL injection flaw (CVE-2026-19949) could allow unauthenticated attackers to achieve remote code execution. The post Over 3 Million WordPress Sites Affected by Migration Plugin Vulnerability appeared first on SecurityWeek.
Cisco Warns of Unpatched Secure Email Flaws, Patches Critical Switch Vulnerabilities
Publicly disclosed S/MIME flaws could expose encrypted email content, while critical IOS XR and Nexus bugs could enable remote code execution and authentication bypass. The post Cisco Warns of Unpatched Secure Email Flaws, Patches Critical Switch Vulnerabilities appeared first on SecurityWeek.
OpenLeash Adds a Human Check to Risky AI Agent Actions
The security tool intercepts potentially dangerous agent actions, blocking clear threats and requesting human approval when intent is uncertain. The post OpenLeash Adds a Human Check to Risky AI Agent Actions appeared first on SecurityWeek.
UK Moves to Block High-Risk Tech Suppliers From Critical Infrastructure
Late amendments to the Cyber Security and Resilience Bill would give ministers new powers to restrict risky technology providers as supply chain attacks intensify. The post UK Moves to Block High-Risk Tech Suppliers From Critical Infrastructure appeared first on SecurityWeek.
Rockwell Automation Patches Over a Dozen Vulnerabilities Across Products
The industrial giant has released advisories for its RSLinx Classic, ArmorStart, ControlFLASH, FactoryTalk, and other products. The post Rockwell Automation Patches Over a Dozen Vulnerabilities Across Products appeared first on SecurityWeek.
Exploit Published for Fresh Cleo Harmony Vulnerability
The security defect allows remote attackers to bypass authentication through argument bearer manipulation. The post Exploit Published for Fresh Cleo Harmony Vulnerability appeared first on SecurityWeek.
Anthropic Details Response to Security Incidents, Unveils Enterprise Safeguards
Anthropic introduced Enterprise Frontier Safeguards (EFS), a system that combines zero data retention with automated monitoring for misuse. The post Anthropic Details Response to Security Incidents, Unveils Enterprise Safeguards appeared first on SecurityWeek.
Malicious Virtualizor Update Served via BGP Hijacking
Using a technically valid TLS certificate for Softaculous’ domains, a threat actor diverted traffic to fake software updates. The post Malicious Virtualizor Update Served via BGP Hijacking appeared first on SecurityWeek.
Attackers Turn Trusted Node.js Runtime Into Malware Delivery Tool in Targeted Attacks
Threat actors are leveraging the trusted Node.js JavaScript runtime in multiple cyber attacks as a way to deploy malicious payloads. According to a new report published by the Symantec Threat Hunter Team today, the attack method has been put to use in attacks targeting government departments, technology companies, and hotels since February 2026. “The technique’s […]
AI agents help compress ransomware intrusion to under 10 hours, raising stakes for CISOs
A ransomware attacker used AI agents to move through an enterprise network in less than 10 hours, according to Palo Alto Networks researchers, who estimated that similar work could have taken human operators about two weeks. The incident involved more than 50 techniques mapped to the MITRE ATT&CK framework, according to the company’s Unit 42 […]
Stop playing with the CISO role. Fix cybersecurity leadership
We have spent years telling chief information security officers (CISOs) that they need to become better aligned with the business. They need to understand strategy. They need to speak the language of the board. They need to build relationships with business leaders. They need to translate cyber risk into business risk. I increasingly believe that […]
Pegasus Zero-Click Spyware Exploit Infects Serbian Student Movement Member's iPhone
The iPhone belonging to a member of Serbia’s student protest movement was infected with NSO Group’s Pegasus spyware, according to new findings from the Citizen Lab in collaboration with the SHARE Foundation. “Our analysis confirmed that an iMessage zero-click exploit was used to infect the device with NSO Group’s Pegasus spyware,” the Citizen Lab said. […]
Zero trust has a big AI agent problem ahead
Despite singing the praises of zero trust for many years, many CISOs have struggled to implement the framework in full. And now comes what could be the final nail: agentic AI. Can zero trust coexist with autonomous agents in typical enterprise environments? Technically, yes. In practice, not likely, given CEO/board-level urgency to accelerate agentic ROI […]
Data Protection Commission announces Final Decision following Inquiry into the Health Service Executive (HSE)
Data Protection Commission announces Final Decision following Inquiry into the Health Service Executive (HSE) ikerinar Thu, 03/09/2026 – 09:42
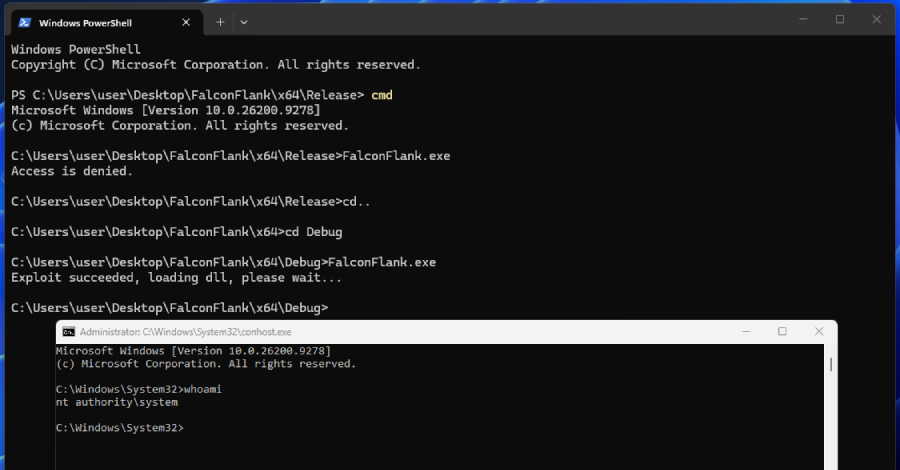
Researcher Releases FalconFlank PoC Showing Privilege Escalation in CrowdStrike Falcon
The security researcher known as Chaotic Eclipse (aka INFINITE NIGHTMARE, MSNightmare, and Nightmare-Eclipse) has dropped a new zero-day dubbed FalconFlank, a privilege escalation flaw impacting Crowdstrike Falcon. “FalconFlank is a 0day privilege escalation that abuses the office malicious macros remediation in CrowdStrike Falcon Sensor,” the researcher said in a GitHub README file, adding
CISA Adds Seven Exploited Flaws as Attackers Deploy Reverse Shells and Crypto Miners
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added seven security flaws to its Known Exploited Vulnerabilities (KEV) catalog after they landed in attackers’ crosshairs. The vulnerabilities are as follows – CVE-2026-83548 (CVSS score: 10.0) – A server-side request forgery vulnerability in SonicWall SMA 1000 Appliances that could allow a remote unauthenticated
Honeypot-Omaha and batch.py [Guest Diary], (Wed, Sep 2nd)
[This is a Guest Diary by Frank Igbokwe, an ISC intern as part of the SANS.edu BACS program]
ISC Stormcast For Thursday, September 3rd, 2026 https://isc.sans.edu/podcastdetail/10080, (Thu, Sep 3rd)
Post Content
SonicWall reports two major security holes under active exploit
SonicWall on Monday reported two major security holes in its Secure Mobile Access 1000 series appliances, both of which it said are being actively exploited, and published patches for each. Consultants called the holes, one of which permits remote attacks that bypass authentication, highly troubling. In its security alert, SonicWall described the first hole, tracked […]
Help Shape the Future of the Series 7 Exam
Help Shape the Future of the Series 7 Exam K34060 Wed, 09/02/2026 – 16:41 September 2, 2026 Features Help Shape the Future of the Series 7 ExamFINRA is launching a job analysis survey Sept. 14 targeting registered representatives to inform updates to the Series 7 qualification exam. A sampling of individuals holding a General Securities […]
DoD confirms ‘refrigeration disruption’ at military commissaries
DysruptionHub raised the suspicion flag yesterday, but couldn’t get a straight answer from DOD as to whether refrigeration outages at 14 commissaries represented a cyberattack. The Military Times fared no better: With more than a half-dozen commissaries on military bases in the continental U.S. reporting refrigeration outages this week, the Pentagon is acknowledging the problem… […]
Hackers expose donor data from Russian fundraisers for Ukrainians, political prisoners
Daryna Antoniuk reports: Hackers reportedly gained access to payment accounts used by two Russian fundraising projects supporting Ukrainians and political prisoners, exposing donor email addresses and limited payment card information. The unknown threat actor targeted Davayte, which raises money for civilians in Ukraine affected by Russia’s invasion, and You Are Not Alone, a project supporting… […]
Luminis Health facilities dealing with a cyberattack
Bridget Byrne reports: Luminis Health is experiencing a cybersecurity incident affecting certain systems across its organization, according to a Facebook post Tuesday. “Our priority remains providing safe, high-quality care to our patients,” the health system said in the post that went up around 6:45 p.m. “We understand the concern this may cause for our patients,… […]
2025085419901 Daniel G. Diaz CRD 1715827 AWC lp.pdf
2025085419901 Daniel G. Diaz CRD 1715827 AWC lp.pdf Anonymous (not verified) Wed, 09/02/2026 – 15:05 Case ID 2025085419901 Document Number 4b809956 Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals Daniel G. Diaz Action Date Wed, 09/02/2026 – 12:00 Related Content Off Attachment 2025085419901 Daniel G. Diaz CRD 1715827 AWC lp.pdf Individual CRD 1715827
The agent didn’t leak anything. It just figured something out
Your agent compares a banker’s calendar with the legal team’s and recognizes a pattern: an unannounced transaction is underway. No one told the agent about the deal. It inferred it correctly. Then it adds one line to an executive briefing for a recipient who was not cleared to know about it: “the deal is moving.” […]
Revenue is no longer a funnel. It’s an AI learning loop
It is Q3 of the fiscal year. The VP of sales walks into the revenue forecast meeting confident. The pipeline is strong, conversion rates are up and the sales team has been running at full velocity. The revenue intelligence motion is working. But something is off. The VP of customer success sees it first. Accounts […]
Why Cisco is redefining its CIO role
The CIO job description is being rewritten in real time. As AI agents take over the interface layer and connect directly to any data source, the skills that once defined great IT leadership — UX fluency, applications integration, build-versus-buy judgment — are giving way to an entirely different set of questions surrounding not how a […]
Engineering AI into the product development lifecycle
AI is already changing how software is built. Google Cloud’s DORA research, based on nearly 5,000 technology professionals, found that 90% now use AI at work, spending a median of two hours a day with it, which translates to roughly a quarter of the working day. In many organizations, the focus is on what happens […]
Cyber resilience is a very human decision problem, not just a technology one
Organizations today are not short of data, particularly in the domain of cyber. What many lack is a timely, trusted assessment that can help leaders act with greater confidence. When a cyber incident begins, the technical questions surface first. What happened? Which systems are affected? Is the activity contained? But the questions that often shape […]
Citrix buys company that containerizes Windows desktop apps independently of the OS
Citrix on Tuesday announced that it has completed the acquisition of longtime partner Numecent, producer of technology that containerizes and manages Windows applications. The acquisition builds on joint efforts to integrate Numecent’s management tool, Cloudpager, with Citrix Desktop-as-a-Service (DaaS) after an integration announced in April let administrators natively publish and manage the application containers through […]
Economic process modeling: Business cases beyond cost accounting
Cortney Pagel has learned to expect a particular question whenever she proposes changing how work gets done. Pagel, a senior business analyst and change manager at ENGIE Impact, often hears it from the digital side of the organization before she has finished explaining the change: How much money are we looking to save here? “I […]
Google, Anthropic, and OpenAI Unveil Cyber AI Models, Safeguards, and Access Programs
Google on Wednesday announced Gemini 3.8 Flash Cyber, which it described as its most capable cybersecurity model, and has made it available to a set of trusted defenders via a new initiative called the Fairwind Program. “The Fairwind Program gives high-priority defenders (like governments, healthcare providers, and telecommunications services) early access to advanced models that […]
James Angel Comment On Regulatory Notice 26-15
James Angel Comment On Regulatory Notice 26-15 fnrw-backend Wed, 09/02/2026 – 13:59 James Angel James Angel <angelj@georgetown.edu> McDonough School of Business Georgetown University Regulatory Notice 26-15 Core Official Date Wed, 09/02/2026 – 12:00 Comment File Comments by Professor James J Angel PhD CFP CFA on Modernizing FINRA Best Execution Guidance Reg Notice 26-15.pdf
Fake Software Installers Disable Windows Update and Weaken Microsoft Defender
An active malware campaign is using bogus software-download websites to impersonate trusted vendors and distribute malicious installers. “The campaign has targeted users looking to download popular software and has resulted in compromises across multiple organizations and industries, primarily affecting China-based operations of multinational organizations and Chinese-speaking users,” Microsoft
CDAS
CDAS K33357 Wed, 09/02/2026 – 11:49 Continuing Education Requirements 30 hours every two years Designation Training Requirements Online, self-study course, including written case study Published List of Disciplined Designees None Online Designation Resource Online at Find an Advisor Issuing Organization Link https://icfs.com/ Investor Complaint Process Submit complaints via mail to Executive Director, Institute of Business […]
90-0034.pdf
90-0034.pdf Anonymous (not verified) Wed, 09/02/2026 – 11:45 Case ID 90-0034 Forum NYSE Document Type Award Award Document 90-0034.pdf Documentum DocID a3aff34b Related Content Off
Malicious .git Configs Can Make Claude, Codex, Cursor, and Other AI Agents Run Attacker Code
Manifold Security has disclosed eight security flaws across seven command-line AI coding agents in which a repository’s own Git configuration names a command that the agent runs on the developer’s machine, four of them still unpatched at publication. The command executes as the user, outside the agent’s sandbox and without an approval prompt, and exploitation […]
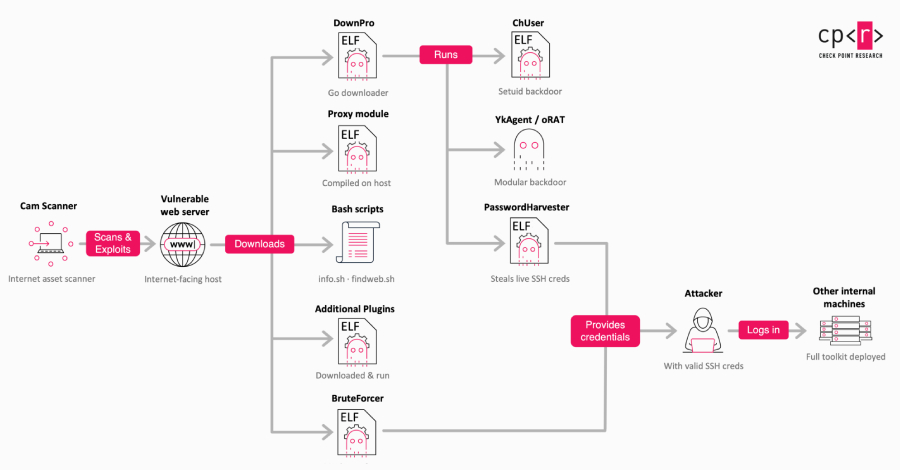
Malicious Apache Modules Hijack Brazilian Government Site Traffic to Push Betting Pages
A Chinese-speaking cybercrime cluster known as Gambling Goblin has been observed installing malicious Apache modules on compromised web servers run by Brazilian government and educational institutions, and using them to divert visitors to attacker-controlled pages promoting online gambling and sports betting. Check Point Research said it has tracked the campaign since mid-2025. The modules
BGP Hijack Delivers Malicious Virtualizor Update That Establishes Persistent Root Access
Virtualizor said hackers used a Border Gateway Protocol (BGP) hijack to divert Softaculous traffic. The hackers then used the diverted update traffic to deliver a malicious Virtualizor package to some installations. A hosting-provider account separately said 5 of its 34 checked Virtualizor hypervisors sustained root-level compromise. The incident window ran from approximately August 28 at […]
Anthropic introduces zero-retention AI safety monitoring for enterprises
Anthropic is introducing a new framework aimed at helping enterprises monitor AI misuse without ceding control over sensitive data, as organizations struggle to balance security visibility with strict compliance requirements. The company announced a new solution called Enterprise Frontier Safeguards (EFS), which “combines the privacy of zero data retention (ZDR) with state-of-the-art safeguards for detecting […]
Exploited JFrog Artifactory bug puts software supply chain on alert
A critical authentication bypass in JFrog Artifactory is now being exploited in the wild, with attackers observed generating administrator tokens and probing the software supply-chain platform’s sensitive data. The flaw, tracked as CVE-2026-82329, was disclosed by JFrog on August 28 and can, under default configuration, allow an unauthenticated attacker with network access to obtain administrative […]
Meta Ads Push StreamRat Android Trojan That Can Gain Near-Complete Device Control
Cybersecurity researchers have disclosed details of a new Android banking trojan called StreamRat that was promoted to Spanish-speaking users through a fake television-streaming campaign on Meta and can give operators near-complete control of infected devices. ThreatFabric said the campaign’s advertisement focused on Spain and reached an estimated 570,950 Meta accounts in the European Union
Communicating Under Pressure: Best Practices for Service Providers
Developed by CISA, the Federal Bureau of Investigation, and international partners, this guidance describes how organizations can plan and execute clear, timely, accurate, and audience-appropriate communications during IT and operational technology (OT) outages. Whether caused by cyber threat actors, human error, equipment failure, or natural hazards, service outages can create disruption and societal panic even […]
CISA Adds Seven Known Exploited Vulnerabilities to Catalog
CISA has added seven new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-9586 Sangoma Switchvox SQL Injection Vulnerability CVE-2026-48710 Kludex Starlette HTTP Request/Response Smuggling Vulnerability CVE-2026-49869 Kestra OSS OS Command Injection Vulnerability CVE-2026-59822 BerriAI LiteLLM Improper Authentication Vulnerability CVE-2026-82329 JFrog Artifactory Improper Authentication Vulnerability CVE-2026-83548 SonicWall SMA1000 […]
How to Secure Enterprise AI: From Adoption to Incident Readiness
The debate about whether AI delivers business value is over. The challenge now is implementing it at scale and securely across every function while meeting board-level pressure to move fast. Organizations must focus on adopting AI at business speed without losing control of cyber risk. Download the full eBook here. The Business Reality In Sygnia’s […]
OpenAI’s Astra Becomes First Model to Cross Critical Cybersecurity Threshold
The designation applies when a model can independently find and exploit zero-day vulnerabilities across many well-defended systems. The post OpenAI’s Astra Becomes First Model to Cross Critical Cybersecurity Threshold appeared first on SecurityWeek.
Chrome and Firefox Updates Patch Dozens of Vulnerabilities
The browser refreshes fix multiple use-after-free, sandbox escape, and privilege escalation bugs. The post Chrome and Firefox Updates Patch Dozens of Vulnerabilities appeared first on SecurityWeek.
23-Year-Old Sality P2P Botnet Disrupted
The shutdown operation involved peer list manipulation and Sality payload URL takedown. The post 23-Year-Old Sality P2P Botnet Disrupted appeared first on SecurityWeek.
SonicWall Warns of Two SMA1000 Zero-Days Exploited in Attacks
The vulnerabilities CVE-2026-83549 and CVE-2026-83548 can be chained for unauthenticated remote code execution. The post SonicWall Warns of Two SMA1000 Zero-Days Exploited in Attacks appeared first on SecurityWeek.
Palo Alto Networks Acquires AI Agent Platform Console
The cybersecurity giant announced the acquisition alongside quarterly results showing a 34% increase in revenue and strong growth in next-generation security ARR. The post Palo Alto Networks Acquires AI Agent Platform Console appeared first on SecurityWeek.
Sevii Targets AI-Speed Attacks With Preemptive Autonomous Defense
Sevii has expanded its ADR platform with AI agents designed to investigate, contain, and remediate AI-driven attacks within minutes. The post Sevii Targets AI-Speed Attacks With Preemptive Autonomous Defense appeared first on SecurityWeek.
Coast Guard Establishes Office of Maritime Cybersecurity Policy
The new office will serve as the central authority for cybersecurity policy covering US ports, vessels, and maritime facilities. The post Coast Guard Establishes Office of Maritime Cybersecurity Policy appeared first on SecurityWeek.
Experiment: Porting a PLC Exploit With AI Takes Hours and Hundreds of Dollars
Forescout researchers used Claude AI to port a remote code execution exploit between WAGO PLC models. The post Experiment: Porting a PLC Exploit With AI Takes Hours and Hundreds of Dollars appeared first on SecurityWeek.
Hackers Start Exploiting Critical Langflow Vulnerability
Tracked as CVE-2026-0768, the security defect allows unauthenticated attackers to execute arbitrary Python code remotely. The post Hackers Start Exploiting Critical Langflow Vulnerability appeared first on SecurityWeek.
Five Venezuelans Plead Guilty in US Court to ATM Jackpotting
The defendants unsuccessfully attempted to physically install malware on ATMs to force them to dispense cash. The post Five Venezuelans Plead Guilty in US Court to ATM Jackpotting appeared first on SecurityWeek.
Attackers Exploit Two SonicWall SMA 1000 Zero-Days That May Form an Attack Chain
SonicWall has released security updates to address two security flaws impacting its Secure Mobile Access (SMA) 1000 series VPN appliances that have been exploited in zero-day attacks. The vulnerabilities, discovered internally by SonicWall’s William Perry and Adam Babis, are listed below – CVE-2026-83548 (CVSS score: 10.0) – A pre-authentication SSRF vulnerability in the Appliance
GeoNetwork Fixes Unauthenticated RCE Chain Affecting Government Geoportal Backends
Two vulnerabilities in GeoNetwork can be chained to achieve unauthenticated remote code execution (RCE) on the open-source geospatial metadata catalog, which sits behind many government and agency geoportals. The project shipped fixes in versions 4.4.12 and 4.2.17 on July 8, 2026, and published the vulnerability details on August 31. GeoNetwork originated at the United Nations […]
Extradited Russian Hacker Faces Charges Over Excel Malware Campaign That Infected Thousands
The U.S. Department of Justice (DoJ) has charged a Russian national, extradited from Cyprus on August 28, with using roughly 255 fake accounts on a freelance platform to send malware-laced Excel attachments to about 80,000 of its users in 2016 and 2017. Searzhudin Tamirlanovich Aktulaev, 40, was arrested in Cyprus in May 2025, the U.S. […]
When the patch tsunami meets the maintenance window
In April 2026, the balance between finding software flaws and fixing them broke. Frontier AI models released by Anthropic and OpenAI can now autonomously identify exploitable vulnerabilities in production software — work that used to take experienced human researchers roughly sixty days now takes about four hours, as Melissa Hathaway documents in a recent Cyber […]
How China industrialized the infrastructure behind state hacking
Last week, the US Justice Department and FBI announced court-authorized seizures of domains hard-coded into two complementary hacking platforms known as “QScan” and “QTRouter,” used by Chinese state-sponsored hackers to target US critical infrastructure and other sensitive networks. A People’s Republic of China (PRC) state-sponsored group known as “QTFY,” employed by a corporation called China-based […]
Researchers Use Claude to Port Pre-Auth RCE Exploit From One PLC Model to Another
Forescout Research – Vedere Labs said it used Anthropic’s Claude to port a working pre-authentication remote code execution (RCE) exploit from one WAGO programmable logic controller (PLC) to another, executing attacker-supplied ARM shellcode on live hardware. The exploit targets CVE-2021-31886, a stack-based buffer overflow in the Nucleus FTP server’s handling of the USER command
Attackers Exploit Critical Switchvox Flaw to Deploy Reverse Shells Without Credentials
Threat actors are exploiting a severe security vulnerability in Sangoma Switchvox, an enterprise VoIP platform, that could allow unauthenticated remote code execution. The vulnerability in question is CVE-2026-9586 (CVSS score: 9.3), a critical unauthenticated SQL injection vulnerability in Sangoma Switchvox SMB Edition 8.3 (104997) that can allow attackers to remotely execute arbitrary code as
Authorities Turn Sality's P2P Network Against Itself, Cutting Off New Malware Payloads
The U.S. Department of Justice (DoJ) on Tuesday announced the takedown of a long-standing peer-to-peer (P2P) botnet known as Sality as part of a coordinated law enforcement operation. The effort was undertaken on August 31, 2026, by authorities from the U.S., Bulgaria, Hungary, and Romania, in collaboration with private industry partners CrowdStrike and the Shadowserver […]
Risky Business #851 -- Agents are just ones and zeros, and tigers are just atoms
On this week’s show Patrick Gray and James Wilson are joined by guest co-host The Grugq to talk through the week’s news, including: Two alleged TeamPCP hackers got arrested in Australia The White House has a plan to boost security for water facilities, but we can’t see it working OpenAI keeps the ol’ Hugging Face […]
ISC Stormcast For Wednesday, September 2nd, 2026 https://isc.sans.edu/podcastdetail/10078, (Wed, Sep 2nd)
Post Content
Anthropic makes changes to stop AI agents running amok again
Learning from the OpenAI-Hugging Face fiasco, as well as from recent revelations about its own model, Anthropic is revamping its security and alignment practices. The company has established controls that flag when a model attempts to break out of a sandbox or successfully accesses the live internet, cordoned off its highest-risk test environments, and proposed […]
What happens when AI models take aim at ICS exploits
LLMs have shown great improvement in vulnerability research and exploit development capabilities over the past six months. But it’s one thing to find vulnerabilities in well documented open-source projects and an entirely different skillset to decrypt file systems and reverse-engineer closed-source low-level firmware in highly specialized embedded devices. That’s why researchers from industrial IoT security […]
FBI Probes Service Selling 153M+ Drivers Licenses
A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada. Based on interviews with individuals whose licenses are available for purchase on this service, it appears to be siphoning images collected by a widely-used […]
2024081842201 Ethan Heisey CRD 6799847 AWC lp.pdf
2024081842201 Ethan Heisey CRD 6799847 AWC lp.pdf Anonymous (not verified) Tue, 09/01/2026 – 18:30 Case ID 2024081842201 Document Number 40ac5e00 Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals Ethan Heisey Action Date Tue, 09/01/2026 – 12:00 Related Content Off Attachment 2024081842201 Ethan Heisey CRD 6799847 AWC lp.pdf Individual CRD 6799847
26-00507.pdf
26-00507.pdf Anonymous (not verified) Tue, 09/01/2026 – 17:25 Case ID 26-00507 Forum FINRA Document Type Award Claimants Faisal Aldemaiji Respondents Interactive Brokers LLC Neutrals Robert Elliot Harrison Hearing Site New York, NY Award Document 26-00507.pdf Documentum DocID 58f2e70e Award Date Official Tue, 09/01/2026 – 12:00 Related Content Off Claimant Representatives Faisal A. Aldemaiji Respondent Representatives […]
2024083956101 Daniel Schmid CRD 6658306 AWC lp.pdf
2024083956101 Daniel Schmid CRD 6658306 AWC lp.pdf Anonymous (not verified) Tue, 09/01/2026 – 16:35 Case ID 2024083956101 Document Number 842558ab Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals Daniel Schmid Action Date Tue, 09/01/2026 – 12:00 Related Content Off Attachment 2024083956101 Daniel Schmid CRD 6658306 AWC lp.pdf Individual CRD 6658306
2022076789501 Charles Schwab & Co., Inc. CRD 5393 AWC lp.pdf
2022076789501 Charles Schwab & Co., Inc. CRD 5393 AWC lp.pdf Anonymous (not verified) Tue, 09/01/2026 – 16:25 Case ID 2022076789501 Document Number abfa4933 Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals Charles Schwab & Co., Inc. Action Date Tue, 09/01/2026 – 12:00 Related Content Off Attachment 2022076789501 Charles Schwab & Co., Inc. CRD […]
CAMBRIDGE INVESTMENT RESEARCH, INC.
CAMBRIDGE INVESTMENT RESEARCH, INC. fnrw-backend Tue, 09/01/2026 – 16:20 MC ID CIRI MC Reporter Type Broker-Dealer MC Paragraph MC Link https://nms605.karngroup.com/7c302ab451306c5353513d3d MC Last Updated Tue, 09/01/2026 – 16:20
If we want to implement AI successfully, we need to completely change how we do businesses
I’ve always thought it was interesting that we’re willing to fight and die to live in a democracy, but everyone is happy to work in a company which is structured like a dictatorship. This thought feels even more pertinent given the rise of AI. As AI continues to transform the world of business, we’re starting […]
Now more than ever, CIOs need to be change agents
CIOs are increasingly expected to drive IT adoption in their organizations, with change management becoming a huge — and more challenging — imperative in the age of AI. Evangelism of the latest technologies has long been part of the job, but many CIOs now say resistance to AI adoption and the fast-paced evolution of IT […]
What changes when AI becomes part of how the business runs?
What changes when AI becomes part of how the business runs The more I speak with CIOs and technology leaders, the more I realize most of us are working through variations of the same AI challenge. How quickly should we move? Which opportunities are worth pursuing? What risks are acceptable? And how do we move […]
What is transformational leadership? A model for motivating innovation
What is transformational leadership? Transformational leadership is a leadership style that aims to encourage, inspire, and motivate employees to innovate and create the change necessary to shape the future success of the company. Underpinning the approach is an emphasis on setting an example at the executive level through authenticity, developing a strong sense of corporate culture, and fostering employee […]
Who gets to decide? The CIO and the new architecture of enterprise authority
For most of my career, technology governance began with a familiar set of questions: Is the system secure? Is it resilient? Does it meet the architecture standard? Can we afford it? Those questions still matter. But they are no longer enough. AI is moving rapidly from producing content and recommendations to initiating actions. It can […]
The access layer: an overlooked driver of modernization ROI
CIOs are being asked to improve user experience and strengthen identity controls while preserving access to the systems that still run critical workloads. Balancing those priorities becomes harder when the access environment has evolved piecemeal around the systems themselves. Yet the way employees securely connect to those systems often receives far less attention. Many organizations […]
Data readiness starts with reducing friction
Most organizations don’t realize they have a data readiness problem until they try to do something new with their data. I’ve seen organizations invest heavily in modernization only to discover they’re still spending too much time finding and validating data. Many have more information than ever before yet answering a simple business question can still […]
CrowdStrike launches cyber frontier AI models, agentic security system
CrowdStrike today announced SafeMind, a cybersecurity-specific AI model-harness system that CEO George Kurtz described as the “first complete agentic system for cybersecurity” at the company’s Fal.Con conference in Las Vegas. At the heart of SafeMind are two purpose-built cybersecurity models, the adversarial Red Tempest and the defensive Blue Solano. Both models have been trained on […]
Attackers Exploit Critical JFrog Artifactory Flaw to Mint Admin Tokens Days After Disclosure
Threat actors are exploiting a newly patched critical security flaw impacting JFrog Artifactory merely days after public disclosure, according to watchTowr. The vulnerability in question is CVE-2026-82329 (CVSS score: 9.8), a case of authentication bypass that could lead to administrative access in Artifactory. “JFrog Artifactory contains an authentication weakness that, under default
Breeze Comet Executes Hundreds of Fraudulent Transactions via Brazilian Payment Systems
Brazilian financial services, retail, and e-commerce organizations have become the target of a financially motivated threat actor dubbed Breeze Comet (formerly UNC5669) since 2024. Google Threat Intelligence Group (GTIG) and Mandiant teams described the threat actor as “specializing in manipulating payment systems and banking software in Brazil to conduct fraudulent transfers.” The adversary
13 Malicious Packagist Packages Target Unpatched iPhones to Steal Crypto Wallet Seeds
Cybersecurity researchers have identified a set of 13 malicious Composer theme packages on Packagist that are designed to inject JavaScript into Vietnamese movie and comic streaming sites that install those libraries and initiate the deployment of spyware aimed at unpatched iOS devices. “The injected code runs two operations against a site’s visitors: a mobile ad-fraud […]
Iranian Hackers Pose as Recruiters to Deliver Cross-Platform RATs Through Coding Tests
The Iranian Nimbus Manticore hacking group has been attributed to two previously undocumented malware families that highlight the continued evolution of its toolset and likely expand its targeting footprint to infect Linux and Apple macOS systems using cross-platform remote access trojans (RATs) developed using Node.js and JavaScript. Russian cybersecurity company Kaspersky is tracking the
OpenClaw rolls out system-wide overhaul, updates security controls across agent platform
OpenClaw has released what it describes as the largest update in its history, introducing a system-wide overhaul spanning runtime behavior, plugins, and security controls, as enterprises increasingly evaluate how such agent-based systems operate across connected environments. “This update touches every part of OpenClaw, including installation, messaging, memory, skills, models, automations, the browser and native apps, […]
IE: HSE fined €645,000 over data breach affecting Westmeath hospital
Adrian Cusack reports: The Data Protection Commission has fined the HSE [Health, Safety, and Environment] more than €600,000 over the mismanagement of historical records held at St Loman’s hospital, Mullingar, and St Conal’s Hospital, Letterkenny. The fine was issued at the conclusion of an inquiry into the handling of paper records at the two facilities… […]
Santa Fe Schools Move Forward With New Cybersecurity Policy
André Salkin reports: The Santa Fe school board approved a new cybersecurity policy this week but delayed a vote on a separate policy governing student data privacy, with most board members calling it too broad and too important to rush through. The delayed measure, Draft Policy 357, would govern how the district treats student data… […]
Rockwell Automation RSLinx Classic
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to cause a denial-of-service condition on the affected product. The following versions of Rockwell Automation RSLinx Classic are affected: RSLinx Classic <=4.50 (CVE-2026-9621, CVE-2026-9622, CVE-2026-9624, CVE-2026-9625) CVSS Vendor Equipment Vulnerabilities v3 8.6 Rockwell Automation Rockwell Automation RSLinx Classic Integer Overflow or Wraparound, Integer […]
Rockwell Automation Historian ME
View CSAF Summary Successful exploitation of these vulnerabilities could crash the device being accessed; an out-of-bounds write condition may allow remote code execution. The following versions of Rockwell Automation Historian ME are affected: Series B 5.202 (CVE-2025-12768, CVE-2026-12661) Series C 7.101 (CVE-2025-12768, CVE-2026-12661) CVSS Vendor Equipment Vulnerabilities v3 8 Rockwell Automation Rockwell Automation Historian ME […]
Rockwell Automation ControlLogix, CompactLogix, CompactLogix 5480, GuardLogix, Compact GuardLogix
View CSAF Summary The following versions of Rockwell Automation ControlLogix, CompactLogix, CompactLogix 5480, GuardLogix, Compact GuardLogix are affected: ControlLogix 5580 <34.015, <35.014, <36.013, <37.011 (CVE-2021-42260, CVE-2021-42260, CVE-2021-42260, CVE-2021-42260) GuardLogix 5580 <34.015, <35.014, <36.013, <37.011 (CVE-2021-42260, CVE-2021-42260, CVE-2021-42260, CVE-2021-42260) CompactLogix 5380 <34.015, <35.014, <36.013, <37.011 (CVE-2021-42260, CVE-2021-42260, CVE-2021-42260, CVE-2021-42260) Compact GuardLogix 5380 <34.015, <35.014, <36.013, <37.011 […]
Rockwell Automation Logix Platform
View CSAF Summary The following versions of Rockwell Automation Logix Platform are affected: ControlLogix 5580 <=V33, V34.011-V34.014, V35.011-V35.013, V36.011-V36.012 (CVE-2026-9637, CVE-2026-9637, CVE-2026-9637, CVE-2026-9637) CompactLogix 5380 <=V33, V34.011-V34.014, V35.011-V35.013, V36.011-V36.012 (CVE-2026-9637, CVE-2026-9637, CVE-2026-9637, CVE-2026-9637) GuardLogix 5580 <=V33, V34.011-V34.014, V35.011-V35.013, V36.011-V36.012 (CVE-2026-9637, CVE-2026-9637, CVE-2026-9637, CVE-2026-9637) Compact GuardLogix 5380 <=V33, V34.011-V34.014, V35.011-V35.013, V36.011-V36.012 (CVE-2026-9637, CVE-2026-9637, CVE-2026-9637, CVE-2026-9637) CVSS […]
Rockwell Automation Redundancy Module Configuration Tool
View CSAF Summary Successful exploitation of these vulnerabilities could allow for an attacker to escalate and execute processes with administrator privileges. The following versions of Rockwell Automation Redundancy Module Configuration Tool are affected: Redundancy Module Configuration Tool 10.00.00 (CVE-2026-9633) Redundancy Module Configuration Tool >=9.00.00|<=10.00.00 (CVE-2026-9634) CVSS Vendor Equipment Vulnerabilities v3 7.3 Rockwell Automation Rockwell Automation […]
Rockwell Automation FactoryTalk Activation Manager
View CSAF Summary The following versions of Rockwell Automation FactoryTalk Activation Manager are affected: FactoryTalk Activation Manager V5.02_and_below (CVE-2026-16675) CVSS Vendor Equipment Vulnerabilities v3 7.8 Rockwell Automation Rockwell Automation FactoryTalk Activation Manager Improper Restriction of Excessive Authentication Attempts Background Critical Infrastructure Sectors: Critical Manufacturing Countries/Areas Deployed: Worldwide Company Headquarters Location: United States Vulnerabilities Expand All […]
Fake Cloudflare CAPTCHA tricks victims into opening a tunnel for attackers
Attackers are using fake CAPTCHA prompts to trick victims into running malicious PowerShell commands as part of a multi-stage intrusion campaign that can establish persistence, conduct network reconnaissance and potentially give operators a path to deeper access within an organization. Microsoft Threat Intelligence said a campaign it calls TerminalFix, a variant of the ClickFix technique, […]
Ransomware Gang Claims Nutex Health Data Breach
The company has notified the SEC that hackers accessed patient, employee, provider, business, and financial information. The post Ransomware Gang Claims Nutex Health Data Breach appeared first on SecurityWeek.
Critical JFrog Artifactory Vulnerability Reportedly Exploited in the Wild
Exploitation of the authentication bypass vulnerability CVE-2026-82329 started just days after its public disclosure. The post Critical JFrog Artifactory Vulnerability Reportedly Exploited in the Wild appeared first on SecurityWeek.
9.5 Million Impacted by Aesto Health Data Breach
Hackers stole personal and health information from the healthcare technology company’s AWS infrastructure. The post 9.5 Million Impacted by Aesto Health Data Breach appeared first on SecurityWeek.
WatchGuard Patches Critical Vulnerabilities
Three critical issues in the Fireware OS iked process could allow unauthenticated attackers to execute arbitrary code remotely. The post WatchGuard Patches Critical Vulnerabilities appeared first on SecurityWeek.
PaperCut Exploitation Escalates to Active Intrusions
CISA has added the vulnerabilities tracked as CVE-2026-82078 and CVE-2026-81578 to its KEV catalog. The post PaperCut Exploitation Escalates to Active Intrusions appeared first on SecurityWeek.
Nightmare Eclipse Drops ‘HardBreacher’ Kaspersky Product Exploit
Kaspersky told SecurityWeek that it patched the vulnerability affecting its Endpoint Security product. The post Nightmare Eclipse Drops ‘HardBreacher’ Kaspersky Product Exploit appeared first on SecurityWeek.
ServiceNow Patches 3 Critical Code Injection Vulnerabilities
Attackers could exploit the security defects to execute arbitrary code and access or tamper with data. The post ServiceNow Patches 3 Critical Code Injection Vulnerabilities appeared first on SecurityWeek.
McKesson Confirms Data Breach as Attacker Deadline Looms
The ShinyHunters extortion group has claimed the theft of 284 million records from the company’s systems. The post McKesson Confirms Data Breach as Attacker Deadline Looms appeared first on SecurityWeek.
What the Hugging Face Incident Teaches Security Leaders About AI Agent Access
Security teams must treat autonomous agents as highly privileged identities. The post What the Hugging Face Incident Teaches Security Leaders About AI Agent Access appeared first on SecurityWeek.
Anthropic Warns Claude Users of Infostealer Malware Infections
The AI giant is logging customers out of their accounts and removing payment data to prevent unauthorized Claude usage. The post Anthropic Warns Claude Users of Infostealer Malware Infections appeared first on SecurityWeek.
China-linked hackers turn Cisco routers into covert attack infrastructure
A China-linked cyber espionage group has expanded beyond VMware environments to target network and authentication infrastructure that enterprises rely on to manage access and administer critical systems, according to new findings from incident response firm Sygnia. The threat actor, tracked by Sygnia as Fire Ant, targeted Cisco IOS XR routers in 2026, using them to […]
Attackers Steal METR API Key and Consume AI Credits Worth About $600,000
METR (short for Model Evaluation and Threat Research and pronounced “Meter”), a research non-profit that evaluates frontier artificial intelligence (AI) models for their ability to carry out long-horizon, agentic tasks, disclosed that it suffered “two notable security incidents” where external actors attempted to gain unauthorized access to its systems. No sensitive information is believed to
Russia-Aligned UAC-0099 Plants Nuclear Weapon Prompt in Malware to Disrupt AI Analysis
Cybersecurity researchers have disclosed a new technique dubbed GuardBreaker that’s been put to use by a Russia-aligned threat actor known as UAC-0099 against a target in Ukraine with an aim to interfere with artificial intelligence (AI)-assisted analysis. The idea, ESET said in a series of posts on X, is to deliberately trip a large language […]
Microsoft nudges enterprise security closer to its passwordless future. But ‘123456’ will survive.
Today marks the beginning of the end of an era for enterprise Microsoft authentication. As of Sept. 1, passkeys are now the default authentication method for Entra ID, Microsoft’s cloud-based identity and access management (IAM) service. By Feb. 1, 2027, Microsoft-provided SMS and voice authentication will be a thing of the past. The move is […]
Attackers Exploit Critical Langflow and Rails Flaws in Credential-Probing and C2 Activity
Threat actors are exploiting two critical flaws impacting Langflow and Ruby on Rails, according to new findings from VulnCheck. The vulnerabilities in question are listed below – CVE-2026-0768 (CVSS score: 9.8) – A lack of proper validation of a user-supplied input vulnerability that could be exploited to execute arbitrary Python code in the context of […]
ISC Stormcast For Tuesday, September 1st, 2026 https://isc.sans.edu/podcastdetail/10076, (Tue, Sep 1st)
Post Content
Guildma (Astaroth) malware infection from Brazilian Portuguese email, (Tue, Sep 1st)
Introduction