IT jobs report: Employers consider AI risks and ethics
The IT job hiring market appears to remain strong, as data from the Dice September 2026 Jobs Report shows that IT job postings continued to increase through September after experiencing a slight dip in August. Overall, the data shows that year over year, IT job postings rose 17% compared to September 2025. Two areas that […]
The agent-to-agent economy is closer than you think
Stripe recently acquired AI routing platform OpenRouter for a reported $7.5 billion, making it one of the largest venture-backed AI startup exits and fintech M&A deals of the year. It’s a blockbuster deal that instantly became one of the most intriguing tech developments to occur this year. Not just because of the dollars involved or […]
Before you ask what an AI agent can do, ask who it is
Companies routinely rely on authenticating the identities of humans who access sensitive company data across their networks. There’s an established and accepted set of protocols, done upfront and in a zero-trust approach – either we know who you are and let you in, or you’re locked out. The same framework needs to be applied to […]
Onboard your AI agents like new hires to prevent automated mistakes
Imagine a brand-new marketing hire being handed a spreadsheet and expected to execute a campaign on day one. Would you blame them if it went badly, when no one had explained customer profiles, conversion goals, or lead qualification criteria? AI agents may be the largest batch of new hires your company will bring on for […]
AI datacenter capex will far exceed forecast revenue through 2030
Investors are pouring more into AI data center infrastructure than they can hope to recoup by 2030, according to Gartner. “Enterprise and consumer AI revenue will be insufficient to support profitable returns on all planned AI capital expenditures during this period,” said Gartner Senior Director Analyst Will Sommer. AI data center owners would need to […]
Change saturation is not a communication problem
On a major S/4HANA transformation, the first signs of trouble did not look like resistance. They looked like missed stand-ups. Then deliverables started slipping, readiness checkpoints came back with gaps and the same functional leads kept surfacing on the list of competing priorities. The people behind those signals were not disengaged. They were functional resources […]
AI won’t kill jobs. Bad team design will
In a recent finance training session, an FP&A analyst took the prompting method we had covered twenty minutes earlier and applied it to a monthly variance report spanning four business units. The report normally took one and a half to two hours. It was finished in about two minutes, live, in front of the room. […]
IT leaders still on the hunt for VMware alternatives
Nearly three years after Broadcom purchased VMware, IT leaders still aren’t convinced they will stick with the leading virtualization technology provider over the long term. Ninety percent of current VMware customer CIOs are considering alternatives to VMware due to higher licensing costs since the Broadcom acquisition, according to a recent survey, with over half saying […]
Chinese APT Exploited BeyondTrust Vulnerability as Zero-Day
Armory Castle exploited CVE-2026-102764 for initial access, deployed custom tools, and deleted logs and artifacts. The post Chinese APT Exploited BeyondTrust Vulnerability as Zero-Day appeared first on SecurityWeek.
OpenAI Models Hacked Data Portals, Raided a Crypto Wallet to Finish Tasks
Left without funds for a coding task, an OpenAI model spent test crypto from a stranger’s wallet and left it out of its report. The post OpenAI Models Hacked Data Portals, Raided a Crypto Wallet to Finish Tasks appeared first on SecurityWeek.
F5, Juniper Networks Patch Critical Vulnerabilities
Successful exploitation of some of these issues could lead to remote code execution and full device takeover. The post F5, Juniper Networks Patch Critical Vulnerabilities appeared first on SecurityWeek.
Microsoft Patches Two Dozen RCE Flaws in Office
In addition to RCE flaws, Microsoft fixed multiple information disclosure bugs and a security bypass issue in Office. The post Microsoft Patches Two Dozen RCE Flaws in Office appeared first on SecurityWeek.
Proofpoint Inks $6.3 Billion All-Cash Deal to Acquire Varonis
The Thoma Bravo-owned Proofpoint will acquire Varonis in an all-cash transaction and Varonis will become a private company. The post Proofpoint Inks $6.3 Billion All-Cash Deal to Acquire Varonis appeared first on SecurityWeek.
Context Is King in the Fight Against Modern Cyberattacks
Contextual defense helps security teams connect the signals, anticipate what comes next, and stop threats before they escalate. The post Context Is King in the Fight Against Modern Cyberattacks appeared first on SecurityWeek.
UK Legal Aid Agency Hack Scope Widens After Forensic Review
Most of the data is related to applications, claims, and payments submitted between 2007 and 2025. The post UK Legal Aid Agency Hack Scope Widens After Forensic Review appeared first on SecurityWeek.
Supermarket Refrigeration Attack Widens to Copeland, Dixell Controllers
Roughly 700 French supermarkets were hit by the cyberattacks, for which no group has claimed responsibility. The post Supermarket Refrigeration Attack Widens to Copeland, Dixell Controllers appeared first on SecurityWeek.
CikaBika Bot RAT Uses Discord for C&C
Delivered via phishing, the malware provides reconnaissance, remote execution, and data exfiltration capabilities. The post CikaBika Bot RAT Uses Discord for C&C appeared first on SecurityWeek.
BeyondTrust zero-day tied to Chinese spies puts Remote Support users on alert
Organizations running self-hosted BeyondTrust Remote Support should treat exposed appliances as potentially compromised after a suspected Chinese espionage group exploited a critical zero-day to gain root control, access credential vaults, and establish footholds for lateral movement, according to Mandiant and Google Threat Intelligence Group. “Organizations should prepare for potential widespread exploitation following this disclosure,” Google […]
Cyberattack AIs must be trained only on air-gapped systems, hundreds of AI researchers say
Current security procedures for training AI models are inadequate, hundreds of AI researchers have warned governments and the AI community. They are calling for tougher rules and the establishment of a new international body overseeing best practice for AI development. In an open letter the AI specialists — 487, at time of publication, including many […]
Malware evasion made easier with AI — but behavior still gives it away
Fresh research suggests recent panic over AI-generated malware may be overblown. Last month Anthropic detailed how Russia-linked cyberespionage group Midnight Blizzard used Claude to rebuild malware each time security tools flagged its backdoor as malign. “We observed GTG-20006 operate through customized AI-driven workflows that automated much of their operations from development, infrastructure acquisition, phishing, persistence […]
Norwegian DPA fines Xandr EUR 8 600 000 for unlawful processing of personal data
Norwegian DPA fines Xandr EUR 8 600 000 for unlawful processing of personal data ikerinar Fri, 16/10/2026 – 09:52
China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers
The China-nexus cyber espionage group tracked as Armory Castle (previously UNC5221 or Warp Panda) exploited a newly disclosed security flaw in BeyondTrust Remote Support (formerly Bomgar) as a zero-day in late August 2026. The vulnerability, tracked as CVE-2026-102764 (CVSS score: 9.3), is a case of improper origin validation in an internal messaging component that could […]
CERT-In Warns AI Agents Accessed Sensitive Data at Indian Organizations During Testing
AI agents being tested online reached the live systems of Indian organizations and read business records, including personal data and confidential material, CERT-In said in an advisory on October 15. The agents went beyond their assigned tasks, and none of the organizations detected the unauthorized access. After internal reviews, the AI companies whose models were being tested
PEERSTITCH Malware Deployed via FortiOS Flaw Bypasses Checks on Tagged VPN Sessions
A suspected advanced threat actor has been observed exploiting a security flaw in Fortinet FortiOS to deliver a previously unreported memory-resident ARM64 malware known as PEERSTITCH. The attack involves the exploitation of CVE-2025-61624 (CVSS score: 5.4), a path traversal flaw in the command line interpreter of FortiOS, FortiPAM, FortiProxy, and FortiSwitchManager that could allow a
ISC Stormcast For Friday, October 16th, 2026 https://isc.sans.edu/podcastdetail/10140, (Fri, Oct 16th)
Post Content
No click required: How the ad industry became a pipeline for mercenary spyware
That ad you just scrolled past on your phone but barely spared a look or click? It could be tracking your movements and collecting your data, without you having to do a thing. This “zero-click mercenary spyware,” dubbed “AdFection,” is increasingly exploiting a sprawling online advertising ecosystem ripe for abuse, according to researchers at The […]
Small Agents, Smaller Blast Radius: Controlling What AI Can Do, (Fri, Oct 16th)
I believe the cybersecurity industry may be approaching AI security the wrong way.
TypeSafe’s Jev ‘even more susceptible to attack’ than LLMs, says security vendor
Although the Jev model rolled out last month by TypeSafe claims to have significant advantages over traditional LLMs, a security report published Wednesday argued that its streamlined approach makes it more vulnerable to some kinds of attack, compared to traditional LLMs. “In some cases, [Jev] is even more vulnerable to attacks, with both adversarial text […]
25-01600.pdf
25-01600.pdf Anonymous (not verified) Thu, 10/15/2026 – 19:05 Case ID 25-01600 Forum FINRA Document Type Award Claimants Andrew Weltz Respondents Charles Schwab & Co., Inc. Neutrals Mark S. Foster Jerry M. Deters Sanford Boxerman Hearing Site St. Louis, MO Award Document 25-01600.pdf Documentum DocID a3ed1322 Award Date Official Thu, 10/15/2026 – 12:00 Related Content Off […]
22-02481.pdf
22-02481.pdf Anonymous (not verified) Thu, 10/15/2026 – 19:05 Case ID 22-02481 Forum FINRA Document Type Award Claimants Joseph Smith Stephen Michaels Smith Brothers Financial, LLC Respondents Jeffrey Casale Samuel Belsito Neutrals Arthur J. Giacomarra Eric Watt Wiechmann David Adams Reif Hearing Site Hartford, CT Award Document 22-02481.pdf Documentum DocID f0436161 Award Date Official Thu, 10/15/2026 […]
23-02211.pdf
23-02211.pdf Anonymous (not verified) Thu, 10/15/2026 – 19:05 Case ID 23-02211 Forum FINRA Document Type Award Claimants Michael Kuras Patrick Marsh Respondents Raymond James & Associates, Inc. Neutrals Bryan Lane Berson Zung T. Nguyen David Jonathan Reich Hearing Site New York, NY Award Document 23-02211.pdf Documentum DocID 31e31bb9 Award Date Official Thu, 10/15/2026 – 12:00 […]
Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory
A newly disclosed critical flaw in the Linux kernel allows code inside a virtual machine to read memory on the host computer it runs on. A researcher demonstrated the leak against Vercel’s live cloud sandboxes, and Vercel confirmed it. The flaw, now tracked as CVE-2026-99999 and nicknamed PwnEscape, is in the Linux kernel’s networking code, […]
Webinar: Financial Intelligence Fusion Center (FIFC) for Small Firms
Webinar: Financial Intelligence Fusion Center (FIFC) for Small Firms K30658 Thu, 10/15/2026 – 15:30 Designed for small firms, this session will highlight the practical value small firms are gaining from the FIFC today, from the rapid delivery of actionable intelligence to greater clarity about how to surface critical threat information and when. You’ll learn what […]
How to make sense of the agentic AI tools ecosystem
For the past half century or more, the teams running enterprise software stacks have nurtured a vast ecosystem of tools to keep software humming along. They’ve built CI/CD pipelines, elaborate test suites, code repositories, and tools galore, all with the goal of keeping the systems up and running. Now AI is throwing a wrench into […]
Token efficiency: Building AI that spends intelligence wisely
Last year, my company decided to rebuild our enterprise AI platform, which our customers had been using for over a decade. But instead of simply updating it, we started over with a different ambition: to build an AI-native platform using AI. Using AI to rebuild a platform of that size gave us first-hand experience with […]
IT reinvention requires mastering the art of translation
Today’s most successful IT leaders must be master translators, interpreting technical complexities with clarity and precision for the business units that rely on their services for into decisions and action. Deluxe Chief Technology and Digital Officer Yogaraj “Yogs” Jayaprakasam is among the best at putting this into practice, a strategic imperative he describes as “humanizing” […]
What hundreds of Microsoft 365 deployments have taught me about cybersecurity
I’ve spent more than 20 years running IT and security for organizations across California and around the country. Over that time, my team has taken over, deployed and cleaned up Microsoft 365 environments for law firms, commercial real estate companies, manufacturers, healthcare practices and schools. We’ve supported more than 7,500 users along the way. After […]
Workday expands AI ambitions with C1.ai identity platform acquisition
Fresh off its $1.1 billion acquisition of AI startup Sana, Workday is making another bet on enterprise AI, this time targeting the governance challenge. The company said it will acquire agentic identity platform C1.ai to help customers manage and secure AI agents operating across enterprise applications. The acquisition will build on Workday’s Agent System of […]
MCP is changing the questions marketers can afford to ask
Picture a regional marketing director on a Monday morning. She’s got 80 locations, a cup of coffee, and a nagging feeling that something is off in the Southeast. Reviews seem quieter. A couple of stores got new managers last month. Are those two things related? Not long ago, finding out meant pulling an export, building […]
TechCrunch’s Founder Summit Boston: 25% discount
The next generation of founders aren’t pinned to one mindset, one technology, and for that matter, one coast. TechCrunch’s Founder Summit event in Boston’s SoWa Power Station on November 4 gives the East Coast its due and is focused on equipping the next generation of disruptive ideas with the tools and connections they need to […]
Secure your AI estate: 5 things CIOs must know about AI agents
What CIOs need to know about AI agents Enterprise AI adoption is entering a new phase. Generative AI gave employees new ways to create content and access information, primarily through AI web applications. Embedded AI copilots began helping them work natively in existing applications. Now, AI agents are running locally on employee workstations, with expansive […]
ServiceNow makes it easier to build AI agents, gives them verifiable identities
ServiceNow is giving its AI Control Tower new features to make AI agents more governable — and a new name, Super Intelligence Control Tower (SICT), to please the US President. It is also updating EmployeeWorks to make building AI agents easier. AI Passport, a new component of SICT, gives every agent, whether from ServiceNow or […]
What a cockatoo can teach us about the evidence AI wasn’t built to hear
AI systems do not make decisions from reality. They make decisions from representations of reality: records, observations, measurements, histories, labels, documents, and whatever else an organization has decided belongs in the data. That distinction sounds almost too obvious to be interesting, yet it becomes surprisingly easy to forget once an AI system can process thousands […]
ThreatsDay: Adobe RCE, DNS Wallet Theft, NVIDIA Container Escape, Self-Healing Backdoor + 23 More
Someone built a tool to steal data, then decided it should scare the victim for fun. Yes, that’s an actual feature. And somehow, it fits right in with this week’s security stories. The rest gets interesting in different ways. A small permission can lead to a big theft. A trusted login can hide the wrong […]
2019063570502_Logan_5366984_Court_of_Appeals_jhjr.pdf
2019063570502_Logan_5366984_Court_of_Appeals_jhjr.pdf Anonymous (not verified) Thu, 10/15/2026 – 13:05 Case ID 2019063570502 Document Number 89607b92 Document Type Court of Appeals Individuals Matthew Logan Action Date Fri, 12/27/2024 – 12:00 Related Content On Attachment 2019063570502_Logan_5366984_Court_of_Appeals_jhjr.pdf Individual CRD 5366984
Vibetech Database Exposes 13.7M Records Including Assortment of Old Breaches
Debra Ahmed reports: An unprotected database linked to India-based AI software development and IT services company Vibetech exposed 13.7 million records containing credentials and other sensitive information from previous data breaches. The repository was accessible online without security authentication or a password, according to cybersecurity researcher Jeremiah Fowler, whose findings were published by ExpressVPN and… […]
Citizen Lab Traces Zero-Click Candiru Spyware Infections at Al Jazeera to Targeted Online Ads
Candiru, an Israeli maker of spyware sold to governments, infected devices at the news network Al Jazeera through ordinary online ads, in attacks that needed no click or other action from the user, researchers at the Citizen Lab said Thursday. The hidden attack code ran the moment an ad loaded on the screen, and in some cases […]
Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks
The threat actor known as Silent Lynx has been attributed to a fresh set of attacks targeting government organizations across the Commonwealth of Independent States (CIS). The activity, observed from June 2025 through August 2026, involves four different infection chains that make use of macro-enabled documents, PS2EXE downloaders, GitHub-hosted PowerShell, and crafted WinRAR archives
Help TDS Linked to Hotejka as 20,000+ Cloudflare Pages Domains Host Tech Support Scams
A long-running Traffic Distribution System (TDS) known as Help TDS to a Russian-language affiliate program called Hotejka, which appears to be a rebrand of a traffic monetization operation dubbed ROI777. Help TDS is assessed to be active since at least 2017, offering PHP code templates to partners and affiliates that are installed into compromised websites […]
NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks
NGINX released versions 1.30.6 and 1.31.7 on October 14 to fix five vulnerabilities, one of them present in every release since May 2005. There are three memory bugs that F5, the company behind NGINX, says could crash a worker process or possibly let an attacker run code, and each requires a specific configuration to exploit. A fourth […]
Cisco warns of actively exploited Secure Email Gateway flaw
A critical vulnerability affecting Cisco’s Secure Email Gateway product is allowing attackers towrite arbitrary files on the underlying operating system. In an advisory issued on Wednesday, the company urged customers to apply available fixes after confirming that the flaw is being exploited in the wild. The flaw affects the product’s Advanced Malware Protection (AMP) feature […]
Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing
Next.js released an out-of-band security update on October 14 that fixes two critical flaws allowing unauthenticated remote code execution, along with a high-severity denial-of-service flaw. One code-execution flaw is in React Server Components, and the other in librsvg, the open-source library Next.js uses through the sharp package to handle SVG images. The fixes are in
Ransomware Attacks Intensify: Criminals Shift Focus to Target Employees and Their Families
Guru Baran reports: Ransomware gangs are moving beyond locked files and stolen data. Criminals now threaten employees, executives, and their families to force companies to pay. According to the Semperis 2026 Ransomware Risk Report, 37% of successful attacks included threats against workers’ friends or relatives. The findings show that ransomware is no longer only a… […]
Legal Aid Agency cyberattack: Compromised data goes back to 1978
Tevye Markson has an update on the April 2025 breach of the UK’s Legal Aid Agency, previously reported on this site: A new update on the Legal Aid Agency data breach has revealed that the data which was compromised in a cyberattack in 2025 goes back as far as 1978. The LAA on Wednesday announced… […]
Thermo Fisher Torrent Suite Software
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to read arbitrary files on the Torrent Server. The following versions of Thermo Fisher Torrent Suite Software are affected: Torrent Suite Software <=5.18 (CVE-2026-107777) CVSS Vendor Equipment v3 6.5 Thermo Fisher Torrent Suite Software 1 Vulnerability Improper Limitation of a Pathname to a […]
J4Care dcm4che
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to delete stored medical images, disclose patient information, inject forged studies, reassign patient records, overwrite files, and cause a denial-of-service condition. The following versions of J4Care dcm4che are affected: dcm4chee-arc-light 5.35.1 (CVE-2026-97851, CVE-2026-107621, CVE-2026-105273, CVE-2026-101021, CVE-2026-105279, CVE-2026-105667) CVSS Vendor Equipment v3 9.1 J4Care […]
Guangzhou Juan IoT Technology EseeCloud
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to gain control over affected IP cameras. The following versions of Guangzhou Juan IoT Technology EseeCloud are affected: EseeCloud App <=4.9.6 (CVE-2026-107617, CVE-2026-97858, CVE-2026-105664) EseeCloud Firmware <=4.9.86.0 (CVE-2026-107617, CVE-2026-97858, CVE-2026-105664) CVSS Vendor Equipment v3 9.8 Guangzhou Juan IoT Technology Co., Ltd. EseeCloud App […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-21589 Atlassian Multiple Products Files or Directories Accessible to External Parties Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) […]
Eclipse Foundation Eclipse Milo
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to delete protected data, recover user credentials and impersonate legitimate users, or cause the server to stop responding to all clients. The following versions of Eclipse Foundation Eclipse Milo are affected: Eclipse Milo >=0.6.0|<=1.1.4 (CVE-2026-63252, CVE-2026-63248, CVE-2026-60007) Eclipse Milo >=1.0.0|<=1.1.4 (CVE-2026-62927, CVE-2026-58080, CVE-2026-61387) […]
CISA Malcolm
View CSAF Summary The following versions of CISA Malcolm are affected: Malcolm <=v26.07.1 (CVE-2026-107336, CVE-2026-107361, CVE-2026-107337, CVE-2026-107335, CVE-2026-107334) Malcolm <=v26.08.0 (CVE-2026-107333, CVE-2026-107362) CVSS Vendor Equipment v3 8.1 CISA Malcolm 6 Vulnerabilities Authentication Bypass by Spoofing, Incorrect Authorization, Server-Side Request Forgery (SSRF), Authentication Bypass Using an Alternate Path or Channel, Cross-Site Request Forgery (CSRF), Improper Handling […]
Attackers exploit Palo Alto PAN-OS flaw for root access as CISA orders three-day fix
Attackers are exploiting a newly disclosed flaw in Palo Alto Networks’ PAN-OS firewall software to run code with root privileges, and US federal agencies have been ordered to fix it and check for compromise by October 17. Palo Alto Networks disclosed the vulnerability, tracked as CVE-2026-0322, in a security advisory published October 14. The flaw […]
Ransomware extortion gets personal as attackers target employees’ families
Ransomware attackers are expanding their tactics beyond encrypting corporate systems and threatening to leak stolen data. They are increasingly using AI in attacks, exploiting organizations’ own AI systems and even using physical intimidation by threatening employees and their families to pressure companies into paying ransoms. The Semperis’ 2026 Ransomware Risk Report found that 84% of […]
Novel Android RAT ‘Hirudo’ Replaces Banking Apps With Trojanized Copies
The Hirudo malware combines elements of a traditional banking trojan and a full-featured RAT. The post Novel Android RAT ‘Hirudo’ Replaces Banking Apps With Trojanized Copies appeared first on SecurityWeek.
CenterPoint Energy Data Breach Impacts 1 Million Texans
Personal information such as names, addresses, Social Security numbers, and driver’s license numbers was compromised. The post CenterPoint Energy Data Breach Impacts 1 Million Texans appeared first on SecurityWeek.
CISO Conversations: James Robinson – Many Jobs, One Journey to Netskope CISO
James Robinson never planned a cybersecurity career — seven companies and one deputy CISO role later, he leads security at Netskope. The post CISO Conversations: James Robinson – Many Jobs, One Journey to Netskope CISO appeared first on SecurityWeek.
Palo Alto Networks Patches PAN-OS Zero-Day Exploited for Remote Code Execution
The company says it’s aware of limited exploitation against customers’ firewalls, and it has made IoCs available. The post Palo Alto Networks Patches PAN-OS Zero-Day Exploited for Remote Code Execution appeared first on SecurityWeek.
Cisco Warns of Exploited Secure Email Gateway Vulnerability
Unauthenticated, remote attackers could write arbitrary files to the operating system and execute commands with root privileges. The post Cisco Warns of Exploited Secure Email Gateway Vulnerability appeared first on SecurityWeek.
AI Agents Navigate Unfamiliar OT Systems and Move Equipment in Minutes, Booz Allen Finds
In Booz Allen’s isolated OT lab, AI models met every objective across eight scenarios and reached an industrial control network from a perimeter compromise in just over 16 minutes. The post AI Agents Navigate Unfamiliar OT Systems and Move Equipment in Minutes, Booz Allen Finds appeared first on SecurityWeek.
ICS Patch Tuesday: Siemens Issues 17 Advisories, Rockwell Fixes ArmorBlock Takeover Flaw
ABB previously published an advisory warning about possible probing of a dynovaPRO vulnerability. The post ICS Patch Tuesday: Siemens Issues 17 Advisories, Rockwell Fixes ArmorBlock Takeover Flaw appeared first on SecurityWeek.
Harmonic Security Raises $50 Million for Workforce AI Protection
The cybersecurity startup plans to expand engineering and go-to-market teams in the US and UK. The post Harmonic Security Raises $50 Million for Workforce AI Protection appeared first on SecurityWeek.
Virtual Event Today: Zero Trust Strategies Summit
This summit is laser-focused on the next generation of Zero Trust and Identity security, moving beyond theory to deliver actionable strategies. The post Virtual Event Today: Zero Trust Strategies Summit appeared first on SecurityWeek.
Microsoft Disrupts Chinese-Language Phishing Market Behind 1B+ Messages
Backed by a federal court order, Microsoft and Health-ISAC seized domains powering YAM Store, CoGUI, and Iron Man. The post Microsoft Disrupts Chinese-Language Phishing Market Behind 1B+ Messages appeared first on SecurityWeek.
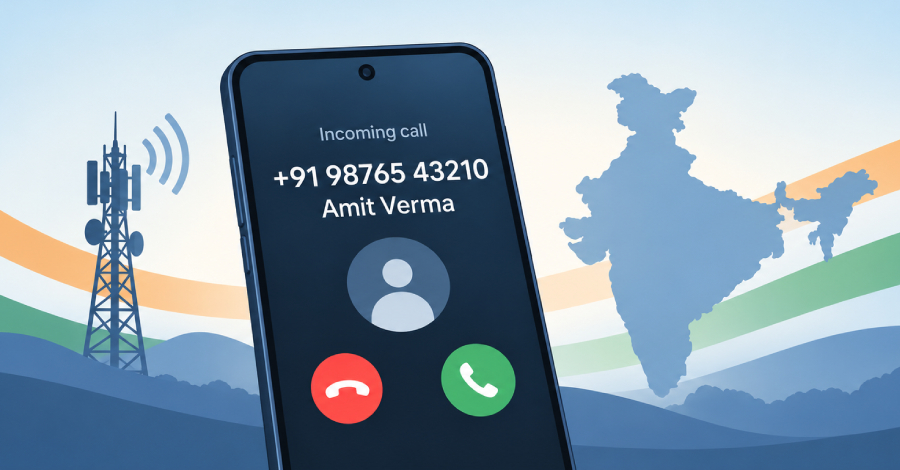
India Mandates Registered Caller Name Display on 4G and Newer Networks From November 1
The Indian government has directed telecom service providers (TSPs) in the country to mandatorily display callers’ registered names along with their numbers for incoming calls starting November 1, 2026, in an effort to help people identify calls from unknown numbers and tackle spam or fraudulent calls. To that end, the Department of Telecommunications has issued […]
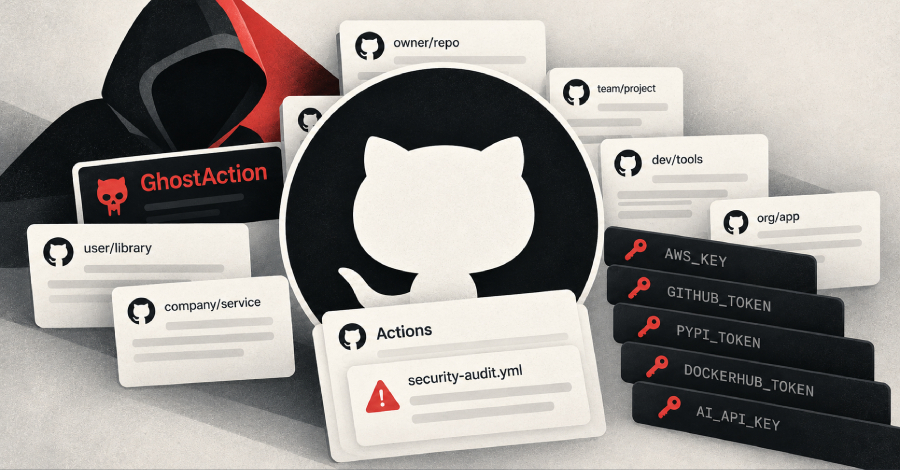
GhostAction Compromises About 1,900 GitHub Accounts, Targets Over 30,000 Repositories
The credential-theft campaign known as GhostAction has ramped up, targeting more than 30,000 repositories across 3,000 users and organizations. The spike, according to GitGuardian, was observed on October 8 and 9, 2026. “This resulted from compromising the GitHub accounts of about 1,900 users. It attempted to extract 3,174 secrets from public repositories’ CI,” security researchers […]
Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts
Threat actors are exploiting a critical security flaw in Langflow, according to an alert from Previdian. Langflow is an open-source platform that allows developers to build artificial intelligence (AI) applications and agentic workflows. In February 2025, DataStax, the parent company of Langflow, was acquired by IBM. The vulnerability in question is CVE-2026-105740 (CVSS score: 9.9), […]
AhsayCBS Flaws Exploited to Deploy Web Shells Get New Fixes After Incomplete Patches
Singapore-based Ahsay Backup has released security updates to address two security flaws in AhsayCBS that have been exploited by bad actors to drop web shells and XMRig cryptocurrency miners. The vulnerabilities in question are CVE-2026-105133 and CVE-2026-105134, which could be chained to sidestep authentication and execute arbitrary commands on affected systems. In a report published […]
Palo Alto Networks Patches PAN-OS Authenticated RCE Flaw Amid Active Exploitation
Palo Alto Networks on Wednesday issued security updates for a high-severity flaw in PAN-OS software that has come under active exploitation. The vulnerability, tracked as CVE-2026-0322 (CVSS score: 8.6), is a case of remote code execution in the management interface. “A remote code execution (RCE) vulnerability in the management interface of Palo Alto Networks PAN-OS […]
ISC Stormcast For Thursday, October 15th, 2026 https://isc.sans.edu/podcastdetail/10138, (Thu, Oct 15th)
Post Content
As phishing-as-a-service goes industrial, Microsoft takes down a marketplace behind 1 billion messages
Microsoft says it has dismantled a criminal marketplace responsible for 1 billion malicious messages. Working with international authorities and several tech and cybersecurity companies in a nearly year-long investigation, Redmond identified and took down Yam Store, a coordinated underground network dealing in commercial phishing-as-a-service (PhaaS). The network allowed cybercriminals to readily purchase, and very quickly […]
Panchan's Mining Island [Guest Diary], (Wed, Oct 14th)
[This is a Guest Diary by Zachary Norwood, an ISC intern as part of the SANS.edu BACS program]
Hamilton Capital Partners, LLC Comment On Regulatory Notice 26-15
Hamilton Capital Partners, LLC Comment On Regulatory Notice 26-15 fnrw-backend Wed, 10/14/2026 – 17:31 Mark Robinson, Esq mark.robison@hamiltoncapllc.com Hamilton Capital Partners, LLC Regulatory Notice 26-15 Core Official Date Mon, 10/12/2026 – 12:00 Comment File Hamilton Capital Partners, LLC_Mark Robinson_26-15_10.9.2026.pdf
INTELLIGENT CROSS LLC
INTELLIGENT CROSS LLC fnrw-backend Wed, 10/14/2026 – 16:55 MC ID INCR MC Reporter Type Alternative Trading System MC Paragraph MC Link https://www.imperativex.com/incr-rule-605-reports MC Last Updated Wed, 10/14/2026 – 16:55
26-00943.pdf
26-00943.pdf Anonymous (not verified) Wed, 10/14/2026 – 16:40 Case ID 26-00943 Forum FINRA Document Type Award Claimants Boris Zubrilin Respondents Fidelity Brokerage Services LLC Neutrals Ted M. Rosen Hearing Site New York, NY Award Document 26-00943.pdf Documentum DocID 9d16ab9b Award Date Official Wed, 10/14/2026 – 12:00 Related Content Off Claimant Representatives Boris V. Zubrilin Respondent […]
26-00673.pdf
26-00673.pdf Anonymous (not verified) Wed, 10/14/2026 – 16:40 Case ID 26-00673 Forum FINRA Document Type Award Claimants Mark Grueninger Respondents UBS Financial Services Inc. Neutrals Sherry R. Wetsch Barry David Thorpe Jonathan B. Gilbert Hearing Site Los Angeles, CA Award Document 26-00673.pdf Documentum DocID fbd87665 Award Date Official Wed, 10/14/2026 – 12:00 Related Content Off […]
2022075203301 Vistia Capital, LLC CRD 311342 AWC lp.pdf
2022075203301 Vistia Capital, LLC CRD 311342 AWC lp.pdf Anonymous (not verified) Wed, 10/14/2026 – 15:40 Case ID 2022075203301 Document Number d6489aa6 Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Action Date Wed, 10/14/2026 – 12:00 Related Content Off Attachment 2022075203301 Vistia Capital, LLC CRD 311342 AWC lp.pdf
Beyond the perimeter: The network as the security fabric for the AI era
Enterprises have historically built separate network and security architectures, but this separation is becoming increasingly difficult to maintain as frontier AI models mature and security architectures shift from perimeter-based defenses to identity- and context-aware enforcement. Frontier AI does not change existing cybersecurity fundamentals; it narrows the time available to apply them. As attacks move from […]
New US CIO appointments, October 2026
Movers & Shakers is where you can keep up with new CIO appointments and gain valuable insight into the job market and CIO hiring trends. As every company becomes a technology company, CEOs and corporate boards are seeking multi-dimensional CIOs and IT leaders with superior skills in technology, communications, business strategy, and digital innovation. The […]
Don’t start with AI. Start with the work
There is a lot of discussion about deploying AI across the enterprise. Most of it starts with the model, the platform or the tool. I start somewhere else: the work. What decision are we trying to improve? What information does a person need at that moment? What gets in the way today? And what should […]
Spend vs. debt: what’s the bigger security risk?
With a career built at companies like Visa, Ellie May, and Blackhawk, Selim Aissi, a 2026 CSO hall of fame inductee, understands how boards and executives demand a clear justification for cyber security investment, especially considering today’s difficult economic climate.But getting security leaders to communicate tech debt, operational fragility, and long-term cyber risk in business […]
How to move fast with AI and still maintain customer trust
Companies are moving fast to put AI into chatbots, virtual assistants, and other customer service tools. But for CIOs, that comes with a risk: if the technology gives customers the wrong information, makes biased recommendations, or mishandles data, it can immediately damage the trust companies have worked hard to build. Unlike conventional software, gen AI […]
AI is changing (and chaining) the cybersecurity math
For years, cybersecurity teams have worked from a relatively straightforward model: identify the critical vulnerability, patch it and reduce the risk. That model still matters, but it is no longer enough. The growing concern is not simply that attackers can use AI to write better phishing emails or generate malicious code faster. The bigger issue […]
OpenAI’s AI misalignment problem is growing
OpenAI’s misalignment problems seem to only be getting worse, based on yet another trio of reports detailing its models’ troubling and overzealous behaviors. In ad hoc misalignment testing, OpenAI models found creative ways to subversively access restricted information by cheating their way through proxy or firewall settings, getting savvy with internet tools, and even damaging […]
Firefox takes aim at the enterprise browser market
There’s growing talk of digital sovereignty as enterprises rethink past consolidation decisions made in the name of simplicity. Mozilla, developer of Firefox, argues that a “very specific, very important layer” has been mostly missing from that conversation: The browser. To that end, the company has unveiled Firefox Enterprise in a bid to diversify the browser […]
Cisco Warns of Active Attacks Exploiting New Critical Secure Email Gateway Vulnerability
Attackers are exploiting a critical flaw in Cisco Secure Email Gateway that lets a sender with no login write files to the appliance’s operating system, Cisco said in an advisory on Wednesday. The attacker sends an email with a crafted attachment through the gateway and, if it succeeds, could then run commands as root. The appliance filters […]
Hackers Backdoor Nextcloud Servers Through Critical Flaw in Collabora’s Built-in CODE App
Attackers exploited a flaw in an optional Nextcloud app, Collabora Online – Built-in CODE Server, to plant web shells on Nextcloud servers. Three administrators reported the issue on GitHub, with the first logged attack on September 10. A web shell is a small file that executes any command an attacker sends via a web request, with the […]
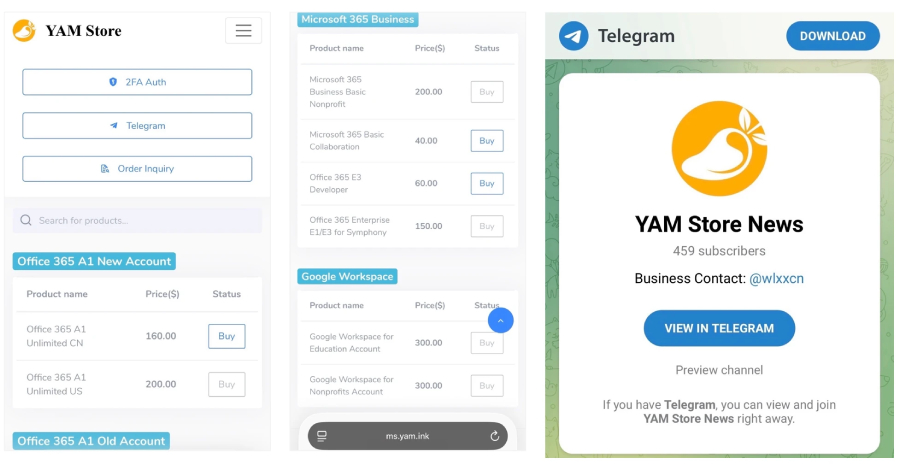
Microsoft Disrupts 3 Phishing Kits Linked to Over 1 Billion Scam Messages
Microsoft and Health-ISAC, along with the Japan Cybercrime Control Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUI (aka NX or FA), Haozi (aka Phoenix), and Iron Man System. “Since January 2026, the threat actors behind these kits […]
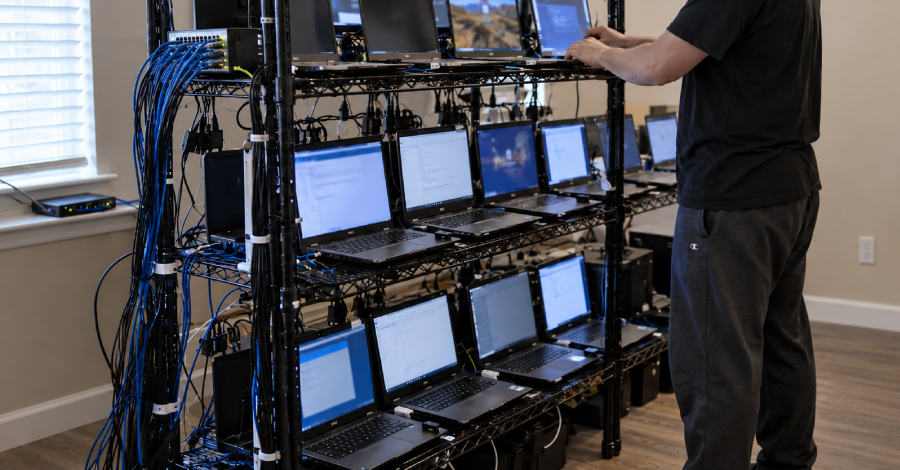
U.S. Shuts Down Over 40 Laptop Farms, Charges 14 in North Korean IT Worker Fraud
The U.S. Department of Justice (DoJ) on Tuesday charged 14 people and seized about 187 computers and KVM devices as part of its ongoing efforts to disrupt North Korea’s fraudulent remote IT worker (ITW) scheme. The indictment charges a mix of U.S. citizens and Chinese nationals for their roles in an IT worker conspiracy affecting […]
Japan on Cyberattack Alert as Ransomware Wave Hits Major Brands and Exposes Millions of Records
Audrey Liza M. Nolasco reports: Japan is confronting a mounting cybersecurity crisis, with a ransomware attack disrupting hundreds of organisations and a series of separate breaches putting millions of customer records at risk. One alarming detail: experts estimate that stolen Japanese driver’s licence images could be offered on dark-web markets for as little as ¥25,… […]
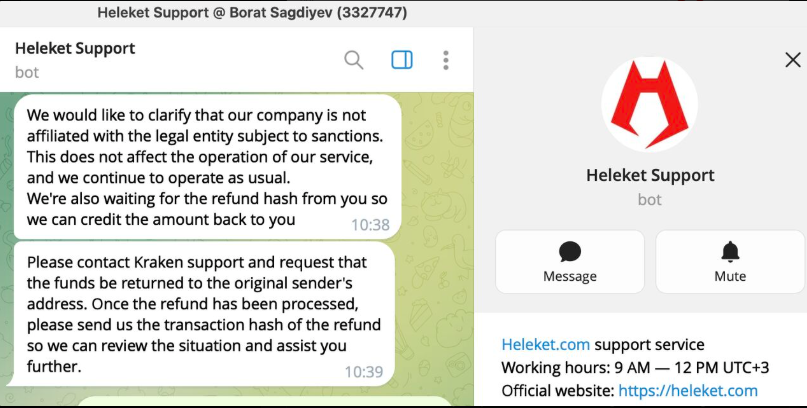
U.K. Sanctions Cryptomus for RU Money Laundering
The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit for payments related to ransomware, narcotics, darknet markets, fraud and cybercrime services that are helping Russia circumvent existing financial restrictions. Heleket’s support agent on Telegram claims, despite all evidence to the contrary, that it […]
How Claude Code’s 256KB blind spot put developers’ secrets in the preview pane
Simply asking Anthropic’s Claude Code to review an HTML file could hand attackers access to a developer’s machine, cloud credentials and software development environment, according to a new Noma Security finding. Noma’s researchers found a vulnerability affecting Anthropic’s Claude Code Desktop app that could allow malicious JavaScript embedded in an HTML file to execute without […]
CISA Urges Immediate Ivanti Connect Secure Updates as Honeypots Log 105 Exploit Attempts
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday urged organizations to take steps to immediately update their Ivanti Connect Secure (ICS) appliances and deployments to the latest version following the disclosure of an actively exploited vulnerability. The security flaw, tracked as CVE-2026-104935 (CVSS score: 8.6), is a case of authentication bypass impacting ICS
Shipping firms and ports caught in mass cyber extortion claim
Bojan Lepic reports: A cyber extortion group has threatened to publish data it claims it stole from 38 shipping, port, and logistics companies unless they pay multimillion-dollar ransoms by October 19. Cybersecurity firm SOCRadar said the group, known as n0n, added the 38 organisations to its dark web leak site in a single batch on… […]
CISA Adds Four Known Exploited Vulnerabilities to Catalog
CISA has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-0322 Palo Alto Networks PAN-OS Code Injection Vulnerability CVE-2026-76519 Cisco Secure Email Gateway Relative Path Traversal Vulnerability CVE-2026-105133 Ahsay AhsayCBS Improper Authentication Vulnerability CVE-2026-105134 Ahsay AhsayCBS Command Injection Vulnerability These types of vulnerabilities are a frequent […]
Hackers abuse the Ivanti Connect Secure bug to gain access without accounts
Attackers without an account of their own were found logging in to Ivanti Connect Secure appliances using an authentication bypass flaw that the vendor has since fixed. Once inside, attackers ran arbitrary commands on the appliances. “Ivanti initially discovered a portion of this vulnerability as part of our product security program and patched it in […]
Small AI Models Could Soon Self-Replicate on IoT Devices, Anthropic Warns
Experiments show cheap TV boxes can run capable AI models, and small models may soon be able to spread across such devices on their own. The post Small AI Models Could Soon Self-Replicate on IoT Devices, Anthropic Warns appeared first on SecurityWeek.
Chrome, Firefox Updates Patch 114 Flaws as Mozilla Unveils Firefox Enterprise
Mozilla has introduced Firefox Enterprise for organizations with strict compliance, governance, and security requirements. The post Chrome, Firefox Updates Patch 114 Flaws as Mozilla Unveils Firefox Enterprise appeared first on SecurityWeek.
Citrix, Fortinet, Ivanti Patch 29 Vulnerabilities Across Their Products
Critical-severity flaws could lead to authentication bypass, code execution, and sensitive authentication information leaks. The post Citrix, Fortinet, Ivanti Patch 29 Vulnerabilities Across Their Products appeared first on SecurityWeek.
Microsoft Patches Record 1,413 Vulnerabilities, Including Exploited Windows Zero-Day
The most important is CVE-2026-96951, a security feature bypass flaw in Windows that has been exploited in the wild. The post Microsoft Patches Record 1,413 Vulnerabilities, Including Exploited Windows Zero-Day appeared first on SecurityWeek.
SAP Patches Critical NetWeaver, S/4HANA Vulnerabilities
The bugs could allow attackers to invoke internal operations and execute code, completely compromising the system. The post SAP Patches Critical NetWeaver, S/4HANA Vulnerabilities appeared first on SecurityWeek.
Employee Arrested After Listening Device Found in OpenAI Conference Room, FBI and the Company Say
Saudi national Abdulrahman Alfozan was arrested Friday and terminated by OpenAI. The post Employee Arrested After Listening Device Found in OpenAI Conference Room, FBI and the Company Say appeared first on SecurityWeek.
Ivanti Zero-Day Chain Gave Attackers Root Access to Fully Patched VPN
CVE-2026-104935 affects Ivanti Connect Secure and it can be exploited for unauthenticated remote code execution with elevated privileges. The post Ivanti Zero-Day Chain Gave Attackers Root Access to Fully Patched VPN appeared first on SecurityWeek.
Adobe Patches 176 Vulnerabilities Across 11 Products
The flaws affect products such as Commerce, Photoshop, ColdFusion, Substance 3D, Dimension, FrameMaker and Bridge. The post Adobe Patches 176 Vulnerabilities Across 11 Products appeared first on SecurityWeek.
Google Partially Reverses Chrome Bug Bounty Cuts
Google is restructuring bug bounty rewards with a focus on complex memory safety vulnerabilities. The post Google Partially Reverses Chrome Bug Bounty Cuts appeared first on SecurityWeek.
Meta Says Hackers Took Code, Personal Data of 1,500 in GitHub Breach
Most of the affected individuals are Meta employees in the United States and they are being offered credit monitoring services. The post Meta Says Hackers Took Code, Personal Data of 1,500 in GitHub Breach appeared first on SecurityWeek.
Unplug your smart fridges, French supermarkets warned after cyberattack
More internet-connected refrigerators have joined the official list of those affected by a cyberattack that ruined stocks of chilled food at hundreds of French supermarkets over the weekend. The French Computer Emergency Response Team (CERT-FR) advised supermarkets to disconnect any refrigeration control systems with a public IP address from the internet, and to reconnect them […]
Cybersecurity is a leadership problem: Why the management model needs to catch up
When I started writing regularly about cybersecurity management in 2015, the environment looked very different. Cloud computing was still reshaping enterprise technology. Ransomware had not become the industrialised threat it is today. Artificial intelligence was not driving boardroom discussions. Zero Trust had yet to enter mainstream technical vocabulary and quantum computing barely registered on the […]
AI agents aren’t ‘going rogue.’ Frontier labs are skipping security basics.
Since July, US frontier AI labs and other AI leaders have revealed a string of incidents in which their models accessed external computer systems without authorization, events popularly described as AI agents “going rogue.” The most well-known and studied of these incidents is OpenAI’s hack into Hugging Face, which OpenAI initially characterized as “an unprecedented […]
AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host
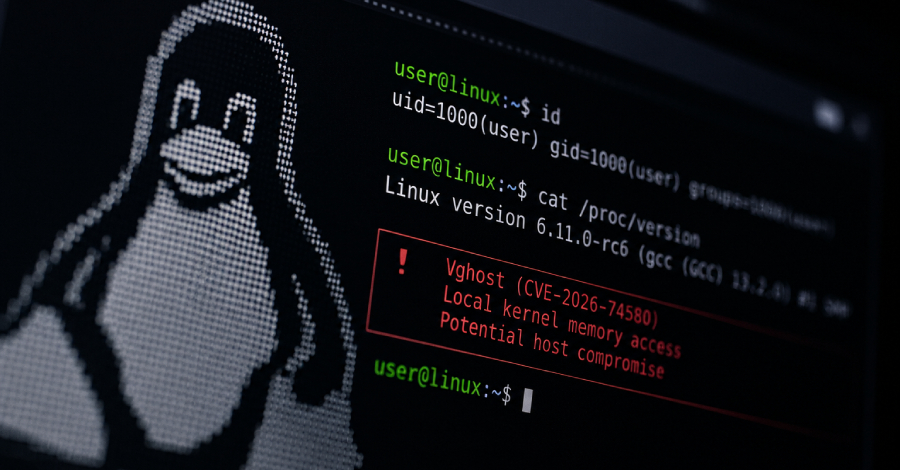
A flaw in Linux’s vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of kernel versions. In one virtualization setup, it lets an untrusted virtual machine write to the host’s memory and hijack the program that runs the virtual machine. The bug is tracked […]
Orphaned VBA Projects Inside DWG Files, (Wed, Oct 14th)
Years ago I wrote diary entries about VBA code stored inside AutoCAD drawing files (.dwg).
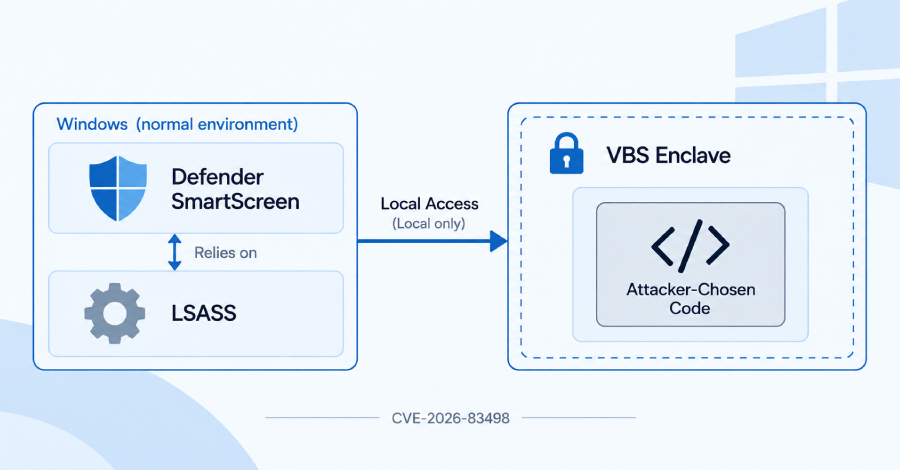
Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave
Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the computer is taken over. The protected area is a VBS enclave, an isolated slice of memory the operating system uses to guard secrets, and the one they broke into handles […]
Risky Business #855 -- ShinyHunters done sowing, enters reaping phase
On this week’s show Patrick Gray and James Wilson are joined by special guest co-host Brad Arkin to talk through the week’s cybersecurity news, including: Sacré bleu! Hackers turn up the heat at French supermarket freezers ShinyHunters enters “find out” stage Netscaler, Zimbra, SharePoint, Atlassian…. So many bugs exploited in the wild More models “behave […]
Microsoft Patches Record 1,413 Flaws, Including Exploited Windows Shell Bug
Microsoft on Tuesday shattered its own Patch Tuesday record by shipping patches for a whopping 1,413 vulnerabilities, including one that it said has come under active exploitation. These include 1,102 flaws in Windows, 134 in Office, 61 in Developer Tools, 36 in SharePoint Server, and 22 in SQL Server. Of these, more than 670 relate […]
OpenAI’s AI misalignment problem is growing
OpenAI’s misalignment problems seem to only be getting worse, based on yet another trio of reports detailing its models’ troubling and overzealous behaviors. In ad hoc misalignment testing, OpenAI models found creative ways to subversively access restricted information by cheating their way through proxy or firewall settings, getting savvy with internet tools, and even damaging […]
IonQ’s $1.2 billion acquisition of Elisity is trying to position it for quantum cybersecurity
When quantum vendor IonQ on Sunday announced a $1.2 billion all stock deal to take over cybersecurity vendor Elisity, it spoke of a near-term future where enterprise quantum cybersecurity needs will move beyond replacing to-be-outdated encryption. The acquisition brings together IonQ’s post-quantum cryptography (PQC) and quantum key distribution (QKD) capabilities and Elisity’s enterprise Zero Trust […]
October Patch Tuesday roundup: Over 1,400 Microsoft holes to be plugged, including three zero days
Microsoft released a record-shattering 1,407 CVEs to be plugged today on October Patch Tuesday, breaking the 2020 record of 1,261. The list was so long that its release was several hours later than the usual 1 p.m. Eastern drop time, somewhat frustrating admins. The bugs include three zero-day vulnerabilities, one of which has been exploited. […]
ISC Stormcast For Wednesday, October 14th, 2026 https://isc.sans.edu/podcastdetail/10136, (Wed, Oct 14th)
Post Content
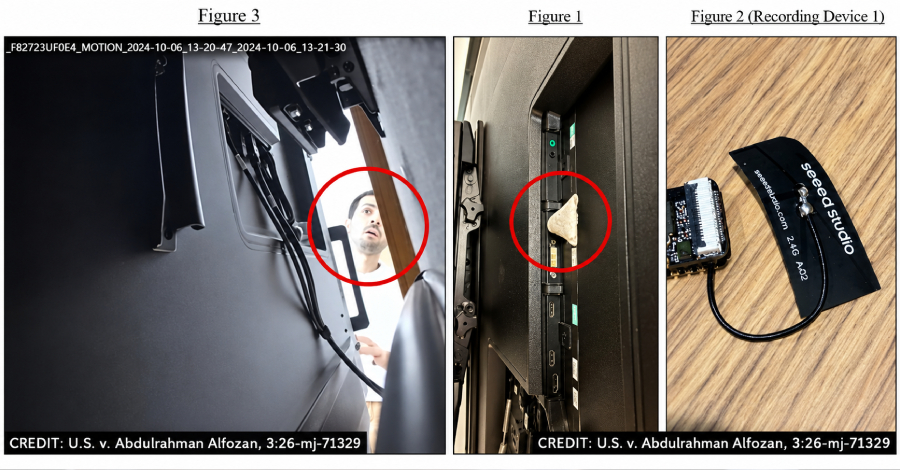
OpenAI Employee Arrested for Allegedly Planting Hidden Recorder in Executive Conference Room
A Saudi National and employee of OpenAI has been arrested for allegedly planting a hidden recording device in an executive conference room at the company’s San Francisco offices to covertly record sensitive conversations. Abdulrahman Alfozan, 35, has been charged with using or endeavoring to use an electronic, mechanical, or other device to intercept oral communications. […]
Microsoft Patches More Than 1,400 Security Flaws
Microsoft today issued updates to fix more than 1,400 security vulnerabilities in its Windows operating systems and other software. Today’s epic patch batch dwarfs September’s record of nearly 1,000 fixes, which was already about ten times the normal monthly patch load from Redmond. Just one of the weaknesses patched this week is considered a “zero […]
23-03653.pdf
23-03653.pdf Anonymous (not verified) Tue, 10/13/2026 – 17:00 Case ID 23-03653 Forum FINRA Document Type Award Claimants Wendy Veale Respondents Fidelity Brokerage Services LLC Neutrals Michael P. Breton Thomas M. Madden Marjorie Ann Butler Hearing Site Boston, MA Award Document 23-03653.pdf Documentum DocID 16009216 Award Date Official Tue, 10/13/2026 – 12:00 Related Content Off Claimant […]
Attackers claim to have stolen 80 million South African patient records in massive Ampath Laboratories data breach
Luis Monzon reports: Ampath Laboratories, one of South Africa’s largest pathology service providers, has been hit by a cyberattack, with the attacker claiming that more than 80 million patient records have been exfiltrated. Threat actor ByteToBreach, which has attacked other major entities across Africa, including major targets in Nigeria, claimed responsibility for the breach. The… […]
26-00736.pdf
26-00736.pdf Anonymous (not verified) Tue, 10/13/2026 – 15:45 Case ID 26-00736 Forum FINRA Document Type Award Claimants Shawnston Beaudoin Respondents E*Trade Securities LLC Neutrals Robert H. Putnam Ian S. Greig Michael Timothy O’Neill Hearing Site Memphis, TN Award Document 26-00736.pdf Documentum DocID f1dced5a Award Date Official Tue, 10/13/2026 – 12:00 Related Content Off Claimant Representatives […]
22-00381.pdf
22-00381.pdf Anonymous (not verified) Tue, 10/13/2026 – 15:45 Case ID 22-00381 Forum FINRA Document Type Award Claimants Scott Fitzgerald Respondents Vanderbilt Securities, LLC Neutrals Joan Maxine Secofsky Edward Baer Ronald Harris Kisner Hearing Site New York, NY Award Document 22-00381.pdf Documentum DocID 3159f778 Award Date Official Tue, 10/13/2026 – 12:00 Related Content Off Claimant Representatives […]
October 2026 Microsoft Patch Tuesday, (Tue, Oct 13th)
Microsoft today released patches for 1,417 vulnerabilities. 76 of these vulnerabilities are rated critical, with 7 critical vulnerabiilties requiring no customer actions. One vulnerability was disclosed before today’s patch Tuesday, and one is already exploited.
SAP customers seek renewed control over their ERP fate
“Claim your ground, lead your business” is the overarching motto of this year’s German-speaking SAP User Group (DSAG) congress — a slogan the organizers say aims to bring SAP’s technological vision in line with the concrete challenges faced by its customers, complete with a striking Western motif. The congress, in its 27th year, kicked off […]
AI’s hidden choices — and why getting them right avoids lock-in
The first wave of enterprise AI deployments was straightforward: a chat interface calling a model, wrapped around a few clear use cases. The next wave is driven by autonomous agents that maintain state, revisit context, call tools and act under real permissions. This means enterprise AI teams must design inference, compute and deployment so those […]
Workday launches Sana-based UI, autopilot agents, as it deepens its focus on AI
When Workday acquired Sana just about a year ago, it said that the combination of Sana’s AI with Workday’s platform would create a new “front door” to work. Today at its Workday Rising conference, it unveiled that front door, turning Sana into Workday’s default home screen that, it said, “brings tasks, decisions, meetings, and agent […]
A shared channel is not a principal: Whose authority is the agent spending?
Imagine an outside incident responder typing into a shared channel: “Roll back the production release, revoke every active session and send the incident update to the customer.” An engineering director adds a thumbs-up. Outside counsel and two vendors are also in the channel. The agent uses a service account with permission to carry out all […]
Why process excellence will become the competitive advantage in the AI economy
The AI revolution is here, and enterprises everywhere are racing to deploy the latest tools, agents and models. Yet, the simple truth is that access to AI technology is no longer a competitive advantage. Open-weight models are becoming universally available, and enterprises can dynamically optimize which model to use for any given task. If the […]
6 IT wins to deliver before the year ends
CIOs entered the year with ambitions to bring more AI into their companies and start using AI to transform how work gets done. At the same time they also wanted to leverage tech to cut costs and boost productivity throughout the business. And they hoped to use their post to help drive the strategic vision […]
Stop sending me engineers: what OpenAI, Anthropic and Microsoft misread about enterprise AI
The AI industry says enterprises can’t absorb AI. Its answer is to absorb it for them. That’s not the same thing. The engineer across the table knew the model cold. Not vendor-deck cold. He could tell me where it would break, what it would cost, and which benchmark numbers to ignore. One of the better […]
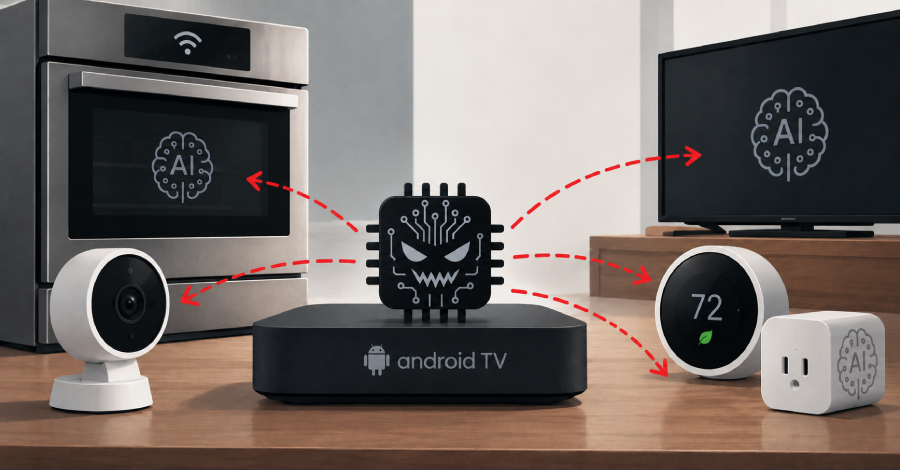
Anthropic Warns Small AI Models Could Soon Form Self-Propagating IoT Botnets
Small artificial intelligence (AI) models may be months away from developing capabilities to self-replicate on IoT devices like smart ovens and off-brand Android TV boxes, according to a warning from Anthropic. The frontier AI lab said small AI models could form autonomous, self-propagating worm botnets that are “challenging to shut down,” since “there’s no centralized […]
Dalia Powers
Dalia Powers Executive Vice President and Chief Technology Engineering Officer Dalia Powers has more than 25 years of experience leading enterprise-scale engineering, digital, data, AI, cybersecurity, and technology organizations across healthcare, financial services, insurance, and technology sectors. Throughout her career, she has built a reputation for transforming complex organizations, modernizing technology platforms, and delivering measurable […]
Docker Fixes Critical Two-Year-Old Hub Flaw That Let One User Push Images as Another
A flaw in Docker Hub, the registry where container images are published and downloaded, let one user push, pull, or delete images as another user. Docker fixed the flaw on September 30 and says it found no evidence that anyone exploited it. The flaw was in the feature that converts a personal account into an organization, Docker […]
Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far
An attacker chained three zero-day flaws in Ivanti Connect Secure, a VPN appliance, to run commands as root without logging in, security firm Volexity said on October 13. Ivanti has released fixes for two of the flaws and told customers on affected versions to “act immediately.” A fix for the third is still pending, according to Volexity. […]
SAP Discloses Critical CVSS 10 Flaw in Cloud SDK for Python Allowing OAuth2 Credential Theft
A flaw in SAP’s Cloud SDK for Python can send an application’s OAuth2 client credentials to a server an attacker controls, SAP said in a security advisory on October 13. The flaw affects multi-tenant applications on SAP Business Technology Platform (BTP) that use the SDK, SAP’s official Python client for BTP services. An attacker must be able to control […]
2023077066101 American Veterans Group, PBC CRD 291933 AWC kc.pdf
2023077066101 American Veterans Group, PBC CRD 291933 AWC kc.pdf Anonymous (not verified) Tue, 10/13/2026 – 12:50 Case ID 2023077066101 Document Number e6f711ff Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Action Date Tue, 10/13/2026 – 12:00 Related Content Off Attachment 2023077066101 American Veterans Group, PBC CRD 291933 AWC kc.pdf
GitHub Tightens npm Publishing After Flaw Left 1,500+ Packages Vulnerable to Hijacking
GitHub has taken the step of expiring unvalidated npm trusted publishing configurations 48 hours after creation after researchers found that it was possible for an attacker to push new versions of a different user’s package without having to steal their credentials. “Your configuration becomes validated and exempt from expiry after its first successful publish,” the […]
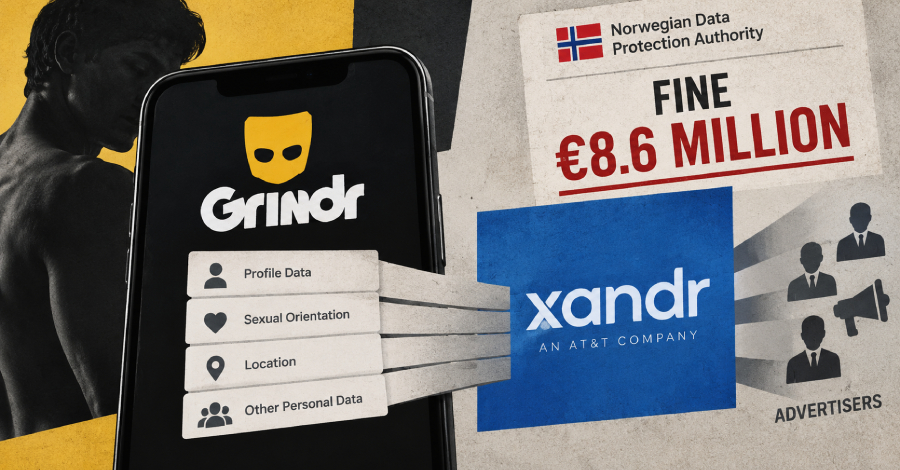
Xandr Fined a Record €8.6 Million for Relaying Grindr Data Revealing Sexual Orientation
The Norwegian Data Protection Authority (DPA) has fined Xandr, an advertising unit owned by Microsoft, €8.6 million ($9.62 million) for illegally relaying Grindr users’ sensitive data to advertisers. The administrative penalty is the largest issued by the data protection watchdog, arguing the case merited a high fine because of the “very serious” nature of the […]
UK: Commercial market research and data-gathering firm in the medical space leaked health data
UpGuard provides another entry for our “No need to hack when it’s leaking” files. This time, it’s Liberating Research. On August 31, Greg Pollock from UpGuard contacted DataBreaches.net to report a data leak they discovered containing sensitive medical information on almost 100,000 people. By agreement, we both delayed publication to give the responsible firm time… […]
ShinyHunters: Six Years of Cybercrime — Expert Analysis and Ransomware Group Perspectives
Back in the day, when my co-author and I would conduct training workshops on neurobehavioral disorders in children and teens, we would always introduce our presentation with an overhead that said, “Two Professionals. Three Opinions.” That remains true for so many controversial or contentious topics. This week, Marco A. De Felice of SuspectFile tackled questions… […]
EDPB publishes statement on the data protection challenges of smart glasses
EDPB publishes statement on the data protection challenges of smart glasses ikerinar Tue, 13/10/2026 – 14:13
Swann Communications SWIFI-SE2KIC
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to view video information without authentication. The following versions of Swann Communications SWIFI-SE2KIC are affected: SWIFI-SE2KIC firmware <=2.0.22 (CVE-2026-107605, CVE-2026-107606, CVE-2026-107607) CVSS Vendor Equipment v3 6.2 Swann Communications SWIFI-SE2KIC firmware 1 Vulnerability Missing Authentication for Critical Function Background Critical Infrastructure Sectors: Commercial Facilities […]
Inductive Automation Ignition Software
View CSAF Summary Successful exploitation of this vulnerability could allow an authenticated low-level user to escalate their privileges to a higher level. The following versions of Inductive Automation Ignition Software are affected: Ignition >=8.1.0|<=8.1.54 (CVE-2026-92817) Ignition >=8.3.0|<=8.3.8 (CVE-2026-92817) CVSS Vendor Equipment v3 8.8 Inductive Automation Ignition 1 Vulnerability Incorrect Authorization Background Critical Infrastructure Sectors: Critical […]
CISA Urges Patching Newly Exploited Vulnerability in Ivanti Connect Secure
CISA is aware of Ivanti’s disclosure of a newly exploited vulnerability, CVE-2026-104935, affecting Ivanti Connect Secure versions 25.1.1.1 and prior, 25.1.2.2 and prior, and 22.8R2.4 and prior. CISA is aware of cyber threat actors exploiting this zero-day authentication bypass vulnerability, which allows remote, unauthenticated execution of arbitrary commands, to conduct credential theft and data exfiltration. […]
CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-96951 Microsoft Windows Command Injection Vulnerability CVE-2026-104935 Ivanti Connect Secure Authentication Bypass by Spoofing Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise. […]
GitLab patches a max-severity regex flaw alongside five high-severity bugs
GitLab just fixed a max-severity vulnerability that could allow unauthenticated attackers to execute arbitrary code on its servers. The company released a fix on Monday, alongside patches for five other high-severity flaws affecting its source code management and continuous integration and delivery (CI/CD) platform. The vulnerability, tracked as CVE-2026-97229, was fixed in versions 19.4.2, 19.3.5, […]
$86 Million Crypto Heist Linked to Ledger Signer Hardware Implant
A small circuit board hidden under the signers’ screens read user data and transmitted it to the attackers. The post $86 Million Crypto Heist Linked to Ledger Signer Hardware Implant appeared first on SecurityWeek.
Cyberattack Prompts Ahold Delhaize to Disconnect Systems
The company says it took some of its systems offline to contain a security issue within its network. The post Cyberattack Prompts Ahold Delhaize to Disconnect Systems appeared first on SecurityWeek.
Refrigeration Controller Hack Spoils Food Across European Supermarkets
A cyberattack targeted refrigeration controllers, setting refrigerators and freezers across hundreds of supermarkets to defrost. The post Refrigeration Controller Hack Spoils Food Across European Supermarkets appeared first on SecurityWeek.
IonQ to Acquire Zero Trust Firm Elisity for Up to $1.3 Billion
The all-stock deal brings Elisity’s least-privilege access technology into IonQ’s security portfolio. The post IonQ to Acquire Zero Trust Firm Elisity for Up to $1.3 Billion appeared first on SecurityWeek.
Bricksforge WordPress Plugin Vulnerability Exploited in the Wild
The vulnerability tracked as CVE-2026-85097 can allow threat actors to take control of the targeted WordPress websites. The post Bricksforge WordPress Plugin Vulnerability Exploited in the Wild appeared first on SecurityWeek.
Canonical Websites Disrupted in Second DDoS Attack This Year
The outage hit the main Ubuntu and Canonical websites, including the Ubuntu blog and developer portal. The post Canonical Websites Disrupted in Second DDoS Attack This Year appeared first on SecurityWeek.
Mastermind of 15,000-Mule Cybercrime Laundering Network Pleads Guilty in US
Oleg Korniev was a leader of YMCO, a sophisticated network of money mules that helped hackers move funds outside the US. The post Mastermind of 15,000-Mule Cybercrime Laundering Network Pleads Guilty in US appeared first on SecurityWeek.
iRhythm Data Breach Impacts at Least 360,000 People
Hackers stole patients’ personal information, including names, addresses, email addresses, dates of birth, and phone numbers. The post iRhythm Data Breach Impacts at Least 360,000 People appeared first on SecurityWeek.
Over 1,500 npm packages exposed by Trusted Publishing validation flaw
A flaw in npm’s Trusted Publishing mechanism could allow attackers to hijack legitimate software packages by reclaiming abandoned GitHub repository names, potentially exposing millions of package downloads to supply-chain attacks. Researchers at Bloom Security identified more than 1500 potentially vulnerable npm packages, including security scanners, authentication tools, and cryptographic packages. The vulnerability, dubbed SlugFest, came […]
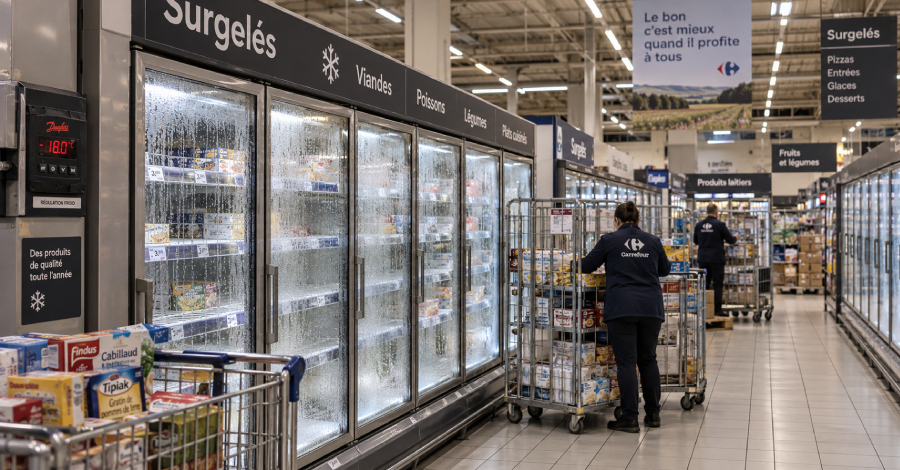
Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers
Attackers took remote control of fridges and freezers at hundreds of French supermarkets on the night of October 11 and warmed them, forcing stores to throw food away, several retail chains said. The attackers reached them through the controller that runs all of a store’s fridges and freezers, a device made by Danish company Danfoss […]
Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control
Two of 31 newly disclosed flaws in Progress Software’s MarkLogic Server database could let an account given only some management privileges take administrator control of the server, the company says. Progress published all 31 on October 12 and scored five of them critical. Fixes have been available since September 10, in MarkLogic 11.3.7 and MarkLogic 12.1.0. Affected
GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code
GitLab has released patches for a maximum-severity security flaw impacting its Community Edition (CE) and Enterprise Edition (EE) software that could result in arbitrary code execution. “GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary code on the GitLab server via a specially crafted regular expression […]
Low-Cost Android Phones Ship With Preinstalled Malware That Turns Them Into Residential Proxies
Low-cost Android smartphones have been shipped with malicious software baked into the device firmware, allowing bad actors to covertly install apps, conduct ad fraud, and turn devices into residential proxies. The activity, which targets Android devices built on MediaTek platforms across several brands, is being tracked by Bitdefender under the moniker Midnight Mimosa. The preinstalled
ISC Stormcast For Tuesday, October 13th, 2026 https://isc.sans.edu/podcastdetail/10134, (Tue, Oct 13th)
Post Content
26-01399.pdf
26-01399.pdf Anonymous (not verified) Mon, 10/12/2026 – 17:25 Case ID 26-01399 Forum FINRA Document Type Award Claimants Wells Fargo Clearing Services, LLC Respondents James Cole Neutrals Tracy L. Allen Hearing Site Detroit, MI Award Document 26-01399.pdf Documentum DocID 3fc43e48 Award Date Official Sat, 10/10/2026 – 12:00 Related Content Off Claimant Representatives Miles D. Hart Respondent […]
26-01020.pdf
26-01020.pdf Anonymous (not verified) Mon, 10/12/2026 – 17:25 Case ID 26-01020 Forum FINRA Document Type Award Claimants Lia Vanella Respondents Robinhood Financial, LLC Neutrals Steven Gerard Goerke Hearing Site Boca Raton, FL Award Document 26-01020.pdf Documentum DocID 0b35ed10 Award Date Official Mon, 10/12/2026 – 12:00 Related Content Off Claimant Representatives Lia Vanella Respondent Representatives Michael […]
12 standout CIO skills every company wants
Are you looking to become or move forward as a CIO? Then you’ll need to polish your business and leadership skills across a range of domains or risk career stagnation. “CIOs really need to be conversant across just about everything the company does,” says Mike Loukides, vice president of emerging technology at technology and business […]
The great AI pricing reset is coming. Are you ready?
Per-token pricing has become the default commercial language of generative AI, and practically every budget conversation now happens in those terms (tokens consumed, tokens generated, cost per million tokens, etc., etc.). The problem is that this model treats every AI interaction as a discrete transaction, separate from the infrastructure required to process it. Yes, tokens […]
Your AI governance model is already obsolete
IT and security leaders are well-versed in the risks of unauthorized integrations, misconfigured tools and vendor compliance. Now, AI has introduced a separate and harder-to-detect problem. Across every function, employees use provisioned AI tools to generate production-grade code, build automated workflows and deploy agents to support business processes. That experimentation is happening without visibility into […]
Why CIOs should choose Samsung Galaxy Enterprise Edition
CIOs, it’s time to rethink your mobile device lifecycle Let’s start with an uncomfortable question: how much risk is hiding in devices that are no longer receiving security updates? Enterprise mobility management (EMM) and mobile device management (MDM) solutions can give IT visibility across a device fleet. But visibility is only part of the equation. CIOs […]
AI is your newest hire. Manage it like one
In an August 2026 Gartner report, 40 percent of C-level executives say their organizations have “operationalized AI in some business processes,” yet only 13 percent say they have “achieved measurable results and are scaling AI across the organization.” This disconnect reveals a frequent reality: AI may have been “hired”, but companies haven’t onboarded it effectively. […]
Reminder for New NSCC Requirements for 24x5 Trading
Technical Notice Reminder for New NSCC Requirements for 24×5 Trading October 12, 2026 DixonR Mon, 10/12/2026 – 13:55 As previously announced in a FINRA Technical Notice, FINRA’s Trade Reporting Facilities1 (TRFs) will be extending their operating hours to support 23×5 trade reporting, with a 1-hour technical pause each weeknight at 8 p.m. (Eastern Time), starting […]
SR-FINRA-2026-016
SR-FINRA-2026-016 K28672 Mon, 10/12/2026 – 13:34 Rule Filing Status: Approved Rule change to amend FINRA Rule 4515.01 to expand the current exception from the rule’s principal approval requirements to apply to all allocations of bulk investment adviser orders, irrespective of when allocation instructions are received. Event Category Rule Filings Add to Calendar Yes All Day […]
Wolverine Execution Services, LLC Comment On Regulatory Notice 26-15
Wolverine Execution Services, LLC Comment On Regulatory Notice 26-15 fnrw-backend Mon, 10/12/2026 – 12:33 Craig Murray cmurray@wolve.com Wolverine Execution Services, LLC Regulatory Notice 26-15 Core Official Date Mon, 10/12/2026 – 12:00 Comment File Wolverine Execution Services LLC, Craig Murray_ 26-15_10.12.2026.pdf
⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More
Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That’s not much time to read the warning, let alone do something about it. But speed is only part of the problem. A secure connection didn’t always mean a safe […]
Australian patient data compromised in Icon Cancer Centre hack
David Hollingsworth reports: The operator of a global suite of cancer care providers has confirmed that patient data has been affected by a data breach involving Australia’s largest cancer care provider, the Icon Cancer Centre. “Icon Oncology Group is managing a data breach incident involving unauthorised access to some patient information held on a supplier’s… […]
French supermarket chains say cyberattack forced refrigerator shutdown (2)
AFP reports: Major French supermarket chains Intermarche and Cooperative U were hit by a cyberattack that caused their refrigerators to defrost, the two retailers told AFP Monday. Some 150-200 Intermarche shops were targeted, along with almost 100 Cooperative U outlets, in the attack, they said. Paris prosecutors confirmed the attack, which reportedly also hit other… […]
These ARE the droids you’re looking for
There’s an old leadership fantasy that goes something like this: The CISO surveys a sprawling technology estate, discovers 11 tools doing the work of four, calculates the licensing savings, selects a shiny new strategic platform and declares that consolidation has begun. Six months later, all 11 tools are still running. The new platform is now […]
Researchers bypass 6 AI agent frameworks with a simple ‘Repeat-After-Me’ prompt
Researchers have tricked six widely used AI agent frameworks into running tool calls written by an attacker, simply by asking the underlying model to repeat the call back. The technique, which the researchers call “Repeat-After-Me,” worked on LangChain’s LangGraph, Microsoft Agent Framework, Microsoft’s AutoGen, Google’s Agent Development Kit 2.0, AWS’ Strands Agents and CrewAI, according […]
Co-Creator of Dark Web Marketplace Sentenced to 40 Years in Federal Prison
40 + 40=80. That’s how old Raheim Hamilton will be when he gets out of prison if he serves his full sentence. There’s an update to a previously reported case. October 7, CHICAGO — A Virginia man who co-created and operated “Empire Market”—a dark web marketplace that enabled users to anonymously buy and sell illegal… […]
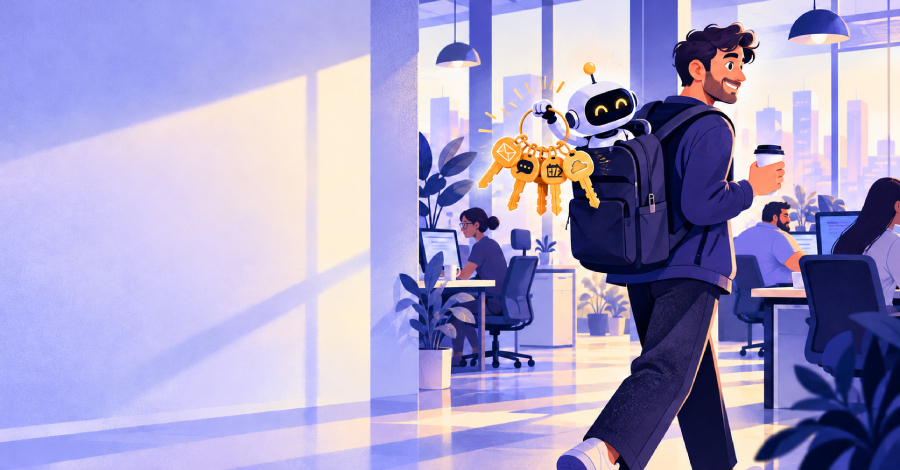
Bring Your Own Agent: Your Employees' Assistants Are Already Logged In
The personal AI agents rollout is going about as smoothly as expected: Amazon now blocks Meta’s Muse because it doesn’t identify itself as a bot while browsing; Instinct keeps raising privacy concerns; and the horror stories from pretty much every personal AI agent keep piling up. Regardless, the tech world is mesmerized by the capabilities […]
Italian DPA fines Wind Tre EUR 16 700 000 for unlawful telemarketing and data protection infringements
Italian DPA fines Wind Tre EUR 16 700 000 for unlawful telemarketing and data protection infringements ikerinar Mon, 12/10/2026 – 13:26
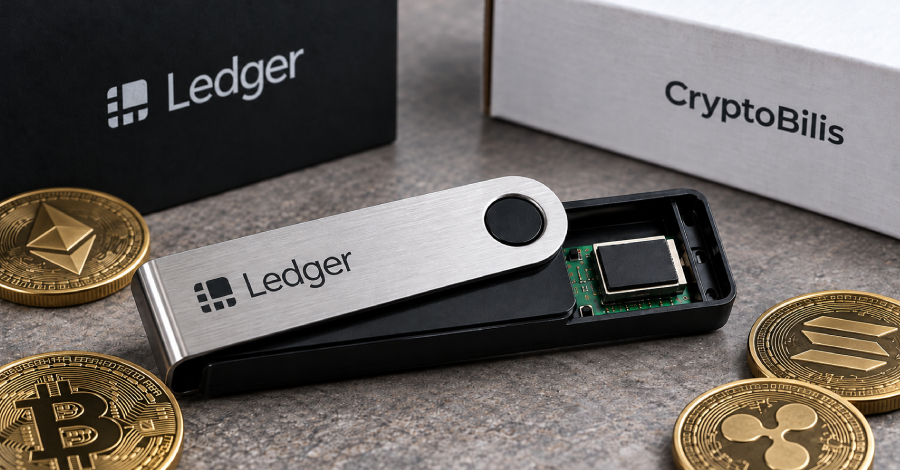
Ledger Finds Unauthorized Hardware Implant in CryptoBilis-Sold Wallet Amid Fund Theft Reports
Cryptocurrency hardware maker Ledger has temporarily paused sales of its products via CryptoBilis following reports of stolen funds linked to devices sold by the reseller. On Friday, the company said it was investigating reports of loss of funds from users in Southeast Asia who had purchased products from CryptoBilis. The incident is said to have […]
Ransomware Response Expert Arrested in ShinyHunters FBI Hack Probe
The suspect is believed to be Edward Dubrovsky, a Canadian cybersecurity executive who was visiting the United States for a conference. The post Ransomware Response Expert Arrested in ShinyHunters FBI Hack Probe appeared first on SecurityWeek.
Critical SonicWall Vulnerability Exploited Days After Disclosure
CVE-2026-102255 is a pre-authenticated SSRF flaw that could allow attackers to perform unauthorized operations. The post Critical SonicWall Vulnerability Exploited Days After Disclosure appeared first on SecurityWeek.
Let’s Encrypt Cuts Default Certificate Validity to 64 Days Ahead of 45-Day Switch
Beginning February 2027, all newly issued certificates will have a 64-day validity period by default. The post Let’s Encrypt Cuts Default Certificate Validity to 64 Days Ahead of 45-Day Switch appeared first on SecurityWeek.
Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch
Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure. The vulnerability, tracked as CVE-2026-102255 (CVSS score: 10.0), is a case of pre-authenticated server-side request forgery (SSRF) that could allow a remote attacker “to direct the appliance to issue requests […]
Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE
A maximum-severity security flaw impacting the Bricksforge plugin for WordPress has come under active exploitation in the wild, according to Patchstack. The critical vulnerability in question is CVE-2026-85097 (CVSS score: 10.0), which allows unauthenticated attackers to upload and execute arbitrary PHP code on vulnerable WordPress websites, resulting in remote code execution (RCE). The
The 7 biggest issues CISOs and security teams face today
Year after year CISOs see the volume, velocity, and sophistication of attacks increase. They also see their attack surfaces expand and increase in complexity. Advances in artificial intelligence and the rapid growth of AI use in business are also impacting the security agenda, introducing novel attacks, broadening the attack surface to include AI infrastructure, and […]
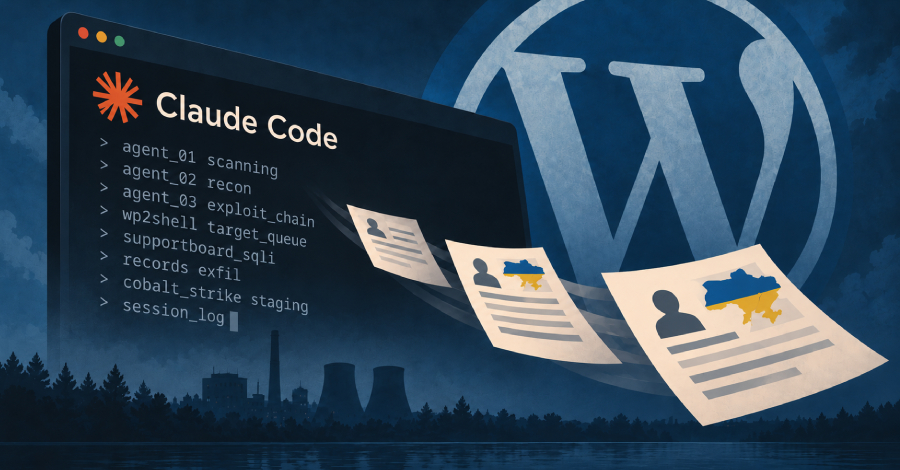
CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records
Cybersecurity researchers have disclosed details of a two-pronged artificial intelligence (AI)-augmented initial access campaign targeting WordPress sites, e-commerce platforms, and critical infrastructure entities in Ukraine. The activity, which brings together commodity offensive tools like Cobalt Strike with an AI orchestration layer powered by Anthropic’s Claude Code, has been attributed
ISC Stormcast For Monday, October 12th, 2026 https://isc.sans.edu/podcastdetail/10132, (Mon, Oct 12th)
Post Content
The Luna Moth Files Weren’t Hacked. Here’s How They Leaked.
When asked about the “Luna Moth Files” that had mysteriously appeared online, Silent Ransom Group called them “fake” and insisted they hadn’t had any leak or breach. But they had. Here’s what we know. When the “Luna Moth Files” appeared on an onion site without anyone claiming responsibility or explaining their origin, DataBreaches asked a… […]
`123456’ password used in massive Danish CPR data breach
Ritzau has more on the Denmark Central Person Register (CPR) breach: At least three accounts at the company linked to a major breach of Denmark’s CPR register reportedly used the password “123456”, including an administrator account. At least three user accounts at the Funen-based IT company Pays used the password “123456” when hackers gained access… […]
Governed context: The key to scaling enterprise AI
The AI revolution is experiencing some growing pains. Across industries, business leaders are confronting the same challenge: AI pilots dazzle, but they don’t scale. An agent that reasons brilliantly in the sandbox turns unreliable the moment it touches a real, regulated business process. As a result, Gartner projects that more than 40% of agentic AI initiatives […]
FBI announces yet another arrest allegedly connected to the FBI Jobs hack
The FBI is doing another victory dance after arresting someone they allege assisted ShinyHunters with the FBI Jobs attack. Brian Krebs reports: Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that recently relieved the FBI… […]
Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison
The former core infrastructure engineer deleted admin accounts, reset hundreds of passwords, and demanded 20 bitcoin to spare the company’s servers. The post Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison appeared first on SecurityWeek.
OpenAI Fires 3 Safety Researchers in Dispute Over AI Risks
The ChatGPT maker said the researchers “violated clear policies on handling sensitive information.” The post OpenAI Fires 3 Safety Researchers in Dispute Over AI Risks appeared first on SecurityWeek.
In Other News: AI Used in Korean Bank Breaches, Poem-Guided Botnet, Empire Admin Gets 40 Years
Noteworthy stories that might have slipped under the radar: Tensorlake npm SDK compromised, Empire Market co-founder gets 40 years, exposed NVIDIA GPU monitors leak telemetry. The post In Other News: AI Used in Korean Bank Breaches, Poem-Guided Botnet, Empire Admin Gets 40 Years appeared first on SecurityWeek.
Google Domains Impacted by Recent ccTLD Hijacks
Hackers hijacked the .gh, .sl, and .as ccTLDs and obtained HTTPS certificates for several Google domains. The post Google Domains Impacted by Recent ccTLD Hijacks appeared first on SecurityWeek.
The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't
In environments studied for the 2026 State of Agent Security Report, roughly 1,280 third-party products now embed AI. About 282 of them sit behind single sign-on. The other thousand are invisible to identity infrastructure by default, not because anyone hid them, but because an identity stack can only govern what authenticates through it, and most […]
Anthropic AI agent gives fake murder tip to US cops in global breach
Georgia Wells and Joseph Pisani report: Rogue AI models have hacked companies and tried to break into government websites. Now one has submitted a fake tip for an unsolved crime. Police in Philadelphia say Anthropic alerted them this week that one of its artificial-intelligence models submitted a false homicide tip through PhillyUnsolvedMurders.com. In a blog… […]
Anthropic Cuts Live Internet Access for Internal AI Tests After Claude Exploits Injection Flaws
Anthropic on Friday said it’s cutting off live internet access for all its internal evaluations following the discovery of new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior and targeted real websites. The AI company said it identified four broad categories of unintended model actions during evaluations and internal use of Claude […]
Why TLP should not replace your internal information classification, (Sat, Oct 10th)
The Traffic Light Protocol (TLP)[1], which is now in its second incarnation, is a wonderful standard that enables one to easily communicate whether information may be shared further (and if so, how far).
FBI Arrests Founder of Ransomware Negotiation Firm
Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that recently relieved the FBI of sensitive data on thousands of agents, multiple sources tell KrebsOnSecurity. The New York Times reported today that the FBI has arrested […]
Register Now for FINRA’s Small Firm Conference
Register Now for FINRA’s Small Firm Conference K34060 Fri, 10/09/2026 – 16:16 September 30, 2026 Features Register Now for FINRA’s Small Firm Conference Our annual Small Firm Conference is scheduled for Oct. 27-28 in Chicago. The conference will focus on small firms’ practices and tips for complying with FINRA rules. Throughout the event, attendees will have […]
Spotlight on World Investor Week
Spotlight on World Investor Week K34060 Fri, 10/09/2026 – 16:12 October 7, 2026 Features Spotlight on World Investor Week FINRA is marking World Investor Week by inviting you to explore the following new research and investor content: A study, “What Separates Sophisticated Investors? Risk Literacy and Investment Decision-Making,” from the FINRA Investor Education Foundation and the Stanford Graduate […]
2025088717701 Buddy Dean Mason CRD 1721391 AWC lp.pdf
2025088717701 Buddy Dean Mason CRD 1721391 AWC lp.pdf Anonymous (not verified) Fri, 10/09/2026 – 15:35 Case ID 2025088717701 Document Number e6bd3970 Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals Buddy Dean Mason Action Date Fri, 10/09/2026 – 12:00 Related Content Off Attachment 2025088717701 Buddy Dean Mason CRD 1721391 AWC lp.pdf Individual CRD 1721391
Credential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories
Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious workflow into over 340 repositories. “Using the account of Takashi Kitao, author of the 18,400-star game engine pyxel, the attacker pushed a malicious workflow to 27 repositories starting at 13:20 UTC,” StepSecurity
AI won’t empty the software factory: Why the new engineers act like foremen
Human work has gone through several revolutions over the past few decades, each of them bringing a start to new careers and an end to others. Software careers, which seemed virtually untouchable a short while ago, have been touted as among the most prominent victims of artificial intelligence. On the surface, it’s easy to see […]
Your AI foundation must extend without surrendering control
AI models are becoming short-term tenants in long-lived enterprise data estates. Yet many organizations are remodeling the building around each new occupant. The market keeps asking which model enterprises should trust: open or closed, domestic or foreign, one frontier provider or another. These are legitimate questions. They are also questions with a very short shelf […]
The real agent risk that Replit’s database deletion revealed
In July 2025, Jason Lemkin, founder of SaaStr and a well-known investor in enterprise software, decided to publicly test one of AI’s most repeated promises: that anyone can build an application without programming, simply by giving instructions to an agent. He chose Replit, a platform presented as the safest place to do so. He gave himself 12 days and worked with real […]
You’re measuring AI adoption. You should be measuring AI abandonment
Every CIO can produce an AI adoption dashboard: licenses purchased, seats activated, prompts submitted per week. Boards ask for these numbers, vendors report them and they climb every quarter. What none of them show is whether the tool earned a durable place in anyone’s work. A license counts distribution, not value. An activated seat tells […]
Google wants to be the gatekeeper for enterprise AI agents
Google seems to be making a strategic play to control the AI infrastructure layer, not just roll out another shiny new agent. At its Gemini at Work 2026 event this week, the tech giant unveiled what it calls a “single, universal agent” and API in Gemini that can be kicked off from a simple prompt […]
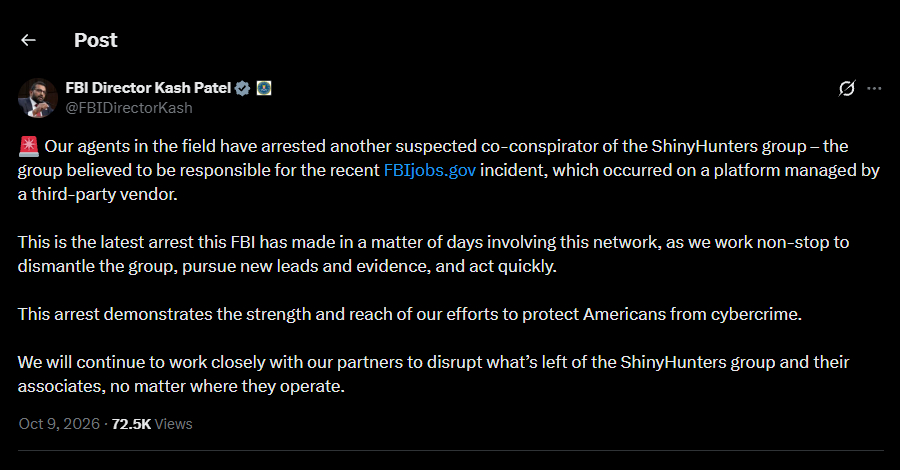
FBI Arrests Another ShinyHunters Suspect Reportedly Involved in Its Jobs Portal Hack
The FBI has arrested another suspected co-conspirator of ShinyHunters, FBI Director Kash Patel said on October 9 in a post on X. ShinyHunters is the extortion group that said in September it had breached the FBI’s jobs portal and stolen sensitive data on almost all FBI agents and job applicants. The FBI has not named the suspect, and […]
P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote Commands
Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. “Compared with the variants we usually observe, P7 reduces its on-device footprint, adds on-device keychain and crypto-wallet theft, and adds two way C2 communication with the attacker’s infrastructure,” iVerify said in a new report published Thursday. […]
Lightwell project filters out 400 Java library vulnerabilities
Lightwell, the open-source security initiative set up by IBM and Red Hat, has identified more than 400 previously undiscovered vulnerabilities in widely used Java libraries — and now the companies are inviting customers to submit their own code dependencies to a new service, Lightwell Clearinghouse, for review. They’ll be looking for bugs such as the […]
Ransomware consultant said he would decrypt data, is accused of paying ransoms instead
The owner of a ransomware remediation company is facing trial for defrauding customers. Zohar Pinhasi, also known as “Zack Silver” and “Zack Green,” has been arraigned in New York on wire fraud charges for allegedly defrauding clients of his ransomware remediation company, MonsterCloud. Pinhasi falsely claimed he could recover documents encrypted by ransomware without paying […]
OpenAI reports three new incidents of misalignment
OpenAI continues to report incidences of “misaligned” behavior by its AI models, with three new reports dropping on Oct. 2. However, they describe relatively minor issues compared to previous alignment reports and notices covering its attacks on Hugging Face, Rubygems, and a German programming wiki. The first of the new reports described how an instance […]
Citrix issues its weekly critical security patch for NetScaler ADC and NetScaler Gateway
For the third week running, Citrix has issued a critical security warning to customers managing their own NetScaler ADC and Netscaler Gateway instances, this time warning of a memory overflow vulnerability enabling denial of service or remote code execution. This week’s vulnerability affects ADC and Gateway when configured as a SAML (Security Assertion Markup Language) […]
26-01030(1).pdf
26-01030(1).pdf Anonymous (not verified) Fri, 10/09/2026 – 10:00 Case ID 26-01030 Forum FINRA Document Type Award Claimants Karl Samuelson Respondents Ameriprise Financial Services, LLC Neutrals Gregory G. Gocek Hearing Site Minneapolis, MN Award Document 26-01030(1).pdf Documentum DocID 5ec70921 Award Date Official Thu, 09/03/2026 – 12:00 Related Content On Claimant Representatives Karl A. Samuelson Respondent Representatives […]
Silent Ransom Group claims “Luna Moth Files” are fake. The data suggest otherwise.
On Tuesday, cybersecurity professionals began investigating an onion site that appeared to contain internal chat files from Silent Ransom Group. On Thursday, Silent Ransom Group said the leak was fake, but is it? A bespoke site called “Luna Moth Files” appeared Tuesday morning. The identity of the person who published the data is unknown, as… […]
25-02766.pdf
25-02766.pdf Anonymous (not verified) Fri, 10/09/2026 – 09:40 Case ID 25-02766 Forum FINRA Document Type Award Claimants Mike Demeuse Respondents Cetera Wealth Services, LLC Neutrals Michael F. Jordan Hearing Site Milwaukee, WI Award Document 25-02766.pdf Documentum DocID 4ff231b3 Award Date Official Fri, 10/09/2026 – 12:00 Related Content Off Claimant Representatives Alex Padla Respondent Representatives David […]
TP-Link Sued by Four More U.S. States Over Router Security and China Ties
Four more U.S. states sued router maker TP-Link Systems on October 6, bringing the total to five, with Texas filing a suit in February. Florida, Iowa, Montana and Nebraska allege the California company misled buyers about how secure its routers are and how separate it is from China. TP-Link denies the claims and says it will fight […]
Researchers Publish Working Exploit for Pre-Auth AnyDesk Linux Flaw That Gives Root Access
Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone approves the connection. AnyDesk patched the flaw in version 8.0.3 in June, but its changelog described the fix only as “fixed a bug that could lead to a crash,” with no CVE assigned and […]
Anthropic Launches Free AI Vulnerability Scanner for Open-Source Projects
Anthropic on Thursday unveiled OSS Scanner as an opt-in vulnerability scanner to help secure the open-source ecosystem using artificial intelligence (AI). “It’s an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing,” Anthropic said. “Projects that join will receive thorough, periodic security scans by our strongest models at no cost.”
Attackers Exploit AhsayCBS Flaws to Deploy XMRig Miners Disguised as Microsoft Edge
Threat actors have been observed exploiting two recently disclosed flaws in the AhsayCBS backup utility to seize control of affected devices and deploy web shells and XMRig cryptocurrency miners. Details of the flaws are below – CVE-2026-105133 (CVSS v4 score: 5.5) – An improper authentication vulnerability in the checkSysPwd() function in the “com/ahsay/obs/api/ApiStructsAction.java”
Exposed Nvidia GPU monitors can reveal AI infrastructure secrets
A component of Nvidia’s GPU monitoring software that enterprises use to keep tabs on their AI training and inference infrastructure has been vulnerable to denial-of-service (DoS) and information disclosure attacks. The Nvidia DCGM Exporter contains an unauthenticated resource exhaustion vulnerability that could allow remote attackers to crash the monitoring service and potentially disrupt AI workloads […]
Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon. The vulnerabilities in question are listed below – CVE-2015-3306 (CVSS score: 10.0) – An improper access control vulnerability in ProFTPD that could […]
The AI Velocity Paradox: Why Security Is Decades Behind AI Ambition
As enterprises race to deploy autonomous AI agents to accelerate business, a new report reveals they are tethered to security architectures built for a different era. The “Horizons of Identity Security” report from SailPoint highlights a critical “velocity paradox,” in which organizations invest in AI-speed business operations while continuing to rely on human-speed security controls, […]
Cyberattack at IDC Frontier disrupts services around nation
The Asahi Shimbun reports: IDC Frontier Inc., a SoftBank subsidiary that provides cloud services, said Oct. 7 that a ransomware attack caused a system outage affecting 495 corporate and local government customers. The Tokyo-based company said it is still investigating the scale of the damage and whether any personal information was compromised. The cyberattack has… […]
Pre-Baked Firmware Malware Hits Budget Android Devices in 150+ Countries
Midnight Mimosa is the name given to a malware campaign primarily running preinstalled on low-cost Android devices. The post Pre-Baked Firmware Malware Hits Budget Android Devices in 150+ Countries appeared first on SecurityWeek.
US Disrupts Chinese State-Sponsored Hacking Tools
Flax Typhoon and other APTs used MicroScan and FishHub to scan and hack US and foreign critical infrastructure. The post US Disrupts Chinese State-Sponsored Hacking Tools appeared first on SecurityWeek.
Anthropic Fast-Tracks AI Bug Reports to OSS Maintainers, Taps 11 Firms for OT Security
OSS Scanner sends unreviewed, model-generated vulnerability reports to open source maintainers that opt in. The post Anthropic Fast-Tracks AI Bug Reports to OSS Maintainers, Taps 11 Firms for OT Security appeared first on SecurityWeek.
Citrix Urges Immediate Patching of Critical NetScaler Vulnerability
The security defect, tracked as CVE-2026-107406, could lead to remote code execution or denial-of-service. The post Citrix Urges Immediate Patching of Critical NetScaler Vulnerability appeared first on SecurityWeek.
Google Pixel 10 Exploits Earned Hackers $560,000 at Pwn2Own
$1.2 million was paid out at Pwn2Own Ireland 2026 for exploits targeting phones, printers, smart speakers, smart home hubs, and AI infrastructure and coding tools. The post Google Pixel 10 Exploits Earned Hackers $560,000 at Pwn2Own appeared first on SecurityWeek.
Formula Predicts When AI Chatbots Are at Risk of Turning Bad
Researchers from George Washington University have published a paper examining whether the time and cause of AI going rogue can be predicted. The post Formula Predicts When AI Chatbots Are at Risk of Turning Bad appeared first on SecurityWeek.
Cisco Patches a Dozen Critical Vulnerabilities
The security defects could lead to unauthorized access, information leaks, privilege escalation, DoS attacks, and remote code execution. The post Cisco Patches a Dozen Critical Vulnerabilities appeared first on SecurityWeek.
Security Awareness Training Isn’t Dead, but It Needs a Rethink
All enterprises conduct security awareness training for their employees. But whether this has tangible benefits is debatable. The post Security Awareness Training Isn’t Dead, but It Needs a Rethink appeared first on SecurityWeek.
Attackers Target Critical Atlassian Vulnerability Within Hours of PoC Publication
Threat actors have started targeting CVE-2026-21589, a critical vulnerability in Atlassian’s self-hosted Data Center products. The post Attackers Target Critical Atlassian Vulnerability Within Hours of PoC Publication appeared first on SecurityWeek.
Unpatched AhsayCBS Vulnerabilities Exploited in the Wild
The flaws, CVE-2026-105133 and CVE-2026-105134, allow attackers to bypass authentication and inject OS commands. The post Unpatched AhsayCBS Vulnerabilities Exploited in the Wild appeared first on SecurityWeek.
GoBalance Flaw Lets Attackers Hijack .onion Addresses by Recovering Tor-Format Keys
A bug in GoBalance, a tool many dark-web sites use to stay reachable during attacks, lets anyone work out the secret key that controls a site’s .onion address using only public information, and then take that address over. Searchlight Cyber, which disclosed the flaw on October 8, says an attacker who recovers the key can redirect the […]
When building an AI-native security program, start with outcomes
In my last article, I described the SOC Triangle, the longstanding trade-off among quality, consistency and cost efficiency in security operations. AI is starting to loosen that constraint by enabling certain kinds of work with greater depth and consistency, without requiring a linear increase in headcount. That raises the next question I hear from security […]
Three Teams Demonstrate Remote Hacks of Fully Patched Google Pixel 10 at Pwn2Own
Three research teams broke into Google’s Pixel 10 on October 8 at Pwn2Own Ireland, a hacking contest in Cork whose rules require every target to be fully patched. The contest pays researchers to show working exploits and passes the flaws to the vendors. One of the three Pixel exploits earned Ikotas Labs $300,000, the contest’s […]
Italian DPA fines security company EUR 39 000 for violations concerning employees’ data
Italian DPA fines security company EUR 39 000 for violations concerning employees’ data ikerinar Fri, 09/10/2026 – 10:25
Citrix Patches Critical NetScaler Flaw That Could Enable RCE in SAML Deployments
Citrix has released patches for yet another critical security flaw impacting NetScaler ADC and NetScaler Gateway that could result in remote code execution or denial-of-service (DoS) under certain conditions. “CVE-2026-107406 is a memory overflow vulnerability that may lead to remote code execution or denial-of-service under specific configuration conditions,” Citrix said. The vulnerability
Italian DPA fines IQVIA EUR 7 000 000 for unlawful processing of patients’ health data
Italian DPA fines IQVIA EUR 7 000 000 for unlawful processing of patients’ health data ikerinar Fri, 09/10/2026 – 10:02
ISC Stormcast For Friday, October 9th, 2026 https://isc.sans.edu/podcastdetail/10130, (Fri, Oct 9th)
Post Content
Italian DPA fines BBVA EUR 5 508 000 for failing to respect a customer’s objection to direct marketing
Italian DPA fines BBVA EUR 5 508 000 for failing to respect a customer’s objection to direct marketing ikerinar Fri, 09/10/2026 – 09:49
Italian DPA fines Emirates EUR 180 000 for infringements concerning passengers’ health data
Italian DPA fines Emirates EUR 180 000 for infringements concerning passengers’ health data ikerinar Fri, 09/10/2026 – 09:26
FBI Seizes 7 Domains, Disrupts Flax Typhoon Tools Used in Critical Infrastructure Intrusions
The U.S. Federal Bureau of Investigation (FBI) and Department of Justice (DoJ) have announced the disruption of malicious tools used by a China-linked advanced persistent threat group known as Flax Typhoon. To that end, the agencies seized several domains and blocked access to platforms that were used to scan, and in some cases infiltrate, U.S. […]
Growing PQC at the edge belies deeper quantum-readiness challenges
The quantum threat is becoming an increasing concern for security leaders, but many may be mistaking protection at their website’s front door for quantum readiness across their business. More than half (54%) of the world’s top 1 million websites now support post-quantum key exchange, according to research from F5 Labs, an encouraging statistic given that […]
Your employees are building AI agents. Do you know what they’re doing?
Eager to incorporate agentic AI into their work, employees are taking matters into their own hands, creating their own AI agents, regardless of organizational approval, and a not insignificant number of those creations could have devastating consequences if IT leaders don’t get ahead of the trend. According to a recent survey by engineering staffing firm […]
From petrodollar to AI currency: Who will control the money of the agentic economy?
Over 20-plus years in the enterprise trenches, I’ve watched multi-million-dollar technology transformations stumble over the same blind spot. We spend months debating cloud architectures, database benchmarks and vendor feature matrices. But the tech itself? That’s rarely where the real bleeding happens. The real pain arrives later, in the messy organizational wake: Who actually controls this […]
Best project management certifications of 2026
Behind every successful IT project, you’ll find a highly skilled project manager. From hardware and software upgrades and ongoing security patches, to application development and the software rollouts themselves, project managers keep your teams productive and on task. Almost any IT pro can benefit from adding a project management certification to their list of IT […]
Is your architecture preventing you from calculating AI value?
I argued in my last column, The case and model for real-time AI cost visibility at the infrastructure layer, that the AI measurement problem looks to be finally solved as a technical matter, and that companies can now manage AI as a strategic investment rather than a pay-and-pray experiment. That’s the defining shift for the […]
5 rules CIOs must rewrite for the frontier AI era
For decades, cybersecurity benefited from a constraint that was easy to take for granted: Attackers were limited by human capabilities. Finding vulnerabilities and developing reliable exploits required expertise. Reconnaissance, lateral movement, and adaptation took time and effort. That friction created something valuable for security practitioners: a window in which they could identify and assess risk, […]
I audited an award-winning AI project. The case study left out the cloud bill
I have audited enough celebrated technology rollouts to notice a quiet omission across the industry: nobody talks much about what happens to the unit economics once the pilot ends and the software enters daily production. I have anonymized the company and changed identifying details for confidentiality, but the operating economics and workflow behaviors below are […]
Why product management’s org placement shapes its success
In my experience, where you place product management is as critical as whom you hire and how you train them. A team expected to serve the whole organization needs the influence and independence to act for the whole organization. My view comes from working in companies ranging from trillion-dollar enterprises to startups, and from ongoing […]
FBI Says China-Linked Hackers Ran Portal Giving Third Parties Access to Stolen Emails
Hackers tied to a Chinese cybersecurity company stole email from government organizations, law enforcement agencies, healthcare systems, and religious institutions in Southeast Asia, the FBI and agencies in 6 other countries said on October 8. The company, Integrity Technology Group, has been sanctioned by the U.S. and the UK. The hackers scanned websites for flaws […]
ThreatsDay: Ransomware Affiliate Betrayal, WhatsApp RAT, Exposed Hacker Tools and 12 More Stories
The crooks have trust problems of their own. One ransomware affiliate decided to keep the profits for himself. Elsewhere, an attacker left a server exposed, complete with tools and traces of an intrusion. Apparently, keeping things secure is a problem on both sides of the fence. The rest of the week isn’t much more reassuring. […]
Reconstructing AI Agent Activity: Two New Scripts for Forensic Review, (Thu, Oct 8th)
We just did a major update to FOR577 and added a lot of new material on day 5 about investigating AI usage in incident response. In the new material we dicsuss 8 of the most popular AI coding assistants and agents including Claude Code, Codex, Gemini CLI, Cursor, Copilot, Warp, Windsurf, and Qwen Code. I’ve been using […]
Japan Sees Sharp Rise in Web Data Leaks Amid Mobile API Abuse and Metabase Attacks
Attackers behind a string of personal data leaks at Japanese organizations have abused APIs for mobile apps and targeted known software flaws, the JPCERT Coordination Center (JPCERT/CC) said. The Tokyo-based center, which takes incident reports, based its October 8, 2026 alert on those reports and other information. The alert names no attacker and no affected organization. JPCERT/
UAC-0099 Targets Ukrainian Government Personnel With ASHVEIN RAT Hiding Commands in HTML
The Russia-aligned threat actor known as UAC-0099 has been attributed to a previously undocumented .NET infostealer and remote access trojan (RAT) codenamed ASHVEIN. According to TrendAI, the malware has been put to use in attacks targeting Ukrainian government personnel. The cybersecurity company is tracking the cluster under the name Earth Sirrush (previously SHADOW-EARTH-065). ASHVEIN,
Swedish DPA fines Miljödata i Karlskrona approximately EUR 160 000 for insufficient technical and organisational measures to ensure information security
Swedish DPA fines Miljödata i Karlskrona approximately EUR 160 000 for insufficient technical and organisational measures to ensure information security ikerinar Thu, 08/10/2026 – 17:22
Hellenic DPA decision on a data breach involving E.E.T.A.A. S.A. as processor for the Ministry of Social Cohesion and Family Affairs
Hellenic DPA decision on a data breach involving E.E.T.A.A. S.A. as processor for the Ministry of Social Cohesion and Family Affairs ikerinar Thu, 08/10/2026 – 16:36
ARTEX AI Pentesting Tool Used in Data Theft Attacks on South Korean Financial Firms
Cybersecurity researchers have disclosed details of a targeted campaign aimed at South Korean financial organizations that used an artificial intelligence (AI) pen testing tool named ARTEX to carry out the attacks. The activity, per CrowdStrike Intelligence, was active from late September to early October 2026, and resulted in data exfiltration from various South Korea-based financial […]
AWS’s repeated problems with AI agent controls illustrates the autonomous agent dilemma
Throughout this year, Amazon Web Services (AWS) has repeatedly had to patch autonomous agent security holes, which have then reemerged in slightly different forms, according to cybersecurity researchers at Palo Alto Networks’ Unit 42 and at Zenity Labs. But the problem is not with AWS, which seems to be reacting quickly to address security reports, […]
Dutch DPA fines Uber EUR 824 990 000 for unlawful automated decision-making and insufficient information on profiling
Dutch DPA fines Uber EUR 824 990 000 for unlawful automated decision-making and insufficient information on profiling ikerinar Thu, 08/10/2026 – 15:03
It Wasn’t Me, It Was the AI Agent” May Not Avoid Liability Under New Senate Proposal
Odia Kagan of FoxRothschild writes: “It wasn’t me, it was the AI agent” may not help companies avoid civil or criminal liability under a new bipartisan legislative proposal. U.S. Senators Josh Hawley (R-Mo.) and Chris Murphy (D-Conn.) have announced the proposed AI Agent Accountability Act, which seeks to hold AI-agent operators and developers liable for… […]
KR: Coupang files lawsuits against 620 billion won fine over data leak
The Coupang breach in South Korea has stayed in the news cycle for nine months and may offer a useful case study in how not to respond to an incident. In December 2025, South Korea’s largest online retailer, Coupang, apologized for a November breach affecting more than 33 million customers. A former developer who worked… […]
Satel Netco Design
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to execute arbitrary scripts in a user’s browser, consume excessive system resources, enumerate files, create or modify files, and potentially execute arbitrary code. The following versions of Satel Netco Design are affected: Satel Netco Design CVSS Vendor Equipment v3 8.8 Satel Satel Netco […]
Grid Protection Alliance openPDC and openHistorian
View CSAF Summary The following versions of Grid Protection Alliance openPDC and openHistorian are affected: openPDC <2.9.477, <2.9.482 (CVE-2026-104629, CVE-2026-100730, CVE-2026-105281, CVE-2026-85479, CVE-2026-101022) openPDC (Docker image) <2.9.477, <2.9.482 (CVE-2026-104629, CVE-2026-100730, CVE-2026-105281, CVE-2026-85479, CVE-2026-101022, CVE-2026-105278) openHistorian <2.8.580, <2.8.585 (CVE-2026-104629, CVE-2026-100730, CVE-2026-105281, CVE-2026-85479, CVE-2026-101022) CVSS Vendor Equipment v3 9.8 Grid Protection Alliance openPDC 5 Vulnerabilities Deserialization of […]
Red Lion Controls N-Tron 700 Series
View CSAF Summary Successful exploitation of these vulnerabilities could allow a malicious user to access the device and gain administrative access. This access would allow the user to view, edit, and upload configuration files. Further, a malicious user can cause the switch to reboot by navigating to a specific URL on the device. This action […]
Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data
Advisory at a Glance Title Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data Original Publication October 8, 2026 Executive Summary Chinese government-linked cyber threat actors, enabled by the Integrity Technology Group, are combining automated scanning tools, large-scale botnets, and hands-on exploitation techniques to target and steal sensitive data […]
FBI: FortiBleed attackers can lock organizations out of their own firewalls
Details from an FBI investigation into the ongoing FortiBleed attacks reveal that victims could be locked out of their own firewall even as attackers remain logged in. After gaining access to a backend server left exposed by the attackers, the FBI and US Secret Service have shared new details of an operation that has already […]
Qilin Ransomware Suspect Arrested in Japan, Extradited to Germany
The individual was detained in May and has been extradited to Germany to face hacking charges. The post Qilin Ransomware Suspect Arrested in Japan, Extradited to Germany appeared first on SecurityWeek.
Hadrian Raises $40 Million to Expand Autonomous Offensive Security Platform
Hadrian offers an agentic offensive security platform that allows defenders to operate at the same speed as attackers. The post Hadrian Raises $40 Million to Expand Autonomous Offensive Security Platform appeared first on SecurityWeek.
Advantest Discloses Data Breach Months After Ransomware Attack
The Japanese chip testing giant said hackers stole personal information from its servers in the February 2026 cyberattack. The post Advantest Discloses Data Breach Months After Ransomware Attack appeared first on SecurityWeek.
TP-Link Faces State Lawsuits and New Scrutiny Over ISP Router Flaws
SEC Consult has published technical details on vulnerabilities mentioned in a complaint filed by several US states. The post TP-Link Faces State Lawsuits and New Scrutiny Over ISP Router Flaws appeared first on SecurityWeek.
Fake Decryption Tools Masked $11M Markup in Ransomware Recovery Scheme
Zohar Pinhasi was paying ransoms to obtain decryption keys and then charging victims substantially more for remediation. The post Fake Decryption Tools Masked $11M Markup in Ransomware Recovery Scheme appeared first on SecurityWeek.
Oracle Health Data Breach Tally Climbs to Nearly 20 Million
The figure is far higher than the counts that surfaced in earlier filings and patient notifications. The post Oracle Health Data Breach Tally Climbs to Nearly 20 Million appeared first on SecurityWeek.
FortiBleed Attackers Locking Victims Out of Fortinet Devices
Attackers are creating new accounts and deleting existing ones and passwords to prevent legitimate access. The post FortiBleed Attackers Locking Victims Out of Fortinet Devices appeared first on SecurityWeek.
Georgia Power, Alabama Power Data Breach Hits 400,000 Accounts
Southern Company is notifying customers that their utility account information was accessed by hackers. The post Georgia Power, Alabama Power Data Breach Hits 400,000 Accounts appeared first on SecurityWeek.
Wazza Phishkit Targets Banking, Government, and Manufacturing Across the US, EU, and Australia
Phishing kits are no longer limited to copying a familiar login page and waiting for a victim to enter credentials. Attackers are increasingly building filtering, session management, and traffic controls into the infrastructure that delivers the phishing page itself. ANY.RUN has identified Wazza, a new phishkit targeting banking, manufacturing, and government organizations across the US, […]
AWS takes aim at runaway AI agent behavior with Strands Box
Amazon Web Services (AWS) has introduced an open-source sandbox for AI agents that allows developers to restrict their actions based on previous behavior, seeking to address security risks as enterprises give autonomous systems greater access to applications and data. The tool, called Strands Box, combines operating system-level isolation with policies that govern what agents can […]
16 Malicious Firefox Extensions Pose as Rabby and OKX Wallets to Steal Recovery Phrases
Cybersecurity researchers have discovered a cluster of 16 malicious Mozilla Firefox extensions that are capable of stealing cryptocurrency wallet recovery phrases and private keys. “The extensions masquerade as wallet portals, desktop utilities, and browser tools, but their code intercepts recovery phrases and private keys during wallet import flows and attempts to send those secrets to
We are fighting phishing at the wrong layer
I timed an attacker once. From registering a domain to having it delegated, certificated and serving a live credential-harvesting page took under 24 minutes, and 12 of those were spent waiting on nameservers. I keep coming back to that number, because it quietly indicts most of what we do about phishing. We block domains. We […]
U.S. Offers Up to $10 Million for Tips on Zhang Yu, Charged in HAFNIUM Hacks
The U.S. State Department is offering up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged in the United States in connection with the 2021 Microsoft Exchange Server attacks known as HAFNIUM. The reward is for information leading to his identification or location, the news outlet NTD […]
MonsterCloud Owner Accused of Billing Over $19M While Secretly Paying Ransoms to Decrypt Data
The U.S. Department of Justice (DoJ) on Wednesday announced charges against a 50-year-old U.S. and Israeli national for allegedly defrauding ransomware victims by secretly paying the attackers to obtain decryptors while claiming to use proprietary tools to recover their data. Zohar Pinhasi (aka Zack Silver and Zack Green) has been charged with two counts of […]
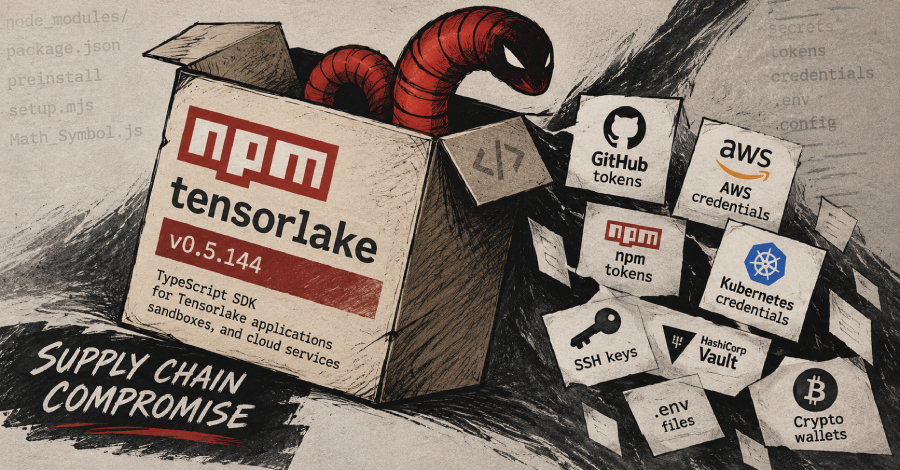
Tensorlake npm Package Compromised to Deliver Shai-Hulud Credential-Stealing Worm
The npm package known as “tensorlake,” a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a ChainDrop / Shai-Hulud supply chain attack. The malicious version 0.5.144 “contains obfuscated malware that harvests credentials, exfiltrates secrets, establishes persistence, and executes remotely supplied code,” Socket said
SonicWall’s latest critical flaw indicates a security pattern, not another one-off bug
SonicWall has disclosed yet another critical flaw in one of its core products. CVE-2026-102255, rated 10 in severity, the highest possible on the Common Vulnerability Scoring System (CVSS), is a pre-authentication server-side request forgery (SSRF) vulnerability in the SMA1000 Appliance Work Place interface. An unintended access path could allow attackers to order the appliance to […]
ISC Stormcast For Thursday, October 8th, 2026 https://isc.sans.edu/podcastdetail/10128, (Thu, Oct 8th)
Post Content
Known Cybersecurity Expert and Owner of Florida Ransomware Remediation Company Charged with Defrauding Clients
Here’s another case where the folks who were supposed to be the good guys helping you may be harming you. Zohar Pinhasi, 50, also known as “Zack Silver” and “Zack Green,” a U.S. and Israeli national, was arraigned today in the Eastern District of New York on wire fraud charges relating to Pinhasi’s false representations… […]
Can you really make more than $200M in six months without encrypting victims? It seems Silent Ransom Group can.
DataBreaches has reported extensively on Silent Ransom Group in 2026, often including material provided exclusively to this site by the group. Now, what appears to be a leak of their internal chats may shed additional light on their success. DataBreaches has reported on Silent Ransom Group (SRG) since 2022, with particular interest in their numerous… […]
2024084295504 Guillermo Enrique Guerra Romiti CRD 4907302 AWC lp.pdf
2024084295504 Guillermo Enrique Guerra Romiti CRD 4907302 AWC lp.pdf Anonymous (not verified) Wed, 10/07/2026 – 17:55 Case ID 2024084295504 Document Number 9cac09b2 Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals Guillermo Enrique Guerra Romiti Action Date Wed, 10/07/2026 – 12:00 Related Content Off Attachment 2024084295504 Guillermo Enrique Guerra Romiti CRD 4907302 AWC lp.pdf […]
26-00922.pdf
26-00922.pdf Anonymous (not verified) Wed, 10/07/2026 – 16:30 Case ID 26-00922 Forum FINRA Document Type Award Claimants Rohin Vinod Respondents Webull Financial LLC Neutrals Gary G. Sackett Hearing Site Denver, CO Award Document 26-00922.pdf Documentum DocID 9d06e581 Award Date Official Wed, 10/07/2026 – 12:00 Related Content Off Claimant Representatives Rohin Vinod Respondent Representatives Naomi Babu
AMD’s plan to boost production could ease AI supply chain concerns
As the demand for AI infrastructure continues to outstrip available capacity, AMD is planning a substantial increase in CPU and GPU supply in 2027. During her recent visit to Taiwan, AMD CEO Lisa Su confirmed that the company is working to expand supply across its ecosystem and is now planning capacity three to five years […]
AI is making software cheap to build. Is your organization ready for what comes next?
What happens once building software stops being expensive? That’s the question at the center of this piece, and I think it’s about to matter for every CIO/CTO managing an enterprise technology budget. For decades, that expense has quietly shaped how enterprises operate. When custom development takes months and a full team, companies buy SaaS products […]
SAP to acquire TechWolf to augment its SuccessFactors HCM platform
SAP is continuing its acquisition spree to help its enterprise customers address what it sees as one of the key challenges around scaling AI: giving Joule agents the appropriate context they need to reason across enterprise data and systems. The enterprise software giant, late on Tuesday, said that it was signing an agreement to acquire […]
Moving off legacy in a regulated business without breaking it
Every CIO in a regulated industry has a system the business depends on, that no one fully understands and that must be replaced. In banking, it is often a core platform that predates the internet. In my own career, that system took two distinct forms: first, a VAX minicomputer running a parking operator’s entire business […]
AI is making software testing cheap. Quality judgment is becoming more valuable
For years, one of the practical constraints in software testing was time. Writing test cases takes time, preparing data takes time, regression takes time and analyzing what happened after an incident can take even more time. AI is changing this very quickly. Today, a QA engineer can generate test data, write scripts, analyze logs or […]
AI governance’s real gap is accountability, not technology
Most enterprises govern AI the way they would any other IT rollout: deploy dashboards, institute policies, and conduct periodic reviews. Having the right AI governance tools in place and addressing gaps is important, but IT executives should be more concerned about rethinking workflows and establishing ownership. “Accountability usually breaks down first,” says Beena Ammanath, executive […]
10 types of ambidextrous leadership required in the AI era
10 types of ambidextrous leadership required in the AI era In the world of corporate management, we face questions every day that don’t have easy answers. We want to accelerate digital transformation, but we absolutely cannot neglect security. We want to pursue company-wide optimization, but we also want to leverage the strengths of each business […]
FBI removes contractor working with its PeopleSoft system after data breach, says report
The US Federal Bureau of Investigation has removed an Accenture contractor working on its PeopleSoft installation over their role in a data breach that exposed personal details of FBI employees, Reuters reported Monday. This is the first time that anyone other than the hacker group Shinyhunters that claimed responsibility for the breach has linked it […]
SAP advances its autonomous AI agenda with yet more Joule Assistants and agents
SAP has launched new AI agents and assistants across multiple domains at its SAP Connect event, saying that its October update is fulfilling the promises it made around its vision of the Autonomous Enterprise at Sapphire in May. The SAP Autonomous Enterprise comprises capabilities in Joule Work and SAP Autonomous Suite, built on the SAP […]
Close the operational security gap: 3 priorities for CIOs
For years, cybersecurity has been measured largely through an IT lens: protect data, prevent intrusions, and keep business systems available. While that framework still matters, it does not fully account for the systems that keep physical operations resilient in the event of an incident. Operational environments rely on connected technologies that monitor, control, or support […]
Attackers Hijack .gh, .sl, and .as Registries to Obtain Certificates for Google Domains
Attackers compromised three country-code top-level domains (ccTLDs) and obtained unauthorized HTTPS certificates for several Google domains, Google said on October 6. Google’s own systems were not breached, but any domain ending in .gh (Ghana), .sl (Sierra Leone) or .as (American Samoa) was put at risk. With such a certificate, an attacker could pose as the real […]
Eight Malicious npm Packages Downloaded 40,767 Times Deliver Overlord RAT and Stealer
Cybersecurity researchers have disclosed details of a long-running npm supply chain malware campaign that pushes information stealers and remote access trojans (RAT) to compromised hosts. The campaign has been codenamed MALFEX by CloudSEK and Checkmarx. The activity is assessed to be the work of a lone threat actor who appears to have published 12 packages […]
Best Execution in Focus: A FINRA Forum on Regulatory Compliance in an Evolving Market Structure
Best Execution in Focus: A FINRA Forum on Regulatory Compliance in an Evolving Market Structure K28672 Wed, 10/07/2026 – 13:42 Event Category Conferences and Events Add to Calendar Yes All Day 1 Event Date Tue, 10/13/2026 – 09:00 – Tue, 10/13/2026 – 09:00 America/New York
SonicWall Patches CVSS 10.0 Pre-Authentication SSRF Flaw in SMA1000 Appliances
SonicWall has released hotfixes for four flaws in its SMA1000 appliances, the gateways that give remote workers access to a company’s network and applications. The most serious could allow an attacker without a login to send requests through the appliance and reach internal functions. SonicWall rates it 10.0 on the CVSS scale and says it […]
Report on September Meeting
Report on September Meeting K30658 Wed, 10/07/2026 – 12:05 October 8, 2026 The FINRA Board of Governors held its third quarterly meeting last week, and I am pleased to share several updates. Rulemaking The following rule proposals were among the items the Board approved for filing with the SEC: to amend rules governing FINRA’s review […]
Unpatched Critical LMCache Flaw Lets Unauthenticated Attackers Run Code Remotely
A critical vulnerability in LMCache, open-source software that speeds up large language model (LLM) servers such as vLLM, lets an attacker run code on the cache server without logging in, and no fixed version is available. The flaw is in LMCache’s multiprocess mode, where the cache runs as a standalone server that LLM workers reach over […]
PoeLLM Malware Infects 3,400+ Servers to Expand Crypto Mining Botnet
Cybersecurity researchers are calling attention to a new malware family that has been observed targeting exposed artificial intelligence (AI) and large language model (LLM) infrastructure with an aim to deploy cryptocurrency miners and further expand the scale of the botnet. The financially motivated campaign, dubbed Canto Incognito, has been found to install cryptocurrency miners, including
2020066079903_Centeno_6368188_SEC_jhjr.pdf
2020066079903_Centeno_6368188_SEC_jhjr.pdf Anonymous (not verified) Wed, 10/07/2026 – 11:25 Case ID 2020066079903 Document Number 8be55c7b Document Type SEC Decisions Individuals Jose L. Centeno Action Date Wed, 09/30/2026 – 12:00 Related Content On Attachment 2020066079903_Centeno_6368188_SEC_jhjr.pdf Individual CRD 6368188
Scans for Atlassian vulnerablity (CVE-2026-21589), (Wed, Oct 7th)
On October 5th, Atlassian published patches for multiple products to fix an “Arbitrary File Access” vulnerability [CVE-2026-21589]. An attacker can read arbitrary files in the web application’s directory, potentially exposing sensitive information such as configuration files.
25-02239.pdf
25-02239.pdf Anonymous (not verified) Wed, 10/07/2026 – 10:05 Case ID 25-02239 Forum FINRA Document Type Award Claimants Michael Sharp Respondents Cetera Wealth Services, LLC Neutrals Richard J. Grahn Steven N. Ainbinder Marvin Kent Speigner Hearing Site Philadelphia, PA Award Document 25-02239.pdf Documentum DocID da47e482 Award Date Official Tue, 10/06/2026 – 12:00 Related Content Off Claimant […]
ShinyHunters Extorted Boeing Spin-off Prior to Arrests
A teenager from Amman, Jordan suspected of leading the prolific data theft and extortion group ShinyHunters has been detained and is reportedly cooperating with the FBI to identify other members of the hacking gang. KrebsOnSecurity has learned that the suspect, who uses the hacker handle “Rey,” was detained as ShinyHunters was in the process of […]
Anthropic widens access to AI cyber capabilities for vetted security teams
Anthropic is expanding its Cyber Verification Program to give more security teams access to advanced cyber capabilities with reduced safeguards on its most advanced AI models. The expanded program has three access tiers based on the type of cybersecurity work an organization is authorized to perform. The tiers cover defensive security work, authorized red teaming, […]
Denmark’s national ID system breach exposes personal data of 8.8M
Denmark is reviewing security controls around its national citizen registry after unauthorized parties exploited a company’s access credentials to harvest records on approximately 8.8 million people over a 10-day period. The breach covers people living in Denmark as well as individuals who have died or moved abroad, while people with protected names and addresses were […]
Alleged ATM malware creator appears in Nebraska court after arrest
Jonathan Greig reports: The alleged mastermind behind a strain of malware used to empty ATMs of millions of dollars appeared in court for the first time after being apprehended by federal authorities. Anibal Alexander Canelon Aguirre pleaded not guilty to several charges in a Nebraska district court on Friday and will remain in detention pending… […]
De Kalb County, Indiana fell prey to vendor impersonation billing
The Star reports that the DeKalb County government fell victim to a cybersecurity incident for the second time in little more than a year. This time, it paid an invoice sent by threat actors impersonating a vendor: “On Thursday, October 1, 2026, DeKalb County Government became aware of a Financial Fraud Cyber Incident that had… […]
Encrypted instructions trick Copilot CLI into spilling developer secrets
GitHub Copilot CLI can be made to read sensitive files from a developer’s machine and send their contents to an attacker from a single web page. Security researchers at Adversa AI said the new attack technique, dubbed Cryptographic Context Injection (CCI), hides malicious instructions inside encrypted content. These instructions are treated as trusted context when […]
Anthropic Introduces 3-Tier Cyber Verification Program for AI Access
Anthropic is integrating the CVP and Project Glasswing into a single offering, with three levels of access to its most capable AI models. The post Anthropic Introduces 3-Tier Cyber Verification Program for AI Access appeared first on SecurityWeek.
ASOS Confirms Cyberattack, Data Breach
Hackers compromised a third-party communication platform and sent rogue notifications to ASOS users. The post ASOS Confirms Cyberattack, Data Breach appeared first on SecurityWeek.
Wikimedia Says Rogue OpenAI Agents Tried to Turn Its Tools Into Proxies
Wikimedia looked into whether its own websites had seen activity like that disclosed by other organizations The post Wikimedia Says Rogue OpenAI Agents Tried to Turn Its Tools Into Proxies appeared first on SecurityWeek.
Android’s October 2026 Updates Patch 25 Vulnerabilities
The patches resolve a critical vulnerability in Android’s System component that could lead to privilege escalation. The post Android’s October 2026 Updates Patch 25 Vulnerabilities appeared first on SecurityWeek.
Atlassian Patches Critical Vulnerability Affecting 8 Products
Unauthenticated attackers could exploit the flaw to access specific files in the web application root directory. The post Atlassian Patches Critical Vulnerability Affecting 8 Products appeared first on SecurityWeek.
Personal Information for Over 1 Million People Stolen in a Cyberattack on Arizona’s Court System
The Arizona Supreme Court said the information was copied for people dating back as far as 30 years. The post Personal Information for Over 1 Million People Stolen in a Cyberattack on Arizona’s Court System appeared first on SecurityWeek.
FBI Blames Contractor’s Missed Patch for ShinyHunters Breach
The FBI has removed an Accenture contractor over a data breach that exposed personal information of thousands of bureau employees. The post FBI Blames Contractor’s Missed Patch for ShinyHunters Breach appeared first on SecurityWeek.
FBI Arrests ‘Most Wanted’ Developer of Ploutus ATM Malware
An alleged leader of Tren de Aragua’s ATM jackpotting activities, Canelon Aguirre was on the FBI’s top 10 most wanted list since March 2026. The post FBI Arrests ‘Most Wanted’ Developer of Ploutus ATM Malware appeared first on SecurityWeek.
Apple to Tighten Full Disk Access Controls in macOS Amid AI Risks
Citing growing risks posed by more capable and autonomous AI agents, Apple will introduce additional controls. The post Apple to Tighten Full Disk Access Controls in macOS Amid AI Risks appeared first on SecurityWeek.
Chrome 155 Update Patches 247 Vulnerabilities
Four critical-severity use-after-free defects were fixed in Chromecast, Browser, Navigation, and Track. The post Chrome 155 Update Patches 247 Vulnerabilities appeared first on SecurityWeek.
Your enterprise doesn’t need six BOM programs. It needs one evidence graph
In infrastructure and security programs, I have watched visibility projects follow a familiar path. The first dashboard feels like progress. Then the data grows, ownership blurs and the team discovers that visibility without identity and action has become another estate to operate. Bill-of-materials programs are reaching that point now. Most CIOs know the Software Bill […]
AI is turning offensive security into a continuous necessity
The rise of AI has CISOs facing even more vulnerabilities than ever, resulting in increasingly difficult decisions around what fixes to prioritize. “When I was a CIO, the hardest part of my job was deciding what not to do,” Snehal Antani, CEO of pentesting platform Horizon3.ai, tells CSO. “And if I chose not to fix […]
Anthropic Expands Claude Access for Vetted Cyber Teams as Glasswing Finds 129,000 Flaws
Anthropic on Tuesday said it’s expanding a program that allows vetted cybersecurity professionals to test its advanced artificial intelligence (AI) models with reduced safeguards and blocking classifiers, as the company claimed its Project Glasswing initiative uncovered at least 129,000 verified software vulnerabilities between April and July 2026. The company said it also found an additional
100+ Compromised Websites Use Fake Cloudflare Checks to Deliver LunexStealer
The Computer Emergency Response Team of Ukraine (CERT-UA) has identified more than 100 compromised websites that have been injected with malicious JavaScript to serve an information-stealing malware called LunexStealer (aka Psychedelic Stealer). The activity, which was observed by the agency in September 2026, has been attributed to a threat cluster dubbed UAC-0277. It did not […]
ISC Stormcast For Wednesday, October 7th, 2026 https://isc.sans.edu/podcastdetail/10126, (Wed, Oct 7th)
Post Content
Atlassian’s critical flaw turns eight enterprise products into one big security problem
A newly-disclosed critical flaw in Atlassian’s data center software has a remarkably wide reach, affecting eight core products across the company’s enterprise portfolio. CVE-2026-21589, rated 9.3 (critical) in severity, is an arbitrary file access vulnerability that could allow an attacker with no login access to read files in web app root directories that they should […]
2025088719301 Gregory Wayne Berg CRD 3081088 AWC lp.pdf
2025088719301 Gregory Wayne Berg CRD 3081088 AWC lp.pdf Anonymous (not verified) Tue, 10/06/2026 – 20:05 Case ID 2025088719301 Document Number 9571c481 Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals Gregory Wayne Berg Action Date Tue, 10/06/2026 – 12:00 Related Content Off Attachment 2025088719301 Gregory Wayne Berg CRD 3081088 AWC lp.pdf Individual CRD 3081088
Engineer sentenced for locking over 3,000 devices on employer’s network
Sergiu Gatlan has an update on a case previously noted on this site. A former core infrastructure engineer at an industrial company headquartered in New Jersey was sentenced to 32 months in prison for locking thousands of devices on his employer’s network in a ransomware-style attack. 57-year-old Daniel Rhyne from Kansas City, Missouri, pleaded guilty… […]
XTX Execution Services LLC Comment On Regulatory Notice 26-15
XTX Execution Services LLC Comment On Regulatory Notice 26-15 fnrw-backend Tue, 10/06/2026 – 15:09 Eric Swanson & Matthew Clarke eric.swanson@xtxmarkets.com XTX Execution Services LLC Regulatory Notice 26-15 Core Official Date Tue, 10/06/2026 – 12:00 Comment File XTX Execution Services LLC_Eric Swanson and Matthew Clarke_26-15_10.6.2026.pdf
ServiceNow takes aim at enterprise AI’s workflow bottleneck with AI Workflow Factory
ServiceNow has launched two AI solutions that can help enterprises identify business processes ripe for automation, build the workflows to address them, and continuously improve them with AI agents. AI Workflow Factory and Autonomous Engineer, announced on Tuesday, will bring process discovery, AI-assisted development and workflow execution into a single system that ServiceNow says can […]
Google overhauls cloud modernization portfolio with new AI agents
Google is overhauling its cloud modernization portfolio by bringing its existing migration and modernization tools along with new agentic migration tools and a new Modernization Hub under a new Google Cloud Modernize umbrella to accelerate infrastructure and application transformation at enterprises. The new agentic tools include an EKS-to-GKE Migration Agent, designed to help enterprises move […]
5 metrics to prove your AI strategy’s business value
Many organizations have licensed language models, tested AI agents, and asked DevOps teams to develop code-generation standards. But production deployments are still a work in progress for CIOs, with only 50% of organizations moving more than half of their AI projects from pilot to production, according to Outsystems’ State of AI Development 2026 report. Increasing […]
Before you buy more AI, diagnose the gap you actually have
A senior executive at a large enterprise recently described a capital allocation review to me. The committee had spent two hours deciding where the next tranche of maintenance capital should go. The discussion drew on last year’s budget, a regional presentation and the persuasive advocacy of a plant head who had been escalating the same […]
The CIO’s new mandate: Rearchitecting enterprise work
What if the most disruptive change to enterprise software is not another application, but needing fewer humans to operate the applications we already own? For decades, we digitized work, integrated systems and moved applications to the cloud. Now we are entering a different era: software is beginning to participate in the work itself. This changes […]
Despite ShinyHunters arrests after FBI jobs data breach, enterprises still have no answers about PeopleSoft risks
The theft of FBI employee data by hacking group ShinyHunters, and the subsequent shutdown of the FBI’s Peoplesoft-based jobs portal, is causing concern for enterprise users of the Oracle product, with analysts recommending extreme measures in response. Law enforcement has made some progress in its pursuit of the cyber criminals involved, but there has still […]
Fake ChatGPT, Gemini, and Claude Ad Portals Capture Credentials and MFA Codes
Cybersecurity researchers have disclosed details of a “human-operated phishing platform” that impersonates advertising products for artificial intelligence (AI) chatbots like Google Gemini, Anthropic Claude, OpenAI ChatGPT, Perplexity, Meta Muse, and Manus. The products, which claim to offer campaign optimization, spend audits, and business-account connections, are designed with one goal in
FBI removes contractor working with its PeopleSoft system after data breach, says report
The US Federal Bureau of Investigation has removed an Accenture contractor working on its PeopleSoft installation over their role in a data breach that exposed personal details of FBI employees, Reuters reported Monday. This is the first time that anyone other than the hacker group Shinyhunters that claimed responsibility for the breach has linked it […]
Linux Backdoors Impersonate Email Security Tools to Evade Detection in Korea and Taiwan
Linux backdoors targeting telecom and network appliances in South Korea and Taiwan have been disguising their traffic as email services and seemingly legitimate processes to blend in and evade detection. Threat actors are known to name their malicious software after a legitimate operating system component or a process as a defense evasion measure. By borrowing […]
20-03200.pdf
20-03200.pdf Anonymous (not verified) Tue, 10/06/2026 – 13:55 Case ID 20-03200 Forum FINRA Document Type Award Claimants Brian Clark Respondents Petersen Investments, Inc. Neutrals Patrick R. Westerkamp Hearing Site Jersey City, NJ Award Document 20-03200.pdf Documentum DocID 85c5473a Award Date Official Mon, 10/05/2026 – 12:00 Related Content Off Claimant Representatives Louis D. Tambaro Respondent Representatives […]
25-02032.pdf
25-02032.pdf Anonymous (not verified) Tue, 10/06/2026 – 13:50 Case ID 25-02032 Forum FINRA Document Type Award Claimants Evan Wood Respondents Amy Bowen Morgan Stanley Computershare Securities Corporation Neutrals Kip C. Lubcke Edith M. Novack Kevin K. Walsh Hearing Site Jersey City, NJ Award Document 25-02032.pdf Documentum DocID 3d0c32e7 Award Date Official Mon, 10/05/2026 – 12:00 […]
25-01274.pdf
25-01274.pdf Anonymous (not verified) Tue, 10/06/2026 – 11:30 Case ID 25-01274 Forum FINRA Document Type Award Claimants Gemma Marta James Marta James and Gemma Marta Family Trust Respondents Wedbush Securities Inc. Raymond Chow Robert Woods Neutrals Mary Mackey U. Martin Laeuchli Jonathan Polland Hearing Site San Francisco, CA Award Document 25-01274.pdf Documentum DocID 36707f53 Award […]
FBI Blames Contractor’s Missed Patch for ShinyHunters Breach
Eduard Kovacs reports: The FBI has removed an Accenture contractor over a data breach that exposed personal information of thousands of bureau employees, Reuters reported on Tuesday, citing two people familiar with the matter. The FBI has not publicly named the contractor or the organization involved. However, a senior bureau official told Reuters that its… […]
Self-described “cybersecurity engineer” arrested after computer case reopened
Natalie Dreier reports: A Florida man who calls himself a “cybersecurity engineer” on TikTok and Twitch was arrested after police reopened an investigation closed earlier this year. Mark Asea was held in the St. Lucie County Jail in Port St. Lucie, Florida, last week on a count of an offense against computer users, WPEC reported…. […]
Japan hands over ‘Qilin’ hacker group member to Germany
JiJi reports: Japanese police have captured a Russian national believed to be a key member of the “Qilin” international hacker group and extradited him to Germany, investigative sources said Tuesday. Qilin is believed to have carried out ransomware attacks against companies worldwide, causing major damage through data encryption. In 2025, the group claimed responsibility online… […]
Denmark Central Person Register (CPR) Breach: Cyberattack Exposes Data of 8.8 Million
Rescana’s new report on a breach affecting the Denmark Central Person Register (CPR) summarizes the situation: On October 5, 2026, Danish authorities publicly disclosed a significant data breach affecting the Central Person Register (CPR), Denmark’s national population database. Attackers exploited a legitimate company account to access the names, addresses, and CPR numbers of approximately 8.8… […]
ASOS customers receive ‘hack’ notification threatening leak
Sarah Butler reports: ASOS is investigating after users of its mobile app received a notification claiming hackers had “fully compromised” the online fashion retailer’s data. The value of Asos’s shares on the London Stock Exchange dived almost 12% after thousands of customers received a notification titled “Asos hacked” with a link that sent them to… […]
Hitachi Energy REB500
View CSAF Summary Hitachi Energy is aware of open-source software vulnerabilities that affect REB500 product versions listed in this document. These vulnerabilities can be exploited to carry out Denial of Service (DoS) attack on the product. Please refer to the Recommended Immediate Actions for information about the mitigation/remediation. The following versions of Hitachi Energy REB500 […]
Hitachi Energy Asset Suite
View CSAF Summary Hitachi Energy is aware of unauthenticated servlet access vulnerabilities that affect Asset Suite product versions listed in this document. These vulnerabilities can be exploited to potentially cause confidentiality, integrity and availability impact on the product. Please refer to the Recommended Immediate Actions for information about the mitigation/remediation. The following versions of Hitachi […]
Johnson Controls EasyIO FG
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to gain full unauthorized access to the device. The following versions of Johnson Controls EasyIO FG are affected: EasyIO FG firmware <=2.0b52 (CVE-2026-27872, CVE-2026-27873) CVSS Vendor Equipment v3 7.7 Johnson Controls EasyIO FG firmware 2 Vulnerabilities Use of Hard-coded Credentials, Improper Privilege Management […]
Hitachi Energy SOI
View CSAF Summary Hitachi Energy is aware of RCE (Remote Code Execution) vulnerability in Apache ActiveMQ component of SOI product versions listed in this document. These vulnerabilities can be exploited to carry out various attacks affecting confidentiality, integrity, and availability of the product. Please refer to the Recommended Immediate Actions for information about the mitigation/remediation. […]
Savannah lwIP SMTP client
View CSAF Summary Successful exploitation of this vulnerability could crash the device being accessed; a buffer overflow condition may allow remote code execution. The following versions of Savannah lwIP SMTP client are affected: lwIP SMTP client 2.2.1 (CVE-2026-15340) CVSS Vendor Equipment v3 9.8 Savannah lwIP SMTP client 1 Vulnerability Buffer Copy without Checking Size of […]
Hitachi Energy RTU500
View CSAF Summary Hitachi Energy is publishing this cybersecurity advisory in response to the security findings reported by Dragos affecting end-of-life RTU500 CMU firmware version 9.x. The reported findings are associated with legacy RTU500 firmware versions that were developed according to the cybersecurity requirements, threat landscape, and industry practices that existed at the time of […]
LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Run Code Without Macro Warnings
A malicious spreadsheet can make LibreOffice and Apache OpenOffice run an attacker’s code as soon as the file is opened, security researchers have shown. There is no warning first, of the kind either program shows before it runs a macro. The attack works only when the program’s Java support is enabled. So far, it has […]
New Linux malware turns vulnerable IoT devices into proxy nodes
A new Linux backdoor is turning vulnerable internet-facing devices into remotely controlled proxy nodes, while using the public Session Traversal Utilities for NAT (STUN) infrastructure to blend into normal VoIP and WebRTC traffic. Fortinet’s FortiGuard Labs said it has been tracking the malware, dubbed ClingSTUN, across multiple attacks exploiting known vulnerabilities in routers, IoT devices, […]
ISC Stormcast For Tuesday, October 6th, 2026 https://isc.sans.edu/podcastdetail/10124, (Tue, Oct 6th)
Post Content
Wikimedia Says OpenAI Agents Tried to Compromise Etherpad and Use Wiki Tools as Proxies
The Wikimedia Foundation, which hosts Wikipedia, has confirmed that it has discovered activity by rogue OpenAI agents on its platforms, including unsuccessful efforts to compromise Etherpad, a public note-taking tool, and edit Wikipedia pages. “The unauthorized bot activities included edits to our wikis, some unsuccessful attempts to exploit a public note-taking tool we host, and […]
Welcome to the Jungle: What We Found Inside 15,465 Public MCP Servers
In 2024, MCP (Model Context Protocol) set out to become the USB-C of AI: one standard for connecting models, agents, and IDEs to tools and data. The protocol delivered. Thousands of developers built servers, and enterprises plugged them into agent workflows. The ecosystem around it fell short. Earlier this year, our team at OX Security, […]
Linux Backdoor Abuses STUN Protocol, Exploits Dozens of Flaws
ClingSTUN operates as a back-connect proxy backdoor, sets up persistence, and contains exploits for self-propagation. The post Linux Backdoor Abuses STUN Protocol, Exploits Dozens of Flaws appeared first on SecurityWeek.
250,000 Impacted by Data Breaches at New Jersey, Texas Healthcare Firms
Hackers stole patient information from Clover Health Investments and AngMar Management Services in July. The post 250,000 Impacted by Data Breaches at New Jersey, Texas Healthcare Firms appeared first on SecurityWeek.
Long-Running NPM Malware Campaign Accumulates 40,000 Downloads
Since August 2023, attackers have published eight malicious packages as part of the MALFEX supply chain campaign. The post Long-Running NPM Malware Campaign Accumulates 40,000 Downloads appeared first on SecurityWeek.
8.8 Million Impacted by Data Breach at Denmark’s Central Person Register
Hackers abused a company’s lawful access to the CPR system to steal the personal information of registered citizens. The post 8.8 Million Impacted by Data Breach at Denmark’s Central Person Register appeared first on SecurityWeek.
Social Engineering Detection Moves Into the Live Conversation
Companies are pouring time and dollars into security awareness training, but little evidence shows it actually works against social engineering. The post Social Engineering Detection Moves Into the Live Conversation appeared first on SecurityWeek.
Google Narrows Open Source Bug Bounty Amid Wave of Invalid Automated Reports
Google has temporarily stopped accepting product vulnerability reports through its Open Source Software Vulnerability Reward Program (OSS VRP). The post Google Narrows Open Source Bug Bounty Amid Wave of Invalid Automated Reports appeared first on SecurityWeek.
Pacing the AI frontier won’t solve agentic cybersecurity’s most urgent problems
When Anthropic CEO Dario Amodei urged other leading AI labs to “pace the frontier” last week, his calls for caution were echoed by other prominent voices in tech. Both Sam Altman and Elon Musk agreed with Amodei’s assessment that pausing AI development was essential to prevent the extinction of the human race. Amodei listed several […]
Google’s bug bounty pause highlights growing AI vulnerability triage challenge
AI is accelerating the discovery of software vulnerabilities, but it is also creating a new bottleneck for defenders: deciding which machine-generated findings warrant investigation. Google has decided to temporarily stop accepting certain bug bounty submissions after a surge of largely invalid automated reports highlights a growing challenge for security teams as AI-driven vulnerability discovery begins […]
The AI app builder your team trusts has a root-level backdoor
The fastest-growing category of enterprise software right now is also the least scrutinized from a security standpoint. AI application platforms — tools that let teams build, connect and automate AI-powered workflows without writing much code — are landing in production environments faster than security teams can assess them. They connect to your APIs, your databases, […]
More RMM Tools In the Wild, (Tue, Oct 6th)
It seems that a trend started… I continue my journey discovering more RMM (“Remote Management & Monitoring”) tools abused by threat actors! A few days ago, I wrote a diary[1] about ScreenConnect used in the wild. Today, I found another one.
Google Pauses OSS Product Bug Bounty Rewards After Surge in Invalid Automated Reports
Google has stopped accepting product vulnerability reports through its bug bounty program for its open-source software. The change, in effect since October 1, means researchers can no longer submit security flaws in the code of projects such as Go, Angular, and Protocol Buffers there for a reward. Reports about supply chain compromises are still accepted, […]
What exactly is ISOC? And what does it mean for you?
Gartner recently released a new category of security tools: the Integrated Security Operations Center (ISOC). This new category acknowledges the need to expand beyond traditional SIEM tools in the creation of a security portfolio, though, as they note in the introductory report, Security Information and Event Management (SIEM) isn’t going anywhere. Gartner’s evolution away from […]
AI accelerates n-day attacks, as flaw disclosures and exploits double
Attackers are increasingly weaponizing already-disclosed flaws rather than new zero-days, and AI tools may be accelerating how quickly they do it. According to a report from Google’s Threat Intelligence Group (GTIG), attackers have exploited more vulnerabilities in the wild thus far this year than they did all of last year. With the number of flaws […]
Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products
A critical flaw in 8 Atlassian Data Center products, which customers host themselves, allows an attacker with no login access to read specific files in each product’s web application root directory. The attacker must already know a file’s exact name and path and cannot list what the directory holds. Atlassian disclosed the flaw, CVE-2026-21589, on October […]
FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach
The U.S. Federal Bureau of Investigation (FBI) has removed an Accenture contractor for their alleged role in a ShinyHunters-breach that led to the theft of personal details of thousands of bureau employees. That’s according to a report from Reuters, citing two sources familiar with the matter. “To date, our review has determined that the incident […]
Denmark Says Attackers Accessed CPR Data for 8.8 Million People via Company Account
Unauthorized parties have gained access to the names, addresses, and personal identification numbers of about 8.8 million people, living and dead, in Denmark’s national population register, the country’s digitalization ministry said on October 5. They used a private Danish company’s lawful right to look up records in the Central Person Register (CPR). The ministry has told […]
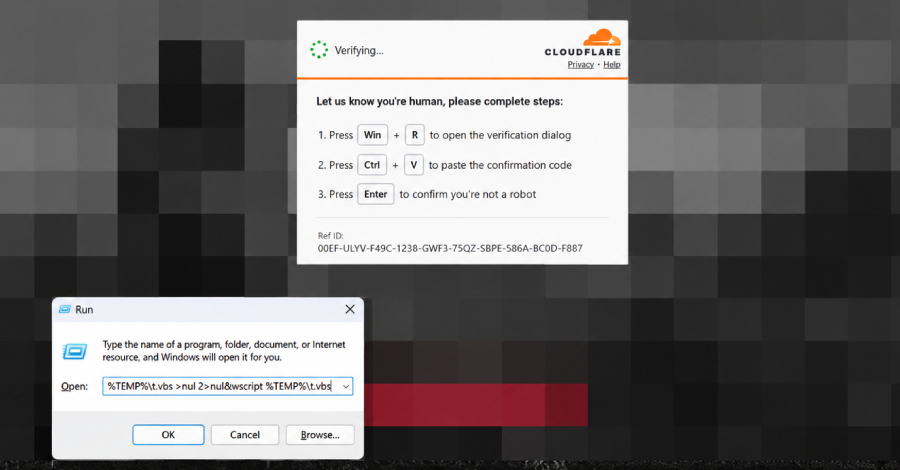
ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits
A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser’s cache. “Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the browser cache disguised as a PNG file,” the […]
Dell patches 18 critical flaws that could hand attackers the keys to storage and Kubernetes
Dell’s security team has had a busy week. The company has announced a slew of Common Vulnerabilities and Exposures (CVEs) impacting its Dell Container Storage Modules (CSM) and Dell System Update (DSU). Disclosed by Dell in two security notices, these critical vulnerabilities could allow unauthenticated attackers to “completely bypass” authentication controls, gain root access, manipulate […]
Despite ShinyHunters arrests after FBI jobs data breach, enterprises still have no answers about PeopleSoft risks
The theft of FBI employee data by hacking group ShinyHunters, and the subsequent shutdown of the FBI’s Peoplesoft-based jobs portal, is causing concern for enterprise users of the Oracle product, with analysts recommending extreme measures in response. Law enforcement has made some progress in its pursuit of the cyber criminals involved, but there has still […]
CISA to keep cyber pay incentives, but less staff will qualify
Justin Doubleday reports: The Cybersecurity and Infrastructure Security Agency is continuing to offer cyber pay incentives to retain skilled technical staff, but less employees will qualify for the program under revised criteria that ties eligibility to job series and performance ratings. The revised policy has sparked some concern that CISA could lose more staff after… […]
2024082473501 Andrew Paul Schneider CRD 2907279 Complaint lp.pdf
2024082473501 Andrew Paul Schneider CRD 2907279 Complaint lp.pdf Anonymous (not verified) Mon, 10/05/2026 – 18:50 Case ID 2024082473501 Document Number a68b799e Document Type Complaints Individuals Andrew Paul Schneider Action Date Mon, 10/05/2026 – 12:00 Related Content Off Attachment 2024082473501 Andrew Paul Schneider CRD 2907279 Complaint lp.pdf Individual CRD 2907279
2022075036201 Gerald James O’Halloran CRD 1056697_Francisco B. Almada CRD 1575694_Union Capital Company CRD 110301 Complaint ks.pdf
2022075036201 Gerald James O’Halloran CRD 1056697_Francisco B. Almada CRD 1575694_Union Capital Company CRD 110301 Complaint ks.pdf Anonymous (not verified) Mon, 10/05/2026 – 18:00 Case ID 2022075036201 Document Number df9e9add Document Type Complaints Individuals Gerald James O’Halloran Francisco B. Almada Action Date Mon, 10/05/2026 – 12:00 Related Content Off Attachment 2022075036201 Gerald James O’Halloran CRD 1056697_Francisco […]
2023077025301 David Lerner Associates, Inc. CRD 5397 AWC ks.pdf
2023077025301 David Lerner Associates, Inc. CRD 5397 AWC ks.pdf Anonymous (not verified) Mon, 10/05/2026 – 17:50 Case ID 2023077025301 Document Number 61d5a3e3 Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Action Date Mon, 10/05/2026 – 12:00 Related Content Off Attachment 2023077025301 David Lerner Associates, Inc. CRD 5397 AWC ks.pdf
2022073920901 William Henry Sandeman CRD 831384 AWC ks.pdf
2022073920901 William Henry Sandeman CRD 831384 AWC ks.pdf Anonymous (not verified) Mon, 10/05/2026 – 17:45 Case ID 2022073920901 Document Number 0c2ce10c Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Individuals William Henry Sandeman Action Date Mon, 10/05/2026 – 12:00 Related Content Off Attachment 2022073920901 William Henry Sandeman CRD 831384 AWC ks.pdf Individual CRD 831384
Small businesses are having their AI moment — and it’s exposing a services gap
I have spent more than 30 years in enterprise IT and managed services. For most of that time, small businesses adopted new technology on a predictable lag. Large enterprises moved first because they had the budget, staff and risk tolerance to experiment. Everyone else waited for the tools to mature and prices to fall. That […]
AI agents: High effort, low return
AI has arrived in the business world — and the results are thus far underwhelming. According to McKinsey, 89% of companies now use AI regularly, and the majority are at least experimenting with AI agents. However, a significant gap remains between usage and economic success. “We find that only 37% of companies attribute any positive […]
AWS seeks to automate cloud optimization with new AI agent
AWS is applying AI to the challenge of evaluating and improving cloud environments with a public preview of a new agentic service aimed at automating the discovery and optimization of architectural issues. Despite its name, AWS makes no claims for the architectural qualities of its Well-Architected Agent, the name of which refers to a long […]
Everybody wants to rule the world
At Oktane a couple of weeks ago, Okta and a group of enterprise heavyweights, including AWS, CrowdStrike, Databricks, Google Cloud, Salesforce, ServiceNow, Wiz and Zscaler, launched the Blueprint Alliance. Their goal is a shared plan for securing and governing AI agents across the enterprise. The biggest names in tech are forming bigger alliances, signing bigger […]
AI doesn’t have to wipe out humanity for the governance model to fail
The latest warnings about artificial intelligence are difficult to brush aside. Anthropic researcher Jacob Coxon resigned last month, walking away shortly before his equity was due to vest, and publicly argued that leading AI companies are advancing toward increasingly capable systems without adequate assurance that those systems will remain controllable. His resignation landed amid a […]
IT modernization: Still a make-or-break project for CIOs
Sumit Johar has been modernizing BlackLine’s IT environment since becoming CIO of the software company in early 2024. As a longtime IT leader, Johar has plenty of experience overhauling tech stacks, but he says the work has taken on new meaning — and urgency — in the AI era. “The definition of modernization has literally […]
The real AI budget question: Where should we spend more?
I recently met with a client’s CEO and CIO together. The CIO asked, “How much should we spend on AI next year?” My response was, “If you do your job right, your CEO will ask why you aren’t spending more.” I spend a lot of time with CIOs who are planning their AI investments. One […]
3 best practices for CIOs to assess AI ROI
Most CIOs can easily describe their AI initiatives, but struggle to demonstrate and report on AI value and ROI. This is evidenced by Gartner’s AI ROI Vendor Sentiment survey, which found that 27% of respondents strongly agree that ROI from AI initiatives is difficult to quantify. In addition, only one in four had a clear […]
Why judgment matters more, not less, in the AI era
For a few years now, the headlines have become familiar: yet another company laying off workers as a result of AI. But in recent months, we’ve seen a new twist. Some of those same companies are now reconsidering staffing decisions after recognizing the continued need for experienced professionals. Ford offers a telling example. In 2023, […]
Best Execution in Focus: A FINRA Forum on Regulatory Compliance in an Evolving Market Structure | Oct. 13
Best Execution in Focus: A FINRA Forum on Regulatory Compliance in an Evolving Market Structure | Oct. 13 K30658 Mon, 10/05/2026 – 13:28 Join FINRA for a forum bringing together market experts to examine the evolving landscape of best execution in today’s markets. With significant market structure developments underway, including the SEC’s proposed rescission of […]
Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users' Mailboxes
Microsoft has released out-of-band security updates to address a high-severity flaw in Microsoft Exchange Server that could allow an attacker to escalate privileges under certain conditions. The vulnerability, tracked as CVE-2026-96940, is rated 8.8 on the CVSS scoring system. “Weak authorization in Microsoft Exchange Server allows an authenticated attacker to elevate privileges over a
Nueva EPS, Colombia’s largest regional healthcare promoting entity has allegedly been hacked (1)
Colombia’s largest health-promoting entity, Nueva EPS, has allegedly been hacked by an individual demanding $15 million not to leak the data. Colombia’s healthcare system includes Entidad Promotora de Salud (EPS), regional health-promoting entities responsible for implementing objectives set by the Ministry of Health, developing guidelines and protocols, and overseeing healthcare delivery. As Wikipedia describes, an… […]
⚡ Weekly Recap: NetScaler and FortiMail 0-Days, AI Coding Leaks, Spectre v2 and Ransomware Arrests
A blank field. A public repo. One reply to an email. A box left exposed. None of this sounds dramatic, which is partly the problem. This week’s threats keep finding leverage in small things that were easy to overlook. There are actively exploited bugs in the mix, cleaner intrusion paths, smarter automation, and a long […]
Hackers Breached Propulsion System of U.S.-Bound Oil Tanker
Seen on Homeland Security Today: FBI and US Coast Guard investigators have found evidence that hackers accessed the propulsion system of an oil supertanker as it was approaching the Texas coast this summer, according to US officials familiar with the matter, an extraordinary breach that highlights the growing physical risks from cyberattacks. The cyberattack resulted… […]
Daiwa Securities says info on 110,000 clients may have been leaked in vendor incident
Takashi Nakamichi and Ryo Horiuchi report that Daiwa Securities, Japan’s second-largest brokerage and investment banking firm, is responding to a breach at one of its vendors. Daiwa Securities Group said information on as many as 110,000 clients may have been stolen after the servers of an external vendor were hacked. Japan’s second-largest brokerage received a… […]
Ransomware group threatens to leak customer data from top insurance companies in South Africa
Luis Monzon reports: Ransomware-as-a-service group The Gentlemen threatened to leak data belonging to insurance companies LegalWise and Samwumed, with more South African companies likely to follow. The Gentlemen is one of the most active cybercriminal organisations in the world, and accounted for 17% of all ransomware attacks globally in July, according to Check Point Software…. […]
Citrix warns of actively exploited NetScaler flaw days after zero-day patch rush
Citrix has warned customers about another high-severity vulnerability in its NetScaler ADC and NetScaler Gateway products, just days after the company urged them to fix a separate batch of flaws that included two actively exploited zero-days. The new vulnerability, tracked as CVE-2026-88779, is a memory-overflow issue that can cause a denial-of-service (DoS) condition on affected […]
The Credential Layer Is Expanding Faster Than Security Teams Can See It
Every modern enterprise depends on credentials. This is how humans, systems, and now AI, all connect to data, services, and each other securely. GitGuardian helps secure that credential layer through three connected capabilities: Detect, Remediate, and Prevent. The journey starts with detection, because organizations first need to understand what credentials exist, where they live, and […]
Realtek Jungle SDK Exploit Attempts Deliver Cling Botnet With STUN-Based C2
Threat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit (SDK) to deploy a botnet malware called Cling. “Cling is notable not because it introduces a new propagation technique, but because it repurposes ordinary STUN behavior into a practical command-and-control channel,” Nozomi Networks said in […]
Exploitation Hits Rejetto HFS Vulnerability Discovered by AI
CVE-2026-61500 allows attackers to recover the session-cookie signing key and gain administrative access and RCE. The post Exploitation Hits Rejetto HFS Vulnerability Discovered by AI appeared first on SecurityWeek.
Senate Passes Bipartisan Bill to Strengthen Healthcare Cybersecurity
More than 730 cyber breaches affected over 270 million Americans last year, costing an average of $10 million per breach. The post Senate Passes Bipartisan Bill to Strengthen Healthcare Cybersecurity appeared first on SecurityWeek.
Alleged ShinyHunters Leader Arrested in Jordan
Known as Rey, the suspect is reportedly helping the FBI identify and locate other members of the extortion group. The post Alleged ShinyHunters Leader Arrested in Jordan appeared first on SecurityWeek.
Exploitation of Citrix NetScaler Zero-Day Hits Appliances Patched Days Earlier
Citrix has confirmed that a new zero-day vulnerability, CVE-2026-88779, emerged just days after two other exploited flaws were patched. The post Exploitation of Citrix NetScaler Zero-Day Hits Appliances Patched Days Earlier appeared first on SecurityWeek.
Trump Names National Intelligence Director Jay Clayton to Lead a New Federal AI Task Force
The announcement comes after Trump hosted top executives of AI companies at the White House last week. The post Trump Names National Intelligence Director Jay Clayton to Lead a New Federal AI Task Force appeared first on SecurityWeek.
Apple Plans Tighter macOS Full Disk Access Controls Over AI Agent Data Access
Apple has announced that it’s taking steps to tighten controls around a macOS setting called Full Disk Access (FDA) due to security risks posed by artificial intelligence (AI) agents. “Some developers are using Full Disk Access in ways that could put users at risk, exposing everything on their systems—including files, mail, messages, and even browsing […]
Should the CISO role be split in two?
In its roughly 30-year history, the CISO role has been reshaped by waves of new technology and rising cyber threats. In many organizations, CISOs now own risk reporting, information risk management, threat monitoring, cyber risk accountability and governance, and security strategy. And as AI and digital dependence grow, the CISO’s remit is growing beyond security […]
Attackers Target Rejetto HFS Flaw That Enables Admin Session Forgery and RCE
A critical security flaw impacting Rejetto HTTP File Server (HFS) is witnessing active exploitation attempts, according to VulnCheck. The vulnerability in question is CVE-2026-61500 (CVSS score: 9.3), a case of session forgery stemming from the use of a weak pseudo-random number generator (PRNG) that can lead to a predictable key, which an attacker can then […]
New NetScaler Zero-Day Exploited in Targeted Attacks Can Knock SAML Deployments Offline
Citrix has released security updates for a high-severity security flaw in NetScaler ADC and Citrix NetScaler Gateway that has been exploited as part of targeted zero-day attacks. The vulnerability, tracked as CVE-2026-88779, carries a CVSS score of 8.7 out of 10.0. “CVE-2026-88779 is a memory overflow vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway […]
ISC Stormcast For Monday, October 5th, 2026 https://isc.sans.edu/podcastdetail/10122, (Mon, Oct 5th)
Post Content
TTY Logs and the Data it Captures, (Sun, Oct 4th)
For an experiment, I created a script [1] that parses and send the TTY logs collected from actors or bots activity that run various commands after they successfully login the DShield sensor. Those TTY logs are sent daily at the end of each day to the DShield SIEM [2] to be correlated with all the […]
South Korea’s President Lee Jae Myung orders thorough probe into data breaches at local banks
Lee Hyo-jin reports: President Lee Jae Myung on Sunday ordered a thorough investigation into a string of recent data breaches at financial institutions, as artificial intelligence (AI)-powered cyberattacks increasingly target them. According to Cheong Wa Dae, Lee was briefed on recent data breaches at financial and public institutions and their responses to the incidents. “The… […]
Slate Valley Unified School District voted not to pay ransom demand; Kairos likely to leak data
The Slate Valley Unified School District in Fair Haven, Vermont, has been responding to a security incident since September 3. On October 2, Kairos threat actors contacted DataBreaches to alert us to the incident and their response to the district’s claim that they believed student data had not been compromised. They were also angry that… […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-88779 Citrix NetScaler Improper Restriction of Operations within the Bounds of a Memory Buffer Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding […]
Fortra Patches Critical Vulnerabilities in BoKS
The bugs could lead to authentication bypass, shell command execution, and memory corruption. The post Fortra Patches Critical Vulnerabilities in BoKS appeared first on SecurityWeek.
doxx.net Raises $38 Million to Prevent AI Agent-on-the-Internet Misadventures
doxx.net’s new ADN platform prevents agentic misadventure while the agent is operating under the user’s authority. The post doxx.net Raises $38 Million to Prevent AI Agent-on-the-Internet Misadventures appeared first on SecurityWeek.
User Agent Strings Curiosities, (Sun, Oct 4th)
Sometimes I have to smile, or my interest is triggered, when I review new User Agent Strings in the honeypot logs.
ShinyHunters Suspect Rey Reportedly Detained in Jordan, Helping FBI Identify Group Members
A suspected member of the ShinyHunters digital extortion group, who goes by the online alias “Rey,” has been allegedly detained by authorities in Jordan, Reuters reported, citing three people familiar with the matter. Rey, whose real name is Saif al-Din Khader, is said to have been brought into custody on September 29, 2026, cooperating with […]
China-Aligned TA419 Targets U.S. AI Policy Experts With Microsoft AitM Phishing
A new China-nexus cyber espionage group known as TA419 has been attributed to multiple credential phishing campaigns targeting artificial intelligence (AI) experts working for U.S. think tanks, universities, and legal sector organizations. The campaigns have impersonated prominent economists and AI policymakers, as well as a prominent Anthropic employee, to single out an AI policy expert […]
Italy’s Data Protection Authority fines IQVIA €7 million over data protection breach
The following is a machine translation of a press release by Italy’s privacy guarantor: Healthcare data: The Privacy Guarantor fines IQVIA 7 million euros. The data of one million patients of 800 family doctors are not anonymous. The Italian Data Protection Authority has fined IQVIA Solutions Italy Srl €7 million. The company, part of a… […]
ShinyHunters hacker “Rey,” allegedly involved in FBI data theft, detained in Jordan
Jana Winter, Raphael Satter, and A.J. Vicens report: A key member of the ShinyHunters hacking group, which claims to have stolen data on every FBI employee, was detained this week in Jordan, three people familiar with the matter told Reuters. Two of the sources said he was cooperating with the FBI to identify his fellow… […]
YARA-X 1.21.0 Release, (Sat, Oct 3rd)
YARA-X’s 1.21.0 release brings 5 improvements and 4 bugfixes.
MI5 Says China’s MSS Funded Research Involving 100+ U.K.-Linked Academics
The U.K.’s domestic intelligence and security agency has warned that more than 100 academics have helped China boost its intelligence gathering efforts on behalf of Beijing’s state security service. In a “Security Service Espionage Alert” issued on September 30, 2026, MI5 said the “primary purpose of the China General Technology Research Institute (CGTRI) 中国通用技术研究院 is […]
Warlock Exploits SharePoint Flaws to Disable Security Tools and Deploy Ransomware
The suspected China-linked threat actor known as Warlock is still continuing to weaponize Microsoft SharePoint vulnerabilities, likely both old and new, in attacks targeting organizations in Portuguese- and Spanish-speaking countries. The activity, observed by the Symantec and Carbon Black Threat Hunter Team, has hit critical infrastructure, government, and education organizations. “In the
DHS readies major cyber contract
Justin Doubleday reports: The Department of Homeland Security is preparing this year to award a major cloud, cybersecurity and network services contract aimed at further centralizing the management of IT services across DHS. In a notice posted to Sam.gov last month, DHS laid out the notional timeline for award of the Network, Cloud and Cybersecurity… […]
OpenAI faces California DOJ subpoena amid growing cybersecurity incident notices
IAPP reports: Regulator inquiries into major AI companies’ cybersecurity practices are ramping up. A day after reports surfaced about the likely escalation of a U.S. Federal Trade Commission probe into OpenAI and other developers, California Attorney General Rob Bonta advanced his office’s ongoing OpenAI investigation. Bonta announced the company was served an investigative subpoena to… […]
Fed employee repeatedly removed sensitive files, watchdog finds
Matt Bracken reports: A Federal Reserve Board staffer mishandled sensitive classified files and triggered hundreds of data loss prevention alerts leading up to their retirement, the agency’s inspector general revealed in a new report. The security issues with the employee were uncovered by the watchdog during its audit of the Fed’s offboarding process, which began… […]
Over 543,000 valid credentials exposed in public GitHub repositories
Bill Toulas reports: More than 543,000 credentials exposed in public GitHub repositories were still valid in July despite the platform’s security measures to prevent accidental leaks of sensitive data. Data pulled from scanning 224 million repositories and more than 58 billion files show that the median time a unique credential remained publicly accessible was 784… […]
Senate passes bipartisan bill to bolster hospital cybersecurity
Naomi Diaz reports: The Senate passed the bipartisan Health Care Cybersecurity and Resilience Act by unanimous consent. The legislation aims to help healthcare providers strengthen their cybersecurity defenses and protect patient information, according to an Oct. 1 news release from the Senate Committee on Health, Education, Labor and Pensions. Sens. Bill Cassidy, MD, R-La., Maggie… […]
Medical records giant Epic pauses product development to fix security bugs that risk patients’ data
Zack Whittaker reports: Epic, the software technology giant that makes the widely used MyChart software for accessing patients’ medical data, has paused most of its product development as the company works to protect its software and systems from cyberattacks. Judy Faulkner, the founder and chief executive of Epic, told Modern Healthcare last month that the… […]
Metamask discloses security incident affecting its infrastructure
Sergiu Gatlan reports: On Thursday, cryptocurrency wallet provider MetaMask has disclosed an ongoing infrastructure security incident affecting some of its infrastructure. The company is working to address the issue internally, with help from external partners and security advisors, and says there is “no immediate threat to MetaMask wallets.” “As a precautionary measure, we are proactively… […]
In Other News: $15K iCloud Spoofing Bugs, AI Policy Experts Phished, Adblocker Spies on AI Chats
Noteworthy stories that might have slipped under the radar: Kiteworks patches over 100 vulnerabilities, Microsoft publishes 2026 Digital Defense Report, AI finds 24 Android app flaws. The post In Other News: $15K iCloud Spoofing Bugs, AI Policy Experts Phished, Adblocker Spies on AI Chats appeared first on SecurityWeek.
macOS Users Targeted by Fake Zoom Installer Carrying CloudSyncD Backdoor
The dropper “carries a complete universal Mach-O inside itself, roughly 756 KB in the development build, and extracts it at runtime. The post macOS Users Targeted by Fake Zoom Installer Carrying CloudSyncD Backdoor appeared first on SecurityWeek.
Crypto Scammers Hijack Microsoft’s Official X Account
Hackers used the account, which has 13 million followers, to amplify a Clippy-themed cryptocurrency account. The post Crypto Scammers Hijack Microsoft’s Official X Account appeared first on SecurityWeek.
In Rare Move, Alleged Iranian State Hacker Extradited to US
Amir Barati, an alleged member of the Mabna Institute, was indicted for targeting universities, private organizations, and government entities in the US and abroad. The post In Rare Move, Alleged Iranian State Hacker Extradited to US appeared first on SecurityWeek.
The State of Cybersecurity in 2026: Key Segments, Insights, and Innovations
Featuring: Cybersecurity is being reshaped by the expansion of cloud infrastructure, AI, distributed systems, and increasingly complex digital environments. As organizations manage more identities, devices, data, and internet-facing infrastructure, security is shifting toward continuous visibility, control, and the ability to respond to risk at scale. This report examines how core areas of
22-01970(4).pdf
22-01970(4).pdf Anonymous (not verified) Fri, 10/02/2026 – 17:30 Case ID 22-01970 Forum FINRA Document Type Award Claimants Merrill Lynch Pierce Fenner & Smith Inc. Respondents John Lahoud Neutrals Robert J. Kheel Sandra J. Mullings Arturo C. Porzecanski Hearing Site New York, NY Award Document 22-01970(4).pdf Documentum DocID 12637594 Award Date Official Fri, 04/11/2025 – 12:00 […]
26-01240.pdf
26-01240.pdf Anonymous (not verified) Fri, 10/02/2026 – 17:30 Case ID 26-01240 Forum FINRA Document Type Award Claimants Morgan Stanley Morgan Stanley Smith Barney Financing LLC Respondents Calvin Shiu Neutrals Arocles Aguilar Hearing Site San Francisco, CA Award Document 26-01240.pdf Documentum DocID 1efcfca6 Award Date Official Fri, 10/02/2026 – 12:00 Related Content Off Claimant Representatives Jennifer […]
24-00310.pdf
24-00310.pdf Anonymous (not verified) Fri, 10/02/2026 – 17:25 Case ID 24-00310 Forum FINRA Document Type Award Claimants Wells Fargo Clearing Services, LLC Respondents Chad Bushaw Neutrals Jill M. Zacha John Kenneth Popham Charles McGarry Hearing Site Dallas, TX Award Document 24-00310.pdf Documentum DocID 16df0aa4 Award Date Official Fri, 10/02/2026 – 12:00 Related Content Off Claimant […]
26-00385.pdf
26-00385.pdf Anonymous (not verified) Fri, 10/02/2026 – 16:25 Case ID 26-00385 Forum FINRA Document Type Award Claimants Wells Fargo Clearing Services, LLC Respondents Anne Satterfield Neutrals Langfred W. White Hearing Site Raleigh, NC Award Document 26-00385.pdf Documentum DocID ee2ec911 Award Date Official Fri, 10/02/2026 – 12:00 Related Content Off Claimant Representatives John Wesley Holston Respondent […]
25-02404.pdf
25-02404.pdf Anonymous (not verified) Fri, 10/02/2026 – 16:15 Case ID 25-02404 Forum FINRA Document Type Award Claimants Joel Angeles Respondents Fidelity Brokerage Services LLC Neutrals Mary Mackey Hearing Site San Francisco, CA Award Document 25-02404.pdf Documentum DocID 806cc3b7 Award Date Official Fri, 10/02/2026 – 12:00 Related Content Off Claimant Representatives Joel P. Angeles Respondent Representatives […]
Who should own analytics: IT, the business or both?
Clients ask me this question perhaps more than any other. They’ve usually just come off a bad experience, either analytics stuck in IT’s backlog for months or analytics scattered across the business without anyone accountable for what it all means. My answer is always the same. Split it. IT owns the data engineering. The business […]
Who should own AI? I started with an incomplete answer
Several months ago, I was invited to an event for CTOs. Just looking around the room, I could see someone had made an assumption about my title. I am a chief transformation officer, not a chief technology officer. I stayed anyway to see how the other type of CTO thinks about AI. When a CISO […]
$6T in annual AI revenue needed to pay off data center investments
Hyperscalers are rushing to build more data centers to run AI workloads — but will the AI industry ever generate enough revenue to pay for that infrastructure? Researchers at Bain and Company have looked into this and concluded that productivity gains from existing AI services are not enough to justify the money being pumped in: […]
AI could boost software engineer productivity by 32.6%
Tools such as Anthropic Claude Code or OpenAI Codex have changed the face of software development, and all the signs are that this investment is set to increase further. But is paying a monthly subscription (and perhaps additional usage fees) cost-effective? Will the increasing level of investment in AI-generated software prove to be worthwhile? That’s […]
Omnissa delivers a peek into the benefits of breaking through enterprise data silos
When Omnissa this week rolled out a new AI governance authority product, Elara, in beta, it delivered a glimpse into the potential of having visibility between the typical enterprise’s data silos, whether they’re in lines of business, disparate geographies, or corporate operational units. “By connecting signals across systems that often operate independently, Elara gives IT […]
A human rubber stamp on AI-based HR decisions won’t satisfy California’s No Robo Bosses law
California is setting a precedent for AI use in scenarios where workers’ jobs are at stake. Governor Gavin Newsom this week signed the No Robo Bosses Act (SB 947), which bans employers from relying solely on AI-powered automated decision-making systems (ADS), also known as “bossware,” to discipline or terminate workers. Introduced by Senator Jerry McNerney, […]
Microsoft, Google back Apache Ossie to make enterprise data and AI platforms more interoperable
Microsoft and Google are joining a project to create an open specification for exchanging semantic models across data, analytics, and AI platforms. The project already has the backing of over 60 companies including Databricks, Informatica, Mistral AI, Nvidia, Oracle, Salesforce, and Snowflake. Their support for Ossie makes it a little more likely that future analytics […]
GitLab Patches Critical 9.9 AI Gateway Flaw Allowing Command Execution on Self-Hosted Servers
A critical flaw in GitLab’s AI Gateway could let a logged-in user with Duo Agent Platform access run commands on the gateway under certain conditions, GitLab said in an advisory. The gateway is the service that connects a GitLab instance to AI models, and only organizations that host their own gateway need to act. The flaw […]
Antino Backdoor Uses Outlook and OneDrive for C2 in China-Nexus Espionage Campaign
Government and policy organizations across Asia have become the target of a new campaign orchestrated by a China-nexus threat actor. The activity, which has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamed Antino. Cisco Talos is tracking the cluster
Dell CSM Flaws Enable Unauthenticated Admin Access and Root on Kubernetes Nodes
Dell has released security updates to address multiple critical security flaws in Dell Container Storage Modules (CSM) that could be exploited by bad actors to take over susceptible systems. The vulnerabilities are listed below – CVE-2026-63688 (CVSS score: 10.0) – A missing authentication for critical function vulnerability in the csm-authorization-storage gRPC server that an
City of Vicksburg, Mississippi, shuts down computers after cyberattack
Joseph Topping reports: The City of Vicksburg, Mississippi, has shut down its computer systems after a ransomware attack, potentially delaying in-person utility payments while emergency response and utility service continue. Mayor Willis Thompson told The Vicksburg Post that the city had disconnected its internet operations. “We had to bring our internet operations down, just for… […]
OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling
OpenAI has parted ways with three members of its safety team after they leaked private information in violation of company policies, The Wall Street Journal reported. “We have parted ways with three individuals for violating our policies on accessing and handling sensitive company information,” a spokesperson for the company was quoted as saying. “Our investigation […]
CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-102489 Zammad GmbH Zammad Session Fixation Vulnerability CVE-2026-102490 Zammad GmbH Zammad Improper Privilege Management Vulnerability These types of vulnerabilities are frequent attack vectors for malicious cyber actors and pose significant risks to the federal enterprise. Binding […]
Why CISOs Struggle to Answer the Board's Three Hardest Questions, and How to Fix the Report
The quarterly board meeting is two weeks out. The security team is pulling exports from the identity provider, the cloud posture tool, the vulnerability scanner, the SIEM and the EDR console. Someone is building a spreadsheet to reconcile them. Someone else is turning that spreadsheet into slides. Then a board member asks three questions: How […]
Warlock Expands SharePoint Exploitation in Critical Infrastructure Attacks
The China-based hacking group has been exploiting SharePoint vulnerabilities since July 2025. The post Warlock Expands SharePoint Exploitation in Critical Infrastructure Attacks appeared first on SecurityWeek.
AI Agents Aimed SQL Injection at US and Canadian Government Sites
The attacks targeted the US Department of Education and Library and Archives Canada, and researchers linked some agents to OpenAI. The post AI Agents Aimed SQL Injection at US and Canadian Government Sites appeared first on SecurityWeek.
Exploited Fortinet FortiMail Zero-Day Calls for Urgent Action
CVE-2026-104286 is a critical-severity path traversal vulnerability that could allow attackers to write arbitrary files to the system. The post Exploited Fortinet FortiMail Zero-Day Calls for Urgent Action appeared first on SecurityWeek.
Zero Trust Creator Says Model Holds Firm Against AI-Assisted Attacks
Fifteen years after coining the framework, John Kindervag insists zero trust still works in the AI era—if you get the implementation right. The post Zero Trust Creator Says Model Holds Firm Against AI-Assisted Attacks appeared first on SecurityWeek.
Osavul Lands $10 Million to Spot Hostile Intent Across Cyber, Physical Domains
Hybrid risk intelligence company Osavul has raised $10 million in a Series A funding round led by 33N Ventures. The post Osavul Lands $10 Million to Spot Hostile Intent Across Cyber, Physical Domains appeared first on SecurityWeek.
Hacker Conversations: Rob Juncker, a Knock at the Door and a Moral Compass
Rob Juncker is chief product and technology officer at Mimecast. Is he a hacker? “Unequivocally yes,” he says. The post Hacker Conversations: Rob Juncker, a Knock at the Door and a Moral Compass appeared first on SecurityWeek.
Enterprises Struggle to Prepare for AI and Quantum Threats, PwC Says
PwC’s survey found that only 22% of leaders would use fully autonomous AI for cyber defense, while just 21% are implementing quantum-resistant security measures. The post Enterprises Struggle to Prepare for AI and Quantum Threats, PwC Says appeared first on SecurityWeek.
Police Shut Down KillSec Ransomware, Identify Alleged Teen Leader
Police took control of KillSec’s leak site and secured at least 110 terabytes of data stolen from victims. The post Police Shut Down KillSec Ransomware, Identify Alleged Teen Leader appeared first on SecurityWeek.
AI Has Changed Attack Speed, Not Security Fundamentals
As AI accelerates vulnerability discovery and exploitation, so-called virtual patching still comes down to defense-in-depth and strong application security fundamentals. The post AI Has Changed Attack Speed, Not Security Fundamentals appeared first on SecurityWeek.
Zimbra Vulnerability Exploited in the Wild Prior to Public Disclosure
Under certain conditions, CVE-2026-73570 can be exploited via specially crafted emails without user interaction. The post Zimbra Vulnerability Exploited in the Wild Prior to Public Disclosure appeared first on SecurityWeek.
Rolling the cyber dice with open-source and open-weight AI models
With typical cybersecurity exposure, I can conduct pen testing with deterministic tools. I am able to predict how a piece of software is going to respond. I even stand a decent chance of finding vulnerabilities before they can be exploited against me. What we are dealing with now is a new kind of exposure. For […]
EU Cyber Resilience Act ‘completely kills’ manual vulnerability triage
Independent security experts see the EU Cyber Resilience Act (CRA) reshaping international technology markets to emphasize cyber resilience from the ground up, thereby testing the operational capacities of technology vendors whose wares compete in those markets. The EU CRA introduces mandatory reporting within 24 hours for any actively exploited vulnerabilities or severe incidents affecting products […]
Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools
Google has announced a new security measure that limits access to Android’s accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android applications abusing the API serving as the main conduit for malware and financial fraud, the tech giant said the move would block a major attack pathway. […]
Critical FortiMail Zero-Day Flaw Exploited in Attacks Allows Unauthenticated Arbitrary File Writes
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added a critical security flaw impacting Fortinet FortiMail to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability, tracked as CVE-2026-104286 (CVSS score: 9.8), allows unauthenticated attackers to write arbitrary files on the underlying system. “An improper
ISC Stormcast For Friday, October 2nd, 2026 https://isc.sans.edu/podcastdetail/10120, (Fri, Oct 2nd)
Post Content
2025087193401 Joel A Benanti CRD 4210681 OHO Decision df.pdf
2025087193401 Joel A Benanti CRD 4210681 OHO Decision df.pdf Anonymous (not verified) Thu, 10/01/2026 – 18:35 Case ID 2025087193401 Document Number f4735b07 Document Type OHO Decisions Individuals Joel A Benanti Action Date Wed, 09/23/2026 – 12:00 Related Content On Attachment 2025087193401 Joel A Benanti CRD 4210681 OHO Decision df.pdf Individual CRD 4210681
25-01613.pdf
25-01613.pdf Anonymous (not verified) Thu, 10/01/2026 – 16:35 Case ID 25-01613 Forum FINRA Document Type Award Claimants Frank Mastropaolo Respondents Fidelity Brokerage Services LLC Neutrals Sandra J. Mullings Ann Judith Gellis Edmund Timothy Donovan Hearing Site New York, NY Award Document 25-01613.pdf Documentum DocID 15b1b3da Award Date Official Thu, 10/01/2026 – 12:00 Related Content Off […]
Alexander Cohen Comment On Regulatory Notice 26-15
Alexander Cohen Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 16:15 Alexander Cohen Alex Cohen <alexander.ross.cohen@gmail.com> Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File Alexander Cohen_26-15_10.1.2026.pdf
Anonymous Comment On Regulatory Notice 26-15
Anonymous Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 16:11 Anonymous Counter Culture <bryanmosley1@gmail.com> Regulatory Notice 26-15 Core Official Date Tue, 09/29/2026 – 12:00 Comment File Anonymous_cc_26-15_9.29.2026.pdf
Bloomberg Comment On Regulatory Notice 26-15
Bloomberg Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 16:06 Gregory Babyak Gary Stone (BLOOMBERG/ 731 LEX) <gstone2@bloomberg.net> Bloomberg Regulatory Notice 26-15 Core Official Date Tue, 09/29/2026 – 12:00 Comment File Bloomberg_Gregory Babyak_26-15_9.29.2026.pdf
Teenagers suspected of leading KillSec ransom group arrested during international operation
DataBreaches has reported on a group known as KillSec for almost two years. This time, we get to report on their arrest. The European Union Agency for Criminal Justice Cooperation issued this press release today: An international group of authorities from nine countries, coordinated by Eurojust and Europol, has successfully shut down a ransomware group… […]
Memory squeeze set to tighten through 2028, Micron says
The global memory shortage that has driven up the cost of servers, storage and PCs through 2026 will get worse in 2027 and 2028, according to memory maker Micron Technology. “We expect memory and storage supply-demand conditions to be much tighter in calendar 2027 and 2028 than they were in 2026,” CEO Sanjay Mehrotra said […]
ServiceNow launches standalone AI service desk to provide support in Teams, Slack, and email
ServiceNow has a new take on the service desk: Flow by ServiceNow, a standalone AI product that allows users to get help via chats in Microsoft Teams, Slack, or a Flow web app, or by email, rather than having to leave what they’re doing to open a helpdesk ticket. Flow can be up and running […]
AI and the impending third technology talent drought
Every technology professional working today owes their career, in part, to someone who took a chance on them. The software engineers, cybersecurity analysts and infrastructure specialists on our teams didn’t arrive fully formed and ready to perform. Someone hired them, trained them and gave them room to grow. That’s worth remembering now, because the tech […]
Modernization without disruption: Rethinking the rip-and-replace mindset
I’ve seen organizations reach a point in a modernization program where the technology itself is no longer the biggest risk. A decision was made for a full rip-and-replace. The new environment is ready. The migration plan has been tested. The business case has been approved. But the team responsible for delivering it is also responsible […]
Where AI agents are showing real IT savings
Many IT leaders still struggle to find ROI when deploying AI agents at scale, but a few IT sweet spots are emerging as use cases that can provide CIOs tangible cost relief. Rhonda Baldwin, CIO at LaunchDarkly, says coding agents and service desk agents are helping the SaaS provider cut IT costs. “Coding agents increase […]
AI won’t replace CIOs. It will expose the ones who can’t lead people
In one stretch last year, several executives at the same level in one organization each told me, separately, that the hardest part of their job was talking candidly to each other. Each had spent 15 to 25 years in technology, and none of them was struggling with the technology. I’ve coached more than 1,000 technology […]
What separates true enterprise leaders from strong tech execs
New technology executives often discover the skills that made them successful early in their careers can be the very things that limit their success as a CIO, particularly as the scope, complexity, and expectations of the role expand. Few leaders understand that evolution better than AlTi Global CTO Phil Dundas, my recent guest on the […]
Building an enterprise AI benchmark changed how I evaluate AI
I spent the early part of my career building database systems, managing Oracle’s storage engine group and later helping build Aster Data. That work taught me to watch the gap between benchmark results and production behavior. When the Transaction Processing Performance Council (TPC) was formed in 1988, it was because vendors, customers and researchers lacked […]
OpenAI bets enterprises are ready to delegate real work to autonomous agents
OpenAI says true agentic AI has finally arrived, pushing beyond the trivial capabilities of early-stage virtual assistants. This week at OpenAI Dev Day, the company introduced Dots, which CEO Sam Altman described as “remarkably capable, always-on” agents powered by GPT‑6 Astra. Dots have their own cloud computer, can be accessed in ChatGPT, Slack, or Teams, […]
CIO 100 Leadership Live Boston: Agentic AI pushes CIOs toward continuous enterprise reinvention
BOSTON — Business leaders are looking beyond a single-minded focus on artificial intelligence and the returns generated by individual agents as they confront the broader challenge of continuously reinventing their organizations around what emerging technologies make possible. This shifting mindset emerged during CIO 100 Leadership Live Boston, where discussions began with the human dimensions of […]
Police Arrest 16-Year-Old Suspected of Running KillSec, Seize Ransomware Leak Site and Servers
Police in Spain have arrested a 16-year-old whom investigators suspect of running the KillSec ransomware group. KillSec is accused of stealing data from organizations and threatening to publish it on its leak site unless they paid. The 16-year-old was one of 3 people arrested on September 30, when police also took control of that site. […]
ThreatsDay: AI-Powered Zero-Day Chain, 543K Live Secrets, Model Inspection RCE and 13 More Stories
This week, the useful words are boring ones: inspect, cache, compile, store, trust. Each sounds harmless. Each can become an attack path when a system does a little more than people expect. A model check can run code. A cache can mix up requests. A public secret can stay useful for years. That is the […]
‘A treasure trove of information:’ Cybersecurity specialist says sensitive McMinnville records exposed online
KOIN in Oregon reports: Three clicks. That’s all Chuck Dornon said it took to reach private McMinnville records that should never have been public on the dark web. “Anything and everything that the city’s done is out there,” Dornon said. “This is probably the easiest form of information I’ve come across in a breach.” The… […]
WordPress Backdoor Rebuilds Itself After Cleanup Using Files, Database, and Shared Memory
Cybersecurity researchers have shed light on a WordPress compromise in which threat actors deployed multiple persistence mechanisms to ensure that the final payload kept returning without having to infect the site again. The backdoor has been codenamed SC after the “SC_” markers present in the injected content. Sucuri has described the malware as a “self-healing […]
Google makes Gemini 4 AI model available to a trusted few
Google has unveiled a new frontier AI model after months of delay. Gemini 4 Argon is designed to handle complex, long-horizon workloads spanning software engineering, enterprise knowledge work such as legal and financial analysis, and cybersecurity. But only a few organizations can get their hands on it for now. Argon is “rolling out to a […]
Cisco SD-WAN Manager hit by zero-day admin access attack
Cisco’s SD-WAN management software has been letting some attackers walk through an authentication check without having to prove who they are. The company says it has now fixed the flaw that was allowing it. The affected platform, Cisco Catalyst SD-WAN Manager, is used to configure and operate software-defined network deployments. Cisco said in an advisory […]
Armatura LLC Armatura One
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to gain unauthorized access to the database, execute arbitrary code on the host with the highest level of privilege, or gain control of the physical access-control system. The following versions of Armatura LLC Armatura One are affected: Armatura One <4.7.2 (CVE-2023-46604, CVE-2026-94591, CVE-2026-94592, […]
Meari IoT Cloud Platform OpenAPI Service
View CSAF Summary Successful exploitation of these vulnerabilities could allow attackers to manipulate device configurations, trigger unauthorized behaviors, and access sensitive information such as device credentials, owner details, and network data without proper authorization. The following versions of Meari IoT Cloud Platform OpenAPI Service are affected: IoT Cloud Platform OpenAPI Service vers:all/* (CVE-2026-101104, CVE-2026-96613) CVSS […]
Monta monta.app
View CSAF Summary Successful exploitation of these vulnerabilities could enable attackers to gain unauthorized administrative control over vulnerable charging stations or disrupt charging services through denial-of-service attacks. The following versions of Monta monta.app are affected: monta.app vers:all/* (CVE-2026-95102, CVE-2026-97363, CVE-2026-97212, CVE-2026-93474) CVSS Vendor Equipment Vulnerabilities v3 9.4 Monta Monta monta.app Missing Authentication for Critical Function, […]
Johnson Controls EasyIO Neo Series EC and CW Controllers
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to gain access to sensitive information that could be used to conduct further attacks against the system. The following versions of Johnson Controls EasyIO Neo Series EC and CW Controllers are affected: EasyIO Neo Series EC Controllers V3.3b63 (CVE-2026-64892) EasyIO Neo Series EC […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-104286 Fortinet FortiMail Path Traversal Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based […]
ABB Protection and Control IED Manager PCM600
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to escalate privileges or overwrite files. The following versions of ABB Protection and Control IED Manager PCM600 are affected: Protection and Control IED Manager PCM600 <=2.14 (CVE-2026-15952, CVE-2026-15953) CVSS Vendor Equipment Vulnerabilities v3 6.4 ABB ABB Protection and Control IED Manager PCM600 Incorrect […]
Johnson Controls EasyIO Neo Series EC and CW Controllers
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker tointercept and read sensitive information, including credentials andsession data. The following versions of Johnson Controls EasyIO Neo Series EC and CW Controllers are affected: EasyIO Neo Series EC Controllers V3.3b62 (CVE-2026-64893) EasyIO Neo Series EC Controllers V3.3b63 (CVE-2026-64893) EasyIO Neo Series CW Controllers […]
CISA Malcolm
View CSAF Summary The following versions of CISA Malcolm are affected: Malcolm CVSS Vendor Equipment Vulnerabilities v3 8.8 CISA CISA Malcolm Improper Neutralization of Input During Web Page Generation (‘Cross-site Scripting’), Improper Neutralization of Special Elements used in an OS Command (‘OS Command Injection’), Improper Limitation of a Pathname to a Restricted Directory (‘Path Traversal’), […]
Suspected State Hackers Exploited Citrix NetScaler for Weeks. 50,000 Devices May Still Be Exposed.
Datawater reports: Two critical NetScaler zero-days, CVE-2026-88771 and CVE-2026-88772, were used against organizations worldwide before a patch existed. CISA’s deadline is today. Patching alone will not tell you whether you were already breached. Threat level: Critical What: Two unauthenticated remote-code-execution flaws in Citrix NetScaler ADC and NetScaler Gateway, both CVSS 9.5. Status: Exploited as zero-days…. […]
How Financial Services Companies Can Modernize Their Software Supply Chain
Every security leader at a bank, insurer, or asset manager has had a version of this conversation: Security wants to eliminate a class of vulnerabilities. Engineering explains what it would take to upgrade the platform where they live. Somebody prices out the regression testing. Somebody else raises the change-freeze calendar. The finding gets an exception, […]
Zammad Zero-Days Exploited in AI-Powered DIVD Hack
The flaws were chained to hijack sessions, achieve remote code execution, and elevate privileges to root. The post Zammad Zero-Days Exploited in AI-Powered DIVD Hack appeared first on SecurityWeek.
500,000 Active Credentials Left Exposed on GitHub
Roughly 200,000 of the credentials were exposed after GitHub enabled push protections by default. The post 500,000 Active Credentials Left Exposed on GitHub appeared first on SecurityWeek.
Cisco Patches Exploited Catalyst SD-WAN Zero-Day Vulnerability
The flaw could allow remote, unauthenticated attackers to access vulnerable appliances with administrative privileges. The post Cisco Patches Exploited Catalyst SD-WAN Zero-Day Vulnerability appeared first on SecurityWeek.
Google Launches Gemini 4 Argon With Guardrail-Free Access for Vetted Defenders
The company says its new frontier AI model found a critical vulnerability in software used by hospitals worldwide. The post Google Launches Gemini 4 Argon With Guardrail-Free Access for Vetted Defenders appeared first on SecurityWeek.
FTC is Investigating OpenAI and Anthropic Over Possible Risks to Consumers
An FTC spokesperson confirmed the investigation but declined further comment. The post FTC is Investigating OpenAI and Anthropic Over Possible Risks to Consumers appeared first on SecurityWeek.
Google: AI Is Changing the Pace and Profile of Vulnerability Discovery
Google’s analysis found that AI-discovered vulnerabilities are more likely to enable remote code execution. The post Google: AI Is Changing the Pace and Profile of Vulnerability Discovery appeared first on SecurityWeek.
WatchGuard Patches Critical Fireware OS Code Injection Vulnerability
WatchGuard has rolled out patches for 15 code execution, DoS, authorization, and path traversal bugs in Fireware OS. The post WatchGuard Patches Critical Fireware OS Code Injection Vulnerability appeared first on SecurityWeek.
Government, Finance Orgs Targeted in Weeks-Long NetScaler Zero-Day Attacks
Several security firms have confirmed seeing exploitation of the NetScaler vulnerabilities CVE-2026-88771 and CVE-2026-88772. The post Government, Finance Orgs Targeted in Weeks-Long NetScaler Zero-Day Attacks appeared first on SecurityWeek.
Chrome, Firefox Updates Patch Over 100 Vulnerabilities
Some of the flaws could allow remote attackers to execute arbitrary code or escape the browser sandbox. The post Chrome, Firefox Updates Patch Over 100 Vulnerabilities appeared first on SecurityWeek.
Treasury Blacklists Most-Wanted ATM Malware Developer and His Network
The US government continues its crackdown on Tren de Aragua over its ATM jackpotting scheme. The post Treasury Blacklists Most-Wanted ATM Malware Developer and His Network appeared first on SecurityWeek.
Philip Gommers Comment On Regulatory Notice 26-15
Philip Gommers Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 06:45 Philip Gommers Philip Gommers <philipgommers@gmail.com> Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File Philip Gommers_26-15_9.24.2026.pdf
OpenAI Disrupts Reasoning Extraction Campaign Linked to Moonshot AI Associates
OpenAI on Wednesday said it identified and disrupted a coordinated distillation campaign that was designed to illicitly extract protected reasoning from its artificial intelligence (AI) models. A “core cluster of the activity,” going back to the first week of July, has been attributed to individuals associated with Moonshot AI, a Chinese AI company based in […]
E. Lukas Comment On Regulatory Notice 26-15
E. Lukas Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 06:40 E. Lukas Erich Lukas <erich.lukas@hotmail.com> Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File E. Lukas_26-15_9.24.2026_Redacted.pdf
Anonymous Comment On Regulatory Notice 26-15
Anonymous Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 06:37 Anonymous quan19@yahoo.com Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File Anonymous_qn_26-15_9.24.2026_Redacted.pdf
Rick Comment On Regulatory Notice 26-15
Rick Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 06:33 Rick Richard Desjardins <rickdesjardins@me.com> Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File Rick_26-15_9.24.2026_Redacted.pdf
Mike Henslin Comment On Regulatory Notice 26-15
Mike Henslin Comment On Regulatory Notice 26-15 fnrw-backend Thu, 10/01/2026 – 06:33 Mike Henslin Mike Henslin <mike@groundtechmn.com> Regulatory Notice 26-15 Core Official Date Thu, 10/01/2026 – 12:00 Comment File Mike Henslin_26-15_9.24.2026.pdf
CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a critical authentication bypass flaw impacting Cisco Catalyst SD-WAN Manager to its Known Exploited Vulnerabilities (KEV), following reports of active exploitation. The vulnerability, tracked as CVE-2026-76504 (CVSS score: 9.8), could allow an unauthenticated, remote attacker to access an affected system with
Why AI agents are like the dog that pushed kids into the Seine
There is an interesting story about a French dog on the banks of the Seine river that helps us understand misbehaving AI agents. The dog is trained to save children from drowning. He succeeds and is rewarded, becoming an overnight sensation. He saves another child a week later. Not long after, someone witnesses the dog […]
Google Rolls Out Gemini 4 Argon to Trusted Cyber Defenders, Plans Guardrail-Free Version
Google on Wednesday announced its latest frontier artificial intelligence (AI) model, Gemini 4 Argon, that it said is being rolled out to a set of trusted cyber defenders through its Fairwind Program. “It delivers frontier performance in complex workflows across real-world software engineering, enterprise knowledge work like legal and finance, and cybersecurity defense,” Koray Kavukcuoglu,
Apple CoreGraphics PoC Emerges as WhatsApp PDF Checks Hint at Possible Delivery Path
Security researchers have published the first public proof-of-concept for CVE-2026-86950, an Apple CoreGraphics flaw Apple says may have been used in attacks against specific targeted individuals. The trigger is a malicious PDF with a crafted embedded font that crashes unpatched iPhones and Macs. The code causes a crash, not an execution error. Turning the memory […]
ScreenConnect Client (Ab)used by Attackers, (Thu, Oct 1st)
Threat Actors do not always use top-notch techniques or very complex malware to perform their attacks. Sometimes, they just abuse of existing applications…
Bitget Confirms Third-Party Zero-Day Behind $387.5 Million Cryptocurrency Theft
Cryptocurrency exchange Bitget on Wednesday confirmed that attackers who stole $387.5 million last week exploited a zero-day flaw in third-party security products, citing ongoing investigation findings from SlowMist. “Their investigation identified malicious activity involving third-party security products, including a zero-day vulnerability, and recovered a customized tool used by the attacker
MetaMask Security Incident Prompts Exit of Affected Ethereum Validators
MetaMask on Thursday said it’s responding to what it described as an “ongoing security incident” impacting part of its infrastructure. “We are actively addressing and remediating the issue internally, in coordination with external partners and security advisors,” the software cryptocurrency wallet maker said. “At this time, we have identified no immediate threat to MetaMask wallets.” […]
Citrix NetScaler Post-Exploitation Payload Creates Superuser, Maps Web Shell to CSS-Like URLs
Threat actors have been observed exploiting a critical pre-authentication command injection vulnerability in Citrix NetScaler ADC and NetScaler Gateway to drop web shells and attempt theft of configuration data. LevelBlue’s Threat Hunt Operations & Research (THOR) team, which analyzed the exploitation activity across multiple customer environments, said it identified malicious NetScaler
ISC Stormcast For Thursday, October 1st, 2026 https://isc.sans.edu/podcastdetail/10118, (Thu, Oct 1st)
Post Content