Does AI actually save employees time? Data is contradictory
It’s early days for AI-assisted work, and sentiments are mixed about its benefits: Does AI actually bring value and save employees time, or does it bog them down and add unnecessary activities? Data from ActivTrak seems to vacillate between those two potential realities: The latest research from the productivity tracking software company says employees who […]
7 sure-fire ways to blow your AI budget
CIOs have always felt pressure to deploy emerging technologies rapidly. Implementation brings challenges, including calculating and measuring upfront investment costs. Deploy too quickly, and when the hype fades, many IT departments are left with a costly architecture to support, security gaps, and operational issues. The same trend is happening with AI. Many CIOs procured enterprise-wide […]
Gen Z is driving the death of the legacy helpdesk ticket
Much has been made of Generation Z’s supposed inability to adequately conform to modern-day corporate culture. A recent Business Insider article on Gen Z (born 1997–2012) workplace readiness contains some damning statistics. The piece cites a 2024 poll of nearly 1,000 business leaders, 75% of which described some or all of the recent graduates they […]
UK Cyber Chief Says the UK Will Face AI Cyberattacks on Critical Infrastructure by 2028
The U.K. will likely face AI cyberattacks on its critical infrastructure by 2028 as criminals and states, including China and Russia, increasingly use AI in their cyber activity. The post UK Cyber Chief Says the UK Will Face AI Cyberattacks on Critical Infrastructure by 2028 appeared first on SecurityWeek.
Google Dismantles XCPE Botnet of 1.3 Million Android Devices
The botnet was created and operated for financial gain by Android OEM/ODM Videostrong Technology. The post Google Dismantles XCPE Botnet of 1.3 Million Android Devices appeared first on SecurityWeek.
NATO’s Crossed Swords Exercise Brings AI Agents Into Cyber Operations Training
The NATO CCDCOE exercise in Estonia introduces AI agents and OpenAI Daybreak into joint cyber and kinetic operations training. The post NATO’s Crossed Swords Exercise Brings AI Agents Into Cyber Operations Training appeared first on SecurityWeek.
Over 100 European Stores Hit as Supermarket Fridge Attacks Return
Attackers again tampered with internet-exposed refrigeration controllers, this time at stores in Belgium, Sweden, Ireland and beyond. The post Over 100 European Stores Hit as Supermarket Fridge Attacks Return appeared first on SecurityWeek.
Cybersecurity M&A Roundup: 37 Deals Announced in October 2026
Significant cybersecurity deals were announced by Absolute Security, Aikido, Anthropic, Cohere, Hex-Rays, and Proofpoint. The post Cybersecurity M&A Roundup: 37 Deals Announced in October 2026 appeared first on SecurityWeek.
Florida Student Aid Website Hack Puts Data of 4.9 Million People at Risk
The Florida Department of Education says SSNs and other personal data may have been exposed in a breach of its financial aid website. The post Florida Student Aid Website Hack Puts Data of 4.9 Million People at Risk appeared first on SecurityWeek.
Revolve Data Breach Impacts at Least 200,000 People
Hackers accessed its online shopping platform and stole customers’ personal and payment card information. The post Revolve Data Breach Impacts at Least 200,000 People appeared first on SecurityWeek.
Google Introduces $250,000 Root-in-Cloud Bug Bounty Reward
The top payout is for high-impact architectural research demonstrating full administrative control. The post Google Introduces $250,000 Root-in-Cloud Bug Bounty Reward appeared first on SecurityWeek.
Malicious Claude Code Extension Served in Cursor Supply Chain Attack
The extension performed host reconnaissance and attempted to create a reverse SSH tunnel. The post Malicious Claude Code Extension Served in Cursor Supply Chain Attack appeared first on SecurityWeek.
Armed with AI, hackers target endpoint security blind spots, raising stakes for CISOs
A China-linked hacking group’s use of AI agents to identify security weaknesses during a global espionage campaign is raising concerns about whether enterprises can detect gaps in their defenses before automated attacks exploit them. CrowdStrike reported that the group, tracked as VAPOR PANDA, used an AI-powered penetration testing framework called ARTEX to target more than […]
Hackers Exploit BTCPay Server Flaw to Steal Bitcoin and Litecoin From Hot Wallets
BTCPay Server, a self-hosted, open-source cryptocurrency payment processor, has urged users to install the latest version of its software in response to reports of Bitcoin and Litecoin being stolen from hot wallets on instances running older versions. “Our investigation found that these attacks targeted servers running BTCPay Server 2.4.1 (released on 23 July 2026) or […]
67% of security leaders say their teams struggle to meet business needs
AI, identity-based attacks, and expanding digital operations are putting pressure on already overstretched cybersecurity teams. Security vendor Barracuda’s Cybersecurity Skills Gap report also found that security teams are struggling to keep pace with expanding responsibilities. The vast majority of the 2,000 IT and security decision-makers surveyed report cybersecurity skills gaps. In particular, the most common […]
Synology NAS Devices Targeted in Ransomware Attacks Exploiting Patched DSM Flaw
Synology is urging customers to update the DiskStation Manager (DSM) software powering its Network Attached Storage (NAS) devices following ransomware attacks. The Taiwanese vendor said it observed threat actors exploiting a vulnerability patched in December 2024 to target devices running outdated versions of DSM. “These attacks aim to encrypt data and extort ransom,” it said […]
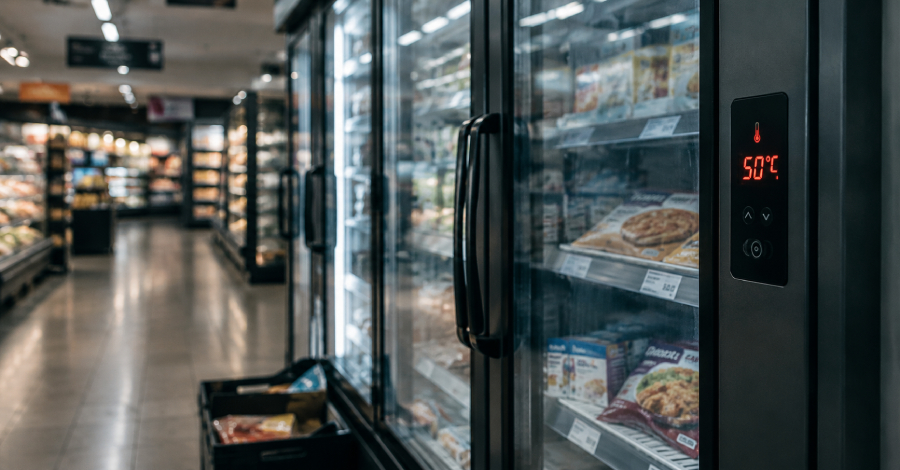
New Wave of Refrigeration Cyberattacks Hits Supermarkets Across Europe, Forcing Stores to Pull Food
Attackers remotely changed the settings on refrigeration controls at supermarkets in Belgium, Sweden, Estonia and other European countries overnight into Monday, November 2, warming fridges and freezers. No chain reported more than several dozen affected stores, and some had to throw away chilled and frozen food or take it off the shelf. Danfoss, a Danish […]
Attackers Exploit Critical Siemens IoT2050 Flaw to Plant Remote Command Backdoors
A maximum-severity security flaw impacting Siemens SIMATIC IoT2050 Advanced devices has come under active exploitation, VulnCheck has revealed. The vulnerability, tracked as CVE-2026-58115 (CVSS score: 10.0), is a case of missing authentication for a critical function that could be exploited by an unauthenticated remote attacker to run arbitrary code. “SIMATIC IoT2050 Advanced devices running
Attackers Target Unpatched CryptoPayment Gateway Flaw That Can Expose Wallet Credentials
Threat actors are attempting to exploit an unpatched maximum-severity security vulnerability in the CryptoPayment Gateway WordPress plugin, according to findings from Defused Cyber. The vulnerability in question is CVE-2026-81648, which carries a CVSS score of 10.0. Successful exploitation of the flaw could permit unauthenticated users to delete arbitrary files on the server and extract
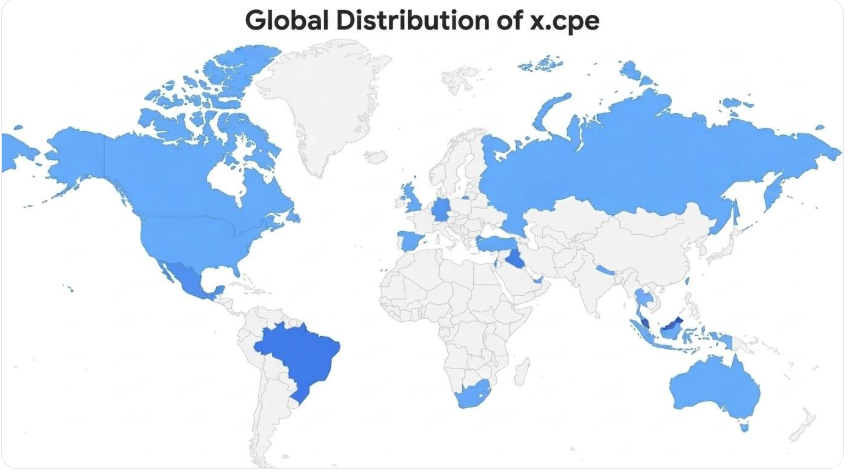
Tech Firms Dismantle Botnet That Turned 1.3M TV Boxes Into Proxies
Google said today it worked with industry partners to dismantle a botnet made up of more than 1.3 million Android TV set-top boxes that ship with malicious software which secretly rents the user’s Internet connection out to strangers and conducts advertising fraud. Experts involved in the takedown say the action is likely to sever the […]
ISC Stormcast For Tuesday, November 3rd, 2026 https://isc.sans.edu/podcastdetail/10162, (Tue, Nov 3rd)
Post Content
European supermarkets that failed to act after French freezer attack are now feeling the heat
Just a couple of weeks after a cyberattack on French supermarket refrigeration systems resulted in spoiled food, and even some fires, retailers in Belgium, Ireland, Sweden, Finland, and Estonia were hit with nearly-identical attacks on Monday. The mid-October attack prompted an advisory from the French Computer Emergency Response Team (CERT-FR) recommending that organizations disconnect any […]
Syrian Man Sentenced for Wide-Ranging Hacking Conspiracy Conducted on Behalf of the Bashar Al Assad Regime
Ahmad Umar Agha (also known as Th3Pr0) had spent more than a decade as a fugitive for targeting of Western media entities, businesses, NGOs, and U.S. and allied government entities October 29 – Today a federal district court in the Eastern District of Virginia sentenced Ahmad Umar Agha to 42 months in prison for his…
A Defense Contractor Gave Their Personal AI Agent Access to a Secure Pentagon System
Vittoria Elliott reports: Earlier this year, sources tell WIRED, a contractor caused a security incident at the Department of Defense by connecting a secure centralized system used by multiple intelligence agencies to their personal account for Claude Code, Anthropic’s AI coding agent. It appears that the agent used by the contractor, who is employed by…
Hackers hit UNM hospital, then apologize and offer patients $2,500. In a new statement, they reveal more about the incident.
In more than 20 years of blogging about breaches, DataBreaches has never seen ransomware threat actors offer monetary compensation to patients affected by their attack. We have seen threat actors regret hitting a hospital or a facility providing direct patient care and then offer them a free decryptor and drop the ransom demands, but this…
HHS’ Office for Civil Rights Settles Ransomware Investigation of Lehigh Valley Health Network
DataBreaches.net previously covered the 2023 Lehigh Valley Health Network breach by AlphV (aka “BlackCat”). The breach garnered a lot of public attention when the threat actors crossed a line by posting nude pictures of patients on their leak site. In 2024, patients settled civil litigation for $65 million. Now HHS has settled its own charges…
UK: Second Liverpool hospital investigates staff over breach of Southport attack patient records
ITV reports yet more insider snooping by hopsital employees in the wake of the Southport terror attack: A second hospital in Liverpool is carrying out an investigation into two potential instances of staff accessing medical records connected with the Southport terror attack. The cases were detected at Liverpool Heart and Chest Hospital as part of…
Supermarket freezers across Europe hit by second suspected cyber-attack
The Guardian reports that supermarket freezers across Europe have been hit by a second suspected cyber-attack, with chains in Sweden, Belgium and Luxembourg reporting fridge temperatures rising overnight, similar to the hack of French stores last month. For more country-specific reports: AFP reports on the attacks in Belgium,SiliconRepublic reports on 13 SuperValu stores hit in…
JPN: Suntory Holdings says personal data of around 100,000 people leaked
Kyodo News reports: Leading beverage manufacturer Suntory Holdings Ltd. on Monday joined a growing list of firms reporting personal data leaks, saying information relating to around 100,000 people, including employees, was leaked following unauthorized access to an external cloud service used by the group. Suntory said it has not confirmed any misuse of the information…
Hong Kong privacy watchdog investigates data leaks linked to major airlines and retailers
Dickson Tam reports: The Office of the Privacy Commissioner for Personal Data said it has received multiple notifications of data breaches involving Hong Kong Airlines, Cathay Pacific, Malaysia Airlines, as well as electronics retailers Yoho Hong Kong and Broadway. As at 30th October, the authority had logged 51 complaints and 48 enquiries related to these…
CT: Killingly Public Schools – Notice of Data Incident
Killingly Public Schools (“KPS”), a school district located in Killingly, Connecticut, was the victim of a recent data privacy incident involving certain personally identifiable information (“PII”). What Happened: In October 2025, KPS detected a disruption to its computer network. Upon learning of the activity, KPS took immediate action to secure its systems which included taking…
KR: HYBE data breach exposes employee medical records, financial details
Lee Hae-rin reports: HYBE, the music agency behind K-pop group BTS, disclosed a cyberattack that exposed personal information of current and former employees and business partners, including resident registration numbers, credit card numbers and medical records. In an apology posted on its website, Oct. 18, the company said an internal security inspection detected unauthorized access…
SR-FINRA-2026-024
SR-FINRA-2026-024 DixonR Mon, 11/02/2026 – 17:03 Financial Industry Regulatory Authority, Inc. (“FINRA”) is filing with the Securities and Exchange Commission (“SEC” or “Commission”) a proposed rule change to (1) amend the By-Laws of the Corporation, the By-Laws of FINRA Regulation, Inc. and the Plan of Allocation and Delegation of Functions by FINRA to Subsidiaries to […]
24-01059.pdf
24-01059.pdf Anonymous (not verified) Mon, 11/02/2026 – 16:37 Case ID 24-01059 Forum FINRA Document Type Award Claimants Jefferies LLC Respondents Dustin Tyner Cantor Fitzgerald & Co. Neutrals Gene M. Bauer Daniel Robert Tereau Christine Neylon O’Brien Hearing Site Boston, MA Award Document 24-01059.pdf Documentum DocID 52efd8c9 Award Date Official Mon, 11/02/2026 – 12:00 Related Content […]
Salesforce acquires Rune Technologies to add offline capabilities to Missionforce
Salesforce is in the process of acquiring US-based defense-tech startup Rune Technologies to add offline capabilities to Missionforce, its Agentforce avatar for national security, defense, aerospace, and government agencies. The startup’s TyrOS platform will be used to extend Missionforce into frontline military logistics, enabling deployed units to forecast supply requirements, optimize resource allocation, and make […]
13 key questions shaping CIOs’ 2027 IT agendas
With 2027 quickly looming, IT leaders should soon be finalizing their objectives for the new year, one certain to be rife with many unknowns if 2026 is any indication. This year began with the call for a pivot from AI pilots to AI ROI, but questions around AI governance and accountability quickly took center stage […]
Collaboration: every CIO’s most underrated competitive advantage
In Foundry’s 2026 State of the CIO survey, 83% of CIOs say their role is becoming more of a hybrid to lead both business and tech initiatives, rather than simply manage IT. As the two become more inseparable, the CIOs who see collaboration as a competitive advantage are putting daylight between them and those who see […]
The middle layer will make or break enterprise AI agents
The hype around AI agents and the models that power them is warranted. But while they can give organizations a real competitive advantage, in reality, how much value they deliver ultimately depends on something much less glamorous: the middleware and integrations that connect agents to systems across enterprise workflows. Enterprises have used AI in various […]
The next digital twin isn’t of a machine, it’s of your business
The digital twin concept earned its credibility in engineering. Its origins trace to a 2002 University of Michigan presentation in which Michael Grieves described a “Mirrored Spaces Model”: a virtual system holding the information about a physical one, linked to it throughout its life. For example, a jet engine manufacturer builds a precise virtual replica […]
⚡ Weekly Recap: Critical CVEs, Linux DDoS Botnet, Device-Code Phishing, Android Spyware and More
Some attacks this week didn’t need much of a trick. A fake support call, a trusted extension, a shared link, or a device with no password. Small things that people barely think about. Yet each was enough to cause serious trouble. Then there were the bigger messes. Billions stolen, hidden networks of hacked devices, poisoned […]
Google Disrupts 1.3 Million-Device Android Botnet, Says TV Box Maker Sold Criminal Access
A botnet of more than 1.3 million Android devices, mostly TV set-top boxes, lost control of its servers in late October in a takedown led by Google. Google says it is highly confident that device maker Videostrong intentionally put a backdoor in the boxes and sold access to criminals. They used the boxes for ad fraud […]
26-00376.pdf
26-00376.pdf Anonymous (not verified) Mon, 11/02/2026 – 10:00 Case ID 26-00376 Forum FINRA Document Type Award Claimants Avner Dei Respondents Independent Financial Group, LLC. Neutrals Sandra J. Mullings Daniel Louis Cevallos Diane S Steiner Hearing Site New York, NY Award Document 26-00376.pdf Documentum DocID bc95560a Award Date Official Fri, 10/30/2026 – 12:00 Related Content Off […]
Mutipath TCP: Use and Detection, (Mon, Nov 2nd)
Last week, an often-ignored TCP option, introduced in 2020, made the news due to a new vulnerability in Linux’s implementation (RFC 8684, CVE-2026-98432)
DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment
Cybersecurity researchers have disclosed details of a cyber espionage campaign targeting Israel and the Kurdistan Region of Iraq by an Iran state-aligned threat actor between August and October 2026. According to a report published by Dream Research Labs, the campaign has led to the compromise of a high-profile individual in Israel, along with additional compromises […]
A compromised DevOps laptop caused the $6.3B Binance breach
Cryptocurrency Exchange Binance blamed a compromised DevOps laptop for the loss of $6.3 billion in cryptocurrency last week, adding that it will now cover any losses faced by its customers. “Binance will cover all losses from the Secure Assets Fund for Users (SAFU) and the company’s funds,” the world’s largest cryptocurrency exchange said in an […]
Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers
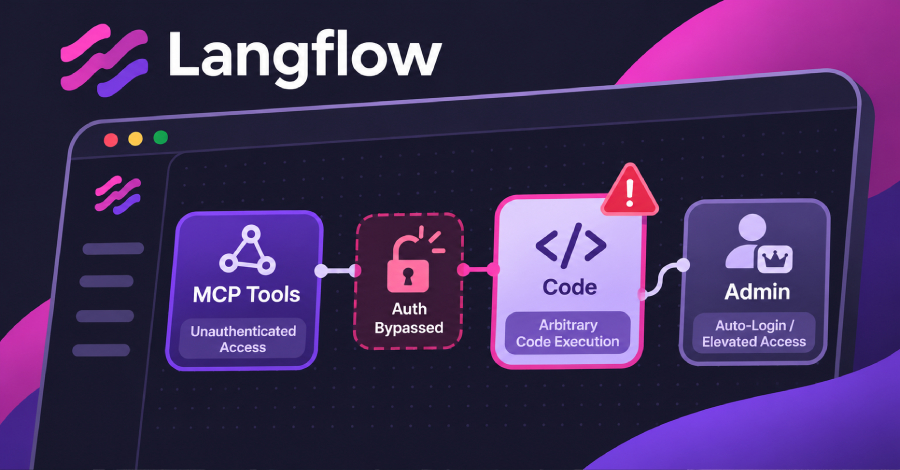
Two critical flaws in Langflow could let a remote attacker with no account bypass authentication or run arbitrary code, IBM said last week. Langflow is an open-source tool for building AI agents and workflows, and its vulnerability reports go to IBM. Every release from 1.0.0 through 1.12.8 has the flaws, and the only fix is version 1.13.0. […]
Cursor removes malicious Claude Code extension after SSH backdoor attempt
A malicious version of Anthropic’s Claude Code extension distributed through the Cursor marketplace attempted to install a persistent Secure Shell (SSH) backdoor on developers’ machines, potentially giving attackers remote access to systems holding source code, credentials and other sensitive information. “Between about 2:27am PT and 1:35pm PT today, a maliciously modified version of Anthropic’s Claude […]
Is Your SOC Ready for AI Agents? A Maturity Check Before You Deploy
Forty percent of security teams now use AI every day, and another 56% are testing it. Only 4% have no plans to adopt it, according to Prophet Security’s State of AI in Security Operations 2026 survey of more than 250 CISOs, SOC leaders and practitioners. For the teams still testing, the next decision is whether […]
Polymarket Returns $3.9 Million to Traders as DebugBear Cites DNS Hijack
DebugBear says its DNS records were compromised via its domain registrar, and early findings show a single customer was targeted. The post Polymarket Returns $3.9 Million to Traders as DebugBear Cites DNS Hijack appeared first on SecurityWeek.
FBI Flags Over 600 Addresses Tied to North Korea’s Binance Heist
The FBI has officially pinned the $6 billion Binance hack on North Korea’s TraderTraitor as the attackers launder the stolen crypto. The post FBI Flags Over 600 Addresses Tied to North Korea’s Binance Heist appeared first on SecurityWeek.
Ivanti Patches Two More Zero-Days Exploited in Connect Secure Attack Chain
CISA has added CVE-2026-111357 and CVE-2026-118527 to its KEV catalog after the Ivanti VPN flaws were chained in zero-day attacks. The post Ivanti Patches Two More Zero-Days Exploited in Connect Secure Attack Chain appeared first on SecurityWeek.
Northstar Security Exits Stealth With $7M to Expose Toxic Risk Combinations
The startup maps how identities, assets and vulnerabilities connect, and uses AI agents to find and fix risky combinations of issues. The post Northstar Security Exits Stealth With $7M to Expose Toxic Risk Combinations appeared first on SecurityWeek.
Chainalysis Discloses Data Breach Following AI-Driven Cyberattack
The attackers used offensive agentic techniques to access the company’s systems and internal tools. The post Chainalysis Discloses Data Breach Following AI-Driven Cyberattack appeared first on SecurityWeek.
Why do we keep testing employees for yesterday’s phishing attacks
“Yesterday’s price is not today’s price,” a phrase Fat Joe popularized in 2021, reminds us that what worked yesterday may not deliver the same value today. In cybersecurity, this matters when we continue to assess employees against familiar phishing techniques while attackers use AI to craft more convincing, personalized messages. Having conducted multiple phishing simulations […]
Who approves the files that control your AI coding assistant?
A pull request adds a helpful setup step for an AI coding assistant. No application source changes. The description calls it a developer-experience improvement, and the reviewer sees a short configuration file beside some Markdown instructions. Before approving it, the reviewer needs to answer a different question: what will this change allow to run on […]
What a security strategy that survives 2027 looks like
Equifax CISO Jeremy Koppen sees the same dynamics most security chiefs are facing: hackers on the one side using AI to perform more sophisticated attacks at unprecedented speed, and defenders on the other adopting AI to match that volume and velocity. “AI is changing the pace on both sides,” he says. “Attackers are using it […]
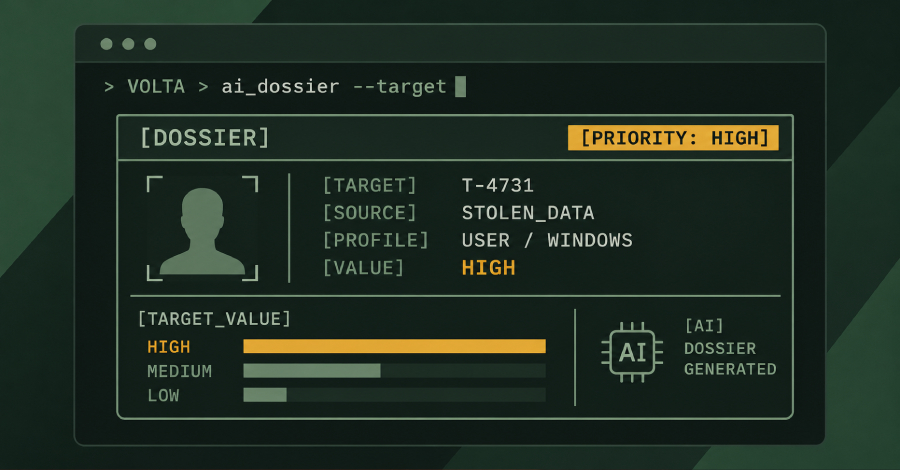
New VOLTA Infostealer Uses Claude, Gemini, and Kimi AI to Rank Victims by Financial Value
Cybersecurity researchers have discovered a new Windows infostealer malware called VOLTA-AUTODOXER (aka VOLTA) that makes use of a large language model (LLM) to rank a victim’s stolen data by their monetization value. Like other typical stealer families, VOLTA is equipped to harvest passwords and cookies from Chromium-based web browsers; data from Outlook profiles and Slack […]
ISC Stormcast For Monday, November 2nd, 2026 https://isc.sans.edu/podcastdetail/10160, (Mon, Nov 2nd)
Post Content
Governing the agent workforce: New data on the next frontier of AI risk
In the fast-paced world of agentic AI, building agents and defending ROI is yesterday’s news. Today, the more pressing challenge is managing and governing the exploding workforce of agents to mitigate growing enterprise risk. The problem intensifies as AI agents move from advisory to more active roles. According to a survey of 200 IT and […]
Cadence Maestro puts domain-trained AI agents to work for chip design
Artificial intelligence has been part of semiconductor design for years, helping engineers optimize chip architectures for performance, power efficiency, silicon area and faster development. More recently, the industry has begun integrating large language models and AI agents into established electronic design automation (EDA) workflows. Now Cadence Design Systems is taking that approach further with its […]
Syrian Hacker Gets Prison Time in US After Over a Decade on the Run
A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities. The post Syrian Hacker Gets Prison Time in US After Over a Decade on the Run appeared first on SecurityWeek.
OneNote File Extraction, (Sun, Nov 1st)
Recently, I had to extract embedded files from a set of OneNote files (extension .one).
CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key
A critical flaw in Canonical’s LXD and MicroCloud let an attacker log in as a trusted client without holding that client’s private key. To do it, the attacker had to reach their HTTPS API over the network and have the trusted client’s public certificate. Once in, the attacker would act as that client, with access […]
Hackers Steal About $2.7 Million From Polymarket Traders via Hijacked DebugBear Script
Malicious code on the website of prediction market Polymarket sold some signed-in traders’ positions and moved their funds to the hackers on October 29. The code had replaced a page-speed script that the site loaded from an outside company. Polymarket says it is refunding about $2.7 million to 726 affected wallets. Blockchain records show crypto worth about $2.64 […]
FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist
The U.S. Federal Bureau of Investigation (FBI) has officially attributed the theft of more than $6 billion in virtual assets to TraderTraitor, a North Korea-aligned elite hacking group also tracked as Jade Sleet, Pressure Chollima, PUKCHONG, Slow Pisces, and UNC4899. The FBI, along with the U.S. Secret Service (USSS) and the Internal Revenue Service Criminal […]
NetamLoader Malware Targets Government Windows 10 Systems in Asia via .NET Injection
Cybersecurity researchers have disclosed details of what has been described as a “highly sophisticated infection chain” targeting government organizations in Asia. The activity, detailed by Kaspersky this week, targeted a custom Windows 10 build used exclusively by government entities in Asia and involves the deployment of a previously undocumented .NET assembly-loading framework codenamed