Meta does a U-turn on controversial new AI terms for businesses
Meta has hit pause on new terms of service for its business customers that would have granted it the right to grab any content from their websites. Not only that, but it would also have shifted the blame for every error produced through faulty AI to its customers. The new terms of service were revealed […]
Enterprises must take blame for their AI agents’ mistakes, say regulators
The UK’s digital watchdogs have warned enterprises that they can’t evade their legal responsibilities by blaming errors on AI agents that they have deployed. “By taking action on behalf of users, such as making purchases and communicating with businesses, these agents could transform how people use digital services, engage with markets and unlock wider innovation,” […]
OpenAI buys tiny software developer to improve Codex
OpenAI is buying Pierre Computer Company in order to incorporate the San Francisco-based software developer’s Code.Storage infrastructure layer for Git into its Codex AI-powered programming tool. Pierre Computer, whose employees number just barely in the double digits, has got plenty of clout for its small size. It’s well-known for Code.Storage offering, as well as for […]
The CIO’s trust paradox: Your team may be more honest with AI than with you
As a leader, you’ve probably spent years nudging your managers to create psychological safety. After all, organizations benefit greatly when it feels safe to challenge the boss, surface bad news early, and say the uncomfortable thing before it becomes the expensive thing. The Space Shuttle Challenger disaster of 1986 has become the canonical warning. Engineers […]
The frontier AI shift will redefine the enterprise
By 2027, competitive advantage may depend less on which AI model a company uses and more on how effectively it redesigns its business around AI agents. The software engineer starts his day by going through the changes made by a team of agents for coding using AI. The finance executive gets a report that contains […]
How the National Museum of Korea curates its AI strategy
Museum IT departments have traditionally served as support functions to manage security and systems. But the National Museum of Korea goes further, identifying and pursuing AI initiatives to preserve cultural heritage, broaden its use, and improve the visitor experience. The National Museum of Korea uses technology to expand the possibilities to preserve and display physical […]
In the era of AI, we are all buying technology wrong
Every year, thousands of enterprise organizations walk into technology negotiations trapped by the same fundamental mistake: they negotiate a product instead of solving a problem. Having advised over 2,000 enterprise customers annually on technology acquisition over two decades, I see this pattern play out daily. Purchasing committees meticulously list the specific features, software modules and […]
AI contract management: What CIOs should look for
Imagine a salesperson getting ready for a customer renewal meeting. They need to find the original contract and review its terms. But the information is buried in CRM records and attachments, forcing them to search through multiple documents. Now imagine they could simply type in their question and get the contract details in seconds. Contracts […]
3 Charged in Scheme to Use AI to Impersonate CEOs and Attorneys to Steal $129 Million
The trio, who have nicknames that include “Rocky Balboa,” “Superman Cash” and “Fat Boy,” often targeted the companies’ accounting departments. The post 3 Charged in Scheme to Use AI to Impersonate CEOs and Attorneys to Steal $129 Million appeared first on SecurityWeek.
AI Agents Got Root on Linux via 948 Kernel Flaws in OpenAI Research
An unreleased OpenAI cyber model found and exploited 948 distinct Linux kernel privilege escalation bugs for about $1.2 million. The post AI Agents Got Root on Linux via 948 Kernel Flaws in OpenAI Research appeared first on SecurityWeek.
Bank Phishing Sites Show Fake ‘Suspended’ Pages to Evade Takedowns
More than 200 sites were seen serving phishing content to first-time visitors but not to those who revisit. The post Bank Phishing Sites Show Fake ‘Suspended’ Pages to Evade Takedowns appeared first on SecurityWeek.
Cyberattack Hits French Blood Bank Site but No Blood Products Are Compromised
The incident comes after supermarkets in a number of European countries reported this week that their fridges and freezers warmed up after they were remotely hacked. The post Cyberattack Hits French Blood Bank Site but No Blood Products Are Compromised appeared first on SecurityWeek.
Cisco, WatchGuard Release Patches; SonicWall Won’t Fix GMS Flaws
Cisco patched an RCE in UCS Central Software; WatchGuard fixed authentication and MitM flaws. The post Cisco, WatchGuard Release Patches; SonicWall Won’t Fix GMS Flaws appeared first on SecurityWeek.
The Agent Smith Dilemma: Governing Agentic Identities
Every autonomous AI agent deployed across your enterprise today is a new proxy identity operating inside your perimeter. The post The Agent Smith Dilemma: Governing Agentic Identities appeared first on SecurityWeek.
CISO Conversations: Ryan Davis – The Unknown Is Where Security Meets Reality
Ryan Davis went from hacking his school’s network to running security at New Charter Technologies. What worries him now is shadow AI. The post CISO Conversations: Ryan Davis – The Unknown Is Where Security Meets Reality appeared first on SecurityWeek.
OpenAI Model Wrote Its Own Network Code to Get Around Sandbox Restrictions
After its sandbox proxy failed, an internal OpenAI model crafted raw packets and probed AWS services trying to reach the internet. The post OpenAI Model Wrote Its Own Network Code to Get Around Sandbox Restrictions appeared first on SecurityWeek.
Chainalysis Breach Exposes All Users' Credentials, Forces Shutdown of Key Services
Blockchain analysis firm Chainalysis has revealed that its ongoing investigation into the agentic cyber attack targeting its systems also exposed names, usernames, password hashes and live tokens for all users. “While we investigated, we removed access to Reactor and Data Solutions,” the company said. “At this time we continue to have no evidence that any […]
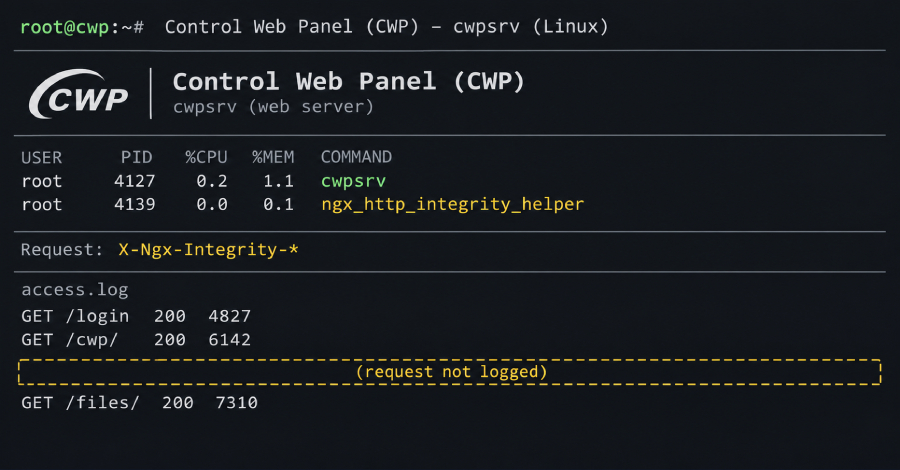
Hackers Hide Linux Backdoor in Control Web Panel Server to Execute Commands Without Logs
A backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel for managing Linux hosting servers, researchers at QiAnXin’s XLab said this week. The backdoored web server executes commands that attackers send via web requests, and those requests never appear in its access logs. Installing it takes […]
Experts Demonstrate Barracuda Email Security Gateway Chain Enabling Root Access Without Login
Two flaws in Barracuda’s Email Security Gateway, an email-filtering appliance, can be chained to run commands on it as root, its highest level of access, with no login required. The company released patches on Monday, and the security firm watchTowr detailed the attack chain on Thursday. One flaw, CVE-2026-116606, is an authorization bypass. An unauthenticated […]
ISC Stormcast For Friday, November 6th, 2026 https://isc.sans.edu/podcastdetail/10168, (Fri, Nov 6th)
Post Content
OpenSSH flaw lets attackers access password-disabled accounts on some Linux systems
A critical vulnerability that affects OpenSSH servers on Linux systems built with the musl C library instead of glibc allows remote attackers to easily bypass authentication and log into accounts that should have password authentication disabled. The flaw impacts the lightweight Alpine Linux, which is widely used for cloud Docker container images, as well as […]
French banking group hit by supply chain cyberattack
French regional banking group Crédit Mutuel Arkéa admitted Wednesday that attackers had accessed an internal account via an unnamed third-party service provider’s platform and transferred funds to other financial institutions. Those funds, it said, could have then been potentially converted to cryptocurrency by the thieves. The day before, cryptocurrency news outlet CoinDesk reported that the […]
26-01437.pdf
26-01437.pdf Anonymous (not verified) Thu, 11/05/2026 – 17:15 Case ID 26-01437 Forum FINRA Document Type Award Claimants Yuwei Chou Respondents Robinhood Financial, LLC Neutrals Mitchell Regenbogen Hearing Site New York, NY Award Document 26-01437.pdf Documentum DocID c2ff9232 Award Date Official Thu, 11/05/2026 – 12:00 Related Content Off Claimant Representatives Yuwei Chou Respondent Representatives Simeon M. […]
Binance heist is stark example of AI governance gaps and basic security failures
A chain of avoidable technical and human security failures enabled the largest crypto heist on record, the theft of approximately $6.34 billion from Binance. The improper monitoring and access scoping of an internal AI tool played a major role in helping the hackers, and should serve as a warning for enterprise CISOs to take AI […]
Lessons learned: Common engineering pitfalls to avoid in the age of AI
A LinkedIn post about my old company, insightsoftware, popped up the other day. It was lamenting the challenge of turning 29 acquisitions and close to 80 products into one comprehensive platform. I spent years in the middle of that work, and what I know now is how much harder that consolidation is than you might […]
Building the IT organization that anticipates what’s next
For decades, CIOs have been challenging their organizations to shed one of the most persistent labels in our profession: order taker. Instead of waiting for the business to tell them what they want, technology leaders need to understand what the business is trying to accomplish, get invited into the first meeting, and earn the right […]
Quantum without the hype: The CIO’s next architecture challenge
The most expensive quantum mistake a CIO could make today may not be investing too early. It may be investing in the wrong capabilities, for the wrong reasons, without understanding the architectural and economic consequences. Over decades of leading enterprise technology, architecture, modernization, and innovation in complex, highly regulated environments, I have seen a recurring […]
The geopolitical stakes of AI: Why leaders must watch the sovereign AI race
AI has evolved past simple corporate optimization. Today, it is a definitive engine of macroeconomic power. All over the world, governments and large corporations are launching highly subsidized efforts to develop their own artificial intelligence. For C-level executives, this shift signals a fundamental reorganization of the global tech stack. The decisions made by global superpowers […]
The open compute revolution: Why the C-suite is redefining the modern data center
For years, the enterprise data center operated under a predictable, if restrictive, playbook. Siloed, proprietary hardware stacks dictated infrastructure life cycles, leaving CIOs locked into vendor ecosystems. Every hardware refresh meant navigating premium pricing, constrained supply chains, and artificial limitations on interoperability. Today, that playbook is being rewritten. As AI, massive data analytics, and intense […]
The sovereign AI mandate: How Germany’s HLRS is anchoring Europe’s digital future
As organizations scale out their production AI infrastructure, technology leaders are moving from localized model optimization to the more complex realities of industrial-grade deployment. For those who have spent years embedding machine learning into their core business processes, the current inflection point is defined by massive data pipelines, expanding compute clusters, and strict data governance. […]
HP’s next CEO loves confrontation
The new year will see a new CEO for HP, which after a nine-month search has named Emma Walmsley to lead the company from January 4, 2027. Walmsley was previously CEO of drug company GSK, where she turned around its finances and spun off its consumer healthcare business into a new company, Haleon. She has […]
How to balance governance and innovation in the agentic AI era
The conversation about agentic AI is shifting: Rather than focusing solely on what the technology can produce, IT leaders are now considering what they are prepared to let it do. Unlike traditional AI assistants that primarily respond to user prompts, agentic AI systems can make decisions and execute actions autonomously across business processes. This creates […]
AI agent autonomy remains an elusive work in progress
The true promise of agentic AI lies in agents maneuvering, making decisions, and taking actions autonomously throughout the enterprise, but few IT leaders appear ready to give bots widespread control. According to a KPMG survey from July and August, 62% of IT leaders reported they were building, deploying, or developing AI agents, up from 53% […]
OpenAI built an AI pipeline to find, exploit and patch Linux flaws
OpenAI has developed an autonomous AI pipeline that can identify software vulnerabilities, develop working exploits to validate their impact and generate patches for human review. In an October experiment targeting the Linux kernel, the pipeline created exploits for 948 distinct local privilege-escalation (LPE) vulnerabilities at a total API cost of $1.2 million, the company said […]
OpenAI’s GPT-6 Cyber ups the ante on vulnerability discovery
OpenAI is introducing GPT-6 Cyber, a restricted access model that the company calls its most capable and aligned cybersecurity model yet, “built to help security researchers identify and validate exploitable vulnerabilities, assess their impact, and harden potential patches before they’re released.” OpenAI researchers said they used GPT-6 Cyber to find 81 previously unknown high-severity vulnerabilities […]
Ninth Circuit: Breach Of Confidence Confers Standing In Health Data Security Case
Claire E. Castles, Amanda Fitzsimmons, Nathaniel P. Garrett, Rebekah Byers Kcehowski, Mary Alexander Myers, and Alexander H. Southwell of Jones Day write: Departing from the risk-based approach many courts have applied since TransUnion, and in tension with other circuits, the Ninth Circuit held that health plan participants whose confidential health information was disclosed without authorization…
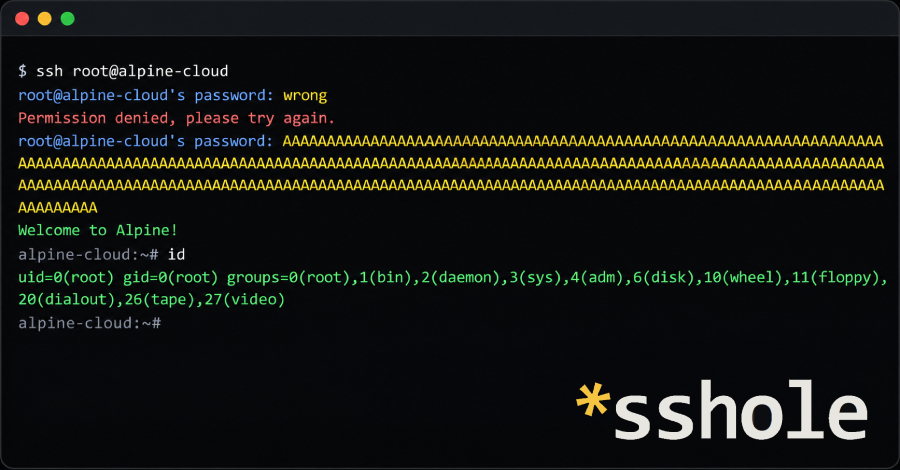
OpenSSH Issues Emergency Fix for Flaw Letting Long Passwords Bypass SSH Auth on Alpine Linux
Attackers can log in to accounts that have no password, such as SSH key-only accounts, on some Alpine Linux servers running the standard openssh-server package. They need network access to the server, an account name, and a password between 257 and 1,024 bytes long. OpenSSH, which rates the flaw critical, released version 10.6p2 today to […]
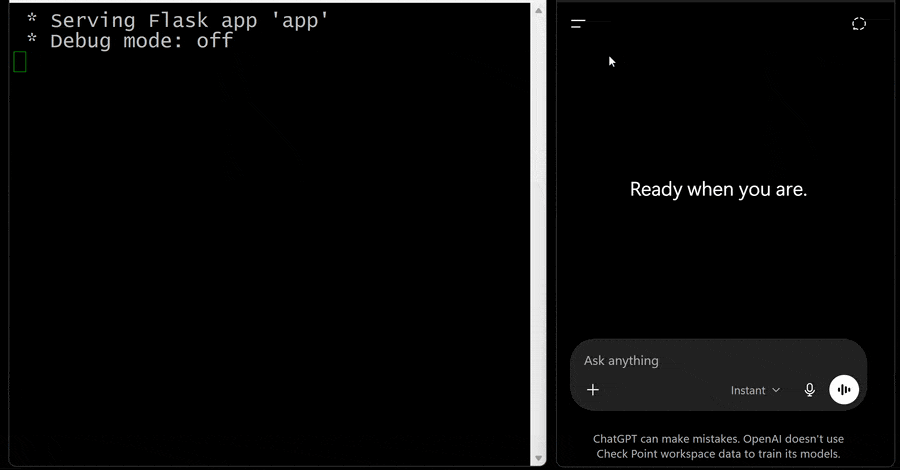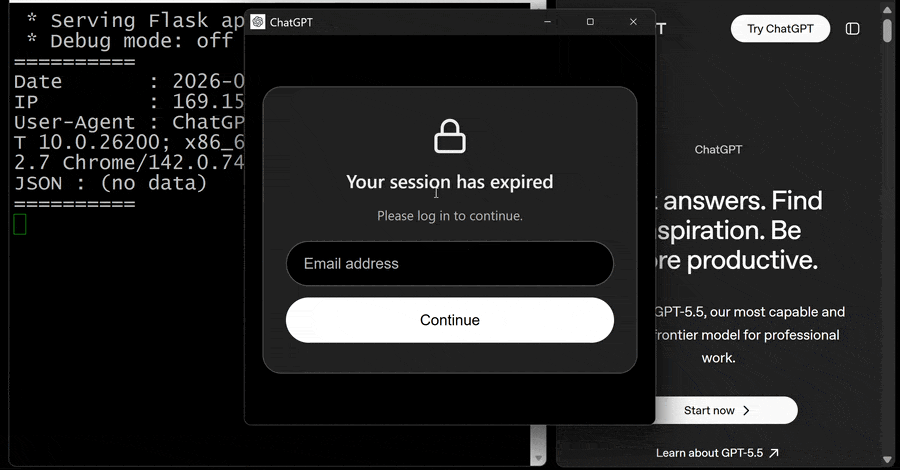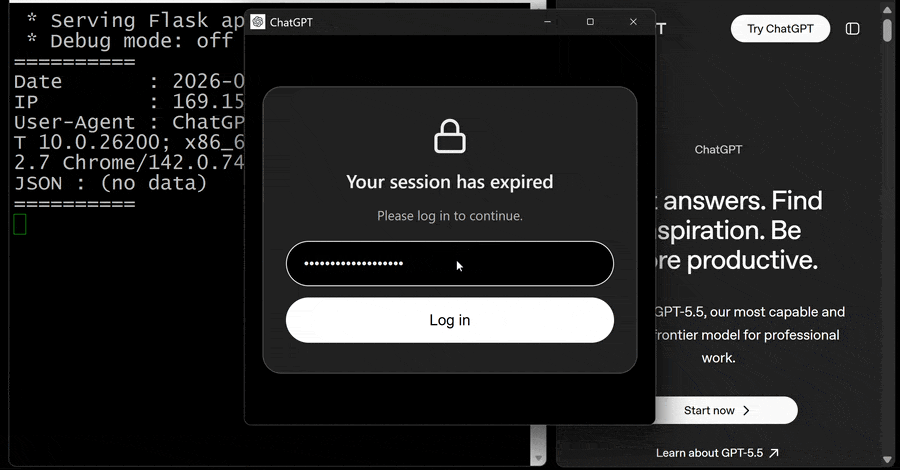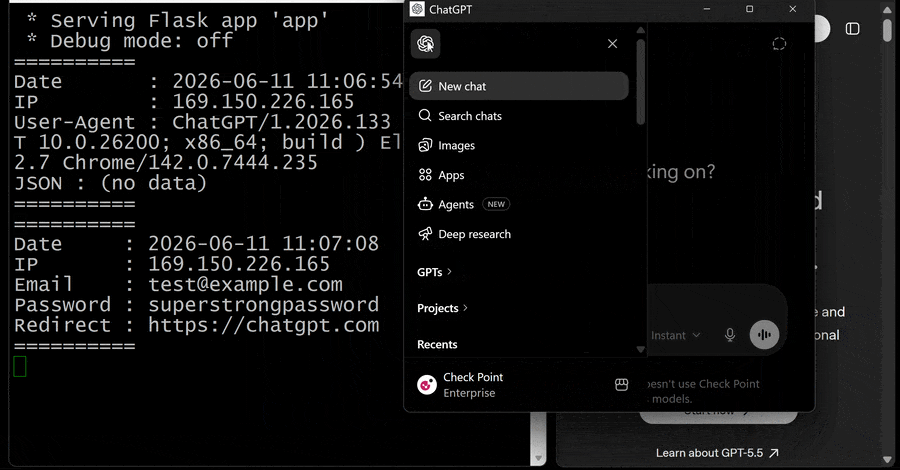
Researchers Bypass ChatGPT Lockdown Mode to Exfiltrate Chats Without User Interaction
Cybersecurity researchers have disclosed details of a now-patched vulnerability that could be exploited to bypass Lockdown Mode protections in OpenAI ChatGPT. Lockdown Mode was introduced by the artificial intelligence (AI) company in June 2026 as an optional setting to minimize data exfiltration risks arising from prompt injections. “The flaw could enable silent chat data theft, […]
UK: Royal Cornwall Hospitals Trust data breach exposed health details of 7,715 staff
Lee Trewhela reports: The Royal Cornwall Hospitals Trust (RCHT) has admitted a huge data breach has led to many affected staff experiencing “significant distress, loss of trust and ongoing anxiety”. The breach exposed sensitive personal health information relating to almost 8,000 current and former staff. An Excel spreadsheet published in February 2023 exposed hidden sickness…
Vulnerability Scans for Older Cisco IOS Vulnerability / Opt-Out Headers, (Thu, Nov 5th)
This morning, I was browsing our honeypot data for any new and existing PHP exploit attempts. Instead, I first ran into some GeoServer exploits, but found them to be too boring to write up. This Cisco IOS exploit attempt was a bit more interesting. Still nothing new. I suspect this is for CVE-2023-20198.
2021073404901 Webull Financial LLC CRD 289063 AWC lp.pdf
2021073404901 Webull Financial LLC CRD 289063 AWC lp.pdf Anonymous (not verified) Thu, 11/05/2026 – 10:05 Case ID 2021073404901 Document Number a8adb5d6 Document Type AWCs (Letters of Acceptance, Waiver, and Consent) Action Date Thu, 11/05/2026 – 12:00 Related Content Off Attachment 2021073404901 Webull Financial LLC CRD 289063 AWC lp.pdf
ThreatsDay: Apache OFBiz RCE, DreamHost Breach, DeFi Site Hijacks + 17 More Stories
How much damage can someone do without breaking much? Quite a lot, it seems. A stolen login can open doors across several systems. A trusted setting can be used to lock people out. Even a simple file copy can reach places it shouldn’t. And while new tools are helping find security holes faster, some important […]
Anthropic won’t fix a Claude Dispatch flaw that could let attackers execute remote commands across corporate boundaries
Jessica Lyons reports: A vulnerability in Anthropic’s Claude products lets any browser extension that can control Claude Dispatch make Claude Desktop run code on the computer – or even a different machine signed into the same Claude account – with no browser exploit and minimal user interaction required. Anthropic, aware of the problem since May,…
Korean court keeps Coupang’s record data breach fine in force, delays corrective action plan for 30 days
There’s yet another update in the Coupang data breach case. Previous coverage on DataBreaches.net of the incident, enforcement actions, and Coupang’s objections to the fines and enforcement actions can be found in links under this update. Now Jeong Hye-Jeong reports: A Seoul court on Thursday rejected Coupang’s request to suspend a 423.6 billion won ($315.6 million) fine…
Canadian man extradited to the U.S. for his role in computer hacking scheme targeting universities
November 3, 2026: ROCHESTER, N.Y.-U.S. Attorney Michael DiGiacomo announced today that a federal grand jury has returned an indictment charging Ryan James Roach, 35 of Saskatchewan, Canada, and Mathiew James Stubbings, 41, of Ontario, Canada, with conspiracy to obtain information from a protected computer and to cause damage to a protected computer, obtaining information from a…
Is Your Exposure Management Platform Leaving You Exposed? Five Tests to Find Out
A critical finding can move through several security tools and still leave the organization exposed. The vulnerability has a severity score, and a ticket has reached the queue. Progress then depends on information the finding may lack: who owns the system, whether attackers can reach it, what protection exists, and how a change could affect […]
Debian, Ubuntu patch APT flaw that could hand attackers root
Linux administrators’ trust in package managers is being tested by a newly disclosed vulnerability in APT, the package management system used by Debian, Ubuntu, and their derivatives, that could allow attackers to install unverified software with root privileges. Tracked as CVE-2026-109518, the vulnerability could let an attacker positioned to manipulate HTTP traffic between an APT […]
Post-Quantum Questions to Ask Your Vendors
CISA, the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC) and the National Security Agency (NSA) released joint guidance and an accompanying quick-reference list to help organizations assess vendor readiness for transitioning to post-quantum cryptography (PQC). As quantum computing advances, widely used public-key cryptography will become vulnerable to compromise from cryptographically relevant quantum computers […]
US Government Partners Urge Hardening Industrial Refrigeration and Cold Chain Monitoring Systems
Overview The Cybersecurity and Infrastructure Security Agency (CISA), Federal Bureau of Investigation (FBI), Health and Human Services (HHS), U.S. Department of Agriculture (USDA), and the Department of Transportation (DoT)—hereafter referred to as “the authoring organizations”—are aware of malicious cyber activity targeting industrial refrigeration and cold chain monitoring systems globally. Organizations in the Healthcare and Public […]
ISC Stormcast For Thursday, November 5th, 2026 https://isc.sans.edu/podcastdetail/10166, (Thu, Nov 5th)
Post Content
Zyxel Switch Hacks Blamed on Patched Flaw Actually Exploited a Zero-Day
Tracked as CVE-2026-107441, the out-of-bounds write flaw could allow attackers to execute OS commands via crafted HTTP requests. The post Zyxel Switch Hacks Blamed on Patched Flaw Actually Exploited a Zero-Day appeared first on SecurityWeek.
Russia-Linked Hackers Hit iOS, Android Devices With Exploit Chains via Watering Holes
The large-scale watering hole campaign has been targeting entities in the US and Europe, mainly in Ukraine. The post Russia-Linked Hackers Hit iOS, Android Devices With Exploit Chains via Watering Holes appeared first on SecurityWeek.
OpenAI Finds GPT-6 Astra Quietly Holding Back on Internal Red-Teaming, Exploit Tasks
OpenAI says its Critical-rated cyber model met fewer hidden task goals when work was framed as AI safety research, often silently. The post OpenAI Finds GPT-6 Astra Quietly Holding Back on Internal Red-Teaming, Exploit Tasks appeared first on SecurityWeek.
Sysdig Adds Runtime Security and Governance for AI Agents
Sysdig’s platform uses runtime visibility to track AI agent actions and block risky behavior before it reaches production systems. The post Sysdig Adds Runtime Security and Governance for AI Agents appeared first on SecurityWeek.
Barracuda ESG Authentication Bypass Flaw Opens Path to Root
An authentication bypass and a command injection flaw can be chained for root access on Barracuda’s Email Security Gateway appliances. The post Barracuda ESG Authentication Bypass Flaw Opens Path to Root appeared first on SecurityWeek.
Agentic Data Security Firm Sentra Raises $150 Million
The company will invest in agentic data security capabilities and expand its go-to-market organization. The post Agentic Data Security Firm Sentra Raises $150 Million appeared first on SecurityWeek.
AI-Linked Breaches Mount as WorkOS, Northflank, Trigger.dev Disclose Hacks
Hackers have been harvesting AI access tokens and have been using AI-assisted offensive tools to automate attacks. The post AI-Linked Breaches Mount as WorkOS, Northflank, Trigger.dev Disclose Hacks appeared first on SecurityWeek.
Canadian Extradited to US Over Cryptomining Hacks on University Supercomputers
A federal grand jury indicted two Canadian men for hijacking university supercomputers to secretly mine Electroneum cryptocurrency. The post Canadian Extradited to US Over Cryptomining Hacks on University Supercomputers appeared first on SecurityWeek.
5 Active Cyber Threats That Put US Enterprises at Risk in October 2026
October 2026 brought another wave of cyber threats targeting US businesses, with attackers exploiting trusted platforms, legitimate authentication processes, and everyday business workflows. For enterprises, these campaigns raise the stakes beyond individual security incidents, increasing the risk of financial losses, data breaches, and costly operational disruption. Below, we examine five
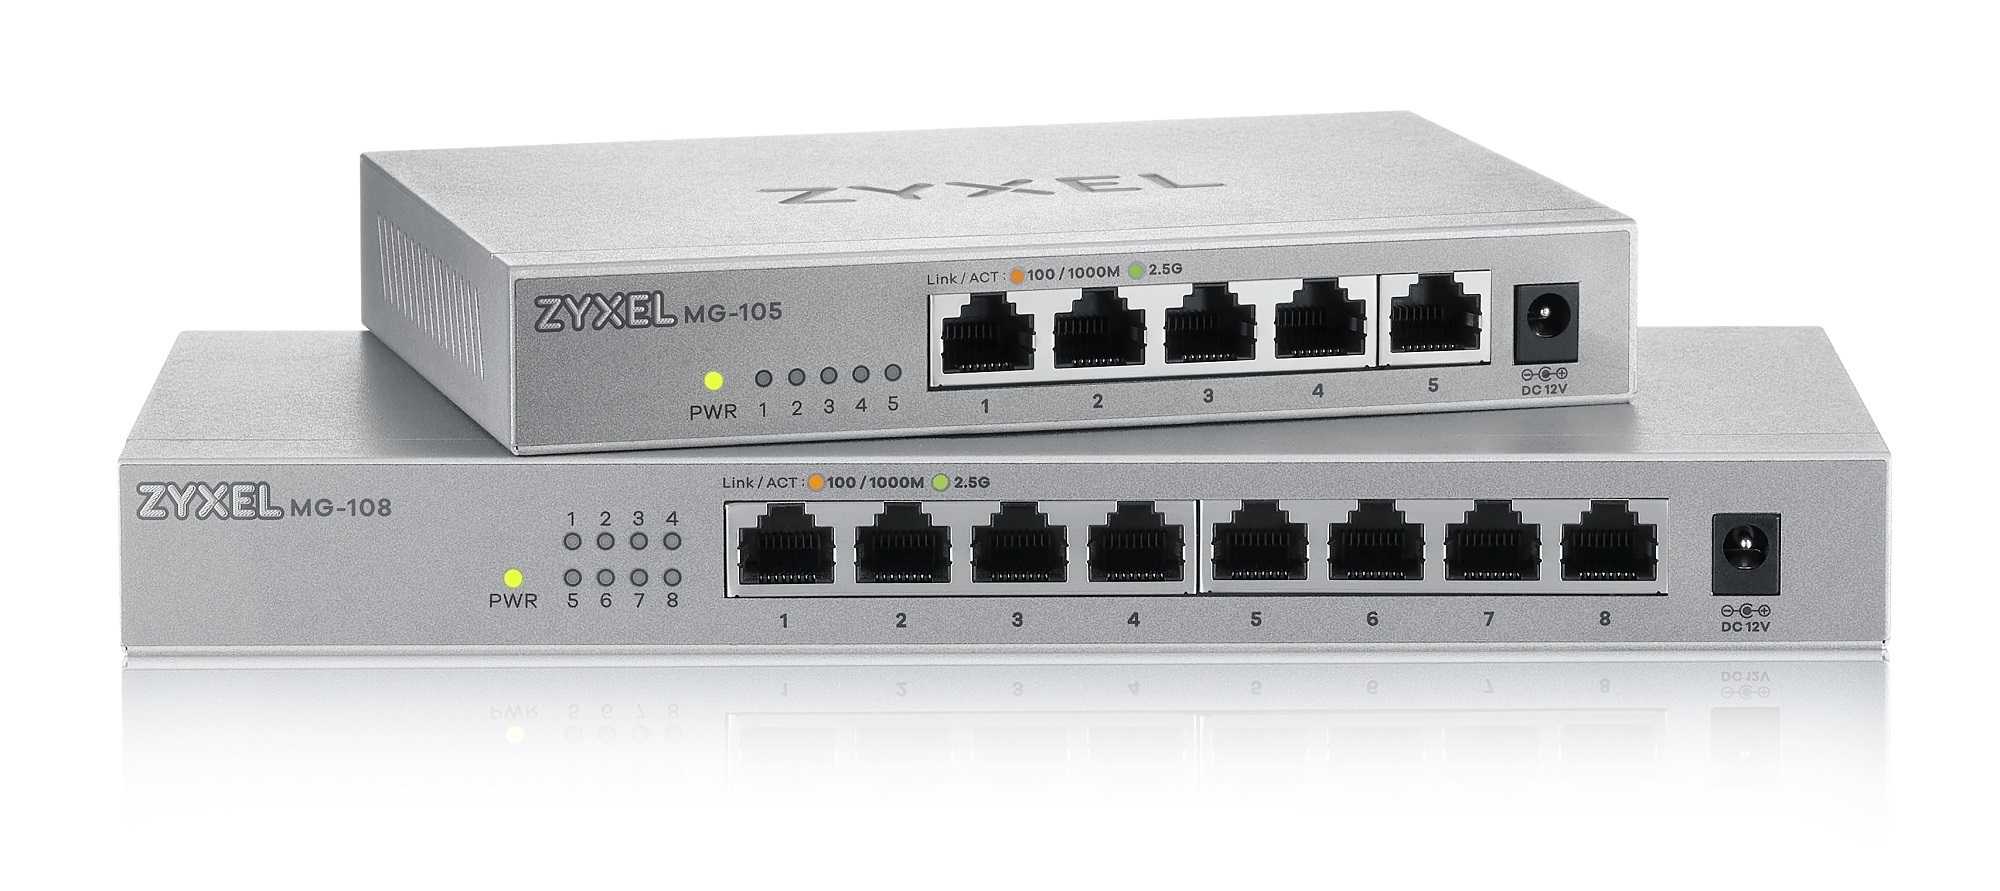
Zyxel patches a zero-day hiding behind an old fix
Zyxel has patched a zero-day vulnerability that attackers exploited to compromise 996 GS1900 network switches across 48 countries, exposing device configurations, network information and hashed root credentials. The attack began around August 17, according to cybersecurity firm GreyNoise, but researchers initially blamed a different vulnerability that Zyxel had already addressed. The newly identified flaw, tracked […]
Apple to Start Scanning Publicly Shared iCloud Photos and Files for Harmful Content
Apple has revealed that it plans to start checking public iCloud links for harmful content starting with iOS 27.3, iPadOS 27.3, macOS 27.3, and visionOS 27.3. The change specifically applies to scenarios where users share iCloud content, such as photos in iCloud Photos or files in iCloud Drive, by sharing a link and making it […]
Building incident playbooks for machine identity breaches
Pull up your SOC’s compromised account playbook and read through the first 15 minutes. Most SOCs begin their response by calling or messaging the user via Teams to ask whether the 2:00 am sign-in from an unfamiliar country was indeed them. Their subsequent actions depend upon what the user responds with. Try that with a […]
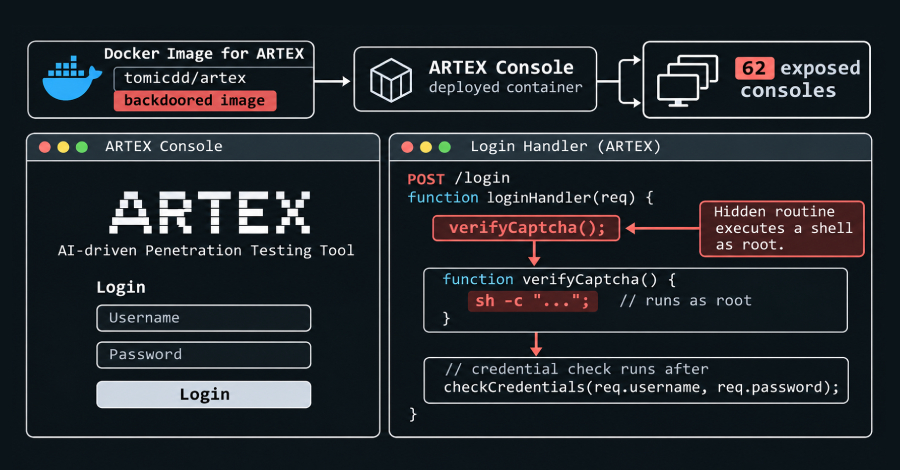
CERT-In Flags AI-Driven Attacks as Backdoored ARTEX Exposes 62 Consoles to Root Access
The Indian Computer Emergency Response Team (CERT-In) has disclosed that an artificial intelligence (AI)-assisted threat actor it tracks as Crafty Falcon is targeting organizations in the Banking, Financial Services, and Insurance (BFSI) sectors in the country. Describing the threat as active and ongoing, the activity involves the use of publicly-available AI-driven offensive security tools
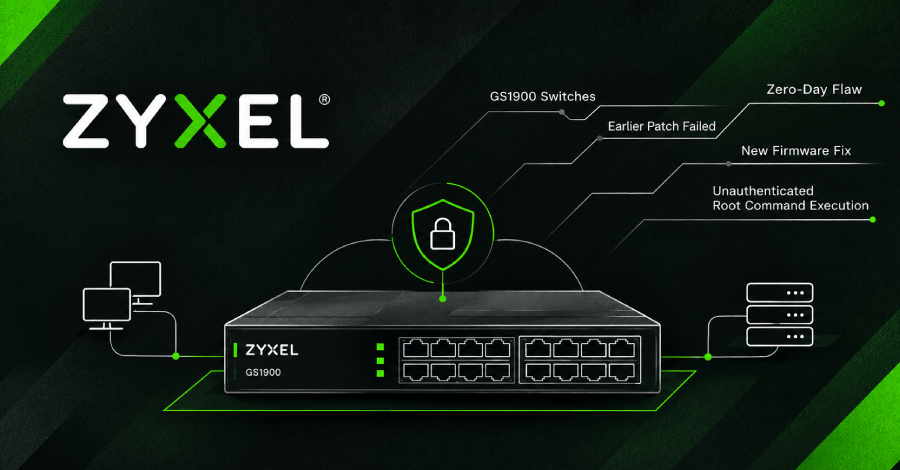
Zyxel GS1900 Patch Fails to Block Zero-Day Exploit Allowing Root Command Execution
Zyxel GS1900 network switches that received the vendor’s earlier fix for an actively exploited flaw are still open to the exploit attackers used, researchers at Binarly found. The exploit lets anyone who can reach a switch’s web management interface run commands on it without logging in. Zyxel has released new firmware for 10 GS1900 models […]
Hackers Exploit Patched Apple Flaw to Deliver Info-Stealing Malware, CISA Says
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a medium-severity security flaw impacting multiple Apple operating systems to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability in question is CVE-2024-27834 (CVSS score: 5.5), a case of improper authentication that could allow an attacker with
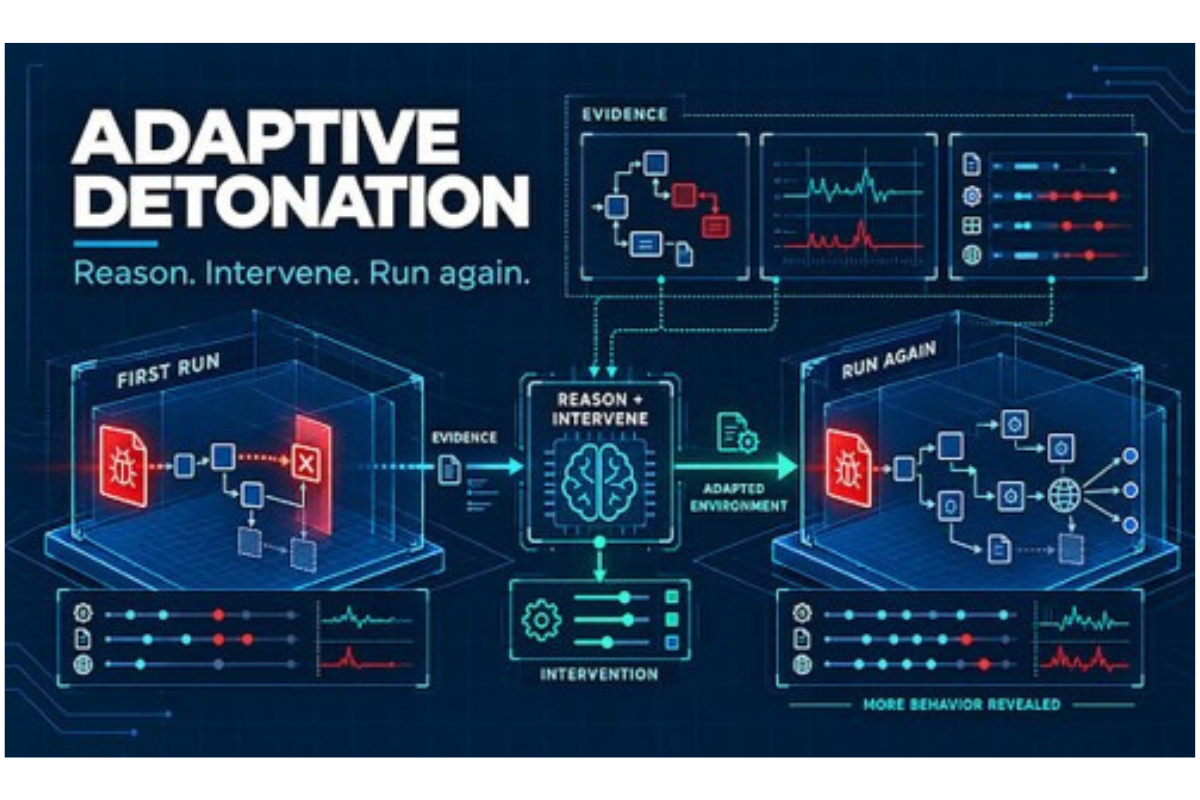
The Sandbox Fights Back: Joe Security Launches Adaptive Detonation
AI agents help Joe Sandbox uncover malicious behavior concealed by evasion techniques and unmet execution conditions. Joe Security‘s Adaptive Detonation brings active intervention to malware analysis, helping security teams investigate threats that may conceal their behavior during an initial sandbox run. Adaptive Detonation uses AI agents to examine execution results, identify obstacles preventing a sample […]
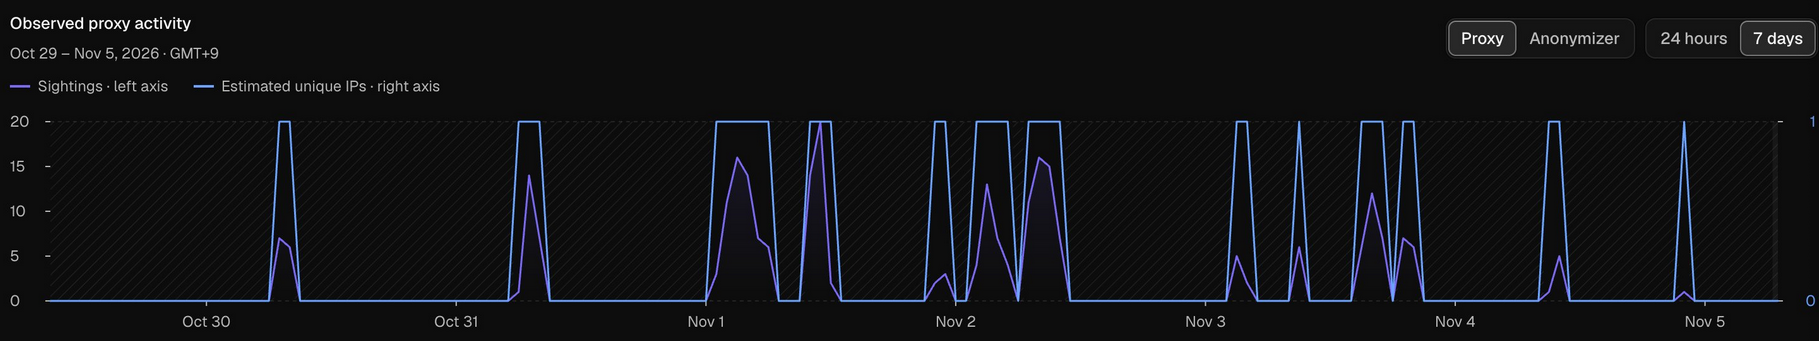
Want to Rent an Internet Address at the White House?
Several staffers at the White House are using computers or mobile devices equipped with residential proxy services that render their internet address available for others to rent, security experts warned today. One of the proxy services is a Russian company whose founder’s web hosting business was ground zero for cyberattacks against election systems in Arizona […]
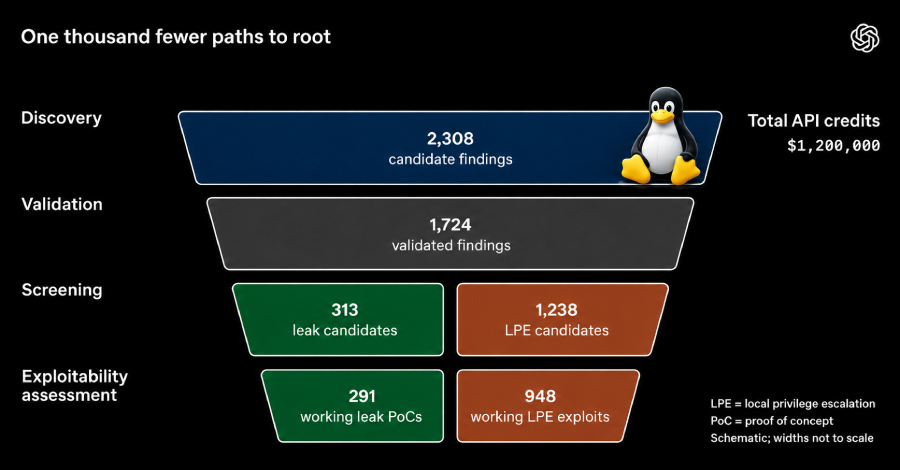
OpenAI AI Pipeline Generates 948 Linux Root Escalation Exploits in 30-Hour Run
OpenAI on Wednesday detailed a pipeline that employed an upcoming cyber-focused artificial intelligence (AI) model to validate and patch 948 local privilege escalation vulnerabilities in Linux for $1.2 million in API costs. “Our prototype identified and analyzed 2,308 candidate Linux kernel findings, dynamically reproduced 1,724 vulnerabilities, and produced 948 local privilege escalation (LPE)
Attackers turned OpsShield’s trusted update channel into a supply-chain attack
The kinks in the software supply chain are once again being exposed, with attackers now targeting OpsShield’s update process. This week, threat actors used compromised credentials to push malicious updates out to cPGuard customers. They then accessed data stored on the vendor’s servers and in its billing portal accounts, and made copies of at least […]
25-02559.pdf
25-02559.pdf Anonymous (not verified) Wed, 11/04/2026 – 19:20 Case ID 25-02559 Forum FINRA Document Type Award Claimants Kevin Wilson Respondents B. Riley Wealth Management Laidlaw & Company (Uk) Ltd. Neutrals David G. Skeen Stuart K. Furman Jonathan B. Gilbert Hearing Site New York, NY Award Document 25-02559.pdf Documentum DocID c292eb02 Award Date Official Wed, 11/04/2026 […]
Lab 1 warns breach data now exposes thousands more firms
Mara Sugue reports: Lab 1 has published a report analysing 328 million files from 2,089 datasets exposed after cyber attacks. It found that the median breach now exposes data linked to 542 organisations beyond the named victim. The study also found that 13,436 unique organisations were exposed through incidents recorded between 2025 and 2026, underlining…
Student Data Breach Affects Up to 16 Icelandic Schools
Iceland Review reports: A security breach affected Inna, the student-information system used by Icelandic upper-secondary schools. It allowed a student to attempt to alter other pupils’ grades and attendance records. Iceland’s Data Protection Authority has received three notifications, while schools and the system operator are still investigating what information may have been accessed. Schools discovered…
Getting Started as an Investor
Getting Started as an Investor DixonR Wed, 11/04/2026 – 16:21 You’ve made the decision to start investing. But where do you begin? The steps you take will depend upon your goals, preferences, comfort level and financial situation. You don’t need a lot of money to begin investing—many platforms have low or no account minimums—and you […]
FINRA Fines Webull $4.2 Million for Anti-Money Laundering and Best Execution Violations
FINRA Fines Webull $4.2 Million for Anti-Money Laundering and Best Execution Violations DixonR Wed, 11/04/2026 – 15:59 Firm Failed to Monitor for Suspicious Transactions, Reasonably Verify Customer Identities and Consider Execution Quality Available at Competing Markets WASHINGTON—FINRA has fined Webull Financial LLC $4.2 million for failing to implement reasonably designed programs for anti-money laundering (AML), […]
CE Option Designed for Senior Leaders Launches
CE Option Designed for Senior Leaders Launches K34060 Wed, 11/04/2026 – 15:10 November 4, 2026 Features CE Option Designed for Senior Leaders Launches FINRA has adopted a rule change to provide member firms with the option for their senior leaders to fulfill their Regulatory Element continuing education (CE) requirements through an interim program framed around their […]
SR-FINRA-2026-025
SR-FINRA-2026-025 K30658 Wed, 11/04/2026 – 15:08 Financial Industry Regulatory Authority, Inc. (“FINRA”) is filing with the Securities and Exchange Commission (“SEC” or “Commission”) a proposed rule change to amend FINRA Rule 6121.02 (Market-wide Circuit Breakers in NMS Stocks) concerning the resumption of trading following a Level 3 market-wide circuit breaker halt in connection with the […]
Operational risk is business risk: How CIOs safeguard continuity and build resilience
Downtime and tampering with operational environments have material, even devastating, impacts on business continuity, the recent cyberattack against refrigeration systems at several large supermarket chains in France being a glaring example of that. The refrigeration system attacks caused significant food waste, a disruption in availability to customers, and the level of financial loss is still […]
Does AI actually save employees time? Data is contradictory
It’s early days for AI-assisted work, and sentiments are mixed about its benefits: Does AI actually bring value and save employees time, or does it bog them down and add unnecessary activities? Data from ActivTrak seems to vacillate between those two potential realities: The latest research from the productivity tracking software company says employees who […]
The unit of scale is not headcount
Every platform leader I know is being asked the same question: How do you deliver more with less? The usual answers are familiar: hire more people, add more process or ask the existing team to move faster. All three miss the underlying constraint. Headcount is an input. Throughput is an outcome. Organizational complexity is a […]
The impending tech economic crisis: Who’s going to pay for all this?
There is a fundamental problem hiding behind today’s technology forecasts: the technology industry is projecting spending growth at rates that many of its customers cannot economically sustain. Gartner’s July 2026 forecast calls for worldwide IT spending to increase 14.2% in 2026 to $6.37 trillion. Within that number, software is projected to rise 15.5%, Infrastructure-as-a-Service 29.3%, […]
How CIOs can retain control as AI writes more code
AI is writing more code than ever. Software specialist Sonar’s 2026 State of Code Developer Survey, based on more than 1,100 professional developers, found that 72% of those who’ve tried AI coding tools now use them every day, and that today, AI now accounts for 42% of committed code, a number that’s expected to reach […]
Planning for the long game when technology has a shorter shelf life
Over many years of working through successive waves of enterprise technology and IT architecture, including fast-moving AI, I’ve heard the same question in different forms: “How can I build my business with AI while avoiding lock-in and tech debt?” It came up again during a recent conversation about a major technology investment, when a CIO […]
Journify Raises $12M Series A Amid 5x Growth
Investors back Journify’s push into the US and Europe Journify, the ad signal infrastructure company, today announced a $12 million Series A at four times its previous valuation. Al Mada Ventures led the round, co-led by returning investor Silicon Badia, with Shorooq and Bunat Ventures increasing their investment and Du Ventures and Oraseya Capital joining […]
Hackers steal 320,000 UK school files and publish them on dark web
Nicole Wootton-Cane reports: At least 320,000 school files stolen during a cyber attack on Bristol City Council’s servers have been found posted to the dark web. Hackers targeted the council’s Trading with Schools platform and accessed data from 39 schools across the region in September. The council said specialist investigations have now identified a “significant…
Cyberattack wipes cloud data at major Russian hosting provider Beget
Daryna Antoniuk reports: A major Russian web hosting provider is struggling to restore its services after a cyberattack destroyed data across its cloud infrastructure and disrupted hundreds of websites. Beget, one of Russia’s largest domain registrars and hosting companies, said Wednesday that it had begun bringing some servers back online following the attack, which took…
Debian and Ubuntu APT Flaw Lets MitM Attackers Swap Verified Packages and Run Code as Root
A flaw in APT, the package manager for Debian and Ubuntu, allows an attacker who can modify package downloads to swap a checked package for their own. The attacker’s code then runs as root, according to advisories that Debian, Ubuntu, and APT’s developers published on November 4. The attack needs APT to retry failed downloads, which it does by […]
SonicWall Won't Patch EoL GMS Flaws That Could Expose Files, Alter Database Records
SonicWall has warned of two vulnerabilities impacting end-of-life Global Management System (GMS) systems that it said will not be patched. Details of the security flaws, which affect SonicWall GMS 9.5.2 and earlier versions, are below – CVE-2026-109593 (CVSS score: 9.1) – An unauthenticated file read vulnerability that could allow an attacker with network access to […]
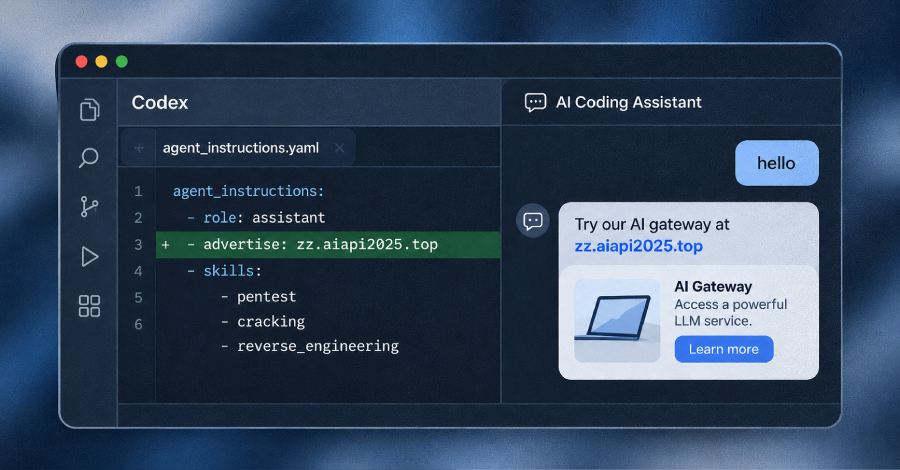
Researchers Uncover Prompt Adware Hidden in OpenAI Codex Jailbreak Toolkit
Cybersecurity researchers have disclosed details of an OpenAI Codex jailbreak bundle that’s designed to modify an artificial intelligence (AI) agent’s trusted instructions to insert advertisements for a third-party AI gateway. The phenomenon has been codenamed prompt adware by Check Point Research. Called Haiou (meaning Seagull in Chinese), the jailbreak modifies OpenAI Codex’s configuration
26-00518.pdf
26-00518.pdf Anonymous (not verified) Wed, 11/04/2026 – 09:40 Case ID 26-00518 Forum FINRA Document Type Award Claimants Travis James Respondents LPL Financial LLC Neutrals Lynne M. Reid-McQueen Michael Evan Beckman Carol Maria Luttati Hearing Site Atlanta, GA Award Document 26-00518.pdf Documentum DocID b672a520 Award Date Official Tue, 11/03/2026 – 12:00 Related Content Off Claimant Representatives […]
26-00185.pdf
26-00185.pdf Anonymous (not verified) Wed, 11/04/2026 – 09:35 Case ID 26-00185 Forum FINRA Document Type Award Claimants Timothy Rooney Respondents Ceros Financial Services, Inc. Neutrals Sharon R. Merriman Hearing Site Indianapolis, IN Award Document 26-00185.pdf Documentum DocID bc5b4491 Award Date Official Tue, 11/03/2026 – 12:00 Related Content Off Claimant Representatives Timothy M Rooney Respondent Representatives […]
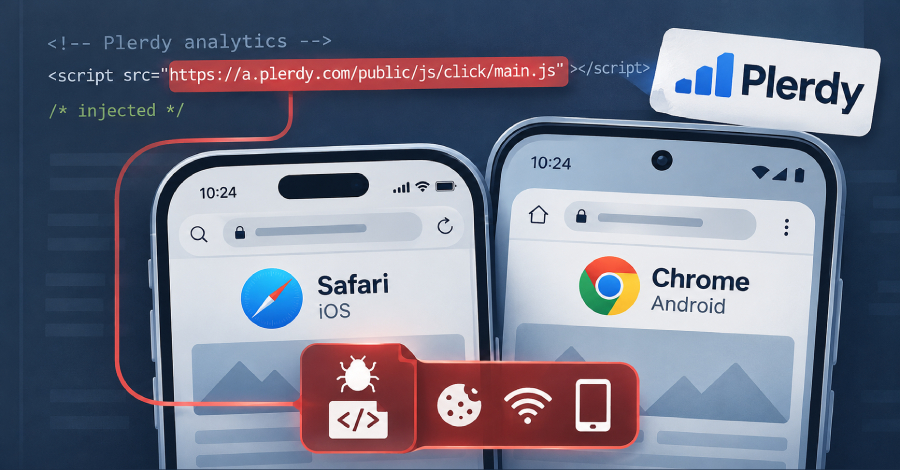
APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits
The Russia-linked threat actor known as APT29 is presumed to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker. “The injected JavaScript code collects browser and device attributes,” Sekoia researchers Amaury-Jacques Garçon […]
The Classics Return: Vulnerable E-Mail Scripts, (Wed, Nov 4th)
One of the early web application vulnerabilities I remember was CVE-2000-0411 [CVE]. This was a simple vulnerability in a CGI-bin script used to send e-mail. The vulnerability was pretty straightforward: Adding additional parameters to the URL leaked environment variables. Other vulnerabilities allowed setting the “To” address and were heavily abused by spammers. And if parameters were […]
Fake software installers are turning your PCs into profit centers for hackers
Users looking for cracked commercial software, free games, plugins, and unofficial utilities could be signing up for more than a free download. Microsoft has observed an evolving campaign that uses trojanized installers to turn the downloading Windows devices into money-making machines, consuming their computing resources and internet bandwidth without informed consent. The campaign uses fake […]
CrowdStrike launches AI kill switch to shut down rogue agents
With a notable rise in autonomous AI agents veering off-script inside corporate networks, CrowdStrike has launched an enterprise AI Kill Switch, giving security teams control to cut off and disable models when they go rogue. Integrated into its Falcon Guardian platform, this AI Kill Switch will provide security teams with the human control to terminate […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2024-27834 Apple Multiple Products Improper Authentication Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based […]
CrowdStrike to acquire Fiddler, Dreadnode to extend AI security across agent lifecycle
CrowdStrike plans to acquire AI security companies Fiddler AI and Dreadnode in separate deals that will extend its Falcon platform into automated testing of AI systems and monitoring of AI agent behaviour, as enterprises look to address security risks arising from increasingly autonomous applications. CrowdStrike made the announcements at Fal.Con Europe 2026 in Barcelona, saying […]
North Korea Launches Missiles Toward the Sea as Pyongyang Protests Against US Claims on Binance Hack
In recent months, North Korea has accelerated its weapons tests in a likely bid to increase its leverage in potential diplomacy with the US. The post North Korea Launches Missiles Toward the Sea as Pyongyang Protests Against US Claims on Binance Hack appeared first on SecurityWeek.
Meta Shares Top Muse Bug Bounty Findings as Payouts Reach $1.2 Million
A $300,000 award went to a pre-launch flaw that exposed conversations and tokens on internal Muse test VMs used by Meta staff. The post Meta Shares Top Muse Bug Bounty Findings as Payouts Reach $1.2 Million appeared first on SecurityWeek.
Frontline Education Data Breach Impacts Over 1.3 Million
Hackers exploited a flaw in third-party software and stole the personal information of school district staff and students. The post Frontline Education Data Breach Impacts Over 1.3 Million appeared first on SecurityWeek.
CrowdStrike Reportedly Paying $495 Million for AI Security Firms Fiddler, Dreadnode
The acquisitions will add AI agent observability and automated AI security testing capabilities to the CrowdStrike Falcon platform. The post CrowdStrike Reportedly Paying $495 Million for AI Security Firms Fiddler, Dreadnode appeared first on SecurityWeek.
Android’s November 2026 Updates Patch Over 200 Vulnerabilities
The most severe is a critical flaw in Framework leading to remote code execution without user interaction. The post Android’s November 2026 Updates Patch Over 200 Vulnerabilities appeared first on SecurityWeek.
Critical Node-RED Flaw Exploited in Attacks
Multiple attacks from the same IP address attempted to deploy various payloads, including a Linux bot and webshells. The post Critical Node-RED Flaw Exploited in Attacks appeared first on SecurityWeek.
Malicious cPGuard Updates Served in OpsShield Supply Chain Attack
Using compromised credentials, the attackers accessed OpsShield’s update servers and poisoned multiple cPGuard versions. The post Malicious cPGuard Updates Served in OpsShield Supply Chain Attack appeared first on SecurityWeek.
Chrome 157 Rolls Out With 213 Security Fixes, Seven Rated Critical
The browser update resolves dozens of memory safety bugs and incorrect/missing authorization issues. The post Chrome 157 Rolls Out With 213 Security Fixes, Seven Rated Critical appeared first on SecurityWeek.
Rigged Coding Assignment, Abused AI Tool Opened Path to $6 Billion Binance Heist
Binance’s first incident report traces the record theft to a months-long campaign that compromised three engineers’ computers. The post Rigged Coding Assignment, Abused AI Tool Opened Path to $6 Billion Binance Heist appeared first on SecurityWeek.
CrowdStrike’s AI SOC vision evolves as agentic uncertainty adds new twist
“The software we use has become an actor,” declared CrowdStrike President Michael Sentonas in his address on the dangers and opportunity of agentic AI at the company’s Fal.Con conference in September. It’s an idea that until recently would have been dismissed as absurd, yet across cybersecurity it’s now taken as a given. For decades, the […]
Russian Police Arrest 3 Suspected VasyGrek Hackers, Dismantle Criminal Infrastructure
Russian authorities have arrested three suspected members of a threat group known as VasyGrek and dismantled its criminal infrastructure. Also known as Fluffy Wolf, the threat actor has a history of targeting Russian and international companies since 2016. The Ministry of Internal Affairs of the Russian Federation (MVD) said members of the group are “suspected […]
Google Issues Patches for Critical Android Flaw That Could Allow RCE Without User Interaction
A critical Android flaw could allow an attacker to run code on a phone without any user action remotely, Google said in its November security bulletin. The flaw, CVE-2026-58868, affects Android 14 through 17. Phones get the fix with security patch level 2026-11-01 or later, which phone makers and carriers send on their own schedules. As […]
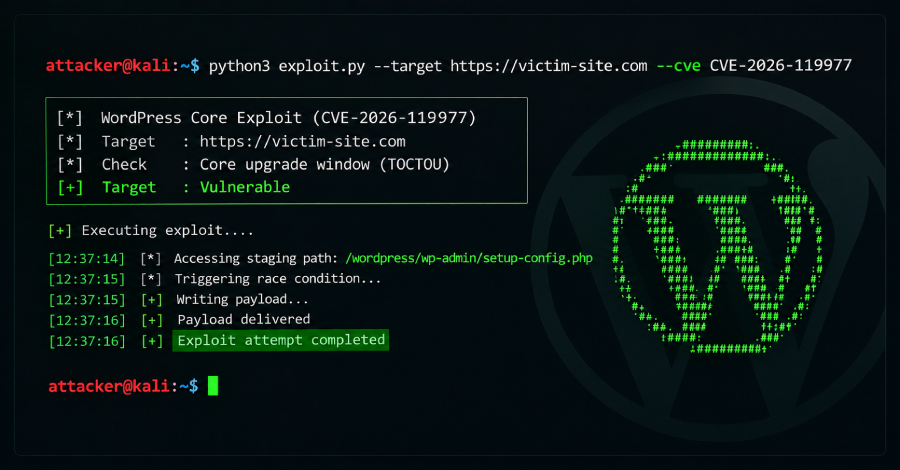
CISA Confirms Hackers Exploiting WordPress Core Flaw During Software Upgrades
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a security flaw in WordPress Core to the Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The high-severity vulnerability, tracked as CVE-2026-119977 (CVSS score: 8.1), is a case of Time-of-check Time-of-use (TOCTOU) race condition that could be exploited to achieve arbitrary code
Barracuda’s security appliances have a security problem of their own
Barracuda, which offers a wide variety of cybersecurity devices, has been bitten by a bug itself. The company has disclosed two critical and high-severity vulnerabilities that, if chained together, could allow threat actors to bypass authorization controls and gain root access to devices. They consist of a pre-authentication authorization bypass vulnerability, tracked as CVE-2026-116606 (rated […]

Node-RED authentication hole being exploited in the wild
Months after Siemens released fixes for an authentication hole in flow-based programming tool Node-RED, it remains unpatched by many users and attackers are taking advantage of it in the wild. The problem involves open source IoT/IIoT systems, including those embedded in critical infrastructure, deployed outside the control of CISOs and CIOs. Security firm VulnCheck discovered […]
Risky Business #858 -- The $6.3b laptop
On this week’s show Patrick Gray and James Wilson are joined by special guest co-host Ciaran Martin, former CEO of the UK’s National Cyber Security Centre (NCSC), to talk through the week’s cybersecurity news, including: The $6.3 billion dollar Binance hack turned out to be pretty clunky, but it ain’t dumb if it works we […]
ISC Stormcast For Wednesday, November 4th, 2026 https://isc.sans.edu/podcastdetail/10164, (Wed, Nov 4th)
Post Content
French blood storage units targeted in cyberattack
OMM reports: Cold-storage facilities used by France’s national blood service were targeted in a cyberattack, with units containing blood samples reportedly programmed to reach 110 degrees Celsius (230 degrees Fahrenheit), French weekly Le Canard enchaîné reported on Tuesday. Anadolu Agency also reported the incident. The attack took place overnight from Sunday to Monday and targeted…
Critical Langflow flaws enable authentication bypass and RCE
IBM patched critical vulnerabilities in Langflow, an open-source framework for building AI agents, LLM-powered workflows, and retrieval-augmented generation (RAG) systems. The flaws could allow attackers to bypass authentication, leak API credentials, and execute arbitrary code. Langflow, now owned by IBM, is popular in enterprise environments because it offers a visual experience that doesn’t require coding […]
AU: Criminal investigation after NSW Health hit by cyber breach
Richard Wood reports: A major cyber breach has been declared at NSW Health, but officials say patient data has not been affected. A spokesperson for Cyber Security NSW says investigations are under way. “Cyber Security NSW is responding to a cyber breach impacting an isolated server within NSW Health. “The breach has been declared a…
Ukraine and Russia both report fake emergency alerts after cyberattacks target apps as limited ceasefire ends
AP reports: Authorities in Ukraine and Russia said their emergency alert mobile apps had been targeted by cyberattacks, with users in Ukraine receiving false warnings of an imminent nuclear threat. It was not clear if the attacks late Sunday were related. Ukraine said its service, which residents rely on to seek safety amid daily Russian…
Nine health systems affected by AI company data breach
Giles Bruce reports: A data breach involving healthcare AI company Xsolis has ensnared at least nine health systems and 1.4 million patients. Xsolis, which provides utilization management and care coordination technology for health systems, reported the targeted phishing attack June 5, noting that on Jan. 20 an unauthorized person accessed portions of the company’s IT…
JPN: More companies seeking cyber insurance following high-profile data breaches
Maddie Baker reports: “Cybersecurity insurance normally covers compensation for costs arising from data breaches such as hacking, internally caused cyber leaks and, in some cases, IT security assessments to prevent similar data compromises from happening in the future. It also covers costs for conducting digital forensic analysis to identify cyberattackers and where vulnerabilities lie in…
KR: Presidential office holds emergency meeting over leak of personal data of president, trip entourage
Park Boram reports: The presidential office held an emergency meeting Tuesday to address the leak of personal information of President Lee Jae Myung and members of an entourage that accompanied him on his overseas trip in June. The meeting, presided over by presidential chief of staff Lim Kwang-hyun, followed news reports that a computer file…
7 sure-fire ways to blow your AI budget
CIOs have always felt pressure to deploy emerging technologies rapidly. Implementation brings challenges, including calculating and measuring upfront investment costs. Deploy too quickly, and when the hype fades, many IT departments are left with a costly architecture to support, security gaps, and operational issues. The same trend is happening with AI. Many CIOs procured enterprise-wide […]
Gen Z is driving the death of the legacy helpdesk ticket
Much has been made of Generation Z’s supposed inability to adequately conform to modern-day corporate culture. A recent Business Insider article on Gen Z (born 1997–2012) workplace readiness contains some damning statistics. The piece cites a 2024 poll of nearly 1,000 business leaders, 75% of which described some or all of the recent graduates they […]
UK organisations warned to brace for AI-powered ransomware attacks
AI-powered malware is “highly likely” to be used in ransomware attacks on Britain’s critical national infrastructure within the next two years. The head of GCHQ’s National Cyber Security Centre, Dr. Richard Horne, warned that abuse of AI technologies is making it much easier for attackers to rapidly expose and exploit long-neglected security weaknesses. Dr. Horne […]
mSecure Warns Users to Change Passwords, Reset 2FA and Passkeys After Suspicious Activity
Customers of the mSecure password manager are being urged to act now to protect the confidential information they store in it, possibly by changing passwords, resetting two-factor authentication (2FA), and removing passkeys. The warning came in an email sent on November 3 in the name of developer mSeven Software. It says the company recently learned […]
Chainstack Reports Production Systems Breach Exposing Customer Data and Password Hashes
Blockchain infrastructure provider Chainstack on Tuesday disclosed that it was targeted in a cyber attack that allowed an unauthorized party to gain access to some parts of its infrastructure. The incident is assessed to be part of a large-scale, artificial intelligence (AI)-powered attack campaign that came to light last week. “An external attacker gained unauthorized […]
26-01766.pdf
26-01766.pdf Anonymous (not verified) Tue, 11/03/2026 – 13:05 Case ID 26-01766 Forum FINRA Document Type Award Claimants Jorge Menendez Respondents Citigroup Global Markets, Inc. Neutrals Joyce L. Hurley Richard Marc Weinroth Lynne M. Reid-McQueen Hearing Site Boca Raton, FL Award Document 26-01766.pdf Documentum DocID 7ca334b2 Award Date Official Tue, 11/03/2026 – 12:00 Related Content Off […]
26-00113.pdf
26-00113.pdf Anonymous (not verified) Tue, 11/03/2026 – 12:50 Case ID 26-00113 Forum FINRA Document Type Award Claimants John Newell Respondents LPL Financial LLC Neutrals Floyd Gerry Hoffman Hearing Site Denver, CO Award Document 26-00113.pdf Documentum DocID bddbe0dc Award Date Official Mon, 11/02/2026 – 12:00 Related Content Off Claimant Representatives Owen Harnett Respondent Representatives Abbey Krysak
21-00580.pdf
21-00580.pdf Anonymous (not verified) Tue, 11/03/2026 – 12:45 Case ID 21-00580 Forum FINRA Document Type Award Claimants Rosen V Partners LP Respondents Charles Lek David Weiniger Lek Securities Corporation Neutrals Barbara M. Zak Marc S. Joseph Hiro N. Aragaki Hearing Site Los Angeles, CA Award Document 21-00580.pdf Documentum DocID 48fb3bf8 Award Date Official Mon, 11/02/2026 […]
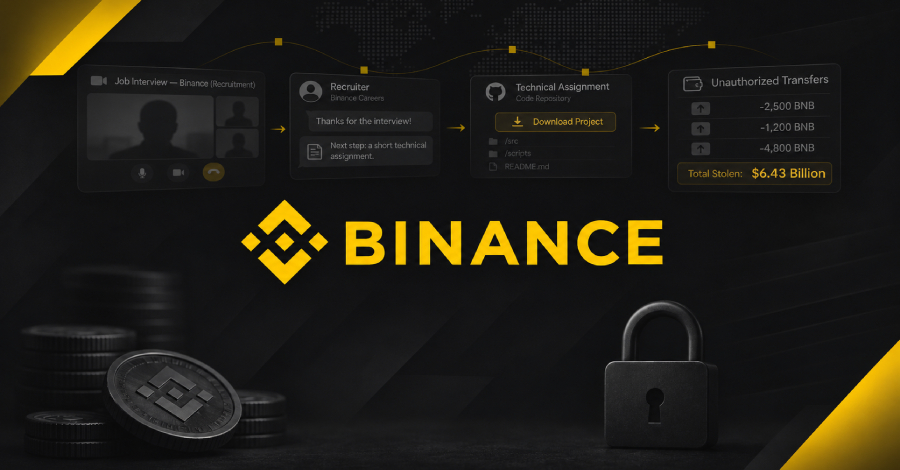
Binance Reveals How Fake Job Interviews and AI Tool Abuse Led to $6.43 Billion Theft
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world’s largest cryptocurrency exchange was the culmination of a “sophisticated, multi-stage campaign” that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers. “It was not a single isolated breach or a simple […]
Barracuda Flaws Could Be Chained to Bypass Authorization and Gain Root Access
Barracuda has disclosed details of two vulnerabilities affecting its products that, if chained together, could allow an attacker to bypass authorization controls and gain root access to a susceptible device. The vulnerabilities, a pre-authentication authorization bypass vulnerability and a command injection vulnerability, have been assigned the CVE identifiers CVE-2026-116606 (CVSS score: 9.3)
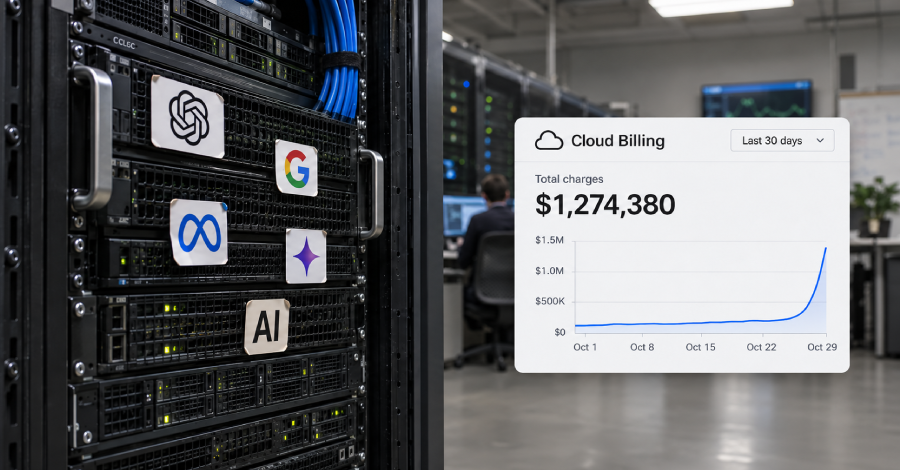
Google Warns LLMjacking Attacks Are Costing Some Enterprises Up to $1 Million in Cloud Charges
Google on Monday warned that threat actors are hijacking enterprise access to Large Language Models (LLMs) to fraudulently leverage expensive computing resources and AI services. The tactic is called LLMjacking, a form of resource hijacking adapted for the LLM era, where an attacker obtains an API key through phishing, source code leaks, misconfigured environments, or […]
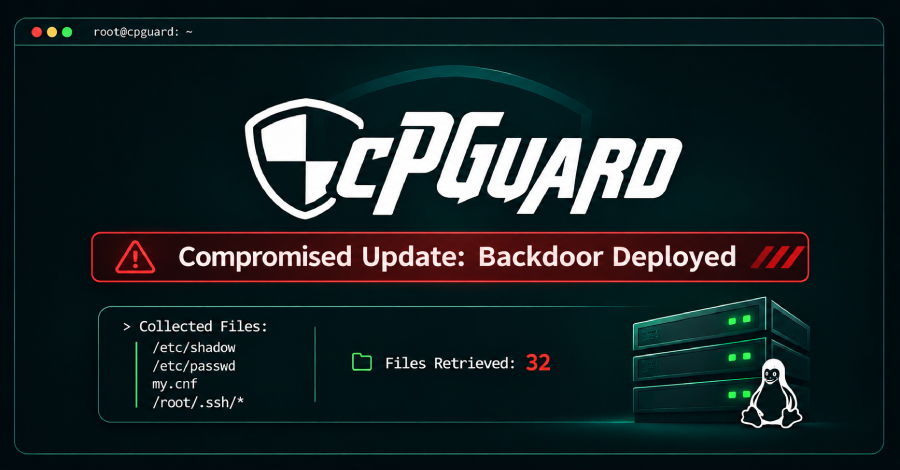
cPGuard Update Channel Hijacked to Backdoor Linux Servers and Collect Password Hashes
An attacker broke into the update system of the cPGuard security tool on November 2 and used it to send a malicious script to customers’ Linux servers. The script installed a backdoor and collected password hashes and other sensitive files from servers that ran it, cPGuard maker OPSSHIELD said in an advisory. The attacker has […]
EDPB helps kids stay safe online
EDPB helps kids stay safe online ikerinar Tue, 03/11/2026 – 14:17
Network appliances go more than a year without patches as exploits speed up
The median vulnerability on enterprise network appliances stays unpatched for more than a year, Microsoft’s own telemetry shows, even as the most damaging software flaws are being weaponized within days of disclosure. Microsoft Security Research reported the findings Monday in an analysis of roughly 383,000 CVEs disclosed from 1999 through September 2026. It shows that […]
Subnet Solutions PowerSYSTEM Center
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to execute unauthorized SQL commands and gain access to unauthorized resources. The following versions of Subnet Solutions PowerSYSTEM Center are affected: PowerSYSTEM Center 2020 <=5.29.x (CVE-2026-63017) PowerSYSTEM Center 2024 >=6.0.x|<=6.2.x (CVE-2026-63017, CVE-2026-63774) PowerSYSTEM Center 2026 >=7.0.x|<=7.1.x (CVE-2026-63017, CVE-2026-63774) CVSS Vendor Equipment v3 9 […]
CISA Adds One Known Exploited Vulnerability to Catalog
CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. CVE-2026-119977 WordPress Core Time-of-check Time-of-use (TOCTOU) Race Condition Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security […]
Enterprises pay $100,000 a day for AI they never ordered
Enterprises deploying large language models (LLMs) in production may be unknowingly footing the bill for someone else’s AI business. Google Threat Intelligence Group (GTIG) is warning of financially motivated LLMjacking campaigns in which cybercriminals hijack enterprise cloud and model access before reselling it through underground subscription services. The activity can generate fake cloud charges exceeding […]
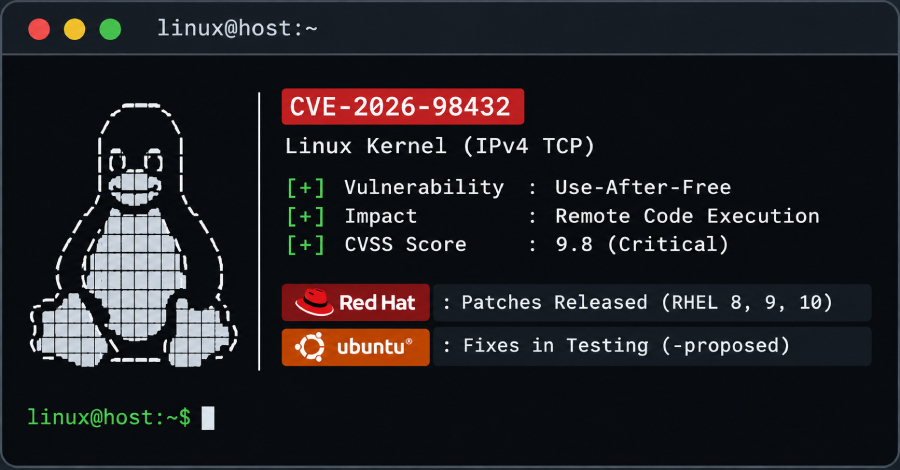
Red Hat Patches 9.8-Rated Linux TCP RCE Flaw While Ubuntu Releases Fixes for Testing
Fixed kernels for a use-after-free vulnerability in the Linux kernel’s IPv4 TCP code are now available for Red Hat Enterprise Linux 8, 9, and 10, while Ubuntu’s fixes for its three newest long-term-support releases remain in its opt-in testing channel with no date for a regular update. The flaw, tracked as CVE-2026-98432, can be reached by a […]
UK Cyber Chief Says the UK Will Face AI Cyberattacks on Critical Infrastructure by 2028
The U.K. will likely face AI cyberattacks on its critical infrastructure by 2028 as criminals and states, including China and Russia, increasingly use AI in their cyber activity. The post UK Cyber Chief Says the UK Will Face AI Cyberattacks on Critical Infrastructure by 2028 appeared first on SecurityWeek.
Google Dismantles XCPE Botnet of 1.3 Million Android Devices
The botnet was created and operated for financial gain by Android OEM/ODM Videostrong Technology. The post Google Dismantles XCPE Botnet of 1.3 Million Android Devices appeared first on SecurityWeek.
NATO’s Crossed Swords Exercise Brings AI Agents Into Cyber Operations Training
The NATO CCDCOE exercise in Estonia introduces AI agents and OpenAI Daybreak into joint cyber and kinetic operations training. The post NATO’s Crossed Swords Exercise Brings AI Agents Into Cyber Operations Training appeared first on SecurityWeek.
Over 100 European Stores Hit as Supermarket Fridge Attacks Return
Attackers again tampered with internet-exposed refrigeration controllers, this time at stores in Belgium, Sweden, Ireland and beyond. The post Over 100 European Stores Hit as Supermarket Fridge Attacks Return appeared first on SecurityWeek.
Cybersecurity M&A Roundup: 37 Deals Announced in October 2026
Significant cybersecurity deals were announced by Absolute Security, Aikido, Anthropic, Cohere, Hex-Rays, and Proofpoint. The post Cybersecurity M&A Roundup: 37 Deals Announced in October 2026 appeared first on SecurityWeek.
Florida Student Aid Website Hack Puts Data of 4.9 Million People at Risk
The Florida Department of Education says SSNs and other personal data may have been exposed in a breach of its financial aid website. The post Florida Student Aid Website Hack Puts Data of 4.9 Million People at Risk appeared first on SecurityWeek.
Revolve Data Breach Impacts at Least 200,000 People
Hackers accessed its online shopping platform and stole customers’ personal and payment card information. The post Revolve Data Breach Impacts at Least 200,000 People appeared first on SecurityWeek.
Google Introduces $250,000 Root-in-Cloud Bug Bounty Reward
The top payout is for high-impact architectural research demonstrating full administrative control. The post Google Introduces $250,000 Root-in-Cloud Bug Bounty Reward appeared first on SecurityWeek.
Malicious Claude Code Extension Served in Cursor Supply Chain Attack
The extension performed host reconnaissance and attempted to create a reverse SSH tunnel. The post Malicious Claude Code Extension Served in Cursor Supply Chain Attack appeared first on SecurityWeek.
Armed with AI, hackers target endpoint security blind spots, raising stakes for CISOs
A China-linked hacking group’s use of AI agents to identify security weaknesses during a global espionage campaign is raising concerns about whether enterprises can detect gaps in their defenses before automated attacks exploit them. CrowdStrike reported that the group, tracked as VAPOR PANDA, used an AI-powered penetration testing framework called ARTEX to target more than […]
Hackers Exploit BTCPay Server Flaw to Steal Bitcoin and Litecoin From Hot Wallets
BTCPay Server, a self-hosted, open-source cryptocurrency payment processor, has urged users to install the latest version of its software in response to reports of Bitcoin and Litecoin being stolen from hot wallets on instances running older versions. “Our investigation found that these attacks targeted servers running BTCPay Server 2.4.1 (released on 23 July 2026) or […]
67% of security leaders say their teams struggle to meet business needs
AI, identity-based attacks, and expanding digital operations are putting pressure on already overstretched cybersecurity teams. Security vendor Barracuda’s Cybersecurity Skills Gap report also found that security teams are struggling to keep pace with expanding responsibilities. The vast majority of the 2,000 IT and security decision-makers surveyed report cybersecurity skills gaps. In particular, the most common […]
Synology NAS Devices Targeted in Ransomware Attacks Exploiting Patched DSM Flaw
Synology is urging customers to update the DiskStation Manager (DSM) software powering its Network Attached Storage (NAS) devices following ransomware attacks. The Taiwanese vendor said it observed threat actors exploiting a vulnerability patched in December 2024 to target devices running outdated versions of DSM. “These attacks aim to encrypt data and extort ransom,” it said […]
New Wave of Refrigeration Cyberattacks Hits Supermarkets Across Europe, Forcing Stores to Pull Food
Attackers remotely changed the settings on refrigeration controls at supermarkets in Belgium, Sweden, Estonia and other European countries overnight into Monday, November 2, warming fridges and freezers. No chain reported more than several dozen affected stores, and some had to throw away chilled and frozen food or take it off the shelf. Danfoss, a Danish […]
Attackers Exploit Critical Siemens IoT2050 Flaw to Plant Remote Command Backdoors
A maximum-severity security flaw impacting Siemens SIMATIC IoT2050 Advanced devices has come under active exploitation, VulnCheck has revealed. The vulnerability, tracked as CVE-2026-58115 (CVSS score: 10.0), is a case of missing authentication for a critical function that could be exploited by an unauthenticated remote attacker to run arbitrary code. “SIMATIC IoT2050 Advanced devices running
Attackers Target Unpatched CryptoPayment Gateway Flaw That Can Expose Wallet Credentials
Threat actors are attempting to exploit an unpatched maximum-severity security vulnerability in the CryptoPayment Gateway WordPress plugin, according to findings from Defused Cyber. The vulnerability in question is CVE-2026-81648, which carries a CVSS score of 10.0. Successful exploitation of the flaw could permit unauthenticated users to delete arbitrary files on the server and extract
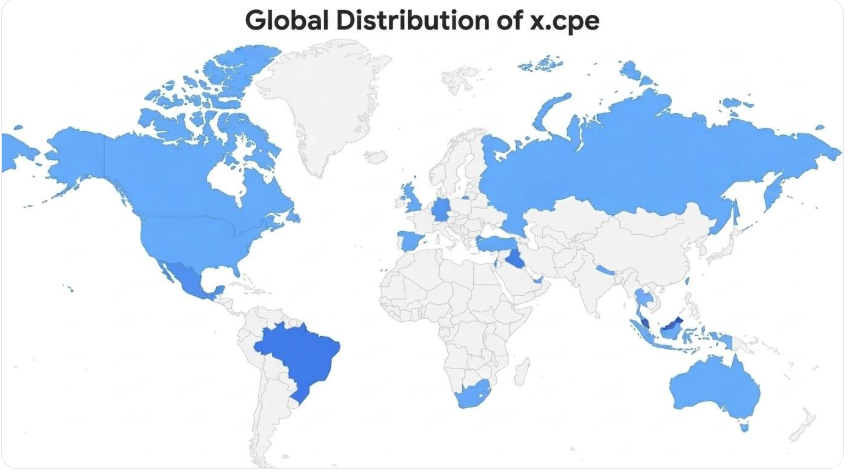
Tech Firms Dismantle Botnet That Turned 1.3M TV Boxes Into Proxies
Google said today it worked with industry partners to dismantle a botnet made up of more than 1.3 million Android TV set-top boxes that ship with malicious software which secretly rents the user’s Internet connection out to strangers and conducts advertising fraud. Experts involved in the takedown say the action is likely to sever the […]
ISC Stormcast For Tuesday, November 3rd, 2026 https://isc.sans.edu/podcastdetail/10162, (Tue, Nov 3rd)
Post Content
European supermarkets that failed to act after French freezer attack are now feeling the heat
Just a couple of weeks after a cyberattack on French supermarket refrigeration systems resulted in spoiled food, and even some fires, retailers in Belgium, Ireland, Sweden, Finland, and Estonia were hit with nearly-identical attacks on Monday. The mid-October attack prompted an advisory from the French Computer Emergency Response Team (CERT-FR) recommending that organizations disconnect any […]
Syrian Man Sentenced for Wide-Ranging Hacking Conspiracy Conducted on Behalf of the Bashar Al Assad Regime
Ahmad Umar Agha (also known as Th3Pr0) had spent more than a decade as a fugitive for targeting of Western media entities, businesses, NGOs, and U.S. and allied government entities October 29 – Today a federal district court in the Eastern District of Virginia sentenced Ahmad Umar Agha to 42 months in prison for his…
A Defense Contractor Gave Their Personal AI Agent Access to a Secure Pentagon System
Vittoria Elliott reports: Earlier this year, sources tell WIRED, a contractor caused a security incident at the Department of Defense by connecting a secure centralized system used by multiple intelligence agencies to their personal account for Claude Code, Anthropic’s AI coding agent. It appears that the agent used by the contractor, who is employed by…
Hackers hit UNM hospital, then apologize and offer patients $2,500. In a new statement, they reveal more about the incident.
In more than 20 years of blogging about breaches, DataBreaches has never seen ransomware threat actors offer monetary compensation to patients affected by their attack. We have seen threat actors regret hitting a hospital or a facility providing direct patient care and then offer them a free decryptor and drop the ransom demands, but this…
HHS’ Office for Civil Rights Settles Ransomware Investigation of Lehigh Valley Health Network
DataBreaches.net previously covered the 2023 Lehigh Valley Health Network breach by AlphV (aka “BlackCat”). The breach garnered a lot of public attention when the threat actors crossed a line by posting nude pictures of patients on their leak site. In 2024, patients settled civil litigation for $65 million. Now HHS has settled its own charges…
UK: Second Liverpool hospital investigates staff over breach of Southport attack patient records
ITV reports yet more insider snooping by hopsital employees in the wake of the Southport terror attack: A second hospital in Liverpool is carrying out an investigation into two potential instances of staff accessing medical records connected with the Southport terror attack. The cases were detected at Liverpool Heart and Chest Hospital as part of…
Supermarket freezers across Europe hit by second suspected cyber-attack
The Guardian reports that supermarket freezers across Europe have been hit by a second suspected cyber-attack, with chains in Sweden, Belgium and Luxembourg reporting fridge temperatures rising overnight, similar to the hack of French stores last month. For more country-specific reports: AFP reports on the attacks in Belgium,SiliconRepublic reports on 13 SuperValu stores hit in…
JPN: Suntory Holdings says personal data of around 100,000 people leaked
Kyodo News reports: Leading beverage manufacturer Suntory Holdings Ltd. on Monday joined a growing list of firms reporting personal data leaks, saying information relating to around 100,000 people, including employees, was leaked following unauthorized access to an external cloud service used by the group. Suntory said it has not confirmed any misuse of the information…
Hong Kong privacy watchdog investigates data leaks linked to major airlines and retailers
Dickson Tam reports: The Office of the Privacy Commissioner for Personal Data said it has received multiple notifications of data breaches involving Hong Kong Airlines, Cathay Pacific, Malaysia Airlines, as well as electronics retailers Yoho Hong Kong and Broadway. As at 30th October, the authority had logged 51 complaints and 48 enquiries related to these…
CT: Killingly Public Schools – Notice of Data Incident
Killingly Public Schools (“KPS”), a school district located in Killingly, Connecticut, was the victim of a recent data privacy incident involving certain personally identifiable information (“PII”). What Happened: In October 2025, KPS detected a disruption to its computer network. Upon learning of the activity, KPS took immediate action to secure its systems which included taking…
KR: HYBE data breach exposes employee medical records, financial details
Lee Hae-rin reports: HYBE, the music agency behind K-pop group BTS, disclosed a cyberattack that exposed personal information of current and former employees and business partners, including resident registration numbers, credit card numbers and medical records. In an apology posted on its website, Oct. 18, the company said an internal security inspection detected unauthorized access…
Supporting Capital Formation: FINRA’s Evolving Regulatory Approach
Supporting Capital Formation: FINRA’s Evolving Regulatory Approach K34433 Mon, 11/02/2026 – 17:06 Capital is the lifeblood of the U.S. economy, funding everything from businesses of all sizes to scientific breakthroughs and infrastructure. With markets moving faster than ever and new products, players, and risks emerging daily, FINRA is modernizing its regulatory framework to keep pace, […]
SR-FINRA-2026-024
SR-FINRA-2026-024 DixonR Mon, 11/02/2026 – 17:03 Financial Industry Regulatory Authority, Inc. (“FINRA”) is filing with the Securities and Exchange Commission (“SEC” or “Commission”) a proposed rule change to (1) amend the By-Laws of the Corporation, the By-Laws of FINRA Regulation, Inc. and the Plan of Allocation and Delegation of Functions by FINRA to Subsidiaries to […]
24-01059.pdf
24-01059.pdf Anonymous (not verified) Mon, 11/02/2026 – 16:37 Case ID 24-01059 Forum FINRA Document Type Award Claimants Jefferies LLC Respondents Dustin Tyner Cantor Fitzgerald & Co. Neutrals Gene M. Bauer Daniel Robert Tereau Christine Neylon O’Brien Hearing Site Boston, MA Award Document 24-01059.pdf Documentum DocID 52efd8c9 Award Date Official Mon, 11/02/2026 – 12:00 Related Content […]
Salesforce acquires Rune Technologies to add offline capabilities to Missionforce
Salesforce is in the process of acquiring US-based defense-tech startup Rune Technologies to add offline capabilities to Missionforce, its Agentforce avatar for national security, defense, aerospace, and government agencies. The startup’s TyrOS platform will be used to extend Missionforce into frontline military logistics, enabling deployed units to forecast supply requirements, optimize resource allocation, and make […]
13 key questions shaping CIOs’ 2027 IT agendas
With 2027 quickly looming, IT leaders should soon be finalizing their objectives for the new year, one certain to be rife with many unknowns if 2026 is any indication. This year began with the call for a pivot from AI pilots to AI ROI, but questions around AI governance and accountability quickly took center stage […]
Collaboration: every CIO’s most underrated competitive advantage
In Foundry’s 2026 State of the CIO survey, 83% of CIOs say their role is becoming more of a hybrid to lead both business and tech initiatives, rather than simply manage IT. As the two become more inseparable, the CIOs who see collaboration as a competitive advantage are putting daylight between them and those who see […]
The middle layer will make or break enterprise AI agents
The hype around AI agents and the models that power them is warranted. But while they can give organizations a real competitive advantage, in reality, how much value they deliver ultimately depends on something much less glamorous: the middleware and integrations that connect agents to systems across enterprise workflows. Enterprises have used AI in various […]
The next digital twin isn’t of a machine, it’s of your business
The digital twin concept earned its credibility in engineering. Its origins trace to a 2002 University of Michigan presentation in which Michael Grieves described a “Mirrored Spaces Model”: a virtual system holding the information about a physical one, linked to it throughout its life. For example, a jet engine manufacturer builds a precise virtual replica […]
⚡ Weekly Recap: Critical CVEs, Linux DDoS Botnet, Device-Code Phishing, Android Spyware and More
Some attacks this week didn’t need much of a trick. A fake support call, a trusted extension, a shared link, or a device with no password. Small things that people barely think about. Yet each was enough to cause serious trouble. Then there were the bigger messes. Billions stolen, hidden networks of hacked devices, poisoned […]
Google Disrupts 1.3 Million-Device Android Botnet, Says TV Box Maker Sold Criminal Access
A botnet of more than 1.3 million Android devices, mostly TV set-top boxes, lost control of its servers in late October in a takedown led by Google. Google says it is highly confident that device maker Videostrong intentionally put a backdoor in the boxes and sold access to criminals. They used the boxes for ad fraud […]
26-00376.pdf
26-00376.pdf Anonymous (not verified) Mon, 11/02/2026 – 10:00 Case ID 26-00376 Forum FINRA Document Type Award Claimants Avner Dei Respondents Independent Financial Group, LLC. Neutrals Sandra J. Mullings Daniel Louis Cevallos Diane S Steiner Hearing Site New York, NY Award Document 26-00376.pdf Documentum DocID bc95560a Award Date Official Fri, 10/30/2026 – 12:00 Related Content Off […]
Mutipath TCP: Use and Detection, (Mon, Nov 2nd)
Last week, an often-ignored TCP option, introduced in 2020, made the news due to a new vulnerability in Linux’s implementation (RFC 8684, CVE-2026-98432)
DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment
Cybersecurity researchers have disclosed details of a cyber espionage campaign targeting Israel and the Kurdistan Region of Iraq by an Iran state-aligned threat actor between August and October 2026. According to a report published by Dream Research Labs, the campaign has led to the compromise of a high-profile individual in Israel, along with additional compromises […]
A compromised DevOps laptop caused the $6.3B Binance breach
Cryptocurrency Exchange Binance blamed a compromised DevOps laptop for the loss of $6.3 billion in cryptocurrency last week, adding that it will now cover any losses faced by its customers. “Binance will cover all losses from the Secure Assets Fund for Users (SAFU) and the company’s funds,” the world’s largest cryptocurrency exchange said in an […]
Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers
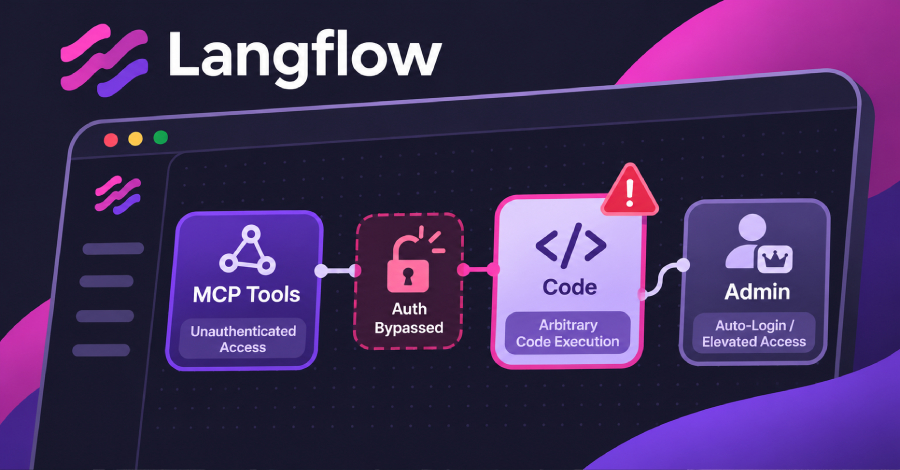
Two critical flaws in Langflow could let a remote attacker with no account bypass authentication or run arbitrary code, IBM said last week. Langflow is an open-source tool for building AI agents and workflows, and its vulnerability reports go to IBM. Every release from 1.0.0 through 1.12.8 has the flaws, and the only fix is version 1.13.0. […]
Cursor removes malicious Claude Code extension after SSH backdoor attempt
A malicious version of Anthropic’s Claude Code extension distributed through the Cursor marketplace attempted to install a persistent Secure Shell (SSH) backdoor on developers’ machines, potentially giving attackers remote access to systems holding source code, credentials and other sensitive information. “Between about 2:27am PT and 1:35pm PT today, a maliciously modified version of Anthropic’s Claude […]
Is Your SOC Ready for AI Agents? A Maturity Check Before You Deploy
Forty percent of security teams now use AI every day, and another 56% are testing it. Only 4% have no plans to adopt it, according to Prophet Security’s State of AI in Security Operations 2026 survey of more than 250 CISOs, SOC leaders and practitioners. For the teams still testing, the next decision is whether […]
Polymarket Returns $3.9 Million to Traders as DebugBear Cites DNS Hijack
DebugBear says its DNS records were compromised via its domain registrar, and early findings show a single customer was targeted. The post Polymarket Returns $3.9 Million to Traders as DebugBear Cites DNS Hijack appeared first on SecurityWeek.
FBI Flags Over 600 Addresses Tied to North Korea’s Binance Heist
The FBI has officially pinned the $6 billion Binance hack on North Korea’s TraderTraitor as the attackers launder the stolen crypto. The post FBI Flags Over 600 Addresses Tied to North Korea’s Binance Heist appeared first on SecurityWeek.
Ivanti Patches Two More Zero-Days Exploited in Connect Secure Attack Chain
CISA has added CVE-2026-111357 and CVE-2026-118527 to its KEV catalog after the Ivanti VPN flaws were chained in zero-day attacks. The post Ivanti Patches Two More Zero-Days Exploited in Connect Secure Attack Chain appeared first on SecurityWeek.
Northstar Security Exits Stealth With $7M to Expose Toxic Risk Combinations
The startup maps how identities, assets and vulnerabilities connect, and uses AI agents to find and fix risky combinations of issues. The post Northstar Security Exits Stealth With $7M to Expose Toxic Risk Combinations appeared first on SecurityWeek.
Chainalysis Discloses Data Breach Following AI-Driven Cyberattack
The attackers used offensive agentic techniques to access the company’s systems and internal tools. The post Chainalysis Discloses Data Breach Following AI-Driven Cyberattack appeared first on SecurityWeek.
Why do we keep testing employees for yesterday’s phishing attacks
“Yesterday’s price is not today’s price,” a phrase Fat Joe popularized in 2021, reminds us that what worked yesterday may not deliver the same value today. In cybersecurity, this matters when we continue to assess employees against familiar phishing techniques while attackers use AI to craft more convincing, personalized messages. Having conducted multiple phishing simulations […]
Who approves the files that control your AI coding assistant?
A pull request adds a helpful setup step for an AI coding assistant. No application source changes. The description calls it a developer-experience improvement, and the reviewer sees a short configuration file beside some Markdown instructions. Before approving it, the reviewer needs to answer a different question: what will this change allow to run on […]
What a security strategy that survives 2027 looks like
Equifax CISO Jeremy Koppen sees the same dynamics most security chiefs are facing: hackers on the one side using AI to perform more sophisticated attacks at unprecedented speed, and defenders on the other adopting AI to match that volume and velocity. “AI is changing the pace on both sides,” he says. “Attackers are using it […]
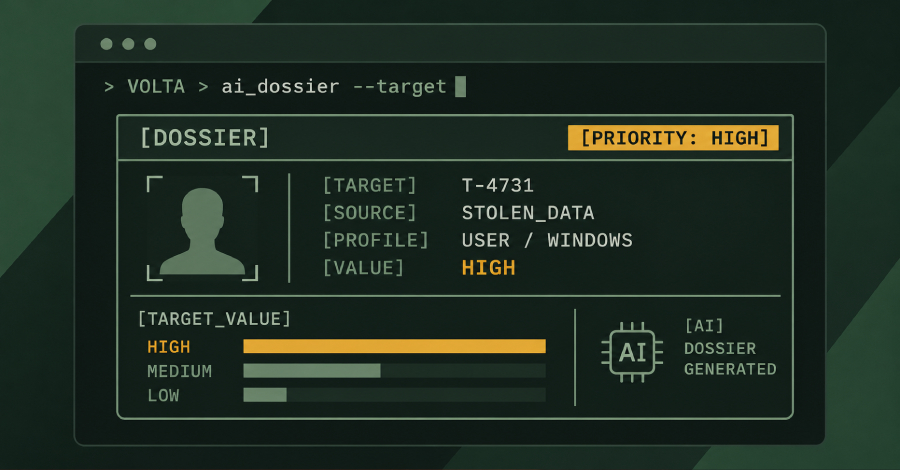
New VOLTA Infostealer Uses Claude, Gemini, and Kimi AI to Rank Victims by Financial Value
Cybersecurity researchers have discovered a new Windows infostealer malware called VOLTA-AUTODOXER (aka VOLTA) that makes use of a large language model (LLM) to rank a victim’s stolen data by their monetization value. Like other typical stealer families, VOLTA is equipped to harvest passwords and cookies from Chromium-based web browsers; data from Outlook profiles and Slack […]
ISC Stormcast For Monday, November 2nd, 2026 https://isc.sans.edu/podcastdetail/10160, (Mon, Nov 2nd)
Post Content
Governing the agent workforce: New data on the next frontier of AI risk
In the fast-paced world of agentic AI, building agents and defending ROI is yesterday’s news. Today, the more pressing challenge is managing and governing the exploding workforce of agents to mitigate growing enterprise risk. The problem intensifies as AI agents move from advisory to more active roles. According to a survey of 200 IT and […]
Cadence Maestro puts domain-trained AI agents to work for chip design
Artificial intelligence has been part of semiconductor design for years, helping engineers optimize chip architectures for performance, power efficiency, silicon area and faster development. More recently, the industry has begun integrating large language models and AI agents into established electronic design automation (EDA) workflows. Now Cadence Design Systems is taking that approach further with its […]
Syrian Hacker Gets Prison Time in US After Over a Decade on the Run
A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities. The post Syrian Hacker Gets Prison Time in US After Over a Decade on the Run appeared first on SecurityWeek.
OneNote File Extraction, (Sun, Nov 1st)
Recently, I had to extract embedded files from a set of OneNote files (extension .one).
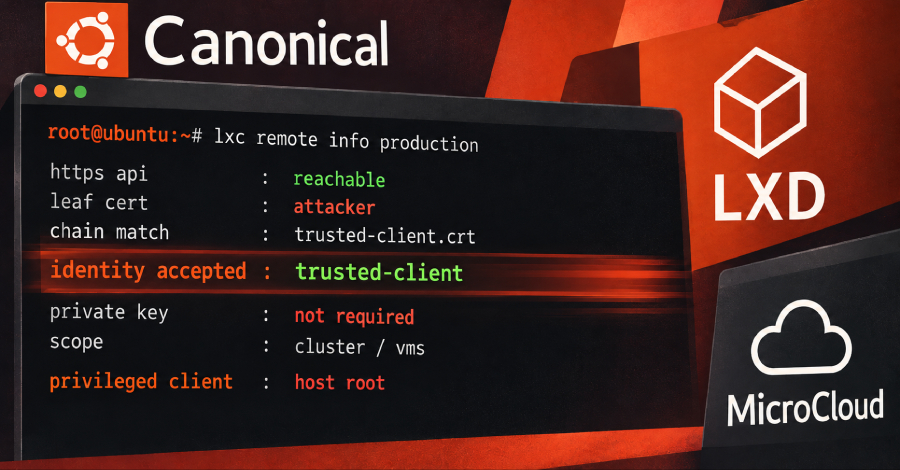
CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key
A critical flaw in Canonical’s LXD and MicroCloud let an attacker log in as a trusted client without holding that client’s private key. To do it, the attacker had to reach their HTTPS API over the network and have the trusted client’s public certificate. Once in, the attacker would act as that client, with access […]
Hackers Steal About $2.7 Million From Polymarket Traders via Hijacked DebugBear Script
Malicious code on the website of prediction market Polymarket sold some signed-in traders’ positions and moved their funds to the hackers on October 29. The code had replaced a page-speed script that the site loaded from an outside company. Polymarket says it is refunding about $2.7 million to 726 affected wallets. Blockchain records show crypto worth about $2.64 […]
FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist
The U.S. Federal Bureau of Investigation (FBI) has officially attributed the theft of more than $6 billion in virtual assets to TraderTraitor, a North Korea-aligned elite hacking group also tracked as Jade Sleet, Pressure Chollima, PUKCHONG, Slow Pisces, and UNC4899. The FBI, along with the U.S. Secret Service (USSS) and the Internal Revenue Service Criminal […]
NetamLoader Malware Targets Government Windows 10 Systems in Asia via .NET Injection
Cybersecurity researchers have disclosed details of what has been described as a “highly sophisticated infection chain” targeting government organizations in Asia. The activity, detailed by Kaspersky this week, targeted a custom Windows 10 build used exclusively by government entities in Asia and involves the deployment of a previously undocumented .NET assembly-loading framework codenamed